Managing WordPress security for 30+ client sites means every site gets the same minimum checks on a fixed schedule, and every alert has a named owner and a deadline written down in advance. At that scale, the risk isn't a missing tool. It's the site nobody has looked at properly since spring.
If a plugin on client site number 23 had a known flaw tonight, how long until someone on your team knew? This playbook is for agencies managing multiple WordPress sites who want a straight answer to that. You'll get a baseline, a weekly WP-CLI sweep script, and alert rules you can copy.
Where does site-by-site checking break down?
Manual checks don't fail loudly. They fade. Site 3 gets a careful look every week. Site 22 gets a glance, then gets skipped during a busy launch. Nobody decides to stop checking it. It just happens, and you find out when something goes wrong there.
Here's a worked example, with our own assumptions. If a proper look at one site takes 10 minutes, 30 sites take 5 hours a week. That's before anyone fixes anything. Most small teams can't protect that time every week, so the checks get shorter and less even.
Alerts don't scale either
The usual fix is "let the plugin email us." That works for five sites. At thirty, the inbox becomes the problem. One agency owner told the Wordfence support forum they cap each site at one email an hour because they "monitor a lot of sites" and would otherwise get "a monstrous number of emails."
Another owner, in a separate thread, got "something like 12 emails within less than 1 minute" for a single blocked IP. When alerts arrive like that, the one that matters looks the same as the forty that don't.
And a weekly check alone is too slow
Speed matters for one kind of issue more than any other: a known flaw in a plugin you run. Patchstack's State of WordPress Security in 2026 report counted 11,334 new WordPress vulnerabilities in 2025, with 91% in plugins. It found about half of high-impact flaws were exploited within 24 hours of going public.
The same report says 46% of those vulnerabilities had no fix from the developer by the time they were made public. So updates alone won't always save you. You need to know which sites run the affected plugin, fast, and decide what to do there.
What should every client site have, the same way?
A shared baseline turns thirty different sites into one checklist. It doesn't need to be fancy. It needs to be identical, so a missing item stands out. Here's the baseline we'd start with, and why each line earns its place.
| Baseline item | Why it matters at 30+ sites |
|---|---|
| Backups you've restored at least once | An untested backup is a guess. Restore one site per tier each quarter |
| An update policy per site | Decide which sites auto-update plugins and which wait for you, then write it down |
| A known list of administrators | Every admin should be a person you can name. Old staff and contractor logins go |
| Login protection | Lockouts after repeated failed logins, plus two-factor login for admins |
| One security plugin, configured the same way | Same firewall mode, same log length, so findings mean the same thing everywhere |
| Alert emails going to your team | Plugins often email the site's own admin address. If that's the client, you won't see it |
The last row catches more agencies than any other. In one WordPress.org thread, a site manager asked why their client, not them, was getting security emails. Check the address in Settings > General and in your security plugin, on every site, once.
If you're still building the baseline, our WordPress hardening checklist covers the site-level settings, and security in your maintenance plan covers how to put it in a contract.
A weekly routine that covers every client site
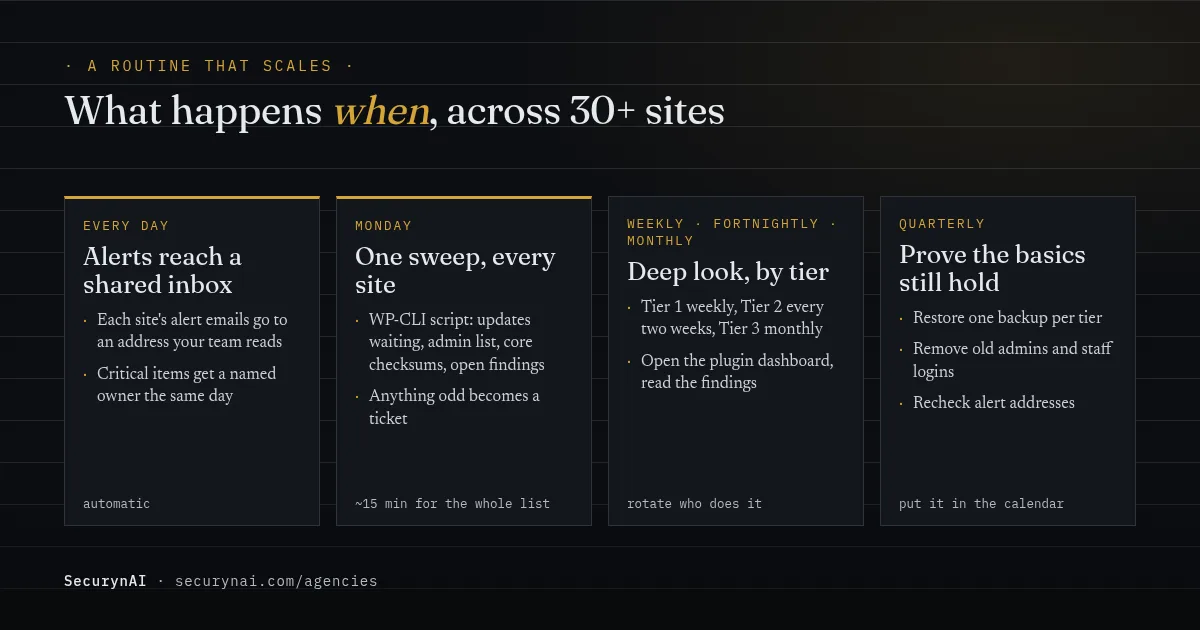
Split the work into a fast sweep of every site and a slower look at a few. The sweep finds what changed. The deep look reads the findings properly. Doing both on a schedule is what keeps site 22 from fading out.
Tier your sites by risk
- Tier 1: stores, membership sites and anything with customer logins or payments. Deep look every week.
- Tier 2: business sites that collect leads through forms. Deep look every two weeks.
- Tier 3: brochure sites with no logins but yours. Deep look once a month.
Every tier still gets the Monday sweep. Tiering only decides how often a person reads the findings in detail.
The Monday sweep, with WP-CLI
If you have SSH access to your clients' hosting, WP-CLI aliases let you run one command against every site from your own machine. First, give each site an alias in ~/.wp-cli/config.yml.
@client-acme:
  ssh: deploy@acme-host.example/var/www/acme
@client-bloom:
  ssh: deploy@bloom-host.example/srv/www/bloom
WP-CLI has a built-in @all alias that runs a command against every registered alias. Run wp cli alias list first to see exactly which sites that covers. Then these three commands only read; they change nothing.
wp @all core verify-checksums
wp @all plugin list --update=available --fields=name,version,update_version
wp @all user list --role=administrator --fields=user_login,user_registered
The first compares core files with the official WordPress.org copies, as the WP-CLI docs describe. The second lists plugins with updates waiting. The third lists every administrator with the date they were created. A new admin you can't name is your first ticket.
Anything odd becomes a ticket with an owner, not a mental note. If you'd rather use a dashboard than a terminal, tools like MainWP describe a self-hosted dashboard for managing many sites. The routine is the same either way.
Who handles each alert, and by when?
Write the response down once, so nobody has to decide it at 6pm on a Friday. The table below is a starting point, not a standard. Match the times to what your contracts actually promise clients.
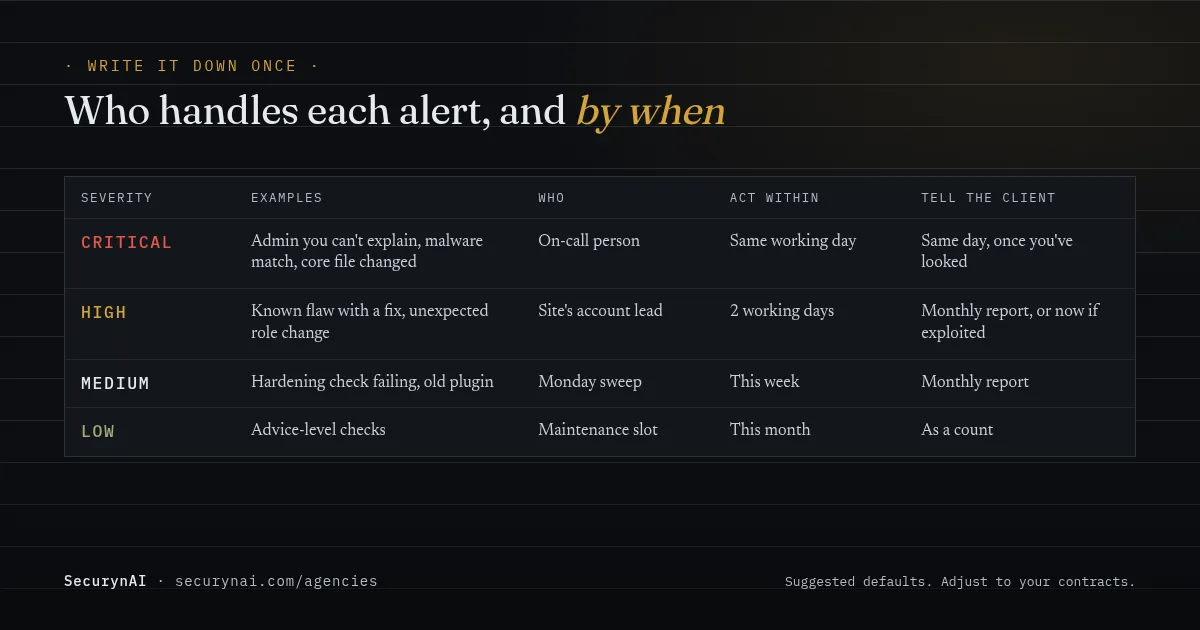
Two rules make this work. First, one person is on call each week, and critical alerts from every site go to them. Second, every alert ends as fixed, accepted with a reason, or scheduled. "Seen it" isn't an outcome.
When a critical alert turns out to be real, our playbook on explaining a hack to a client covers what to say. For the monthly report, the client security report template gives you a format.
Why shared access can turn one problem into thirty
At portfolio scale, your own logins are the biggest single risk. One reused password or one infected laptop can reach every site you manage. That's a risk a single-site owner simply doesn't carry.
A 2023 WordPress.org thread shows how this looks. The poster had "at least a dozen" sites hacked at once, with hidden admin accounts on each, despite updates and a security plugin on every site. They suspected their own computer.
- Give each person their own login on each site. No shared "agency" admin account.
- Keep passwords in a team password manager, unique per site.
- Remove access the day someone leaves. Our offboarding playbook lists what to revoke.
- Treat an unexplained new admin as a break-in. The new admin user guide and privilege drift guide walk through the checks.
How SecurynAI fits a 30-site portfolio
We at SecurynAI want to be plain about this first. There's no central multi-site console. Each site runs its own copy of the plugin, with its own dashboard. If one screen for every client is a must, a management tool like MainWP is the better fit for that part.
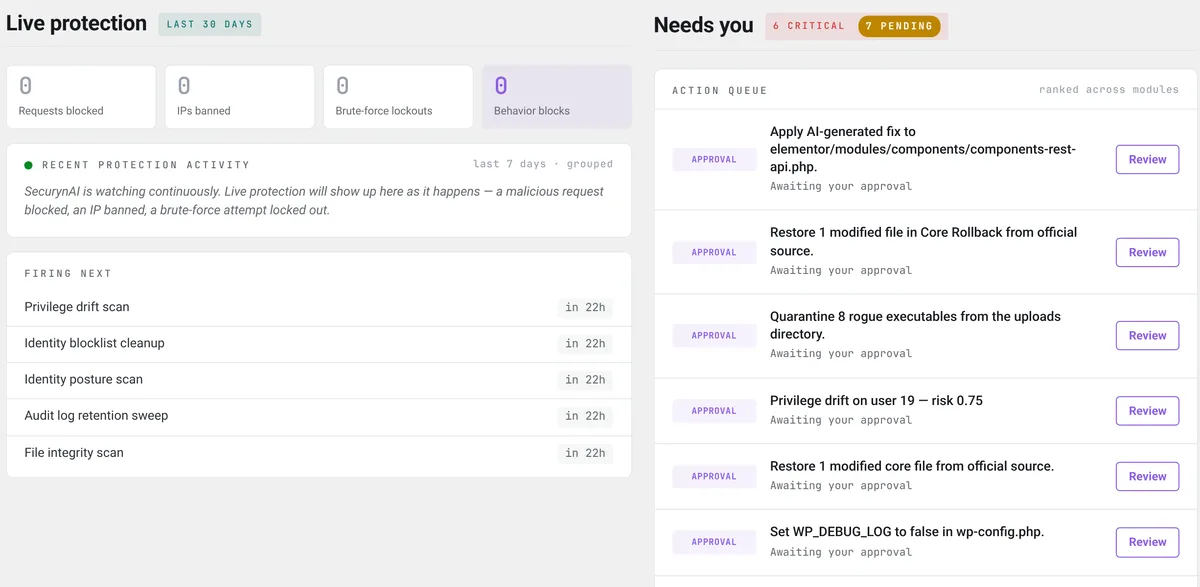
What we built for is making each site's check short. The free plugin's Dashboard shows a posture line ("X of Y checks passing", with the change this week), a count of critical items under Needs you, and an action queue ranked across all its checks. That's the screen for your tiered deep look.
What the free plugin checks on each site
- A daily file scan of core, plugin and theme files against official checksums. It also checks every PHP file under wp-content against 13 bundled malware signatures, with no live feed. It flags only high-confidence obfuscated code, and detects without cleaning anything.
- Vulnerability alerts for installed plugins, themes and core, in plain English.
- A runtime firewall that starts in Monitor mode. It logs matches without blocking until you switch each site to Block. Login lockout works in either mode; automatic IP blocks need Block.
- Role and admin changes, and an activity log you can keep for 1 to 365 days (7 by default).
On every client site, open Settings > General. Switch on Email serious findings (it's off by default) and put your agency address in Send alerts to. Left empty, emails go to the site's admin address, which may be the client's.
Only new critical and high findings are emailed, and findings from one scan arrive as a single email, so thirty sites won't flood your inbox. Also set Keep activity for to 30+ days, in case you need to investigate an incident.
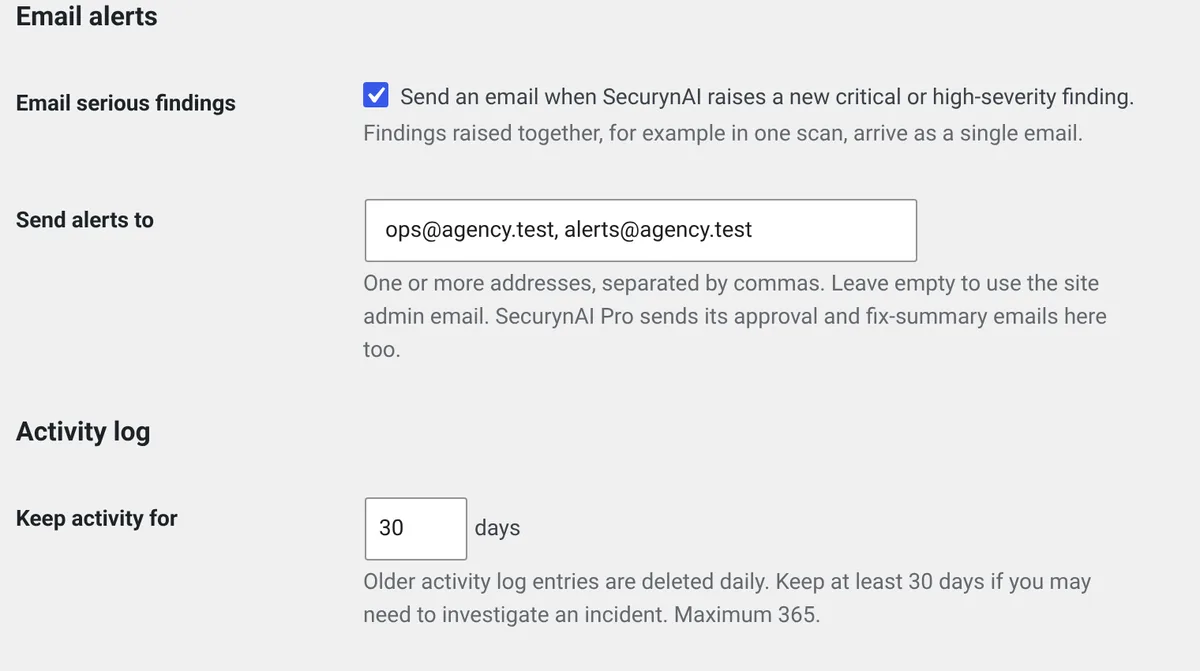
Turn every site's findings into one list
You can add SecurynAI to the WP-CLI sweep. These lines show the plugin's status and version, each site's firewall mode, and a count of open findings by severity. We ran them on our own test site. They only read.
wp @all plugin get securyn --fields=name,status,version
wp @all option pluck securyn_settings firewall_mode
wp @all eval 'global $wpdb; $t = $wpdb->prefix . "securyn_findings"; foreach ( $wpdb->get_results( "SELECT severity, COUNT(*) AS n FROM $t WHERE status = \"open\" GROUP BY severity" ) as $r ) { echo "$r->severity: $r->n\n"; }'
A site still reading monitor after you meant to switch it to Block shows up straight away. So does a site where the plugin was deactivated.
What Pro adds for teams
Pro ($79 per site per year) adds more email. Fixes that need a person's approval wait in a queue: critical items are emailed straight away, the rest in a daily digest. With an alert address set, these go there instead of to every administrator, so client admins don't get them.
An optional daily summary, off by default, lists fixes applied, reverted or failed, with one-click revert links. Some incident responses also email the admin address, with the severity in the subject line.
Pro's Patch Queue can update vulnerable plugins automatically. By default, its policy auto-approves updates from wordpress.org when a fixed version exists, rolling back if the update fails. Themes, core and premium plugins show "Manual update required". Pro can also export a 90-day compliance evidence bundle per site.
None of this replaces backups, updates or good hosting. It shortens the time between "something changed" and "someone who can fix it knows."
Quick check: is your portfolio under control?
- Could you list every client site, its tier and its owner in five minutes?
- Do all alert emails reach an inbox your team reads every day?
- Have you restored a client backup in the last three months?
- Can you name every administrator on your Tier 1 sites?
- Does each person on your team have their own login on each site?
- Is your alert response written down, with times?
Five or six yeses means the routine is working. Three or four is common, and a month of steady work closes the gaps. Fewer is a normal place to start. Pick your Tier 1 sites, set up the sweep there, and widen it once it's a habit.
Managing multiple client sites: FAQ
Do I need a central dashboard to manage 30+ client sites?
It helps, but it isn't the first thing to fix. A dashboard shows you everything in one place; it doesn't decide who acts on an alert or check that backups restore. Get the baseline and the weekly routine right first, then add a console like MainWP or Wordfence Central if switching between sites is the bottleneck.
How often should an agency check client sites for security issues?
Run a quick automated sweep of every site once a week, and look closely at each site on a schedule set by its risk: stores and membership sites weekly, brochure sites monthly. Critical alerts shouldn't wait for either. Patchstack found that about half of high-impact WordPress flaws are exploited within 24 hours of going public.
Should security alerts go to me or to the client?
To you, if you're paid to look after the site. Security plugins often email the site's admin address or an address set in their own settings, so check both on every site. In SecurynAI, that's Send alerts to under Settings > General. Clients still hear about anything serious, but from you, with the context and the fix.
Does SecurynAI have a multi-site dashboard?
No. SecurynAI runs as a plugin on each site, with its own dashboard, and there's no central console today. Agencies use the per-site dashboards, email alerts sent to one agency address and a WP-CLI sweep to see the whole portfolio. Bulk licensing for many sites is available on request.
Looking after 30 or more client sites? Start with the free plugin on your Tier 1 sites, then talk to us about bulk licensing for the rest. A real person replies.
See agency options →