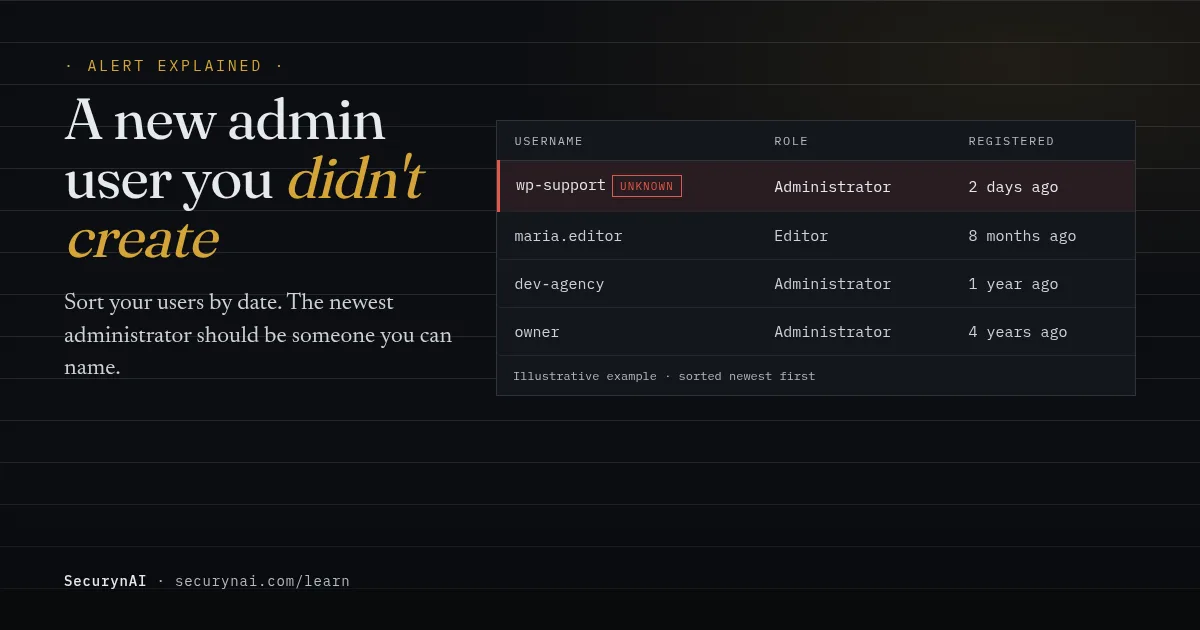
A rogue admin account is a WordPress user with the Administrator role that nobody who runs the site created or approved. An administrator can install plugins, edit theme code and add more users. So an account like that is full control of your site in someone else's hands.
You've found a new admin user you didn't create. Here's the safe first move: don't delete it yet. Write down its username, email and registration date, then ask everyone with admin access whether they made it. That one message settles a surprising number of these.
Is a new admin user you didn't create always a hack?
Not always, but usually. WordPress doesn't make administrator accounts by itself. If nobody on your side can explain the account, treat it as a break-in until you've proved otherwise.
Innocent explanations exist. A developer, agency or host's support team may have added a login for a job, and a few services set up their own account. In each case, someone you work with can say exactly where it came from.
Alerts can also fire on your own work. In a WordPress.org support thread, a site owner kept getting an "admin user created outside of WordPress" warning about an account they'd added themselves. Support first raised a possible compromise, then helped clear the alert once the account was confirmed.
When it's probably fine
- A teammate, developer, agency or your host confirms they created it, and says why.
- The name or email clearly matches a service or plugin you set up that day.
- The registration date lines up with a job you know about.
When to treat it as a break-in
- Nobody claims it, or the email is a free webmail address no one recognises.
- The name looks official but isn't, like wpsupport or adminbackup.
- You delete it and it comes back.
- It appeared around the same time as an unfamiliar plugin, odd redirects or an admin login from an unusual location.
How does a rogue admin account get created?
There are three common routes. Knowing which one you're dealing with tells you where to look before you delete anything.
1. A flaw in a plugin
Plugins are where most WordPress holes are. Patchstack's State of WordPress Security in 2026 report counted 11,334 new WordPress vulnerabilities in 2025, with 91% in plugins. It found the median time to mass exploitation of heavily targeted flaws was five hours.
Some flaws let a stranger create an administrator directly. In April 2025, Patchstack reported a bug in the SureTriggers plugin (version 1.0.78 and below) that let attackers add admin accounts on sites where the plugin's secret key wasn't set. The first attack it recorded came about four hours after it added protection for the flaw.
2. Code running in a real admin's browser
Sometimes the attacker never logs in: a planted script creates the account when a real admin opens a page. One owner described this in a WordPress.org thread about Brevo for WooCommerce: "every time I visit the Brevo plugin page on my WP backend, a new illicit admin user is created." Brevo said version 4.0.51 fixed it.
3. A backdoor that recreates the account
Once attackers are in, they often plant code whose only job is to bring the admin back. Sucuri traced one recurring admin called "user" to two lines in the active theme's functions.php. It was recreated every time anyone visited the site.
Some go further. In July 2025, Sucuri found a fake "WP Compatibility Patch" plugin that created an admin called adminbackup. It hid that account from the Users screen, adjusted the admin count to match, hid itself from the Plugins list and blocked attempts to delete the user.
There's also a quieter trick: changing settings so every new signup becomes an admin. In one WordPress.org thread, a site owner found that "all accounts created come up as administrator," even through normal registration.
How to check your WordPress admin users properly
Look first, change things later. In the dashboard, go to Users, filter by Administrator, and check each name and email. Then open Settings > General and confirm New User Default Role is Subscriber or your lowest role. If you have SSH and WP-CLI, the commands below only read.
1. List administrators, newest first
wp user list --role=administrator --orderby=registered --order=DESC --fields=ID,user_login,user_email,user_registeredwp user list passes extra options to WordPress's user query, which accepts registered as a sort order. You should be able to name the account at the top.
2. Run it again without plugins or your theme
Malicious code can hide a user from lists. Adding --skip-plugins --skip-themes stops normal plugins and your theme from filtering the results, though the WP-CLI handbook notes must-use plugins still load.
3. Ask the database directly
wp db prefix)wp db query "SELECT ID, user_login, user_email, user_registered FROM wp_users ORDER BY user_registered DESC LIMIT 10"wp db query runs plain SQL with your site's database login, so no plugin can hide a row. If an account shows here but not in step 1, something is hiding it. That alone tells you the site is compromised.
4. Check the settings and app passwords
wp option get default_role
wp option get users_can_register
wp user application-password list 42
administrator as the default role is never right. And application passwords let apps sign in as a user without the normal password, so check the new account and your real admins for any you don't recognise.
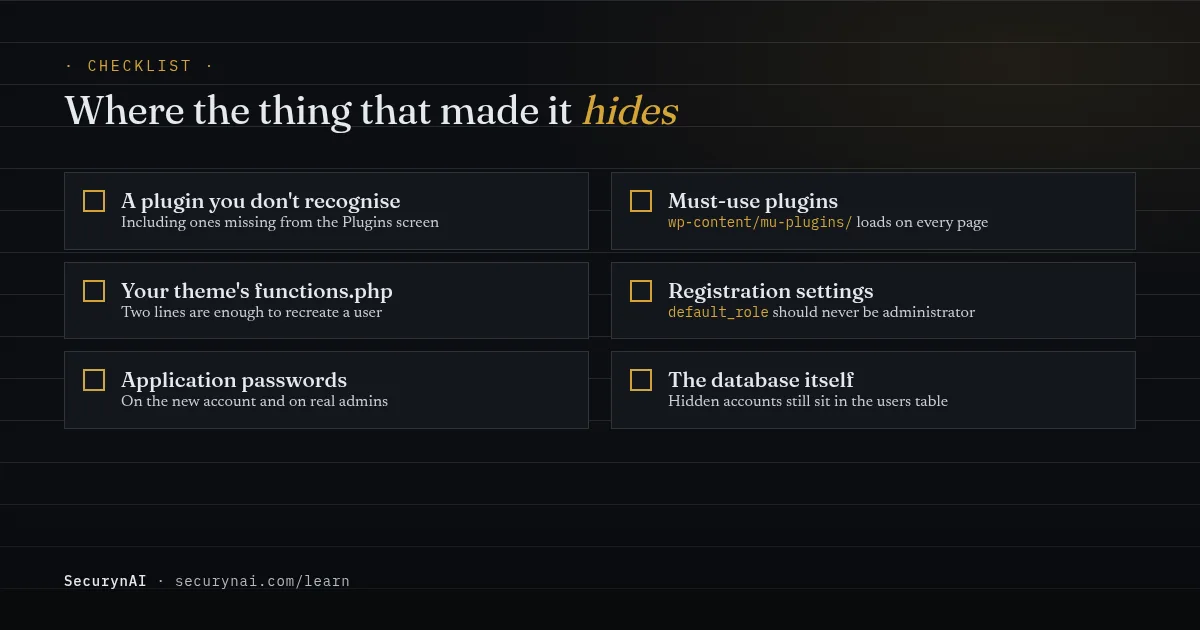
What to do about a rogue admin account, in order
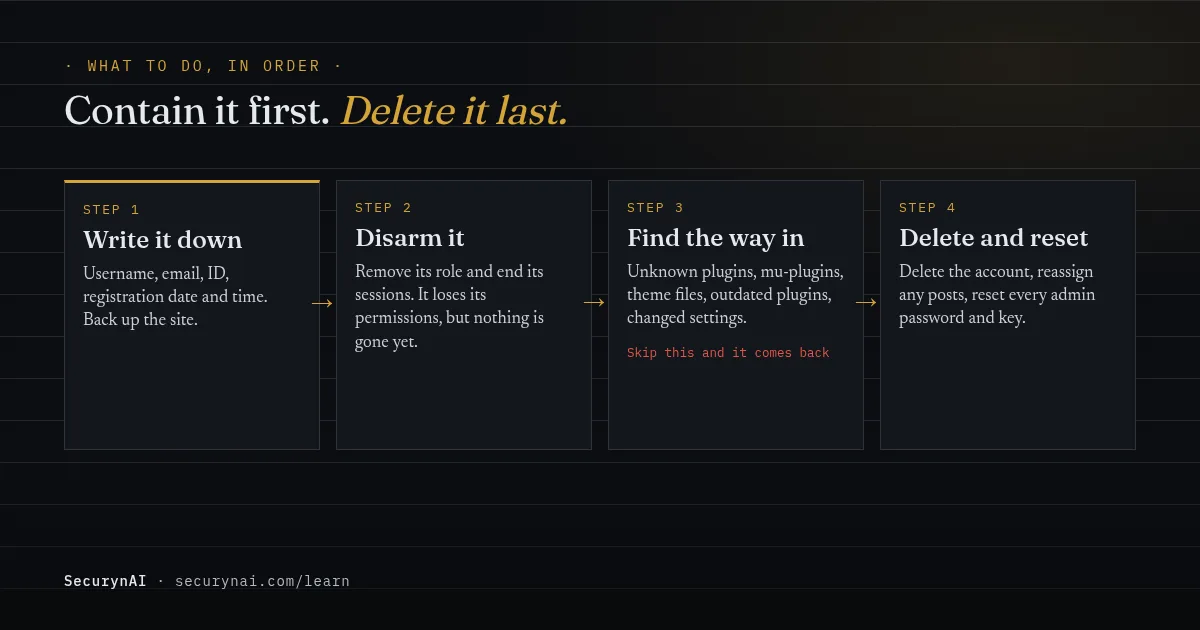
Contain it first and delete it last. Deleting straight away feels right, but if the thing that made the account is still there, it just makes another. Back up the site (files and database) before you change anything, then work through these steps.
- Write it down. Save the username, email, user ID and registration time. You'll need them to match up activity logs, and to explain what happened to a client.
- Disarm the account. Remove its role, which strips its permissions, then log it out everywhere. With WP-CLI:
wp user remove-role 42(with no role named, it removes all of them on a single site) andwp user session destroy 42 --all. - Find the way in. Look for plugins you don't recognise, files in
wp-content/mu-plugins/, recent edits to your theme, and outdated plugins with known flaws. Our webshell guide shows how to search for hidden files. - Close it. Remove the malicious code, update or remove the vulnerable plugin, and put the default role and registration settings back.
- Delete the account. Hand any posts to a real user with
wp user delete 42 --reassign=1, where 1 is an admin you trust. - Reset every admin password and key. Include hosting, SFTP and database passwords, and revoke application passwords you don't recognise. An attacker with admin access may have seen any of them.
If the account keeps coming back, treat the whole site as compromised. Work through our full cleanup guide or restore from a clean backup. For a client's site, see our playbook on explaining a hack to a client.
How SecurynAI flags a new admin user
We at SecurynAI built this check because WordPress tells plugins when a user is given a role but keeps no history you can look back on. The free plugin flags a new account that starts as an administrator as a critical privilege drift finding, the moment WordPress assigns the role.
A new account that gets your site's default role, usually Subscriber, isn't flagged. That keeps normal signups quiet. A new editor or shop manager is flagged as high. Each finding sits on the Identity screen with the roles it gained, a plain-English explanation and a next step.
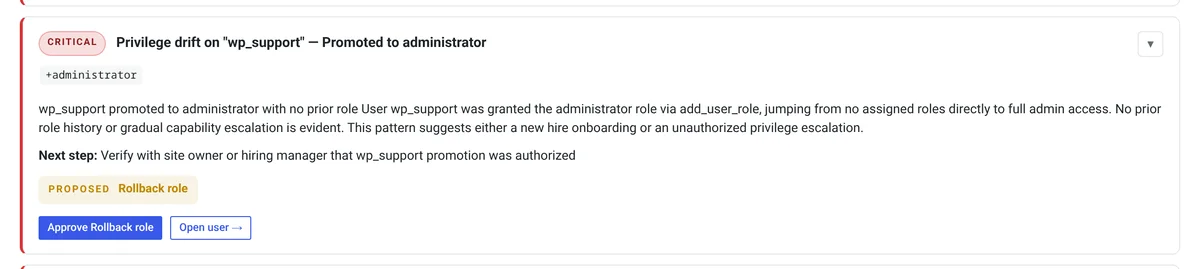
The free plugin also offers a Rollback role fix. For a brand-new account, that means taking away every role it has, which matches step 2 above. Nothing changes until you click approve, the account itself isn't deleted, and a Revert option puts the role back if you got it wrong.
The Audit Log records every new user with their roles, plus changes to the default role and registration settings. It keeps a week of activity by default. And the hardening checklist warns if your default role is anything other than Subscriber.
Two tricks attackers use are covered too. If someone first sets the default role to Administrator, new signups are still flagged, because a privileged default role doesn't count as normal onboarding.
The second trick, an admin account inserted straight into the database, bypassing WordPress, is caught by the daily privilege scan instead of the moment it appears. That gap of up to a day is why the database query above is still worth running.
With your own AI key, each file-integrity scan also asks the AI to flag recent admin accounts with generic names. On Pro ($79 per site per year), we add a risk score. A brand-new administrator always scores as high risk, so the rollback goes to your approval queue, where by default one admin approves it.
None of this replaces updating plugins or keeping backups.
Quick check: could you spot a new admin today?
- Can you name the person behind every administrator account?
- Is your New User Default Role set to Subscriber?
- Is registration closed, unless you really need it open?
- Would you know within a day if a new admin appeared?
- Are all your plugins updated, with unused ones removed?
Five yeses means you're in good shape. Two to four is common and quick to fix this week. Fewer is a normal starting point. Our WordPress hardening checklist covers the rest, and the guides to privilege drift and dormant admin accounts deal with the other admin problems: existing users who gain access, and old accounts nobody uses.
New admin user FAQ
Why does the unknown admin user come back after I delete it?
Because something on the site recreates it. Usually that's a few lines of code in a plugin, a must-use plugin or your theme's functions.php, and it runs on every page load. Find and remove that code first, then delete the account.
Should I delete the rogue admin or just change its password?
Neither, at first. Remove its role and end its sessions so it loses its permissions, then find how it was created. Delete it once the way in is closed, and reset the passwords of your real admins too.
Will SecurynAI flag an admin account I created myself?
Yes. A new account that starts as an administrator is flagged as critical, because the plugin can't know who intended it. If it was you or a teammate, confirm that and you're done.
Want to know the moment a new administrator appears, not weeks later? The free SecurynAI plugin starts watching user roles as soon as you install it.
Install free →