You cleaned up the hack. The spam is gone, the redirect stopped. A week later it's back. Before you delete anything else, take a full copy of the site as it is now. You'll want it if you need to trace what happened. Then read on, because a webshell is the most likely reason the cleanup didn't hold.
What is a webshell, in plain English?
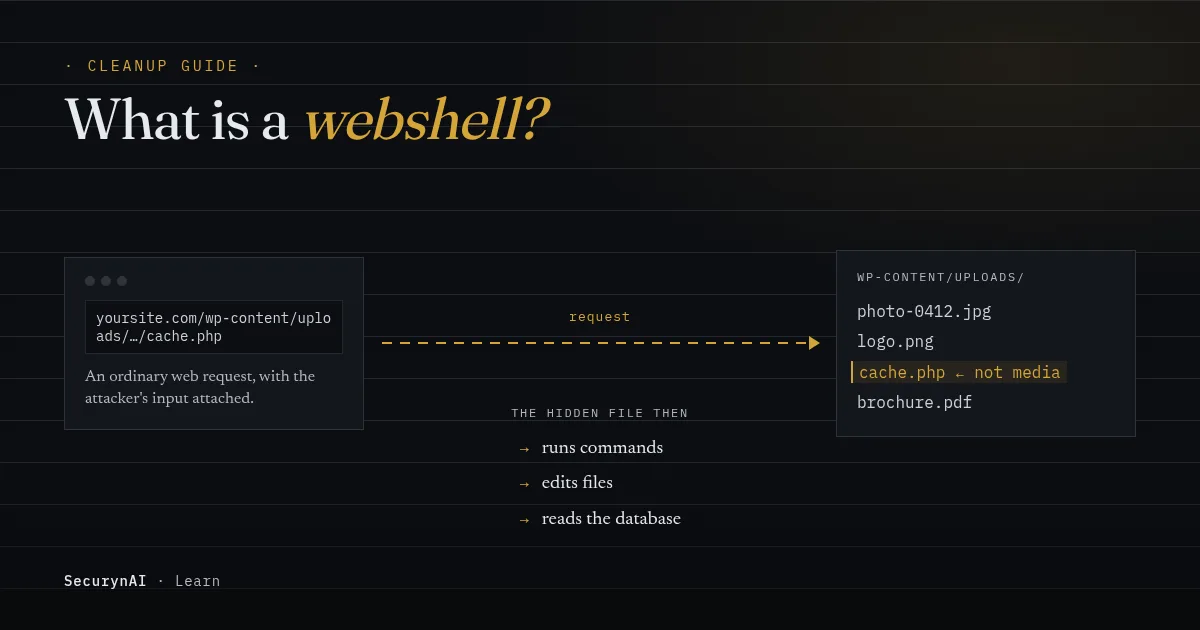
A webshell is a script an attacker leaves on your web server so they can send it commands through an ordinary web address. On WordPress it's almost always a PHP file. Visit its URL with the right input, and it runs code, edits files or reads your database on the attacker's behalf.
It isn't the bug that let them in. It's what they leave behind after getting in, so they never need that bug again. MITRE ATT&CK files webshells under "persistence" for exactly that reason: adversaries use them "to establish persistent access to systems."
Why a webshell brings a "cleaned" WordPress site back
Most hacked sites still have a backdoor in them when cleanup starts. In its 2022 Website Threat Research Report, Sucuri found that 69.63% of the compromised sites it cleaned had at least one backdoor, and its team removed 1,188,864 backdoors that year.
You can see this pattern in the support forums. In one WordPress.org thread, a site owner deleted a malicious file only to watch it reappear. The reply was blunt: "Sounds like a backdoor is still being left on the server."
A webshell survives the usual cleanup steps because:
- Updating the plugin doesn't touch it. The webshell is its own file. Closing the original hole doesn't remove what came through it.
- Changing passwords doesn't touch it. It never logs in. It runs its own code.
- A backup only helps if it's older than the infection. Restore one taken after the webshell arrived, and you restore the webshell too. Our guide to restoring after a hack covers how to pick the right one.
Where does a webshell hide on WordPress?
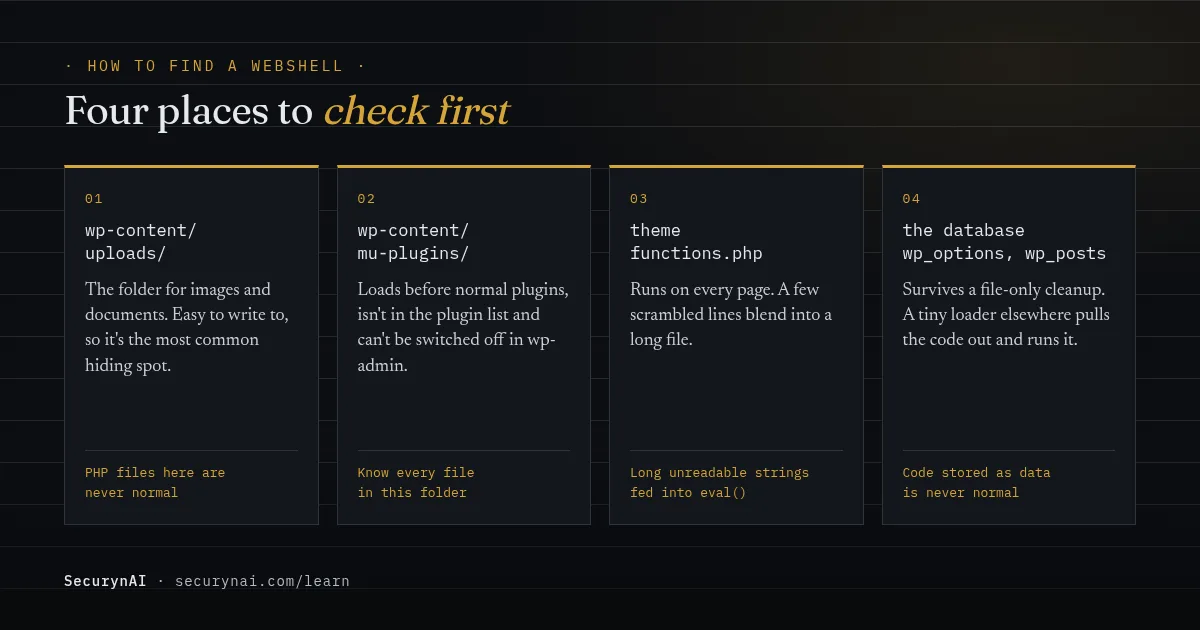
Start with the folders that should never hold code, then move to the files nobody reads. Here are the usual spots, roughly in the order we'd check them.
| Location | Why attackers use it | Is PHP normal here? |
|---|---|---|
wp-content/uploads/ | It's writable, and a file upload flaw drops files straight into it | Almost never. An empty index.php is the only common exception. |
wp-content/mu-plugins/ | Runs on every page, before normal plugins, and can't be switched off from wp-admin | Sometimes. Some hosts add their own. Check each one is yours or your host's. |
Theme files (functions.php, index.php) | Runs on every page load, and long files hide an extra function well | Yes, which is why code here is easy to miss |
The database (wp_options, wp_posts) | Survives a file-only cleanup. A tiny loader elsewhere pulls the code out and runs it. | Code stored as data is never normal |
The mu-plugins row deserves a second look. According to the WordPress documentation, must-use plugins load "before normal plugins," don't appear in the regular plugin list, and "cannot be disabled from wp-admin." That makes them a quiet place to park a backdoor.
Expect the code to look scrambled. Webshells rarely read as plain PHP. They wrap the real payload in layers of encoding so a quick text search won't spot it.
How to find a webshell, step by step
Look first, delete later. If you haven't yet, back up the whole site (files and database) before you change anything. The commands below only read and list. They need SSH access and, for the wp commands, WP-CLI. If you don't have either, your host's support team can usually run them for you.
1. Look for code in the uploads folder
find wp-content/uploads -type f \( -name "*.php" -o -name "*.phtml" -o -name "*.phar" \)Media folders hold images and documents. Any script here with real code in it should be treated as hostile until you've proven otherwise.
2. Check core and plugin files against the official copies
wp core verify-checksums
wp plugin verify-checksums --all
These compare your files with the checksums WordPress.org publishes (core, plugins). Premium plugins and themes from elsewhere aren't covered, so compare those against a fresh download from the vendor.
3. List recently changed PHP files
find wp-content -type f -name "*.php" -mtime -14Match each result to an update you actually ran. A file that changed when nobody updated anything is worth opening. Attackers can fake file dates, though, so a clean result here isn't proof.
4. Read your mu-plugins and theme functions file
Open every file in wp-content/mu-plugins/ and your active theme's functions.php. You're looking for code you can't explain, especially long unreadable strings fed into eval(). If something looks off and you're not sure, ask before deleting. Some legitimate plugins use encoding too.
Found a webshell? Here's what to do next
Finding one webshell means you look harder, not that you're done. Attackers often leave a spare. One freelancer's write-up of a reinfecting client site found a disguised uploads file, scrambled theme code, a rogue admin and a cron job, all working together.
Webshells aren't a WordPress-only habit, either. Cisco Talos reported attackers deploying web shells in 35% of the incidents it responded to in the fourth quarter of 2024, up from under 10% the quarter before.
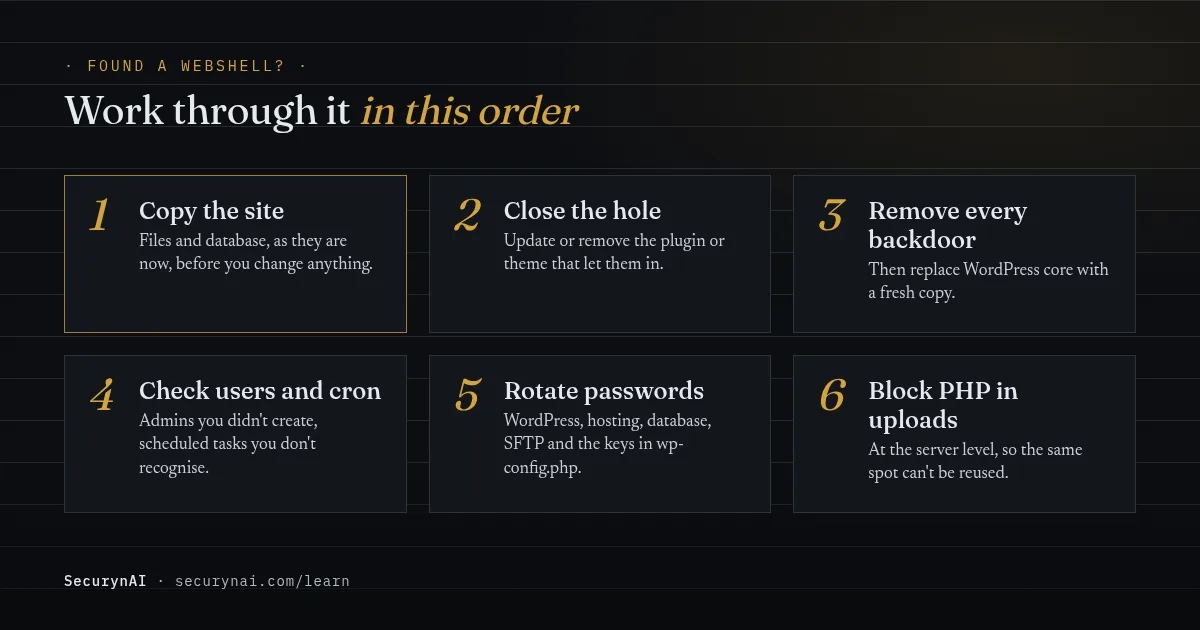
Once you've got a copy for your records, work through this order:
- Close the hole. Update or remove the plugin or theme that let them in. Removing the webshell first just invites a new one.
- Remove every backdoor you found, and replace WordPress core with a fresh copy rather than editing it. The full malware removal guide walks through this.
- Check for the other ways back in: admin users you didn't create and scheduled tasks you don't recognise.
- Rotate every password and key: WordPress users, hosting, database, FTP/SFTP, and the security keys in
wp-config.php. - Stop PHP running in uploads at the server level, so the most common hiding spot can't be reused. Our hardening checklist covers it.
That last step comes up again and again. The top answer in a Linode community thread warns that deleting infected files "will only be a temporary fix," because "most intruders will create an additional point of entry."
How we at SecurynAI check for webshells
The free SecurynAI plugin runs these checks for you, on a daily schedule by default. Here's exactly what it looks at, so you know what's covered and what isn't. All of the following are in the free version.
- Scripts in uploads. It flags any PHP-type file (
.php,.phtml,.pharand similar) underwp-content/uploads. - Known webshell patterns. It checks PHP files in
wp-contentagainst a set of patterns, such as encoded strings fed intoeval()or commands run straight from a visitor's input. Each hit shows the matching snippet and a plain-English reason. - Heavily scrambled code. It only raises this when the shape is near-certain, like a decoder feeding directly into
eval(), because plenty of legitimate plugins use some encoding. - Changed core and plugin files. It compares core and WordPress.org plugins against official checksums.
We'll be straight about the limits. SecurynAI doesn't scan the database for stored code, and no pattern list catches every webshell, a point we cover in why scanners get things wrong. It doesn't replace backups or updates. Pro adds an AI plugin-code scanner and one-click fixes with undo ($79 per site per year).
Webshell FAQ
Is a webshell the same as a backdoor?
Close enough for cleanup purposes. A backdoor is any hidden way back into a site, and a webshell is one kind: a script that runs the attacker's commands when they visit its URL. A rogue admin account or a malicious cron job is a backdoor too.
Will restoring a backup remove a webshell?
Only if the backup was taken before the webshell arrived. If it was already there when the backup ran, restoring puts it straight back. Even a clean restore leaves the original hole open, so update or remove whatever let the attacker in.
If I block PHP in the uploads folder, am I safe?
It closes the most common hiding spot, and it's worth doing. But webshells also hide in theme files, must-use plugins and the database, where that rule doesn't reach. Treat it as one layer, not the fix.
Will changing my WordPress password get rid of a webshell?
No. A webshell doesn't log in, so your password doesn't matter to it. Change passwords after you've removed it, so stolen logins can't become a second way back.
Cleaning up, or just want to know if something's hiding? The free plugin checks uploads, core files and known webshell patterns every day.
Install free →