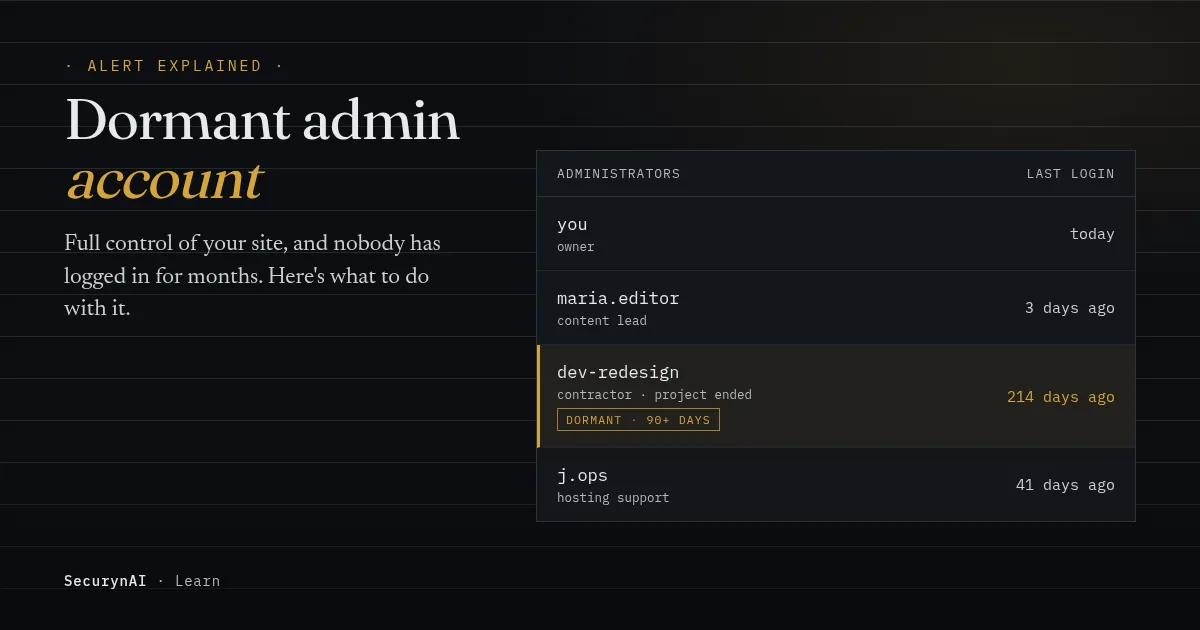
A dormant admin account is a WordPress administrator that nobody has logged into for a long time, usually 90 days or more. It still has full control of the site. It just has no one watching it.
Most are harmless leftovers. A few are a quiet way in. Either way, the fix is the same: find out whose it is, then remove it, demote it, or lock it down.
You got an alert about a dormant admin account. Nothing is broken and nobody is attacking you right now. So why flag it at all? Because an unused admin login is pure risk with no upside, and inactive WordPress admin users tend to pile up quietly over the years.
Is a dormant admin account actually dangerous?
Usually it's a leftover, not an intruder. Think of the freelancer from last year's redesign, a staff member who moved on, or a developer given access "just for today" in 2023. The account isn't doing anything. That's exactly the issue.
An admin account nobody uses is all risk and no benefit. If its password leaks, whoever has it gets full control of your site. And since the owner isn't logging in, nobody notices the odd login or the new plugin until much later.
Stolen passwords are still a common way in. Verizon's 2026 Data Breach Investigations Report found credential abuse was the first step in 13% of breaches. That's down from the top spot a year earlier, but still a major route.
On WordPress specifically, Wordfence's 2024 State of WordPress Security report says it blocked more than 100 billion password-guessing attacks in 2023, and that these made up the majority of attacks it saw.
Old accounts are the soft target in those attacks. They were often set up before you used strong, unique passwords or two-factor login, and the password may have been reused somewhere that has since leaked.
When it's probably fine
- You know exactly whose account it is, and they still need admin access occasionally.
- It has a strong, unique password and two-factor login.
- It's your own account and you simply haven't logged out and back in since installing SecurynAI (see the FAQ below).
When to act today
- Nobody can say who the account belongs to.
- The username or email looks unfamiliar, generic, or random.
- It was created recently but is already flagged. That's closer to a new admin user you didn't create, and that guide is the one to follow.
That last case is a real pattern. In one WordPress.org support thread, a site owner deleted an unknown admin called "wordpress" several times, and it kept coming back. The moderator's read: a script on the site was recreating it, which means the site was already compromised.
How to find inactive WordPress admin users
Here's the catch: WordPress doesn't record when a user last logged in. A site owner pointed this out years ago in a WordPress.org thread on deleting inactive users, and it's still true. The Users screen shows the role and email, not the last visit.
So start with the list you can get. In the dashboard, go to Users and filter by Administrator. If you have shell access, this WP-CLI command shows every admin and when they were created:
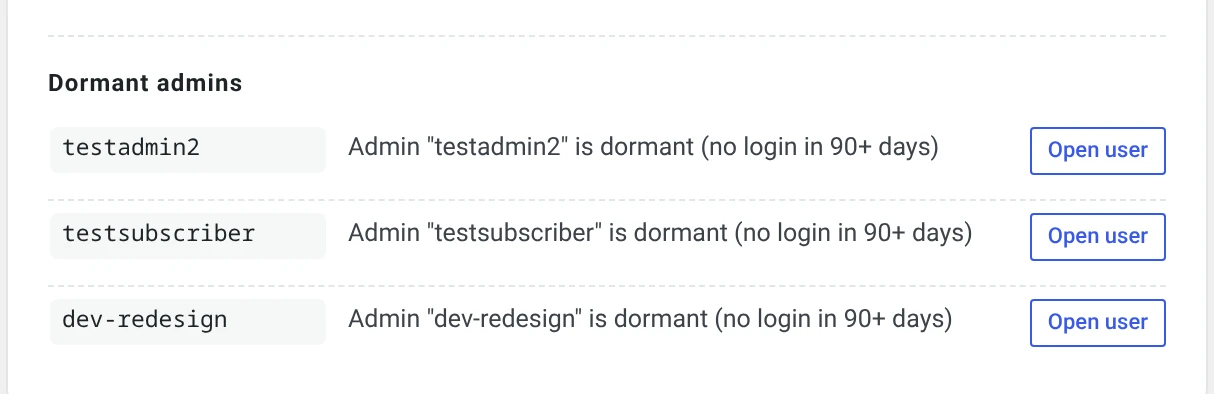
wp user list --role=administrator --fields=ID,user_login,user_email,user_registeredFor each name on that list, ask one question: who is this, and do they still need full control? If you can't answer, treat it as a candidate for removal. To know who has actually gone quiet, you need something that logs logins, such as a last-login plugin or a security tool.
What to do with a dormant admin account
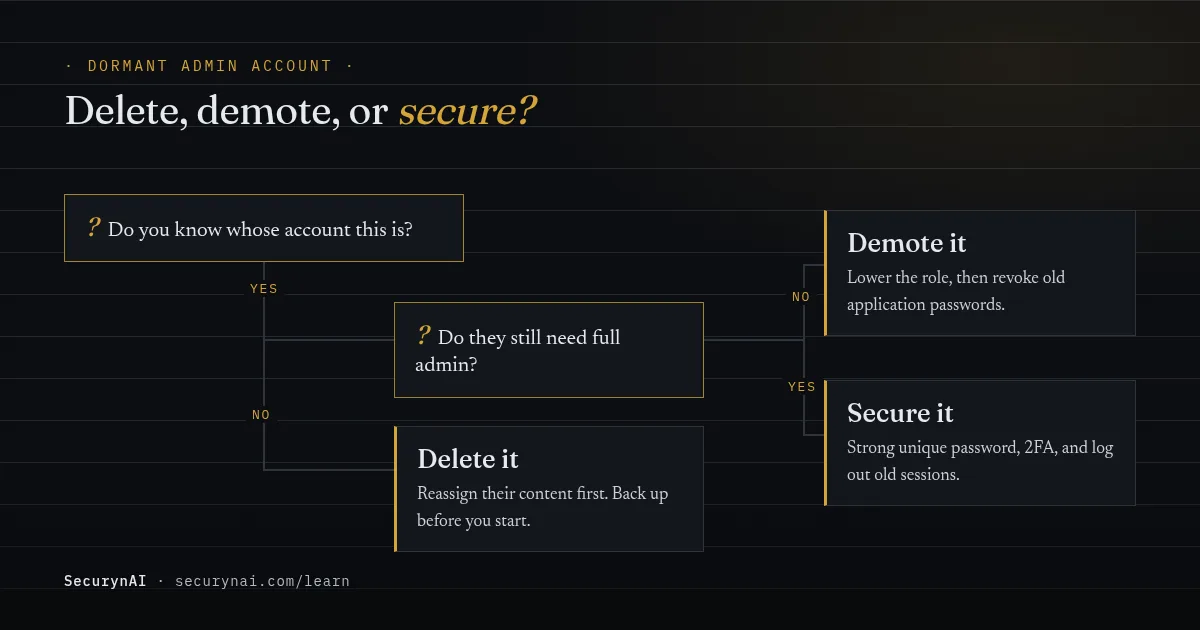
Pick one of three outcomes. The right one depends on whether a real person still needs that level of access.
1. Nobody needs it: delete it
Before you delete, make sure you're logged in as a different administrator you know works. Then delete the user and hand their posts and pages to someone else, so nothing disappears. WordPress asks what to do with the content when you delete a user. Choose Attribute all content to another user.
wp user delete 123 --reassign=1Back up first if this site matters to you. The --reassign option moves the user's posts to user ID 1 here. Without it, their content can go with them.
2. They need some access: demote it
An editor who writes posts doesn't need to install plugins. Change the role in Users, or with wp user set-role 123 editor.
One thing to know: demoting doesn't remove the account's application passwords (keys that let apps talk to your site as that user). They'll keep working with the lower role. Revoke any you don't recognise from the user's profile screen.
3. They need admin: secure it
Keep it, but give it a strong, unique password and two-factor login. Then end any old sessions, since a login cookie can stay valid for up to 14 days by WordPress's default:
wp user session destroy 123 --allIf you look after client sites, this is also the moment to tidy up how access is handed out. Our playbook on offboarding a client site securely covers the accounts agencies tend to leave behind.
How SecurynAI checks for dormant admins
We at SecurynAI built this check because last-login data is the piece WordPress is missing. The free plugin records every login it sees, then once a day flags any administrator with no successful login in 90 days. It's a medium-severity finding. It doesn't change or remove anything on its own.
Each finding says which account it is and recommends demoting or disabling it until the owner confirms they still need admin. When that person logs in again, the finding clears itself on the next daily check. SecurynAI also flags admin accounts where it can't detect a two-factor plugin, which pairs well with option 3 above.
On Pro ($79 per site per year), we add a fix you can apply from the finding: log the dormant admin out of every browser. It needs approval first, because it forces a real person to sign in again. Neither version replaces good habits, like removing access the day a project ends.
Quick check: your admin accounts
- Can you name the person behind every administrator account?
- Does each of them still need full admin, not just editor?
- Has every admin logged in within the last 90 days?
- Does every admin use two-factor login?
- Do you remove access when a contractor's project ends?
Five yeses means you're in good shape. Two to four is common and easy to fix this week. Fewer than that is a normal starting point, and our WordPress hardening checklist plus the guide to securing the login page are good next steps. If an admin has more access than their role suggests, read up on privilege drift too.
Dormant admin account FAQ
Why is my own admin account flagged as dormant?
SecurynAI only knows about logins it has seen since it was installed. If you were already logged in when you installed it, no login was recorded yet. Log out and back in, and the finding clears on the next daily check.
Should I delete or demote a dormant admin account?
Delete it if nobody can say who it belongs to or why it needs access. Demote it if the person still needs some access. Deleting also removes the account's application passwords, while demoting leaves them in place, so revoke those separately.
Will deleting a WordPress user delete their posts?
It can. WordPress asks what to do with the user's content when you delete them. Choose to attribute all content to another user, or use wp user delete with the --reassign option.
Does WordPress record when a user last logged in?
Not out of the box. Core WordPress doesn't store a last-login date, so you need a plugin or a security tool that logs logins to know which accounts have gone quiet.
Not sure which of your admins have gone quiet? The free plugin starts keeping track from the day you install it.
Install free →