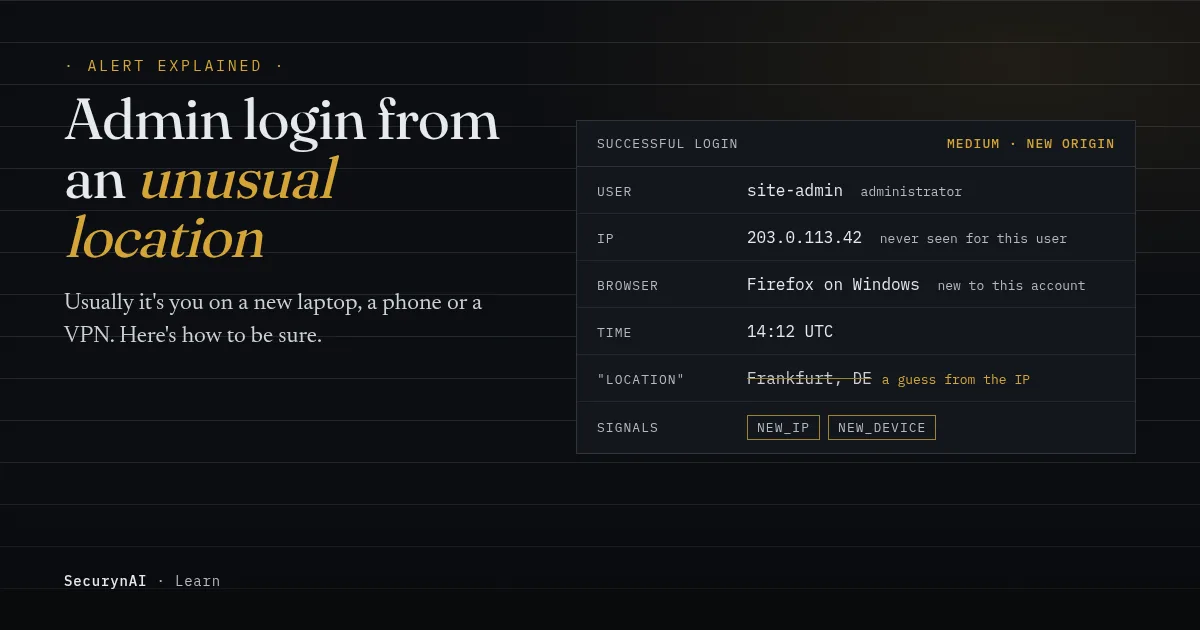
An "admin login from an unusual location" alert means someone signed in to an administrator account from an IP address or browser that account hasn't used before. It's a prompt to check, not proof of a hack. Most of the time, the person was you.
So start with one question: was this me, or someone I gave access to? If the answer is a clear no, don't wait. Sign that account out everywhere and change its password first, then come back and work out what happened. The steps are below.
Is a login from an unusual location actually bad?
Usually not. The "location" on a login alert is a guess made from the IP address, and that guess is often wrong. Your home internet provider can change your address overnight. Your phone on mobile data can appear to be in another city. A VPN can put you in another country.
The research backs this up. A 2017 academic study, summarised by ARIN, tested how well IP location databases place internet routers. At city level, about 75% accuracy was the upper limit, so at least one in four was wrong. Country level topped 95% for US routers, and was less reliable elsewhere.
Real site owners hit this all the time. In one WordPress.org support thread, an East Coast owner got an admin-login alert placed in San Jose. A volunteer asked whether they'd used a phone on mobile data or a VPN. The owner then realised their internet connection had a changing IP, so the login was probably theirs.
When it's probably fine
- You, or a teammate, logged in on a new laptop, a fresh browser, or after a big browser update.
- You were on a VPN, on hotel or office Wi-Fi, or on your phone's mobile data.
- A tool you use signs in for you, such as a maintenance service or a backup plugin.
When to act now
- Nobody on your team recognises the login, the browser or the time.
- It came straight after a run of failed login attempts nobody made.
- Something changed after it: a new admin user, a new plugin, or edited files.
How to check a suspicious WordPress login
Match the login to a person before you change anything. This takes a few minutes, and it saves you from locking out a colleague by mistake.
1. Ask who it could be
Check with anyone who has admin access, including agencies, freelancers and your host. Then think about tools. In one MainWP community thread, a stream of admin-login alerts turned out to be a bug in a firewall plugin's update, not a person at all.
2. Compare the browser and the time
Most alerts show the browser (the user agent) and a timestamp. Does the browser match a device you own? Watch the time zone. Many tools log in UTC, so a login at 2am UTC can be your own evening session in the US.
3. See which sessions are still open
WordPress keeps a record of each active login, including the IP and browser it came from. If you have shell access, this WP-CLI command lists them for one user (replace site-admin with the username):
wp user session list site-admin4. Check what the account did next
A login on its own is a question. A login followed by changes is a much stronger sign. Look for new administrators, plugins you didn't install, and recently edited files. Our guides to a new admin user you didn't create and privilege drift cover the account side in detail.
The login wasn't you: what to do, in order
Cut off access first, then investigate. These steps don't delete anything, so you can do them before you've taken a backup. Back up before you remove any files or users later on.
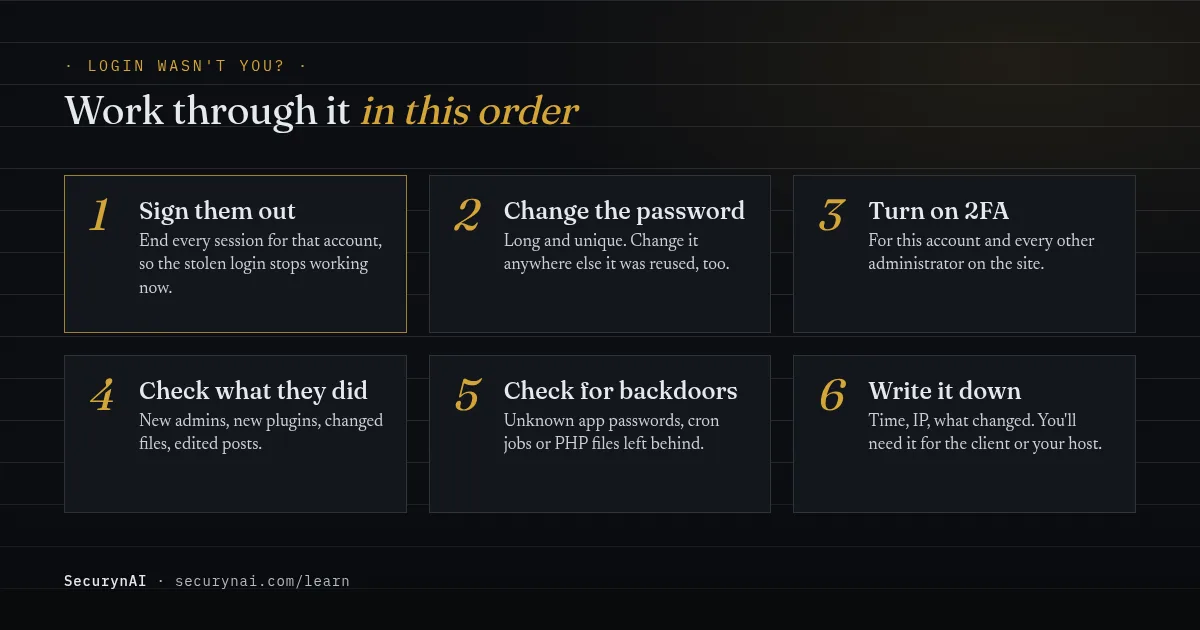
1. Sign the account out everywhere
If it's your own account, open Users > Profile and click Log Out Everywhere Else. The button has been in WordPress since version 4.1, and admins get a similar one when editing another user. From the command line, the WP-CLI session command ends every session at once:
wp user session destroy site-admin --all2. Change the password, then turn on two-factor login
Use a long, unique password, and change it anywhere else it was reused. Then add a second step at login for every administrator. It's the single change that does the most here. Microsoft's 2023 study of its own accounts found multifactor login cut the risk of compromise by 99.22%, and by 98.56% when the password had already leaked.
3. Look for a way back in
A careful intruder leaves something behind before they leave. Check for admin accounts you don't know, unfamiliar application passwords on each admin's profile, new plugins and odd files. Our guides on webshells and rogue cron jobs show where to look.
If you look after the site for a client, write down the time, the IP and anything that changed. You'll need it for the conversation, and our playbook on explaining a hack to a client helps with the wording.
How SecurynAI decides a login looks unusual
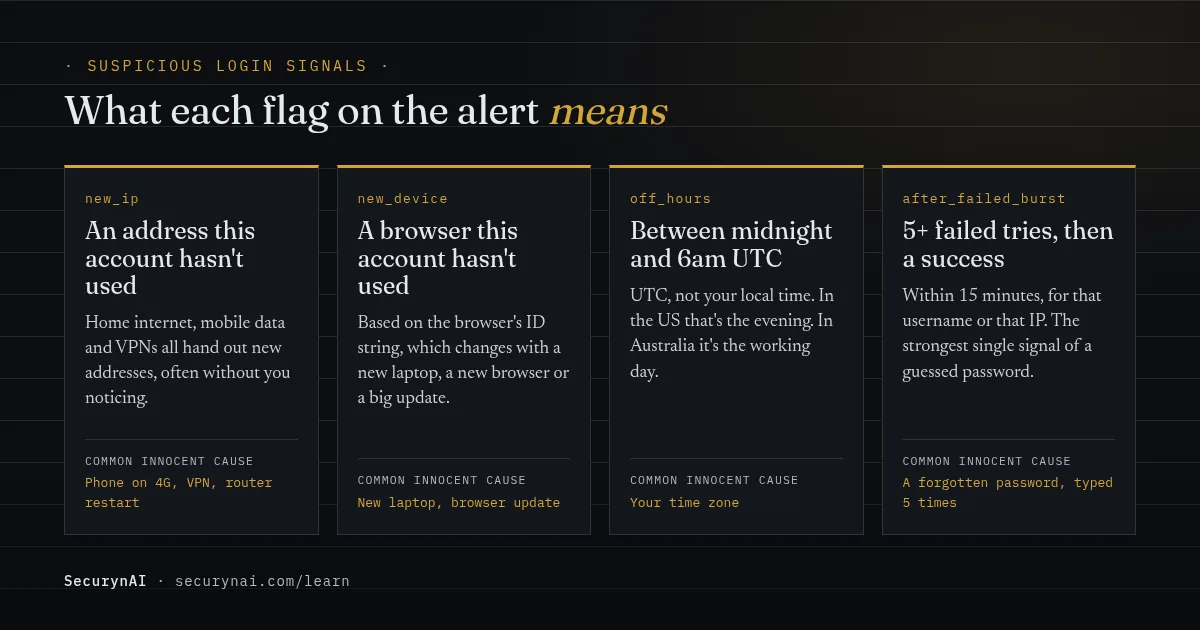
We at SecurynAI don't guess your location in the free plugin. It compares each successful login with that user's past logins and scores four signals. The baseline is the last 50 IP addresses and 50 browsers each user has signed in from. A user's first login after install only sets that baseline.
| Signal on the alert | What it means | Opens a finding on its own? |
|---|---|---|
new_ip | An IP address this user hasn't logged in from | No. It needs a second signal. |
new_device | A browser ID this user hasn't used. A browser update can change it. | No. New IP and new browser together is a medium finding. |
off_hours | Between midnight and 6am UTC, not your local time | No. It only adds weight. |
after_failed_burst | 5 or more failed tries for that username or IP in the 15 minutes before | Yes, as high. With a new IP and browser, critical. |
The check runs on every successful login, not only administrators. Medium and higher findings appear on SecurynAI's Identity page with the score, signals, IP and browser. The free plugin can email the site admin and suggest signing the user out or locking the account. It never changes an account on its own. You approve that step.
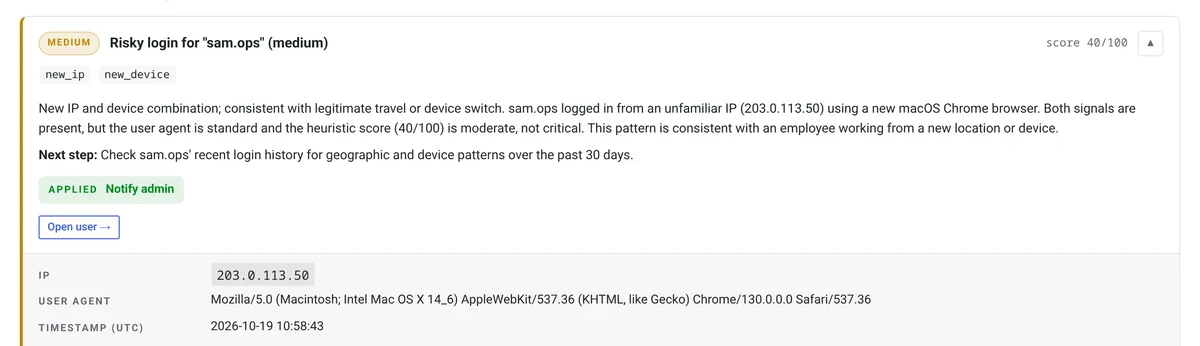
A locked account can be unlocked from the same page. Signing someone out can't be undone, but they can simply log in again. On Pro ($79 per site per year), asking the user to re-verify runs on its own, and signing them out does too when the recommendation is high-confidence. Locking the account always waits for an admin to approve. Pro also adds an impossible-travel check that looks up where each IP is and flags logins too far apart to be real.
Neither version replaces the basics. SecurynAI spots the odd login and tells you what it means. Strong passwords, two-factor login and removing old accounts are what stop the next one. Our guide to securing the login page and the WordPress hardening checklist cover them.
Unusual admin login FAQ
Why did I get a suspicious login alert when it was me?
The usual causes are a new laptop or browser, a browser update, a VPN, or your phone on mobile data. Typing the wrong password five times before getting it right also looks like a guessed password. If the time, browser and IP match something you did, it was you.
Can I trust the city shown for a login?
Treat it as a rough guess. A 2017 study found IP location databases were right about the city no more than about 75% of the time, and a VPN can move you to another country entirely. The country is usually closer, but still not proof of where someone was.
Should I block logins from other countries?
It can cut noise if everyone with an account works from one country. The cost is locking out anyone who travels or uses a VPN, and attackers can use a VPN too. Two-factor login does more to stop a stolen password, so start there. If you do get shut out, see locked out of wp-admin.
Does WordPress record the IP address of each login?
Not as a history. Core WordPress keeps no login log, but each active session stores the IP and browser it started from. You can see them with the WP-CLI command wp user session list, followed by the username.
Want to know which logins were really new, without digging through logs? The free plugin starts learning each user's usual devices from the day you install it.
Install free →