Your host emailed about a flood of requests to xmlrpc.php, or your logs are full of them. Short answer: this is probably bots guessing, not someone inside. Before you block anything, check two things. Does anything on your site use XML-RPC? And does every admin account have a strong, unique password? The rest of this guide shows how.
What is xmlrpc.php, and why do bots attack it?
xmlrpc.php is an older door into WordPress that lets other apps log in and do things remotely. It's how Jetpack connects your site to WordPress.com, and how some mobile apps and remote publishing tools post content. It also handles pingbacks, the notices blogs send each other when they link.
Anything that accepts a username and password can be used to guess one. So bots send login attempts to xmlrpc.php as well as to the normal login page. In a two-week sample, Wordfence counted 108 million attacks on XML-RPC against 106 million on wp-login.php, with 224,461 IP addresses hitting both.
That data is from 2017, but the habit hasn't gone away. Wordfence's 2024 State of WordPress Security report calls password-guessing the most common attack on WordPress sites. It blocked more than 100 billion of these attempts in 2023, from over 74 million IP addresses.
Is the system.multicall trick still a threat?
Much less than it used to be, if your WordPress is up to date. XML-RPC has a method called system.multicall that bundles many commands into one request. In 2015, attackers used it to pack "hundreds or thousands of username/password combinations" into each request, according to SecurityWeek's report on Sucuri's findings.
WordPress closed that gap in version 4.4, through core ticket #34336. Now, once one login fails inside a request, the XML-RPC login code refuses the rest without checking them. A bundle of a thousand guesses gets one real try.
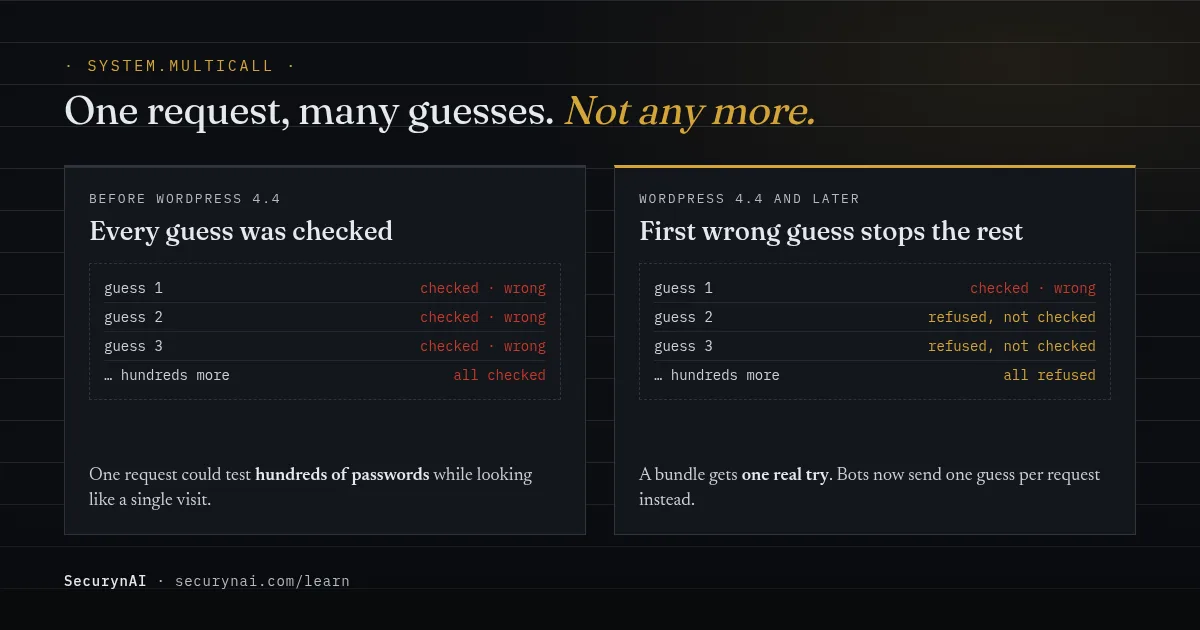
So why do the warnings keep coming? Because bots don't stop. They send one guess per request instead, from many addresses, and every request still makes your server do work. One site owner in a WordPress.org support thread found xmlrpc.php was eating 87% to 98% of the bandwidth on their three busiest sites.
Is an xmlrpc.php attack dangerous?
The attack itself is noise. The danger is a weak password on an account it can reach. Thousands of failed guesses don't hurt you. One correct guess does.
| Probably fine | Worth acting on today |
|---|---|
| Every admin uses a strong, unique password | An admin password is short, old or used on other sites |
| You recognise every administrator account | There's an admin you can't name |
| The site feels normal and nothing changed | The site is slow, or your host says it's using too many resources |
| Your host or a plugin is already throttling or blocking the requests | Every request reaches WordPress and nothing limits them |
If you find an administrator you don't recognise, stop here and follow our guide to a new admin user you didn't create. That's a different, more urgent problem.
Should you disable XML-RPC on WordPress?
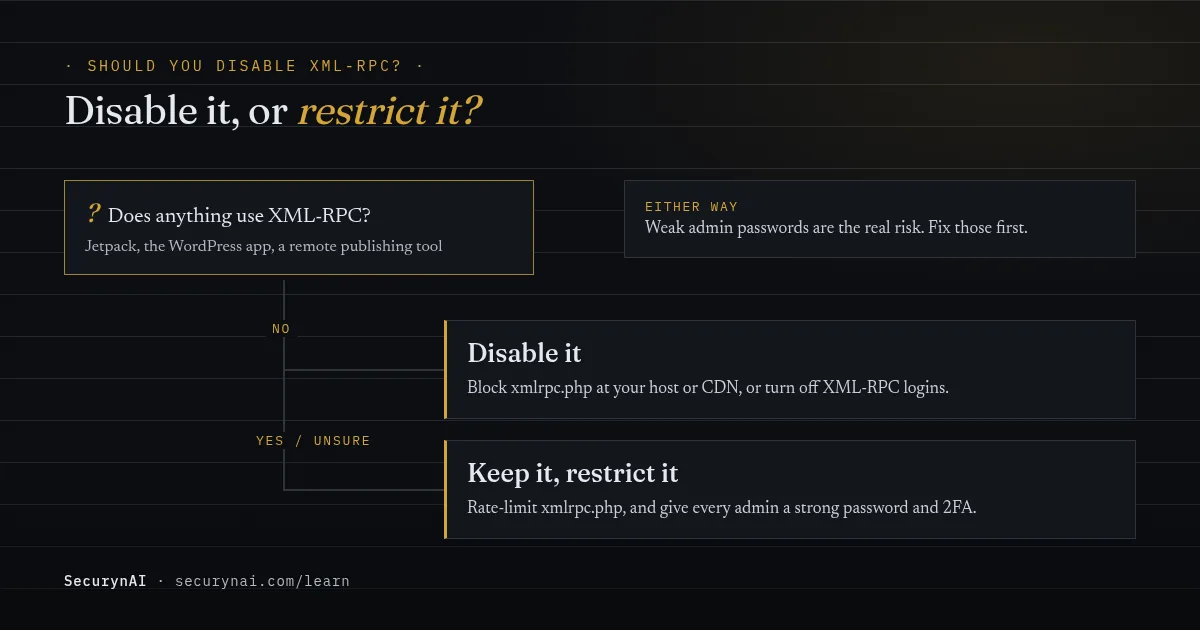
If nothing uses it, yes. If something does, restrict it instead. WordPress's own brute-force guidance says it plainly: "If you don't use XML-RPC, disable it." For sites that need it, such as those using Jetpack or mobile apps, it says to "restrict it (WAF rules) and rate-limit aggressively."
Jetpack is the usual catch. Its support page warns that blocking xmlrpc.php "stops WordPress.com from reaching your site and breaks the Jetpack connection." Hosts sometimes block it by default, too. In one WordPress.org thread, an owner's analytics stopped arriving because the host had blocked the file.
Not sure whether it's open? Visit yoursite.com/xmlrpc.php in a browser. Jetpack's troubleshooting guide says an open file shows "XML-RPC server accepts POST requests only." Here are your options, from heaviest to lightest.
| Option | What it stops | What it breaks |
|---|---|---|
Block xmlrpc.php at your host, CDN or web server | Everything. Requests never reach WordPress, which saves server load. | Jetpack, apps and anything else that uses XML-RPC |
Turn off XML-RPC logins (the xmlrpc_enabled filter) | Password guessing through XML-RPC | Apps and tools that log in through it. Pingbacks keep working. |
| Keep it open, but rate-limit it | Floods from a single address | Nothing, if the limit is sensible |
One detail trips people up. Despite its name, the xmlrpc_enabled filter only "controls whether XML-RPC methods requiring authentication" are on. That covers the login guessing, but it doesn't switch off pingbacks or the file itself.
What to do when xmlrpc.php warnings keep coming
Protect the accounts first, then decide what to do with the file. Passwords matter whichever option you pick, because bots try the normal login page too.
- List your administrators. In the dashboard, go to Users and filter by Administrator. With shell access, WP-CLI does the same:
wp user list --role=administrator. Can you name every one? - Fix weak passwords and add two-factor login. WordPress's docs advise "strong, unique passwords and a password manager" and 2FA for every admin. Core doesn't include 2FA, so you'll need a plugin.
- Pick an option from the table above, once you know what uses XML-RPC. Back up any server config file before you edit it, then test Jetpack or your app.
- If the flood is slowing your site, ask your host to block or rate-limit
xmlrpc.phpat their edge, so the requests never reach WordPress.
Looking after client sites? Our playbook for managing 30+ client sites covers handling alerts like this across a portfolio. For the wider login picture, see how to secure the WordPress login page.
How SecurynAI handles XML-RPC brute force
We at SecurynAI treat XML-RPC as one more way to log in, so it gets the same protection as the login page. Most of this is in the free plugin, with one setting you need to know about.
- Login lockouts (Free). Failed logins through XML-RPC are counted with all the others. After 20 failures in 15 minutes from one IP address, or against one username, the IP is locked out for 30 minutes and you get a high-severity finding. These are the default numbers.
- An xmlrpc.php rate cap (Free). Each IP address gets 30 requests to
xmlrpc.phpper minute. Anything over that is refused until the next minute starts, and tricks like/./xmlrpc.phpare caught. - A hardening check (Free). SecurynAI flags XML-RPC as enabled (medium severity) and lists the manual steps to turn it off, with a reminder to re-test Jetpack or your app.
- One-click disable with undo (Pro). Pro can switch off XML-RPC logins for you and strip the pingback header, and you can undo it in one click if something breaks.
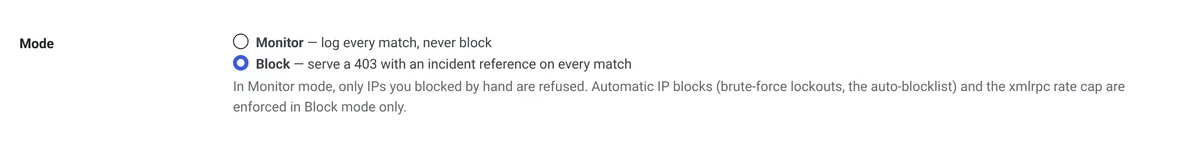
Here's the setting. The firewall starts in Monitor mode, which logs but doesn't block. The xmlrpc.php rate cap only works in Block mode, and so does blocking a locked-out IP across the whole site. In Monitor mode, lockouts still refuse that IP's login attempts. Switch to Block once you've checked the firewall log for false alarms.
We'll be straight about the limits. SecurynAI doesn't replace strong passwords, two-factor login or your host's own protection, and it can't stop requests from arriving. If a flood is hurting your server, a block at your host or CDN is still the right fix. If you're weighing tools, our SecurynAI vs Wordfence comparison sets out the differences.
Quick check: is your site ready for XML-RPC brute force?
- Do you know whether anything on your site uses XML-RPC?
- Can you name every administrator account?
- Does every admin have a strong, unique password?
- Does every admin use two-factor login?
- Is something limiting requests to
xmlrpc.php, whether your host, a plugin or a server rule?
Five yeses means these warnings are just background noise. Two to four is common and quick to fix this week. Fewer than that is a normal starting point, and our WordPress hardening checklist is a good next step. If you're wondering whether a firewall plugin is worth it at all, read do you need a WAF.
XML-RPC brute force FAQ
Is it safe to disable xmlrpc.php?
Yes, if nothing on your site uses it. WordPress's own security docs say that if you don't use XML-RPC, you should disable it. Check for Jetpack, the WordPress mobile app and any remote publishing tool first, and test them afterwards.
Does disabling XML-RPC break Jetpack?
Fully blocking xmlrpc.php does. Jetpack's support docs say blocking it breaks the connection to WordPress.com. If you use Jetpack, rate-limit XML-RPC and protect your admins with strong passwords and two-factor login instead.
Why do I still see xmlrpc.php hits after disabling XML-RPC?
Bots don't know you've turned it off, so they keep sending requests. Those requests now get an error instead of a password check. A block at your host or CDN stops them reaching WordPress at all, which also saves server resources.
Thousands of xmlrpc.php hits: does that mean someone got in?
No. Hits are attempts, not logins. What matters is whether any guess worked, so check your administrator list for accounts you don't recognise and make sure every admin has a strong, unique password.
Seeing xmlrpc.php warnings and want them handled? The free plugin locks out password-guessing IPs and can rate-limit xmlrpc.php once you switch the firewall to Block.
Install free →