Security monitoring, as something you sell, is the recurring work of watching a client's site for attacks, risky changes and vulnerable plugins, and acting on what you find. Working out what to charge for WordPress security monitoring means pricing that work, not the plugin, and fitting it into your maintenance plan pricing.
Picture it (this one's illustrative): a client asks why their care plan went up by $20 a month. If you can answer in one sentence, and the answer is about what you do for them, your price is probably fine. If you can't, keep reading.
What do agencies charge for security monitoring today?
Most agencies don't sell monitoring on its own. Security is usually one part of a monthly care plan, and the published prices reflect that. Here's what we could verify on public pages in October 2026. These are vendor and agency prices, not a market survey, so treat them as reference points.
| Who | What it covers | Published price |
|---|---|---|
| Freshy (US agency guide) | Basic plan: updates, backups, "basic security monitoring" | $30 to $100 a month |
| Wbcom Designs (Aug 2026) | Standard tier: security monitoring, performance checks, monthly report | $99 to $199 a month |
| Help4bis (Australia, Apr 2026) | Care plans with firewall, login protection, malware scanning | $49 to $200 a month (AUD) |
| Sucuri Platform | Monitoring, firewall and unlimited manual cleanups, one site | $229 to $549 a year |
| Wordfence Care / Response | Set-up, monitoring and incident response by their analysts, one site | $590 / $1,250 a year |
Two things stand out. Small-site care plans that include security cluster between about $30 and $200 a month. And when a security company does the cleanup for you, the price per site rises, because someone is on the hook when a site gets hacked.
The pricing worksheet: four numbers per site
Price from the cost up, then sanity-check against the market, never the other way round. Market ranges are wide enough to justify almost any number, so they can't tell you whether you're losing money. Your own costs can. Fill in these four numbers for one typical client site.
1. Your time per site, per month
Count the minutes you'll really spend: reviewing findings, updating flagged plugins, answering the client's "is this bad?" email, and writing a short monthly note. Multiply by what an hour costs you, including overheads.
For a reference point, the US Bureau of Labor Statistics puts median pay for web developers and digital designers at $47.85 an hour (May 2025), before any overheads.
2. Tools per site, per month
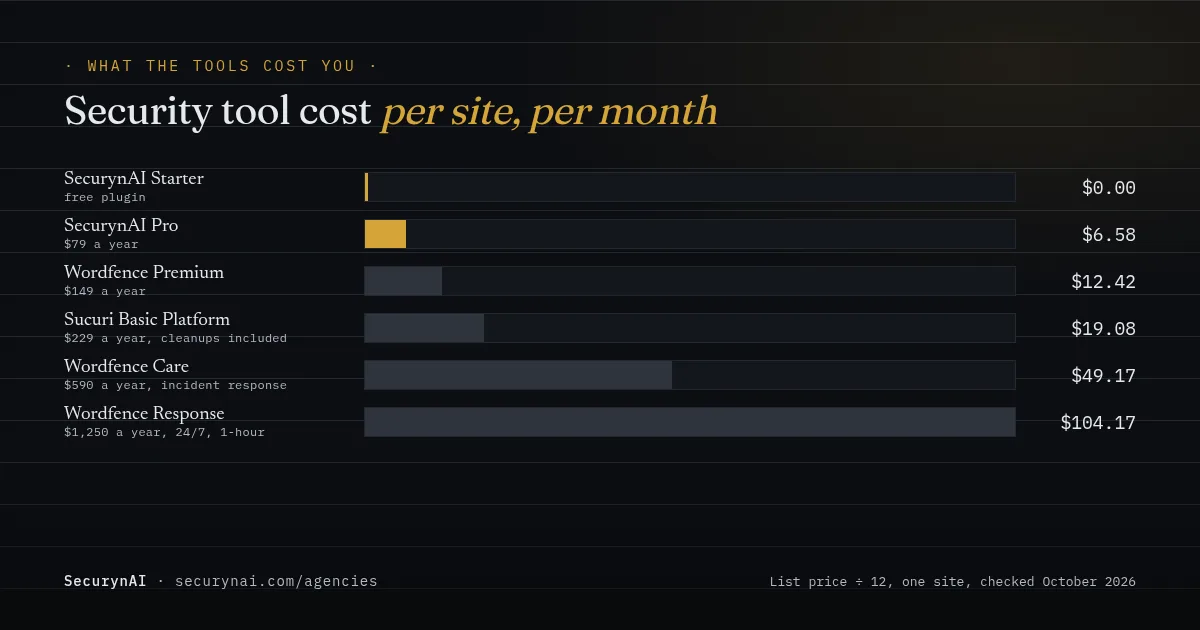
Divide each tool's yearly price by 12. Include the security plugin, any paid vulnerability feed and, if you use AI explanations, the API cost. This is usually the smallest number on the sheet, which is the point: clients pay for your attention, not for a licence.
3. An incident reserve
Some month, a site will need cleaning up. Set money aside for it in every site's price, so that month doesn't wipe out your margin. Help4bis says an emergency cleanup "runs $500 to $2,000" depending on how deep the hack went. Use your own history if you have it; ours below is an assumption.
4. Your margin
Pick the margin you need and divide total cost by one minus that margin. A 40% margin means price = cost ÷ 0.6. Don't skip this step to win a client. Thin security pricing is how monitoring quietly turns into "we'll look at it when we have time."
A worked example (illustrative numbers)
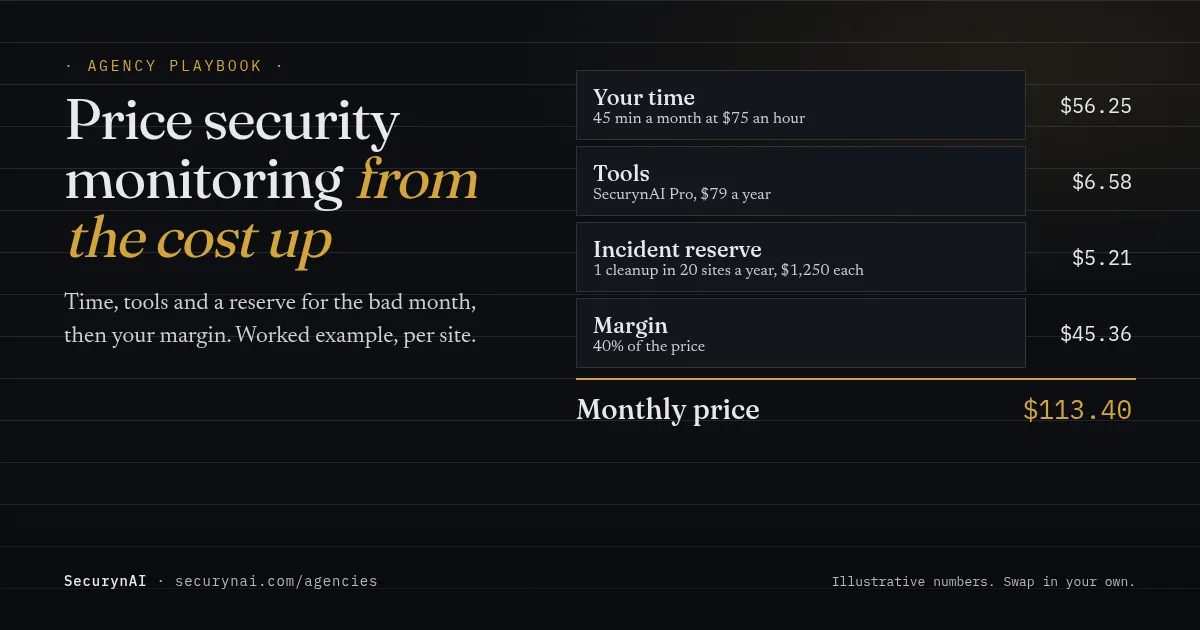
These figures are assumptions, not data from real clients. We rounded the BLS hourly figure up to $75 to cover overheads, and assumed one cleanup a year for every 20 sites, at $1,250 each.
| Per site, per month | "Watch" tier | "Watch and fix" tier |
|---|---|---|
| Your time | 20 min = $25.00 | 45 min = $56.25 |
| Tools | Free plugin = $0.00 | SecurynAI Pro = $6.58 |
| Incident reserve | $0 (cleanup billed hourly) | $5.21 (cleanup included, capped) |
| Total cost | $25.00 | $68.04 |
| Price at 40% margin | $41.67, round to $45 | $113.40, round to $115 |
Both land inside the published ranges above. That's the sanity check doing its job. If your number lands far outside, look again at your time estimate before you look at your price.
Which pricing model fits your agency?
Once you know the number, decide how to show it. For most agencies, a flat add-on or a tier upgrade is easier to defend than pricing per incident.
| Model | Works well when | Watch out for |
|---|---|---|
| Flat add-on per site | Most clients already pay you for maintenance | Clients comparing it with a cheap plugin price |
| Part of a higher tier | You want to move basic-plan clients up | Basic-tier sites still need someone to notice a hack |
| Per incident, cheap monitoring | Very price-sensitive clients | You earn more when sites get hacked, which clients can sense |
The per-incident model has a real tension. If cleanup is where you make money, there's little reason to invest in the monitoring that prevents it. Some clients still prefer it, and that's fine, as long as the contract says exactly what "monitoring" means.
What should a security monitoring fee include?
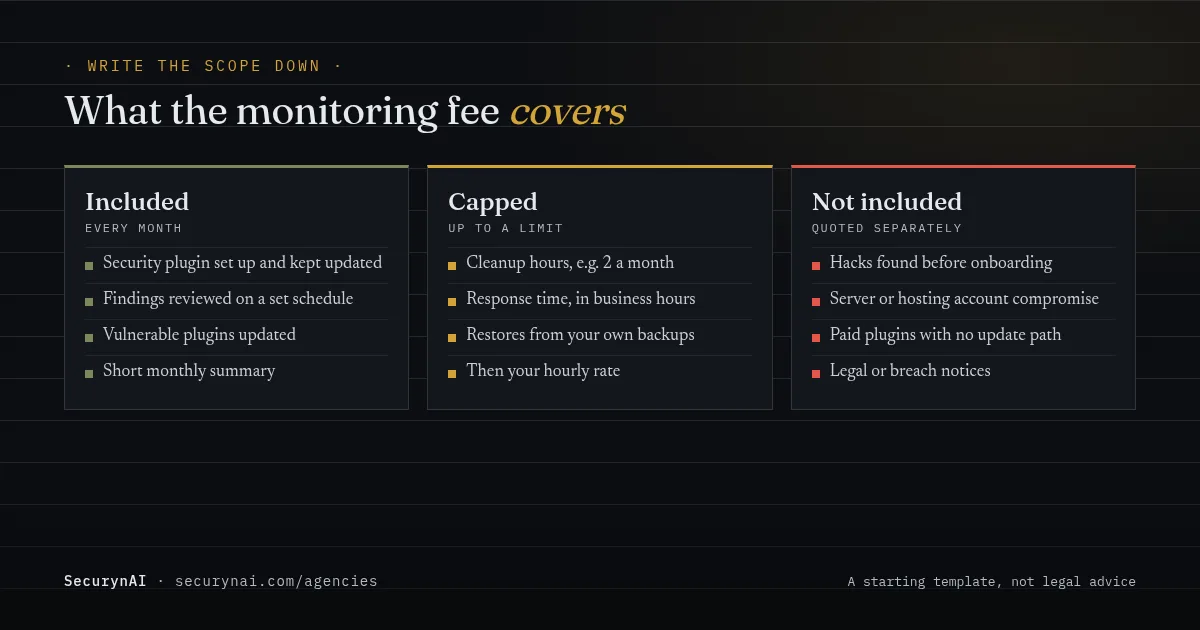
Most pricing arguments are really scope arguments, so write the scope down before you quote. Split it into three columns: what's always included, what's included up to a limit, and what you quote separately.
Updates alone aren't monitoring. Patchstack's State of WordPress Security in 2026 found 11,334 new WordPress vulnerabilities in 2025, and 46% "did not receive a fix from the developer in time for public disclosure." Your scope should say what you do when there's no update yet, for example disable the plugin or ask the client first.
Cleanup is the line to get right. Forum support teams can explain how to clean a site, but not do it. In one WordPress.org thread about a client's compromised store, Wordfence support walked through checks and then pointed to paid cleanup services. Decide in advance whether that cleanup is your job, and for how many hours.
Exclude problems you can't control. In another WordPress.org thread, a site owner on an 11-year-old reseller account saw a freshly reinstalled site reinfected within about 48 hours, and replies pointed at the outdated server rather than WordPress. Server compromise belongs with the host, so say so in writing.
How SecurynAI fits on the cost side
We at SecurynAI built the plugin to cut the "your time" number, mainly by explaining each finding in plain English so triage takes minutes. Each client site runs its own copy of the plugin; there's no central console for all your sites. Budget a few minutes per site to log in and check.
The free plugin (Starter) covers the watching part. It has a firewall that starts in Monitor mode, logging matches until you switch it to Block, plus login lockout, which works in either mode. It runs daily file checks on core, plugin and theme files, and vulnerability alerts for installed plugins.
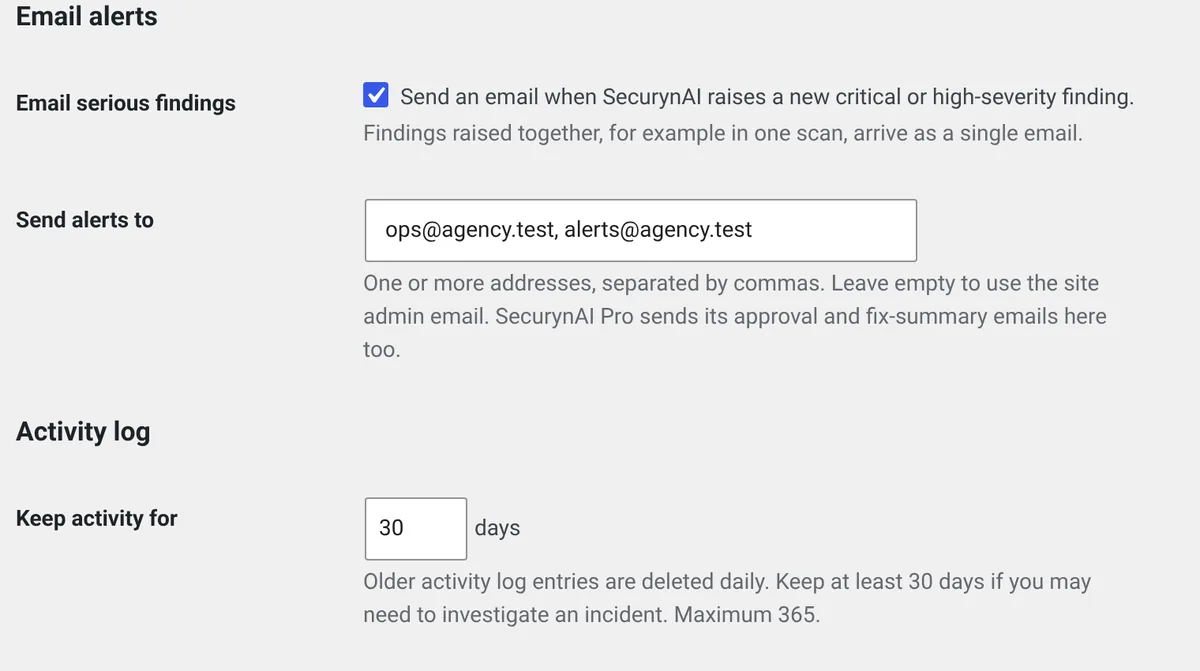
That daily scan also checks every PHP file under wp-content against 13 bundled malware signatures and flags high-confidence obfuscated code. It detects only; it doesn't clean files. The activity log keeps 7 days by default; raise that to 30 or more in Settings in case you need to investigate an incident.
Email alerts are off by default. On every client site, switch on "Email serious findings" in Settings > General and put your agency address in "Send alerts to". Only new critical and high-severity findings are emailed, and findings raised together arrive as one email, so your inbox stays manageable. Medium and low findings still wait for your review.
SecurynAI Pro ($79 per site per year) is what the "watch and fix" tier above assumes. Its Patch Queue ranks vulnerable plugins, and Fix Now updates wordpress.org plugins that have a fixed version. Themes, core and premium plugins show "Manual update required."
In Pro, we send risky fixes to an approval queue first. Critical items are emailed at once, and anything else waiting goes in a daily digest. With an alert address set, those emails go to you rather than the client's administrators.
Pro can also send a daily summary of the fixes it applied, reverted or failed, with one-click revert links; switch it on under Settings > Modules.
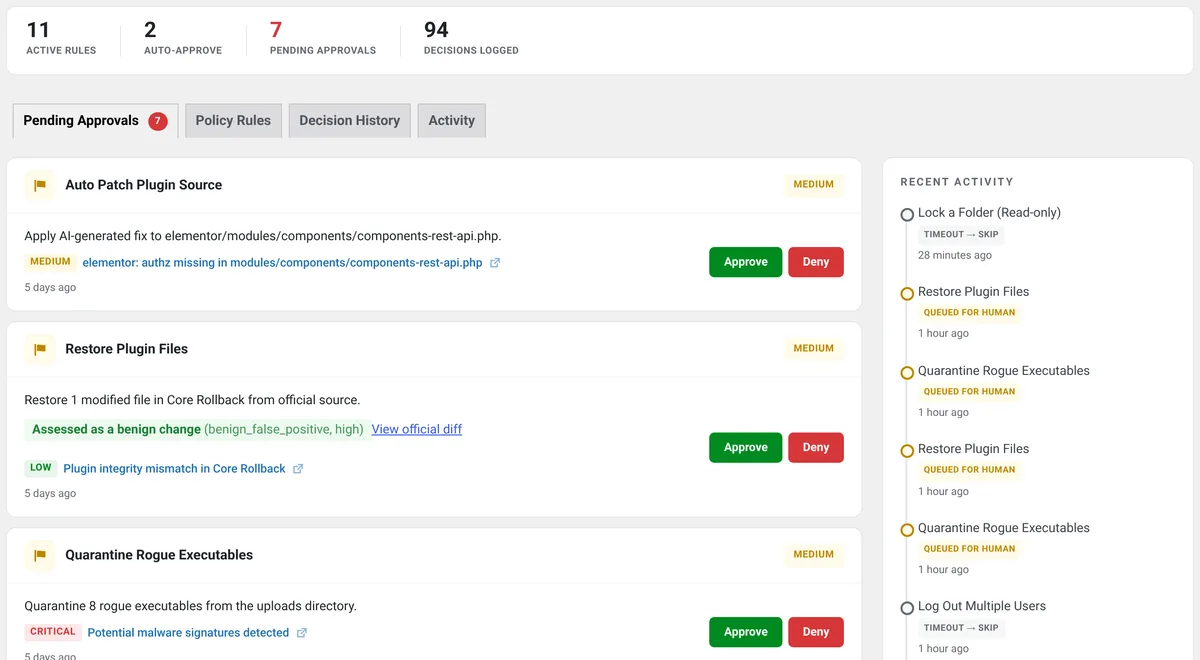
Pro also keeps a 90-day audit archive and can export a ZIP of findings, incidents and decisions mapped to SOC 2, GDPR, PCI DSS or ISO 27001 controls. That's useful evidence for a client who asks what you actually did. Running many client sites? Volume pricing is available on request.
None of this replaces backups, updates or decent hosting, and it won't stop every attack. It helps you notice sooner and explain more clearly, which is what the client is paying for.
How to tell clients about the new price
Lead with what changes for them, not with the number. Offer it to existing clients first as an opt-in, and make it the default for new clients. Here's a short email you can adapt.
Keep the monthly note short and specific: what was checked, what was updated, what needs a decision. Our client security report template gives you a layout, and our guide to security in your maintenance plan covers what the work looks like week to week.
Quick check: is your security monitoring price right?
- Do you know how many minutes a month each site's security takes you?
- Does the price include a reserve for the month a site gets hacked?
- Does the contract say how many cleanup hours are included?
- Does it exclude hacks that were there before the client signed up?
- Could you explain the line item in one sentence to a client?
Five yeses means your pricing will survive a real incident. Three or four is common and quick to fix at the next renewal. Fewer is a normal starting point.
When a cleanup does land, our guides on the real cost of a hack cleanup and removing WordPress malware help you scope it, and the WordPress hardening checklist makes a good onboarding task.
Want to see what findings look like before you price them? Our guides to privilege drift and attack chains show two common alerts, explained. For more on running security across many sites, browse the agency playbooks.
Security monitoring pricing FAQ
Should security monitoring be a separate line item?
It helps. A named line shows the client what they pay for, and it stops security being the first thing squeezed when a plan gets tight. If you'd rather keep one price, make security the clear difference between your basic and higher tiers.
Should hack cleanup be included in a maintenance plan?
Include a capped amount, not unlimited cleanup. A few hours a month covers most small incidents, and anything beyond that goes at your hourly rate. Always exclude hacks that were there before the client signed up.
Can I charge for monitoring if I use a free security plugin?
Yes. The client pays for your time and judgment: reviewing findings, updating what's flagged, and knowing what to do when something looks wrong. The tool cost is only one of the four numbers in your price.
How much should I charge for WordPress maintenance per month?
Published agency prices for basic plans that include security monitoring mostly sit between about $30 and $200 a month, depending on site type and region. Work out your own cost per site first, then check where it lands in that range.
Pricing security across a roster of client sites? See how SecurynAI works for agencies, and ask us about volume pricing.
SecurynAI for agencies →