Security in a WordPress maintenance plan is a written promise: what you check on each client site, how fast you act when a check fails, and what you tell the client afterwards. You don't need a security hire to add it. You need a routine, a few rules decided in advance, and tools that explain what they find.
Here's a simple test. If a plugin on one of your client sites had a known flaw tonight, would your plan catch it before the client did? If the honest answer is "probably, if someone looks," this playbook is for you. It works for a freelancer with eight care-plan clients and for an agency with sixty.
What should WordPress maintenance plan security cover?
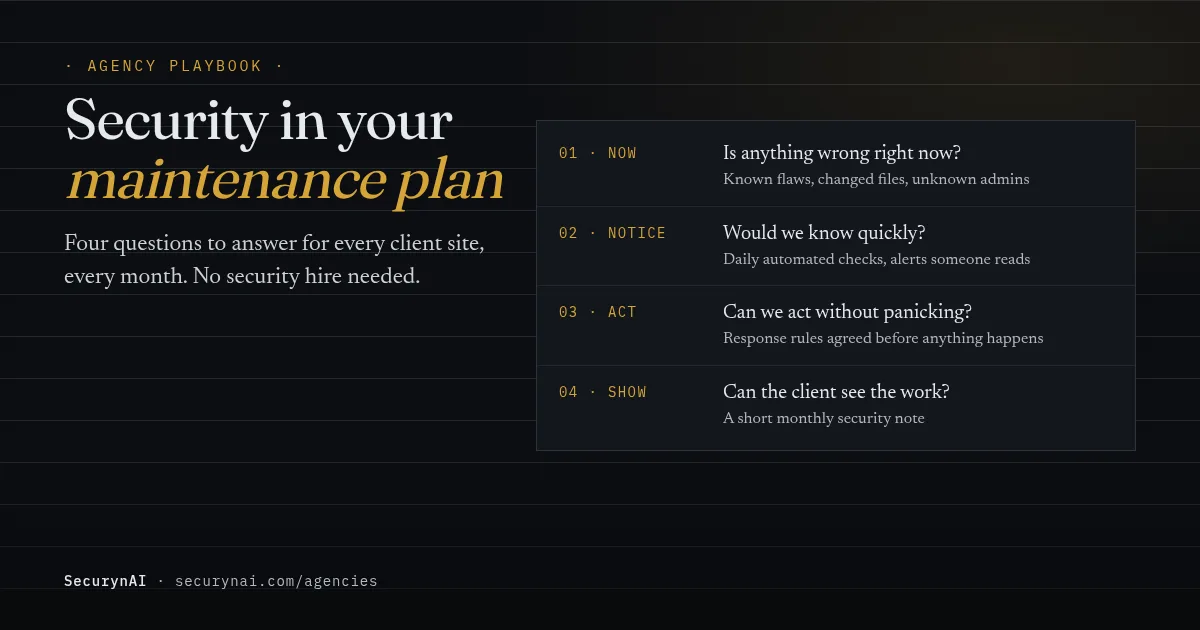
You don't need to become a security firm. You need to answer four questions for every site, every month.
- Is anything wrong right now? A plugin with a known flaw, a changed core file, an admin nobody recognises.
- Would we know quickly if something went wrong? Checks that run daily, and alerts that reach a person who reads them.
- Can we act without panicking? Rules, agreed in advance, for who does what and how fast.
- Can the client see the work? A short monthly note in plain words, not a dashboard screenshot.
Updates alone don't answer the first two questions. Patchstack's State of WordPress Security in 2026 report counted 11,334 new WordPress vulnerabilities in 2025, with 91% in plugins. It found that 46% had no developer fix by the time they were made public.
Timing matters too. The same report puts the weighted median time to mass exploitation of heavily exploited flaws at 5 hours. A monthly update round can't keep pace with that on its own, so the plan needs daily checks that someone reads. That's the real gap between "we keep things updated" and security coverage.
Your maintenance plan security checklist, by cadence
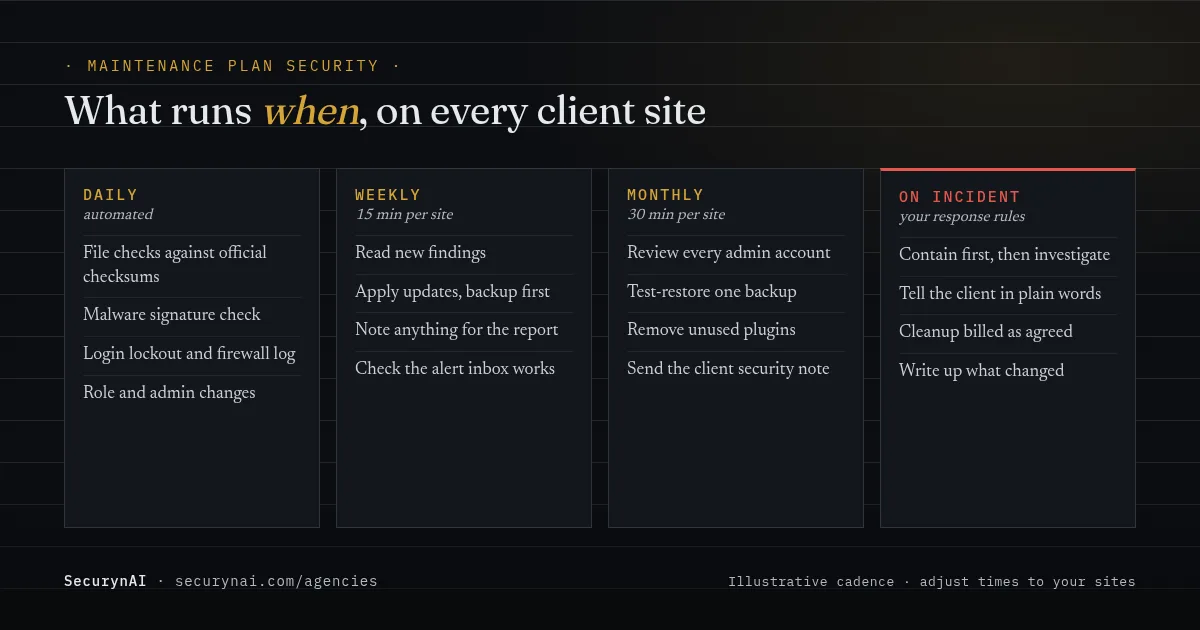
Split the work by how often it needs doing, and most of it becomes routine. Daily checks should be automated. Weekly and monthly tasks are short, human and billable. The times below are an illustrative starting point; time your own sites for a month and adjust.
Daily (automated)
- Check core, plugin and theme files against official checksums.
- Check installed plugins, themes and core against a vulnerability feed, as often as your tool allows.
- Log failed logins and lock out password guessing.
- Flag new administrators and role changes.
Weekly (about 15 minutes a site)
- Read every new finding, and mark each one as act, schedule or dismiss.
- Apply updates. Back up first, and check the site afterwards.
- Write one line for the monthly note about anything you fixed.
- Confirm alert emails still arrive.
That last item catches more agencies out than you'd think. In one WordPress.org support thread from 2024, a site owner on SiteGround stopped getting security login alerts. Other users reported the same problem, and the thread closed without a confirmed fix. An alert that never arrives is the same as no alert. Send mail through SMTP and test it.
Monthly (about 30 minutes a site)
- Review every administrator account and remove the ones nobody can justify.
- Test-restore one backup to staging, not just "backup completed".
- Remove plugins and themes that are deactivated or unused.
- Send the client their security note.
If you have SSH access, these read-only WP-CLI commands cover the monthly look in a minute per site. They change nothing.
wp core verify-checksums
wp plugin verify-checksums --all
wp plugin list --update=available --fields=name,version,update_version
wp user list --role=administrator --fields=user_login,user_email,user_registered
The first two compare files against WordPress.org's official copies. Premium plugins aren't on WordPress.org, so there's no official copy to compare them with. Our guide to a core file that was silently altered explains what to do when a check fails.
Decide your response rules before anything happens
The worst time to decide who handles a hacked site, and who pays, is while it's hacked. Write your response rules once, put the short version in the contract, and use the same rules on every site.
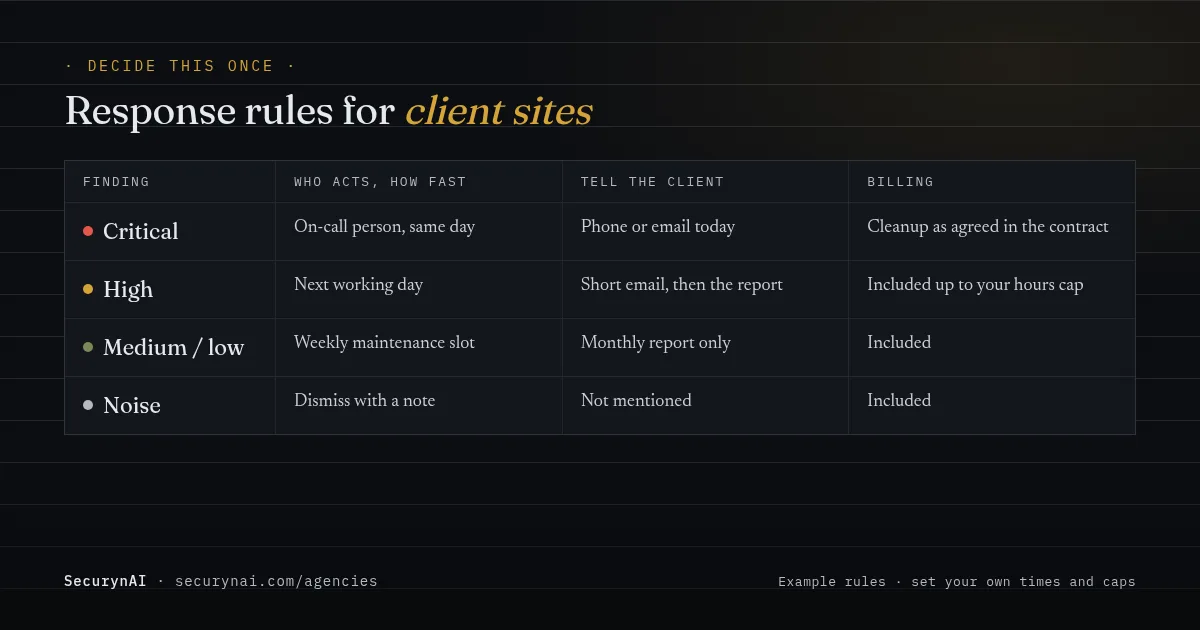
The table above is an example, not a standard. A brochure site and a busy WooCommerce store deserve different response times. What matters is that you set them in advance, and that the client signs off on them.
Decide where cleanup sits
Cleanup is the expensive part, and it's where plans go wrong. You have three honest options: include it with an hours cap, price it separately at your hourly rate, or pass it to a specialist service. Our guide to the real cost of a hack cleanup helps you choose.
If you pass it on, know what specialist cover costs. We checked these on the vendors' own pages in October 2026:
| Service | Price | What's included |
|---|---|---|
| Wordfence Care | $590 a year | They set up and monitor Wordfence; incident response included |
| Wordfence Response | $1,250 a year | 24/7 incident response, 1-hour response time |
| Sucuri platform | $229 to $549 a year, one site per plan | Unlimited manual cleanups; malware removal response estimate from 30 hours down to 6 hours, depending on plan |
Whichever you choose, write it down. "Cleanup is billed at our hourly rate after the first two hours" is a fine policy. Silence is not, because the client will assume it's free. Our incident-response retainer playbook covers the paid-on-standby version.
How do you show clients the security work?
Good security work is invisible, so you have to make it visible. Phil Storey puts it bluntly in a Glow blog post on care plans: "if you just rely on that and don't do anything to prove value, your clients will eventually leave."
He's just as firm on reports: "You should always send reports to your clients, even if they don't read them." Andre Gagnon of SureFeedback made the related point in a 2020 post: clients "don't see the value, because they don't understand it." The fix is to explain the work, briefly.
A monthly security note you can copy
Keep it to five lines. Here's a template; swap in your real numbers.
Status: no open security issues. (Or: 1 issue in progress, see below.)
Checked daily: files, known plugin flaws, logins, admin accounts.
Fixed this month: updated 6 plugins, 2 of them for known security flaws.
Blocked: 214 password-guessing attempts; no accounts affected.
Next month: we'll remove 2 unused plugins and review admin access.
No jargon, no CVE numbers unless the client asks. If something did happen, say what, what you did, and what changes now. Our playbook on explaining a hack to a client has the wording for that conversation.
One practical catch: many tools keep logs for a short time. Copy the numbers you need into the note weekly, so nothing has expired by month-end. For a fuller layout, see the client security report template.
Pricing security into the plan: a worked example
Price the time, not the fear. The figures below are an illustrative worked example with stated assumptions, not market rates. Put in your own hourly rate and your own timings.
| Line | Assumption | Per site per month |
|---|---|---|
| Weekly review | 15 min × 4 weeks = 1 hour at your rate (say $R) | 1 × R |
| Monthly review and note | 30 min | 0.5 × R |
| Tooling | SecurynAI Starter is $0; Pro is $79 a year | $0 to about $6.60 |
| Incident buffer | Your choice, e.g. 0.5 hour per site | 0.5 × R |
At an assumed $R of $80 an hour, that's about $160 to $167 of cost per site per month before margin. Your numbers will differ, and they should. Our guide on what to charge for security monitoring covers tiering and margins in depth.
Where SecurynAI fits in a maintenance plan
We at SecurynAI built the plugin for exactly this job: daily checks that explain themselves, so the person doing maintenance doesn't need a security background. It runs on each site separately. There's no central console across client sites, so you review each site in its own wp-admin.
What the free plugin covers
The free Starter plugin covers most of the automated list above. Every day it checks core, plugin and theme files against official checksums. The same scan checks every PHP file under wp-content against 13 bundled malware signatures, and flags high-confidence obfuscation such as a decoder fed into eval. It detects only and doesn't clean files.
It also locks out password guessing and flags new admins and role changes. Its vulnerability feed syncs every 4 days by default; you can set it to daily in Settings.
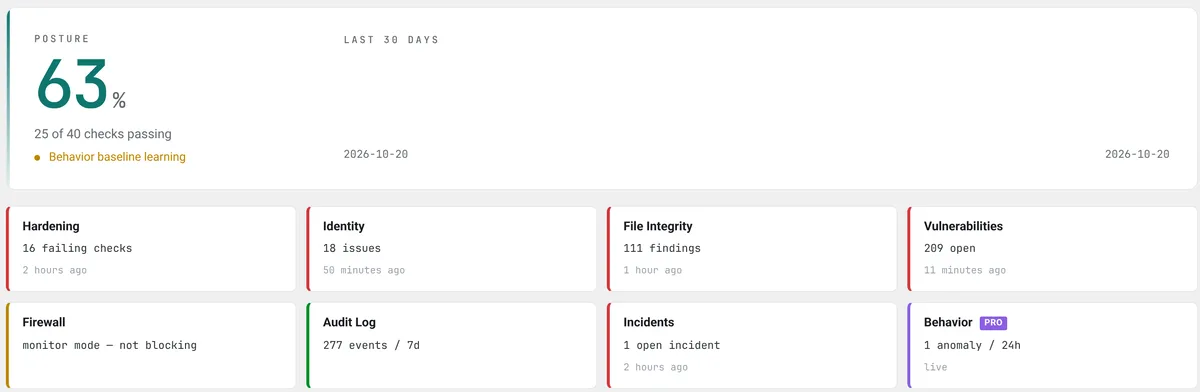
Its runtime firewall starts in Monitor mode. It logs matching requests without blocking them until you switch it to Block, so you can check a client site for false positives first. Login lockout works in either mode. The dashboard shows a hardening score with a 30-day trend, which is handy for the monthly note.
Limits to plan around
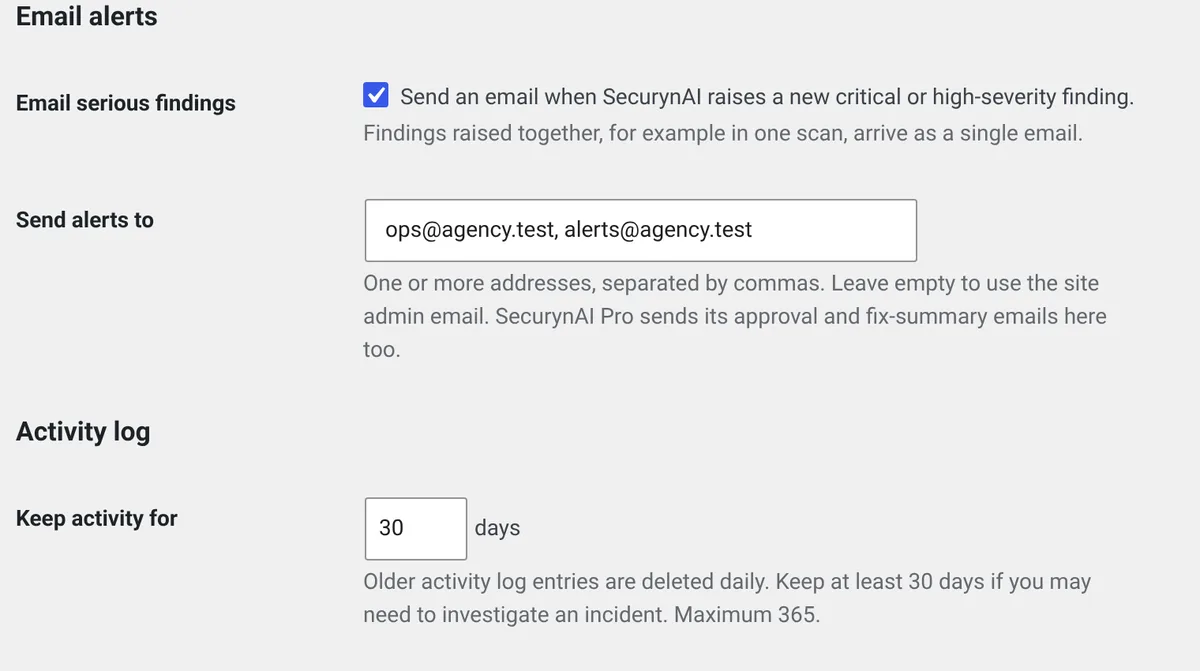
Two settings to change on every client site. In Settings > General, switch on email alerts and put your agency address in "Send alerts to". Alerts are off by default and cover only new critical or high findings. Findings from one scan arrive as a single email, so your inbox stays usable across many sites.
Then raise "Keep activity for" from its 7-day default to 30 days or more, so you can look back after an incident. Medium and low findings still show only in wp-admin, so keep the weekly review and copy what you need into the note.
None of this replaces backups, updates or good hosting. The plugin finds and explains. Your plan is the promise that someone acts.
What Pro adds for agencies
Pro ($79 per site per year) adds what helps at scale. Its Patch Queue ranks known flaws, and Fix Now updates WordPress.org plugins that have a fixed version. Themes, core and premium plugins show "Manual update required". By default those updates run on their own.
If you'd rather review each update, set that rule to queue for approval. Pro also keeps a 90-day activity log.
Pro emails pending approvals: critical ones straight away, the rest in a daily digest. Once your agency address is set in Email alerts, these go there instead of to every administrator, so client admins don't get them. Without an address, they go to the site's administrators.
You can also switch on a daily summary of the fixes Pro applied, reverted or failed, with one-click revert links, in Settings > Modules. It's off by default. If you look after many sites, the Agency Ops page explains bulk pricing, which we quote on request.
Quick check: is security really in your maintenance plan?
- Does every client site run automated checks every day?
- Have you tested, this month, that alert emails actually arrive?
- Are your response times and cleanup terms written in the contract?
- Can you name the person behind every administrator account on every site?
- Does each client get a short security note every month?
- Have you restored a backup in the last 90 days?
Five or six yeses means security is a real part of your plan. Three or four is common and fixable within a month. Fewer is a normal starting point. Begin with the WordPress hardening checklist and our guide to automatic updates, then work through the list above. For more agency workflows, browse the agency playbooks.
Maintenance plan security FAQ
Should security be a separate line item or part of the maintenance plan?
Either works, as long as the plan says what's covered. Many agencies include monitoring and routine response in every tier, then price cleanup separately or cap it by hours. What matters is that the client can read the scope and know what happens if something goes wrong.
Is installing a security plugin enough for a maintenance plan?
No. A plugin checks and logs, but someone still has to read the findings, apply updates, test backups and talk to the client. The plugin is the tool. The plan is the promise that a person acts on what it finds.
Who is responsible if a site on my maintenance plan gets hacked?
That depends on your contract, which is why the scope matters. Write down what you monitor, how fast you respond, and whether cleanup is included. This is general information, not legal advice, so have your agreement checked if you're unsure.
Do I need a security specialist to offer security in my plans?
Not for routine work. Detection, updates, account reviews and plain-English reporting are within reach of any WordPress developer with the right tools. Keep a specialist or a cleanup service in your back pocket for the rare complex incident, like the multi-step break-ins in our attack chain guide.
Building security into your maintenance plan? Try SecurynAI free on one client site this week and see what your weekly review would look like.
Install free →