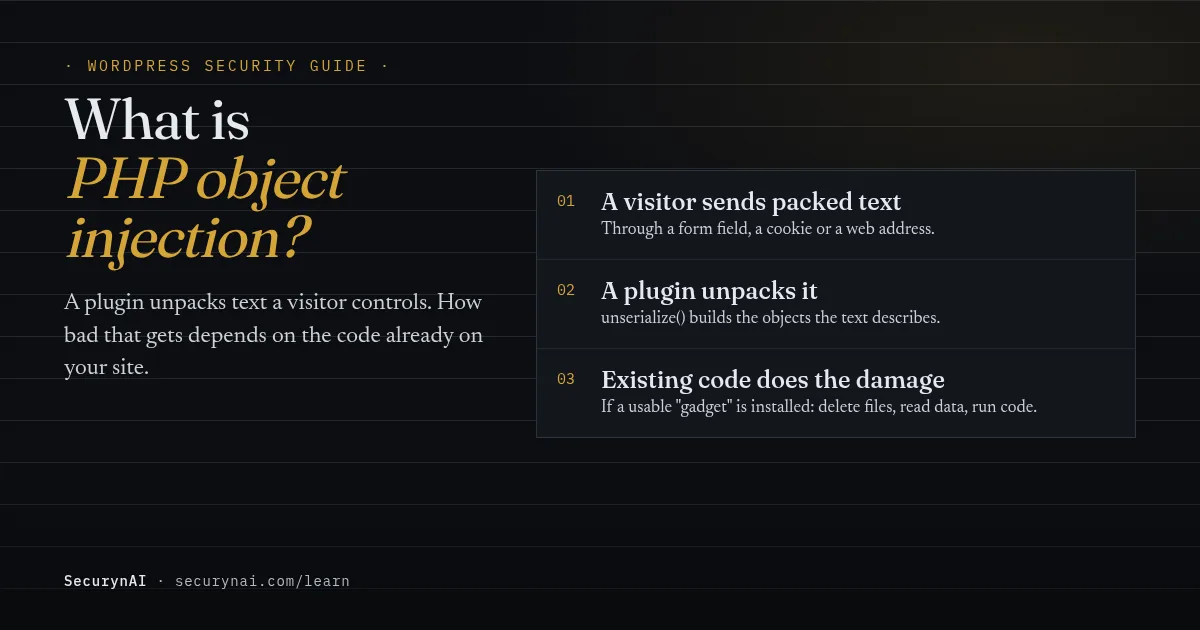
PHP object injection is a flaw where a WordPress plugin unpacks text that a visitor controls, letting that visitor decide which PHP objects your site builds. It's also called insecure deserialization. On its own it often does little, but combined with the right code elsewhere on the site, it can delete files, expose data or run an attacker's code.
If you're here because a plugin advisory or a security alert mentioned PHP object injection, here's the safe first step. Update that plugin to the fixed version the advisory names, or deactivate and delete it if there's no fix yet. Then check your Users screen for administrators you don't recognise. The rest of this guide explains why.
First, what serialization means, and why WordPress uses it
Serialization is just packing data into text so it can be stored and unpacked later. PHP's serialize() turns a list or an object into a single string. Its partner, unserialize(), turns that string back into the original thing. WordPress stores many plugin settings and widget options this way in the database.
A packed list looks something like this, purely as an illustration:
a:2:{i:0;s:5:"apple";i:1;s:6:"banana";}That reads as "an array of 2 items: a 5-letter string, apple, and a 6-letter string, banana." Nothing dangerous there. The catch is that the same format can describe an object, a bundle of code and data, and unserialize() will build it. That's fine when your own site wrote the text, and risky when a visitor did.
How PHP object injection works, in plain English
The bug is a plugin trusting packed text it didn't create. It might read it from a form field, a cookie or a web address, then pass it straight to unserialize(). Now the visitor, not the plugin, chooses what gets built, including objects of any class the site has loaded.
Building an object sounds harmless. But some PHP classes contain "magic methods" that run on their own, for example when an object is unpacked or when PHP throws it away at the end of a request. Security researchers call a class like that a gadget.
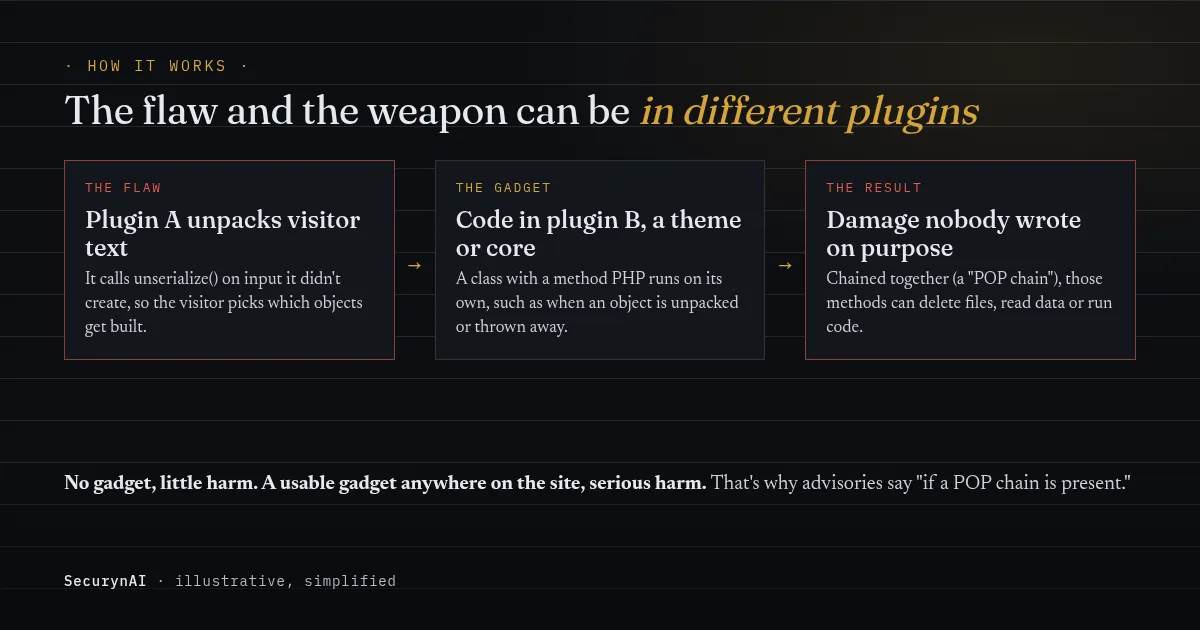
If an attacker can build objects of the right gadget classes, with property values they chose, those automatic methods can be chained into something the original developers never intended. That chain is called a POP chain, short for property-oriented programming. Typical results are deleting a file, reading private data or running code.
The odd part is that the flaw and the weapon often live in different places. The vulnerable plugin only does the unpacking. The gadget can sit in a completely unrelated plugin, your theme or WordPress core. That's why the same advisory can be minor on one site and critical on another.
If you write or commission custom code
The fix on the developer side is simple: never pass visitor input to unserialize(). The PHP manual says not to, "regardless of the options value of allowed_classes," and to use "a safe, standard data interchange format such as JSON" instead. OWASP's Deserialization Cheat Sheet gives the same advice for PHP.
// Unsafe: the visitor chooses which objects get built
$prefs = unserialize( wp_unslash( $_COOKIE['my_prefs'] ) );

// Safe: JSON can only describe plain data, never objects
$prefs = json_decode( wp_unslash( $_COOKIE['my_prefs'] ), true );
WordPress's own maybe_unserialize() calls unserialize() underneath, so it isn't a safe substitute for visitor input. Ask your developer to search the code for both and confirm each one only reads data the site wrote itself.
Why "no known POP chain" doesn't mean safe
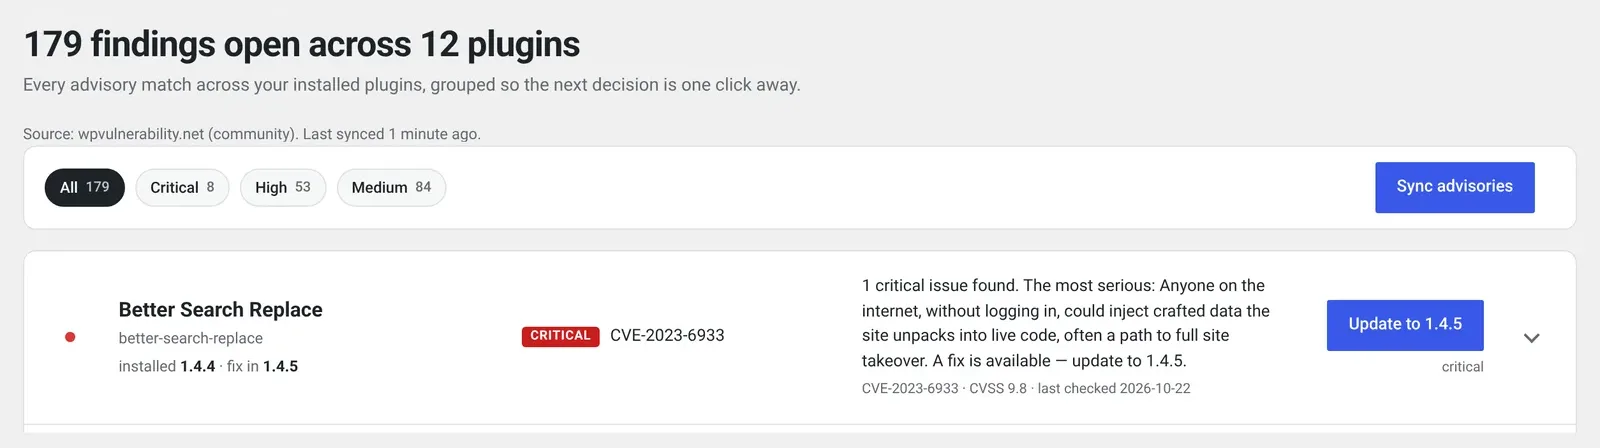
Many object injection advisories say the plugin has no gadget of its own. That's about the plugin, not about your site. Better Search Replace, a database tool with more than a million active installs on WordPress.org, is the textbook case.
Its flaw, CVE-2023-6933, affected every version up to 1.4.4 and needed no login. The NVD record says "No POP chain is present in the vulnerable plugin," but if one is present "via an additional plugin or theme," an attacker could "delete arbitrary files, retrieve sensitive data, or execute code." NVD scores it 9.8 out of 10. Version 1.4.5 fixed it.
Gadgets can even sit in WordPress core. The WordPress 6.4.2 release in December 2023 fixed "a Remote Code Execution vulnerability that is not directly exploitable in core," noting "a potential for high severity when combined with some plugins." In other words, core had a piece an object injection bug elsewhere could use.
A real example: GiveWP, and why one update wasn't enough
GiveWP shows the worst case: a gadget inside the same plugin. The donation plugin, with more than 100,000 active installs, had CVE-2024-5932 in every version up to 3.14.1. Per the NVD record, unauthenticated attackers could inject an object through a donation form field, and "the additional presence of a POP chain allows attackers to execute code remotely."
Version 3.14.2 fixed it in August 2024. Then researchers found a way around that fix. CVE-2024-8353 describes "essentially the same vulnerability" in versions up to 3.16.1, "mostly patched in 3.16.1," with "further hardening" in 3.16.2. Sites that updated once and then stopped were exposed again.
Attackers noticed. Patchstack's State of WordPress Security in 2026 lists the GiveWP flaw, "PHP Object Injection to RCE," at number 6 in its "Top vulnerabilities of all time exploited in 2025." The lesson isn't "update once." It's "keep updating," because a first fix isn't always the last.
Is PHP object injection serious on your site? How to read the advisory
Two words in the advisory tell you most of what you need: who can trigger it, and whether a POP chain exists. Speed matters too. The same Patchstack report puts the weighted median time to first exploit for heavily targeted flaws at 5 hours, and says "the first 24 hours are critical."
| The advisory says | What it means | Do this |
|---|---|---|
| Unauthenticated, POP chain present | Anyone can try it, and the weapon ships with the plugin | Update today, or remove the plugin |
| Unauthenticated, no known POP chain | Harm depends on gadgets elsewhere on your site | Update today anyway |
| Needs a login (Subscriber, Contributor) | Risky if strangers can register | Update this week, sooner if sign-ups are open |
| Needs an administrator | An attacker would already need admin access | Update in your normal cycle |
| No fix released | Nothing to update to yet | Deactivate and delete, or replace it |
When a fix exists, updating really is the whole answer for site owners. In a 2026 WordPress.org thread about a cookie-consent plugin flagged for PHP object injection, the developer's reply was: "Simply updating the plugin will fix the vulnerabilities."
Sometimes the alert reaches you before the developer has acted. In a thread about a timetable plugin, support first said there were "no details about it" on the advisory, then shipped 2.4.14, "which resolves the PHP Object Injection vulnerability." In another thread, an activity-log plugin's developer said "we were never contacted," then released 5.3.3 with the fix.
So if an advisory has no fix yet, a short wait for the developer is reasonable, provided only an administrator can trigger the flaw. If anyone can, deactivate the plugin until a fix lands. Our guide on how to read a CVE explains the scores in more detail.
How to protect a WordPress site from PHP object injection
You can't audit for gadgets yourself, so the practical defence is fewer flaws and less code. In order of impact:
- Keep core, plugins and themes updated, and keep doing it after the first fix, as GiveWP showed. Our guide to automatic updates covers the trade-offs.
- Delete plugins and themes you don't use. That removes possible entry points and possible gadgets. A deactivated plugin's files are still on the server until you delete it.
- Find out the day a plugin you run gets an advisory, through a vulnerability feed or alert service, not weeks later from a changelog.
- Keep registration closed unless you need it. Flaws that need a Subscriber login are open to anyone if anyone can sign up.
- Treat a firewall as a second layer. Whether it helps depends on its rules, covered below. Our guide on whether you need a WAF explains the types.
If you think a flaw was already used, back up the site as it is now before changing anything. Then follow our guide to removing WordPress malware. Code execution often ends with a backdoor file, which our guide to webshells explains.
What SecurynAI does about PHP object injection, and what it can't
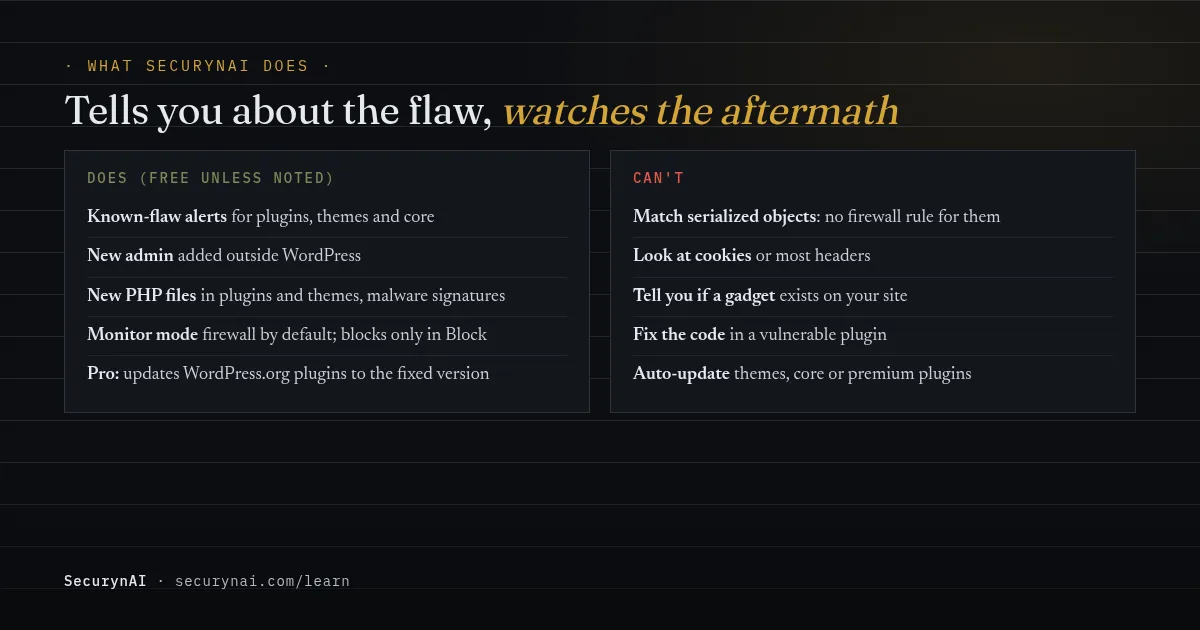
We at SecurynAI can tell you about the flaw and watch for what an attacker does next, but our firewall won't catch the injection itself. The real fix is the plugin update. Here's exactly where the plugin helps, and where it stops.
Known-flaw alerts, in plain words
The free plugin checks your plugins, themes and WordPress version against the wpvulnerability.net feed every 4 days by default (you can set 1 to 30 days in Settings), and again after you update a plugin, a theme or WordPress itself.
For an object injection advisory that needs no login, the built-in explanation reads: "Anyone on the internet, without logging in, could inject crafted data the site unpacks into live code, often a path to full site takeover." Advisories titled "Deserialization of Untrusted Data" get the same wording. It names the fixed version when the advisory lists one.
Email alerts for critical and high findings are off until you turn them on in Settings.
The free firewall has no rule for serialized objects
Plainly: none of the free firewall's 13 rules looks for a serialized object, so an object injection payload passes through unless it also happens to contain another attack pattern. The rules also don't read cookies, a common place for plugins to keep packed data, or request headers other than the user agent.
One rule overlaps slightly: "PHP stream wrapper" flags phar:// and similar addresses in a web address or form field, which some object injection attacks rely on. The firewall starts in Monitor mode, logging matches without blocking until you switch it to Block.
Catching what an attacker does next
Free checks look for the usual results of a successful attack:
- A new administrator added outside WordPress, for example written straight into the database, raises a critical finding on the next daily scan.
- A new PHP file inside a plugin or theme whose version didn't change is reported as file drift.
- Known malware patterns: the daily file scan checks every PHP file under wp-content against 13 bundled signatures and flags high-confidence obfuscation. It detects only; it doesn't clean files.
- PHP files in uploads raise a high finding, and a change to the Site URL or Home address does too.
What Pro adds
On Pro ($79 per site per year), the Patch Queue ranks flaws by risk. A seeded rule updates a WordPress.org plugin in the "Fix now" band to the fixed version without waiting for approval, unless you set it to wait.
It snapshots the plugin first and rolls back if the update fails or leaves the plugin's main file broken. Themes, core and premium plugins show "Manual update required".
With your own AI key, Pro can also read part of a plugin's code and flag unsafe deserialization, with file and line. That's a pointer for a developer, not proof a gadget exists. Pro can quarantine malware-signature hits, waiting for your approval by default, but it won't move files belonging to an installed plugin or the active theme.
Here's what neither version does. SecurynAI doesn't fix the flawed code in a plugin, can't tell you whether a usable gadget exists on your site, and doesn't replace backups, updates or good hosting.
Quick check: is your site exposed to PHP object injection?
- Are all plugins and themes on their latest versions?
- Have you deleted plugins and themes you don't use?
- Would you hear about a new advisory for a plugin you run within a few days?
- Is user registration closed, or do you know why it's open?
- Can you name every administrator account on the site?
- Would you notice a new PHP file appearing inside a plugin folder?
Six yeses is a solid baseline. A no on the first question is the one to fix today. For the rest, our WordPress hardening checklist is the next step, and our guide to SQL injection covers the other common way plugin bugs reach your data.
PHP object injection FAQ
Is PHP object injection the same as insecure deserialization?
Yes, for practical purposes. Insecure deserialization is the general name, used across languages, and PHP object injection is what it's called when PHP's unserialize() is the function at fault. Advisories may also call it "deserialization of untrusted data". The advice is the same: update the plugin.
The advisory says "no known POP chain". Can I ignore it?
No. It means the vulnerable plugin doesn't carry a gadget of its own, not that your site has none. Another plugin, your theme or an older WordPress version could supply one. Update anyway; it's usually a few minutes of work.
Does a firewall stop PHP object injection?
Sometimes, if it has rules for serialized objects and inspects the part of the request the plugin reads, such as a cookie. Not every firewall has one, and SecurynAI's free firewall doesn't. Treat any firewall as a second layer behind updating.
Doesn't WordPress itself use serialized data?
Yes. WordPress stores many settings as serialized text and unpacks them when it reads them back. That's normally safe because the text was written by your own site. The danger starts when a plugin unpacks text that a visitor can change.
Want to hear, in plain English, the day a plugin you run gets a PHP object injection advisory, and notice if someone adds an admin or a PHP file afterwards? The free SecurynAI plugin does both from the day you install it.
Install free →