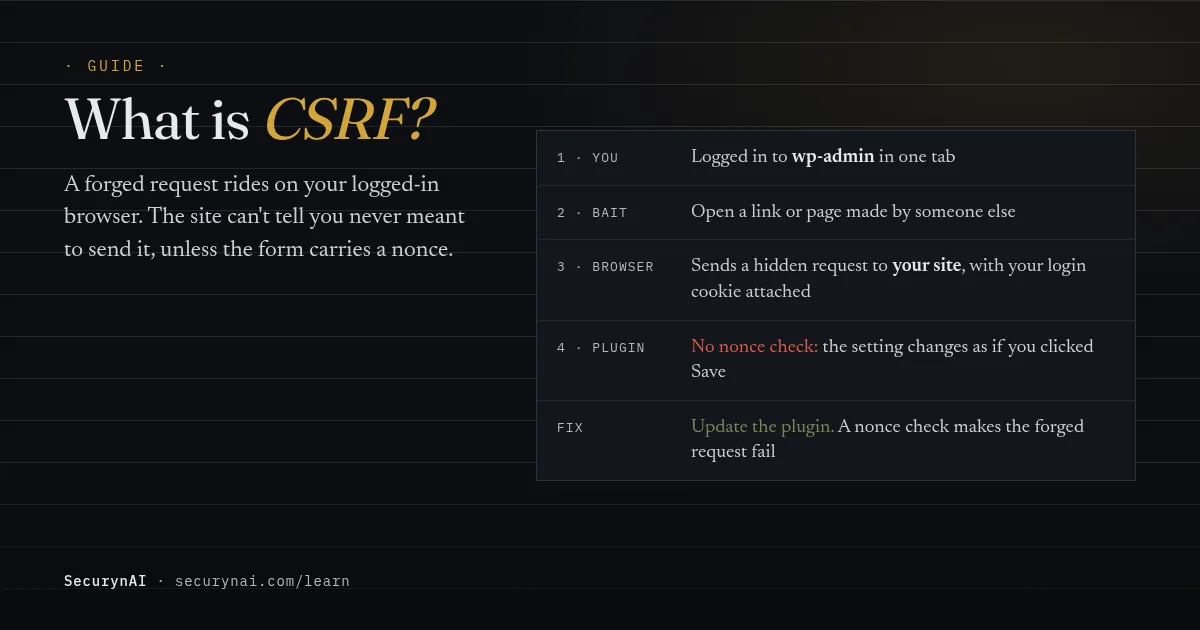
CSRF (cross-site request forgery) is an attack that tricks a browser that's already logged in to your site into sending a request you never meant to send. The attacker never sees your password. They borrow the fact that you're logged in, and the change happens with your account's permissions.
If you're here because an alert says a plugin you use has a CSRF vulnerability, here's the short version. It's usually a medium-severity flaw, and it only works if someone with access clicks a booby-trapped link while logged in. Update the plugin when a fix is out. Until then, avoid clicking unfamiliar links while you're logged in to wp-admin.
How cross-site request forgery works, in plain English
Your browser hands your login to your site on every request, no matter which page asked for it. When you log in to WordPress, your browser stores a cookie that proves who you are. From then on, it sends that cookie with every request to your site: links you click in wp-admin, and requests that start on someone else's page.
That second part is the whole trick. A page somewhere else can contain a hidden form or link that points at an action on your site, such as "save these settings". If you open that page while logged in, your browser sends the request with your cookie attached. To your site, it looks exactly like you clicked Save.
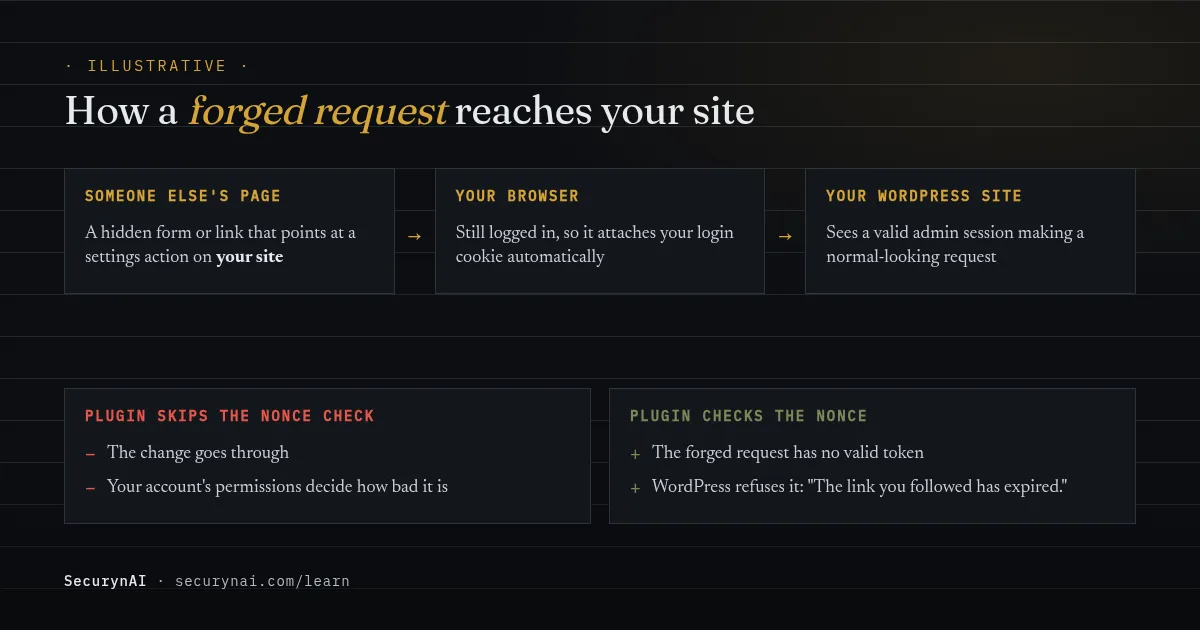
OWASP, the web security project, puts it in one line: CSRF "tricks an authenticated user's web browser into performing an unwanted action on a trusted site." The attacker can't read your site's reply. They can only make your browser fire the request, so CSRF is about changing things, not stealing data directly.
What can a CSRF attack actually do to a WordPress site?
A forged request can do whatever the logged-in person could do on that screen, and nothing more. That's why CSRF flaws aim at administrators. A subscriber who gets tricked can only change their own profile. An administrator who gets tricked can, through a flawed plugin, change site-wide settings.
| Who gets tricked | What a forged request could change | How worried to be |
|---|---|---|
| Subscriber or customer | Their own profile or account settings | Low |
| Shop manager or editor | Orders, products, posts the plugin lets them edit | Medium |
| Administrator | Plugin settings, and through a bad flaw, site options such as who can register | Depends on the flaw: read the advisory |
On its own, CSRF can't run code on your server, read your database or see your password. It needs a logged-in person to open the attacker's page at the right moment, which is why advisories usually rate it lower than flaws anyone can exploit directly.
How WordPress nonces stop CSRF (and what they don't do)
A nonce is a secret token that proves a request came from your site's own form, not from someone else's page. When WordPress or a well-built plugin shows a settings form, it adds a hidden nonce tied to your user account and that specific action. When the form comes back, the code checks the token before doing anything.
A page on another site can't read that token from your browser, so a forged request arrives without it and fails. In WordPress, a failed check usually shows a plain page saying "The link you followed has expired." If you've ever seen that after leaving a tab open overnight, that was the same protection at work.
Two details trip people up, and the WordPress nonces documentation is clear on both:
- They aren't single-use. Despite the name ("number used once"), a WordPress nonce stays valid for a while. The docs say "the actual lifetime is thus variable between 12 and 24 hours."
- They aren't a permission check. The docs say nonces "should never be relied on for authentication, authorization, or access control," and tell developers to protect functions with
current_user_can()as well.
So a safe plugin handler checks two separate things: that the request came from its own form, and that the person sending it is allowed to make the change. Here's a simplified, illustrative version:
// 1. Did this request come from our own form? (stops CSRF)
check_admin_referer( 'myplugin_save_settings' );

// 2. Is this person allowed to change settings? (stops broken access control)
if ( ! current_user_can( 'manage_options' ) ) {
    wp_die( 'Not allowed.' );
}
A missing nonce check is a CSRF flaw. A missing permission check is a different flaw, broken access control. Advisories sometimes mention both. Our guide to broken access control covers the second one.
Real WordPress CSRF vulnerabilities, from mild to serious
CSRF is common, but most WordPress CSRF flaws are small. Patchstack's WordPress vulnerability statistics for 2025 list CSRF as the fourth most common type, at about 13% of disclosed flaws, behind cross-site scripting, "other" and broken access control.
The big picture is plugins. Patchstack's State of WordPress Security in 2026 counted 11,334 new WordPress vulnerabilities in 2025, with 91% in plugins and 9% in themes. WordPress core's own forms check nonces, so CSRF almost always comes from a plugin or theme that skipped the check.
Three real cases show the range, all from the US National Vulnerability Database (NVD):
- Mild: SR WP Minify HTML, 2026. CVE-2026-1392 let a forged request "update plugin settings" in versions up to 2.1. Scored 4.3 out of 10. Annoying, not dangerous.
- Store-relevant: Appointment Booking plugin, 2026. CVE-2026-11866, fixed in 5.6.3, let a forged request overwrite the booking form or disconnect "the connected payment gateway". Scored 5.4, but a quiet way to lose bookings or payments.
- Serious, with a catch: LoginPress, 2025. CVE-2025-1764, in versions up to 3.3.1, could change site options so new sign-ups became administrators. Scored 7.5. But NVD notes a debug setting "must be set to 'true' to exploit the vulnerability", which few live sites have.
Developers often see it the same way. In a WordPress.org support thread about a CSRF report, the plugin's developer replied that it "was rated as low severity by Patchstack with no action needed for users. But we should fix this and we will!" That's a healthy response: low risk, still fixed.
A plugin you use has a CSRF flaw: what to do
Read the advisory's "what can it change" line first. That tells you how fast to move. Our guide on how to read a CVE explains the scores. Then work through these steps:
- Check whether a fixed version exists, and update to it. If you can, turn on automatic updates for that plugin. Our guide to automatic updates covers the trade-offs.
- If there's no fix yet, decide whether you need the plugin. For a flaw that only changes the plugin's own display settings, waiting is usually fine. For one that touches users, registration or payments, deactivate it or find a replacement.
- Until it's fixed, change your habits. Log out of wp-admin when you're done, or use a separate browser profile just for managing the site. Don't open links from unexpected emails or comments while logged in.
Fixes don't always arrive quickly. In one WordPress.org thread, a developer promised "a fix in the next update", and a user later said they'd been "checking it every day for 3 months" before deleting the plugin. Another 2026 CSRF report has no reply at all. If a report sits unanswered for weeks, plan to replace the plugin.
How to tell if a CSRF attack already worked
Look for the change the flaw allows. For the worst kind, the role-and-registration trick, check three places:
- Settings › General: is "Anyone can register" ticked when it shouldn't be, or is "New User Default Role" set to anything above Subscriber (or Customer on a store)?
- Users: are there administrators or shop managers you don't recognise?
- Settings › General: has the administration email address changed?
If any of these look wrong, fix the setting first. Then back up the site as it is now before you delete any account, and follow our guide to a new admin user you didn't create. An attacker with admin access may have done more than add one account.
How to protect a WordPress site from CSRF
You can't add nonce checks to someone else's plugin, but you can shrink the chances a flaw gets used. In order of impact:
- Keep plugins and themes updated, and delete the ones you don't use. A deleted plugin can't have a flaw.
- Have fewer administrators. CSRF needs a logged-in victim with power. Give staff the lowest role that does their job, such as Shop Manager or Editor.
- Keep the default role low and registration closed unless you need it. Then a forged settings change has less to work with.
- Separate admin browsing from everyday browsing. A browser profile used only for wp-admin is a simple habit that removes most of the risk.
- Fix cross-site scripting flaws quickly. OWASP's CSRF Prevention Cheat Sheet warns that "Cross-Site Scripting (XSS) can defeat all CSRF mitigation techniques!" See our XSS guide.
Browsers help a little too. Cookie settings like SameSite limit when a cookie travels with requests from other sites. OWASP calls SameSite "useful as a defense-in-depth control but it does not replace a proper CSRF defense." The nonce check in the plugin is still what counts.
If you write or commission custom code
Ask your developer to confirm three things for every form, AJAX action and REST route that changes something: it checks a nonce, it checks current_user_can(), and it never changes data on a plain GET link. OWASP puts the last one bluntly: "Do not use GET requests for state changing operations."
What SecurynAI does about CSRF, and what it can't
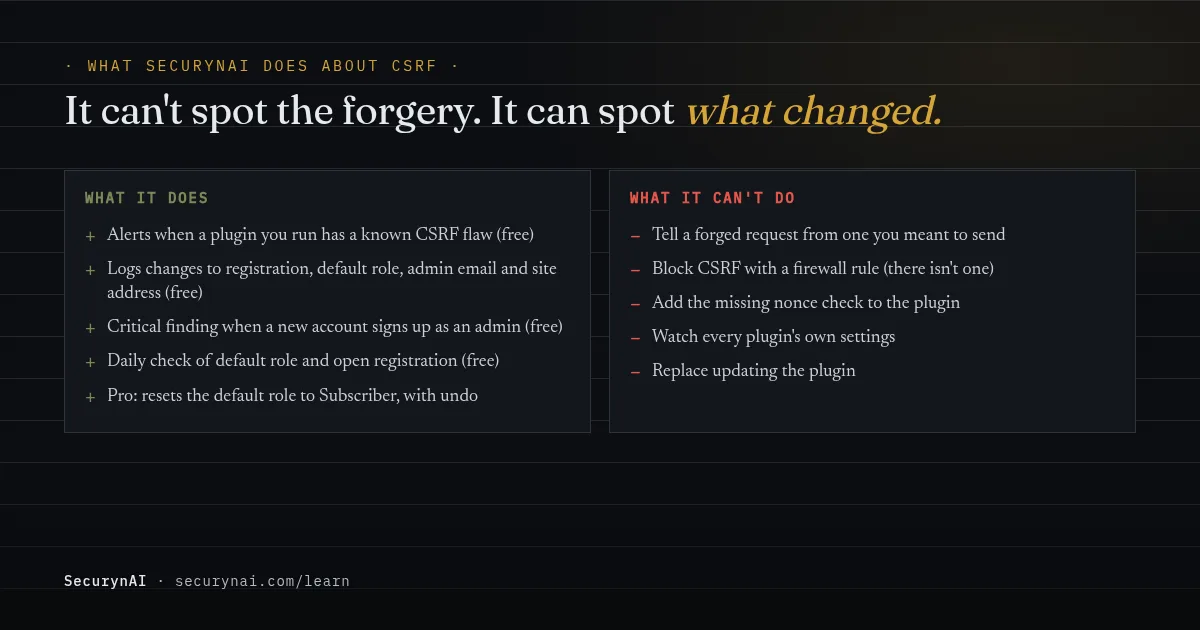
We at SecurynAI can't tell a forged request from one you meant to send. Nobody outside the plugin's own code can. It comes from your browser and IP address, with your valid login, and looks like normal use. What we can do is flag known CSRF flaws and notice the changes a successful attack leaves behind.
No CSRF firewall rule, on purpose
The free firewall checks requests against 13 attack patterns for things like SQL injection, cross-site scripting and path traversal. None of them is for CSRF, because a forged request carries no attack text to match. The firewall also starts in Monitor mode, logging matches without blocking until you switch it to Block.
Known-flaw alerts (free)
The free plugin checks your plugins, themes and WordPress version against the wpvulnerability.net feed every 4 days by default, and again after updates. A CSRF advisory gets a plain-English line saying the flaw could "trick a logged-in user's browser into performing actions they never intended," plus the version that fixes it when the advisory lists one.
Spotting what a CSRF attack changed (free)
The worst WordPress CSRF flaws change who can sign up and what role they get. SecurynAI watches exactly that:
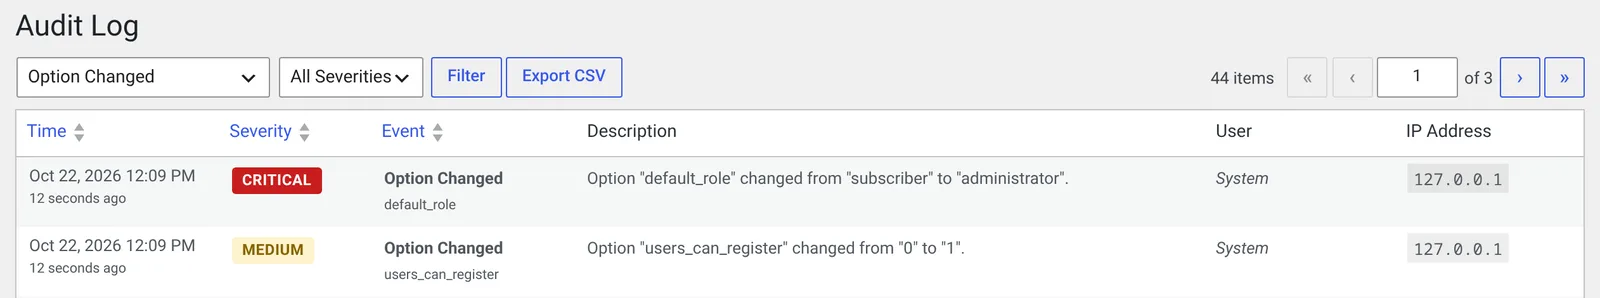
- The Audit Log records changes to "Anyone can register", the default role, the admin email address and the site address, with old and new values. A default role that can manage settings, promote users or edit others' posts is logged as critical. It also logs new users, role changes, profile email changes, password resets and new application passwords.
- A new account that signs up as an administrator raises a critical privilege-drift finding as soon as the role is set. We normally ignore a new user getting the default role, but not when the default role itself is a powerful one.
- Hardening checks run daily, and flag a default role above Subscriber or Customer (medium) and open registration (low).
- A change to the Site URL or Home address raises a high finding.
Email alerts for critical and high findings are off until you turn them on in Settings. The registration, default-role and admin-email changes are Audit Log entries, not findings, so they don't send an email on their own.
What Pro adds
On Pro ($79 per site per year), resetting the default role to Subscriber is one of the automatic hardening fixes, applied without waiting for approval and with undo. Pro's Patch Queue scores CSRF lower on impact than code-execution or SQL injection flaws, and its automatic updates only cover WordPress.org plugins with a fixed version.
For a high-risk privilege-drift finding, such as a new administrator, Pro queues "Undo a suspicious role change" for your approval. Approve it and the roles roll back; a brand-new account loses only the roles it was given. It never runs without your approval.
With your own AI key, Pro can also read part of a vulnerable plugin's code and flag a missing nonce check, with file and line. That's a pointer for a developer, not a code audit.
Here's what neither version does. SecurynAI doesn't add the missing nonce check to a plugin, doesn't watch every other plugin's own settings, and can't undo a change a plugin made inside its own options. None of this replaces updates, backups or good hosting.
Quick check: how exposed is your site to CSRF?
- Are all plugins and themes on their latest versions?
- Have you deleted plugins you no longer use?
- Is "New User Default Role" set to Subscriber (or Customer on a store)?
- Is registration closed, or open only because your store or membership needs it?
- Can you name every administrator, and does each one need that role?
- Would you hear about a known flaw in one of your plugins within a few days?
Six yeses is a solid baseline. A no on the first or third is the one to fix today. If you'd like to go further, our WordPress hardening checklist is the next step.
CSRF FAQ
Is CSRF the same as cross-site scripting (XSS)?
No. XSS gets an attacker's script running inside your own site's pages. CSRF sends a request from outside your site, using your login. They're linked, though: script running on your site can read the nonce, so an XSS flaw can defeat CSRF protection.
What does "The link you followed has expired" mean in WordPress?
It's the message WordPress shows when a nonce check fails. Usually the page sat open too long, so its nonce went stale. Reload the page and try again. It's the CSRF protection doing its job, not a sign of an attack.
Can a firewall stop CSRF?
Not reliably. A forged request comes from your own browser, with your valid login, and usually contains nothing that looks like an attack. The real fix is a nonce check in the plugin's code, which means updating the plugin.
A plugin I use has a CSRF flaw that needs an admin to click a link. Should I worry?
Update it, but there's usually no need to panic. Most CSRF flaws are rated medium and only change that plugin's own settings. If the flaw can change user roles, registration or payment settings, update today, and until then don't click unfamiliar links while logged in.
Want to hear the day a plugin you run gets a known CSRF flaw, and know straight away if a new admin account appears? The free SecurynAI plugin does both, in plain English.
Install free →