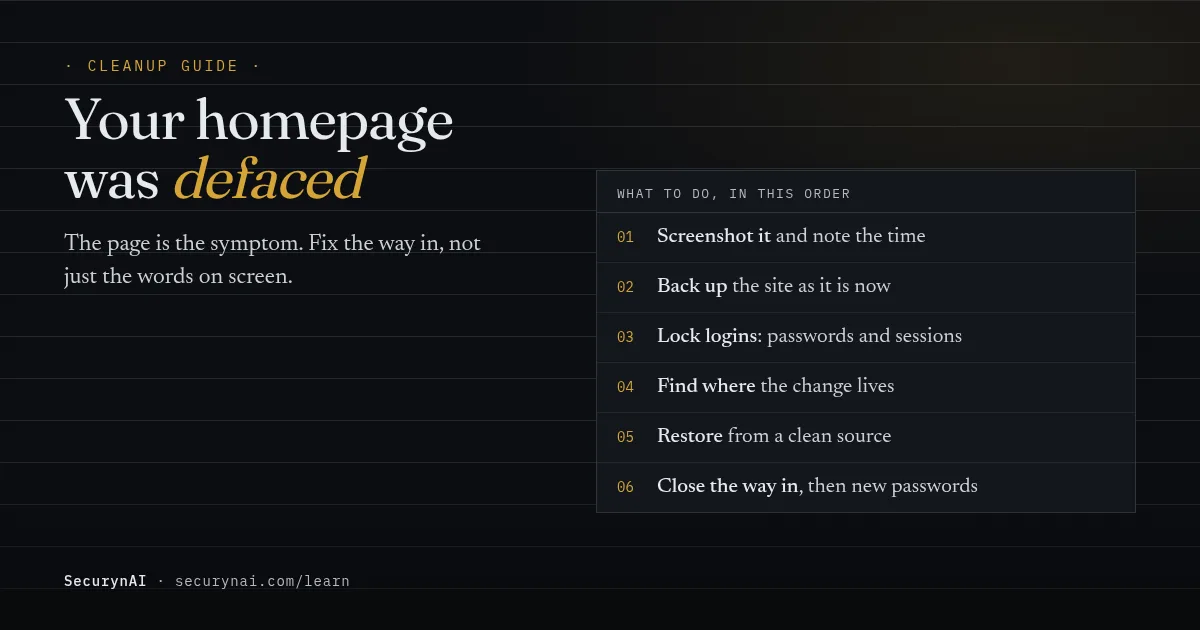
Website defacement is when someone gets into your site and changes what visitors see, usually the homepage, to show their own message. On a WordPress site defaced this way you'll often see a "hacked by" line, a political slogan, or a ransom note. Unlike most hacks, it isn't hiding. That's the one good thing about it: you know.
If your site is showing it right now, the safest first step is to take a screenshot and note the time, then back up the site exactly as it is. Don't delete or "fix" anything yet. The defaced copy is your record of what changed, and your safety net if the cleanup goes wrong.
Is it website defacement, or a different hack?
Defacement changes your own page for everyone. Other hacks send visitors somewhere else, or hide spam where you won't look. Open the site in a private window and on your phone, logged out. If the strange page shows there too, it's on your site, not in your browser.
- You land on a different website. That's a redirect. See site redirecting to another URL.
- Spam pages show in Google, but your site looks fine. See pharma hack and SEO spam.
- A red browser warning appears first. See "Deceptive site ahead".
WordPress's own "My site was hacked" FAQ lists "you can visibly see that your site has been hacked when you open it in the browser" as a clear sign. A defacement doesn't need a second opinion. It does need a calm order of work.
What to do in the first hour after a defacement
Preserve, then lock, then fix. Fixing the page first destroys the clues and leaves the door open.
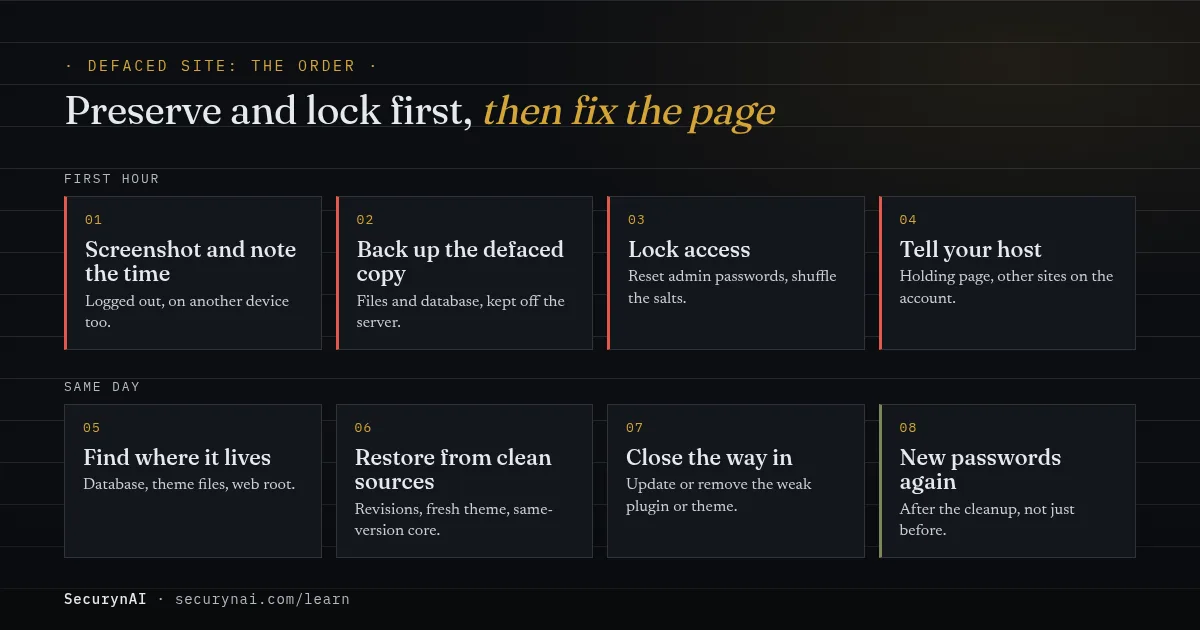
1. Screenshot it and write down the time
The WordPress FAQ calls documentation "the first actionable step": what you see, when you noticed, and what changed recently, like a new plugin or theme. Note the time zone too. The exact message matters, because the same text often appears on other hacked sites and can hint at how they got in.
2. Back up the defaced site, files and database
Use your host's backup tool, or download the site folder and export the database. With WP-CLI, this writes the database to a file you name:
wp db export defaced-copy.sqlKeep the copy off the server and label it clearly so nobody restores it by mistake.
3. Lock every login
Reset all administrator passwords and log everyone out. The FAQ's method is to replace the secret keys in wp-config.php, which ends every session. wp config shuffle-salts does it in one line. Then check Users for administrators you don't recognise.
4. Tell your host, and decide what visitors see
Your host can check for access outside WordPress and see whether other sites on the account are affected. If you can't fix the page within the hour, ask them about a holding page or taking the site offline for now. A short "back soon" beats a stranger's message on your homepage.
Where a defacement lives on a WordPress site
The defaced page you see is stored in one of three places, and the fix depends on which. Work through them in this order, because the first one is the most common and the easiest to put right.
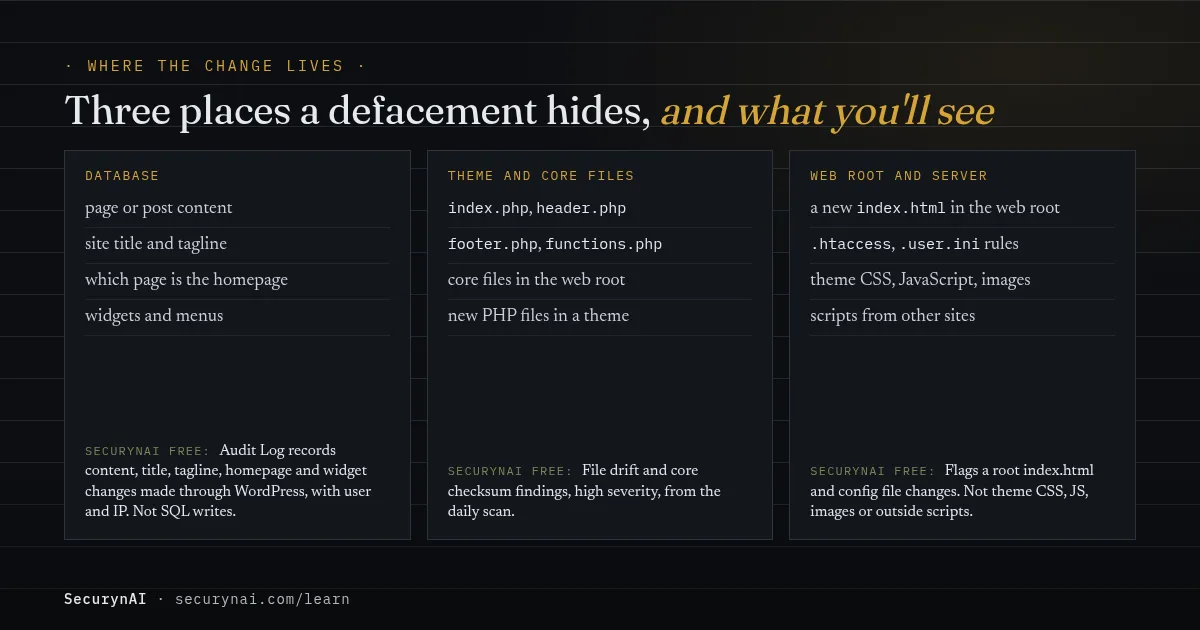
In the database: page content, title and settings
Many defacements just overwrite a page's content, the site title or the tagline. Check Pages, then Settings › General and Settings › Reading, where the homepage is chosen. Look at widgets and menus too.
One owner's WordPress.org thread shows how quiet this can be. The title and tagline changed to a "hacked by" message, then a post's content was replaced, but its edit dates didn't change. The replies pointed to an outdated plugin with a known flaw, not a stolen password.
In theme and core files
If the page content looks normal in the editor but the site still shows the message, the change is in a file. The WordPress FAQ names index.php, header.php, footer.php and functions.php as common targets, because they affect every page. Compare them with a fresh copy of your theme, and check core with wp core verify-checksums.
Outside WordPress altogether
Sometimes the attacker drops a plain index.html into your web root. On Apache, the default index setting is index.html, and when several files are listed the server "will return the first one that it finds", so that file can win over WordPress.
Check the root folder for files you didn't put there, and read every .htaccess. The FAQ calls .htaccess one of the files "most often updated and used for nefarious activities".
How to restore a defaced WordPress page from a clean source
Put things back from a source you trust, rather than editing the defaced version by hand. Back up first if you skipped step 2, because each of these replaces what's there now.
- Page or post content: open the page's revisions, find the last version you wrote and click Restore. WordPress keeps the title, content and excerpt for each saved update.
- Site title, tagline, homepage setting: set them back by hand in Settings.
- Theme files: replace the theme folder with a fresh download from WordPress.org or the vendor. Keep a child theme, but read its files line by line.
- Core files: replace
wp-adminandwp-includesover SFTP with the same version you run. The FAQ warns the dashboard reinstall "often only overwrite[s] existing files, and hacks often introduce new files".
If the attacker went further than one page, follow our full WordPress malware removal guide. A clean backup from before the attack can also be the fastest route, which our guide to restoring from backup after a hack covers. If you can't log in at all, start with locked out of wp-admin.
Why the defacement comes back if you only fix the page
The page is the symptom. If the way in is still open, the same message can return within hours. In one WordPress.org thread, a "Hacked by" message kept appearing after the owner deleted flagged files. The reply was blunt: if it comes back, "the point of entry wasn't found and patched."
Defacement is often only the visible part. Sucuri's 2023 Hacked Website Report found 4.15% of the compromised sites it remediated were defaced, while 49.21% had at least one backdoor. So check for a hidden way back in; our guide to finding a webshell shows what one looks like.
The way in is usually a plugin. Patchstack's State of WordPress Security in 2026 counted 11,334 new WordPress vulnerabilities in 2025, 91% of them in plugins. And 46% had no fix by public disclosure, so sometimes "update it" means "remove it until there's a fix".
Finish with the step people skip: change every password again once the site is clean. The FAQ is specific that this means WordPress, SFTP, the hosting panel and the database, done after the cleanup.
In a 2024 forum thread about links pointing to a hacked landing page, support gave the same advice and added the host, "best positioned to confirm problems that could have occurred outside of WordPress."
What SecurynAI shows after a defacement, and what it doesn't
We at SecurynAI don't clean hacked sites, and the free plugin doesn't undo a defacement. What it gives you is a record of what changed and when, which makes steps 5 to 7 faster. Here's how each place from the diagram above looks in the free plugin.
| Where the change is | What SecurynAI free shows | What it misses |
|---|---|---|
| Posts, pages, block-theme headers and footers, patterns, block navigation menus, products | Audit Log entry, for example Page "Home" updated., with the user, IP and time | The old and new text (use revisions), classic menus, and writes made straight to the database with SQL |
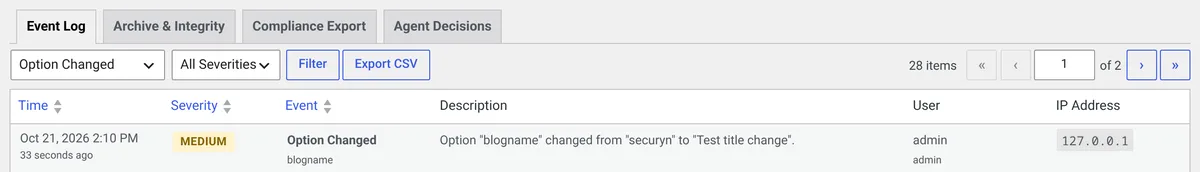
| Site title, tagline, homepage setting, widgets | Audit Log entries showing the old and new values, plus Site URL, Home, admin email and theme switches | Changes made straight in the database, except the site address |
| Site URL or Home | A high "Site address changed" finding, also checked daily, so a change made in the database is caught too | Nothing on this one |
| Theme or plugin PHP files | "File hash drift detected" (high), listing files that changed or appeared without a version update, including edits made in the theme file editor | HTML, CSS, JavaScript and images in themes |
| WordPress core and the web root | "WordPress core integrity mismatch" (high), listing modified files, plus PHP files and an index.html in the root marked "not part of WordPress" | New subfolders in the root, and other non-PHP files |
.htaccess, .user.ini, php.ini, wp-config.php | "Server or WordPress config file changed" (medium), listing the file, the time and the added lines | The first scan only records the files, so earlier changes don't show |
File checks run in the daily scan, not the moment a file changes. Audit Log entries don't send email. File drift, core mismatches and a site address change are high findings, so they do, if you've turned on the optional email alerts for critical and high findings.
Config file changes are medium, so they show on the dashboard without an email.
The Audit Log keeps 7 days by default, adjustable up to 365, and exports to CSV.
On Pro ($79 per site per year), SecurynAI can propose restoring a modified core file, or a file in a WordPress.org plugin, from the official copy. That fix waits for your approval by default. It has no restore for theme files, and its quarantine refuses files of the active theme, so theme repairs stay manual.
The firewall starts in Monitor mode, logging attacks until you switch it to Block. Login lockout works in either mode. None of this replaces backups, updates or good hosting.
Quick check: is your website defacement cleanup finished?
- Do you have a screenshot, the time, and a labelled copy of the defaced site stored off the server?
- Did you check page content, the title and tagline, the homepage setting, theme files, core files and the web root?
- Was everything put back from a clean source, not edited by hand?
- Can you name every administrator account?
- Did you update or remove the plugin or theme that likely let them in?
- Did you change every password again after the cleanup?
Six yeses means the page and the door are both fixed. If you're telling customers or a client what happened, keep it short: what they saw, that it's resolved, and what you changed. Agencies can use our playbook on explaining a hack to a client.
Website defacement FAQ
Can I just put the old homepage back?
You can, and you should, but only after you've backed up the defaced copy and locked logins. Putting the page back changes what visitors see. It does nothing about how the attacker got in, so the same message can return the same day.
How did they change my page if nobody logged in?
Usually through a flaw in a plugin or theme. A flaw can let someone write to the database or drop a file without ever using the editor, which is why the post's edit date and your login history can look untouched. Update or remove the weak component, then change every password.
Will Google flag my site for a defacement?
Not always. SecurynAI doesn't watch Google's blocklist, so check Search Console's Security Issues report to be sure. If there is a warning, request a review only once the cleanup is finished. Google says malware reviews take a few days, and warnings go within 72 hours of the site being found clean.
Cleaned up a defacement and want a record of the next change to your pages and files? The free SecurynAI plugin starts its Audit Log and file checks the day you install it.
Install free →