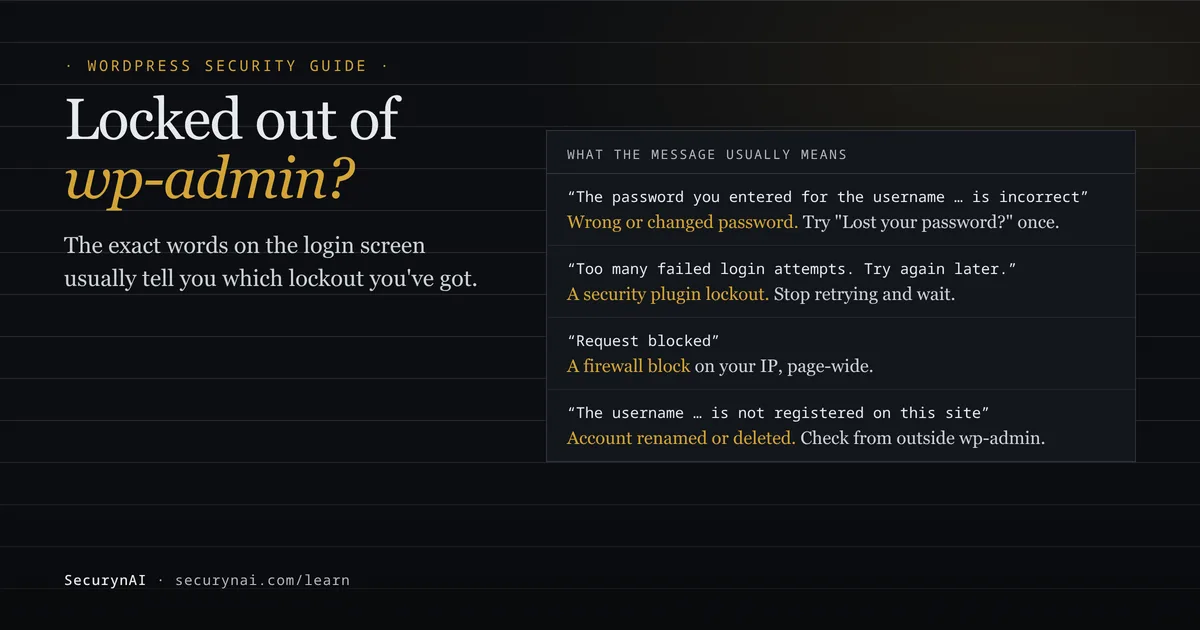
Being locked out of wp-admin means WordPress, a security plugin or your server is refusing your login, so you can't reach the dashboard. If you can't log in to WordPress admin right now, the safest first move is to stop retrying. Every failed attempt can count toward a lockout and make the wait longer.
Then read the message on the login screen word for word. It usually tells you which of four situations you're in. Three are ordinary. One is a hacked account, and that needs a careful order of work.
Why am I locked out of wp-admin? Four usual causes
Match what you see to a cause before you change anything. The fix for a plugin lockout (wait) is the opposite of the fix for a takeover (act now).
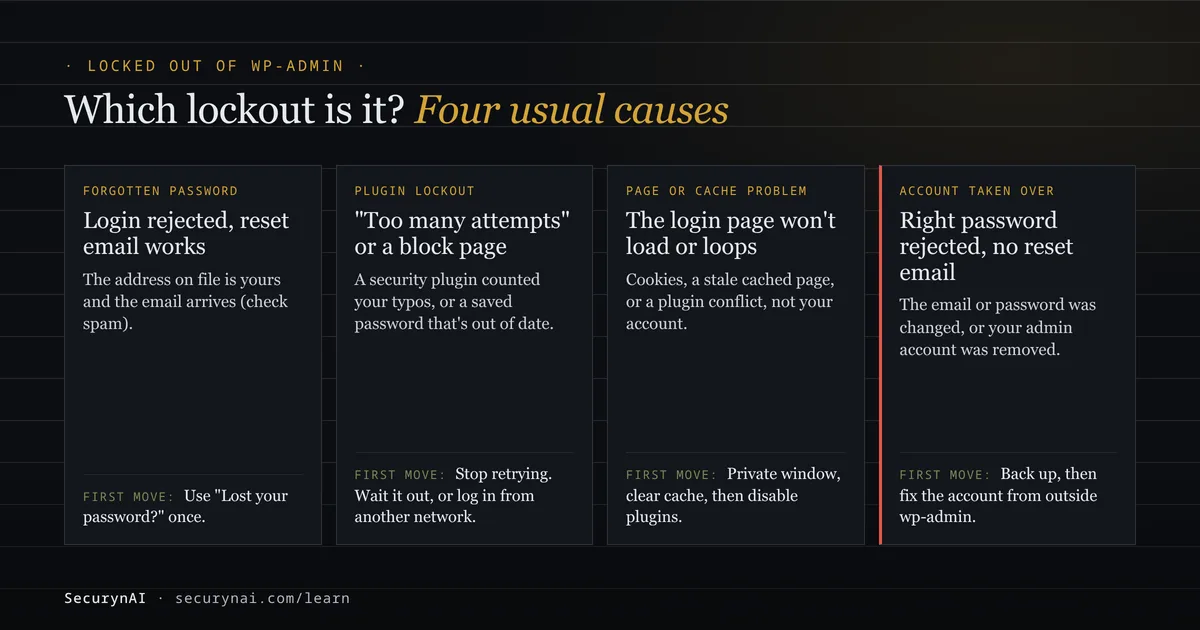
| Likely cause | What you see | First move |
|---|---|---|
| Wrong password | "The password you entered for the username … is incorrect." | Use "Lost your password?" once |
| Login lockout | "Too many failed login attempts" or "locked out", set by a security plugin or your host | Stop and wait, or try another network |
| Firewall block | A plain "Request blocked" or 403 page, even on the homepage | Try from your phone's mobile data to confirm |
| Page or cache | The login page loops back to itself or won't load | Private window, then clear your host's or CDN cache |
| Account changed | "The username … is not registered on this site", or no reset email ever arrives | Back up, then work from outside wp-admin |
Forgot your password, or the reset email never arrives?
The "Lost your password?" link is the right first step, as long as the email on your account is still yours. WordPress's reset your password guide calls it "normally, the easiest way," and lists other routes for when "your email isn't working correctly."
If no email shows up, check spam first. Plenty of hosts can't send mail reliably, and WordPress's troubleshooting FAQ says reset emails often go missing because the server has no working mail setup or the message is treated as spam. That's a mail problem, not a hack.
It becomes a security question when the email on the account isn't yours any more. You can only check that from outside wp-admin, as shown below.
Locked out by a security plugin? What to do
A login lockout is the plugin doing its job, and it usually ends on its own. Login-limit features count failed attempts and block the address they came from. That includes you, after a few typos or a password manager filling in an old password.
A 2026 WordPress.org thread shows the pattern. An owner set a 24-hour lockout and then got caught by it. The plugin's support team explained it was "brute force protection doing its job," told them to check whether the blocked IP was their own, and suggested shortening the lockout.
- Wait it out. Most lockouts are timed. Don't retry while you wait, or some plugins start the clock again.
- Try another network. Lockouts usually key on your IP address, so your phone's mobile data often gets you in.
- Ask another admin to clear the block from the plugin's settings.
- Disable the plugin from outside. If none of that works, rename the plugin's folder (next section).
If the lockout keeps coming back with no typos from you, someone else is guessing at your username. Another WordPress.org thread describes admin accounts locked for 60 minutes again and again until the poster deactivated the plugin. Turning protection off isn't the fix there. Changing a guessable username and adding two-factor login is.
How to disable a plugin when you can't reach the dashboard
Using SFTP or your host's file manager, go to wp-content/plugins and rename the plugin's folder, for example by adding .off. WordPress then treats it as missing and deactivates it. If you don't know which plugin is responsible, WordPress's own FAQ renames the whole plugins folder, which "will disable all plugins."
Settings are kept in the database, so nothing is lost. Once you're logged in, rename the folder back and reactivate the plugin from the Plugins screen. Don't leave a security plugin switched off once you're back in. If you have WP-CLI, wp plugin deactivate does the same job.
If SecurynAI locked you out: every lockout and how to undo it
We at SecurynAI build a security plugin, so we'd rather be upfront: ours can lock you out too. Here's every way it can refuse a login, how long each lasts, and the safe undo. All of these were checked against the plugin's code in October 2026.
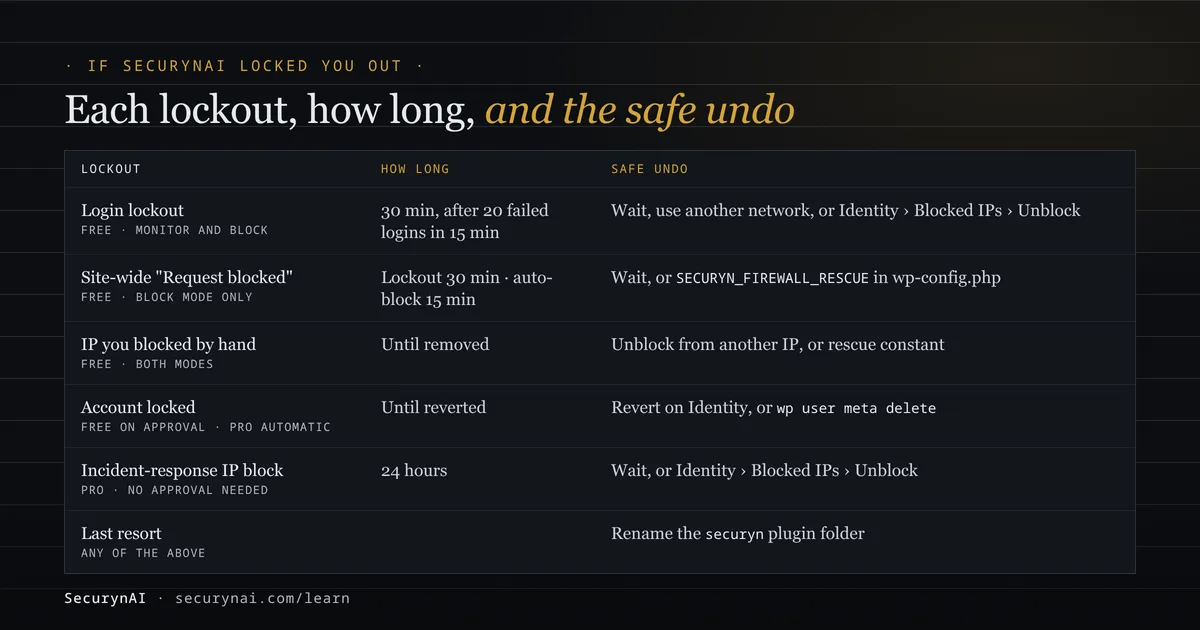
| Lockout | What you see, and for how long | Safe undo |
|---|---|---|
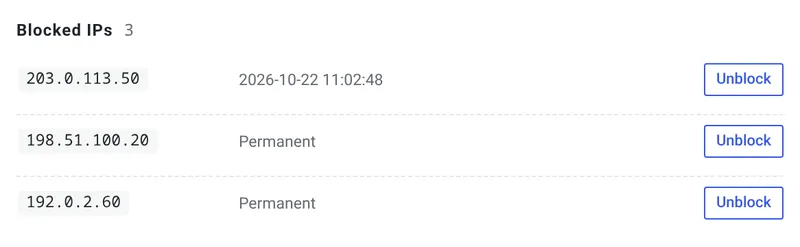
| Login lockout | Free, in Monitor and Block mode. "Too many failed login attempts. Try again later." After 20 failed logins in 15 minutes from one IP, or against one username, that IP can't log in for 30 minutes | Wait 30 minutes, log in from another network, or have another admin click Unblock under SecurynAI › Identity › Blocked IPs |
| Site-wide block | Free, Block mode only. A "Request blocked" page on every page, wp-admin included, for a locked-out IP (30 minutes) or an IP auto-blocked after 10 firewall hits in 15 minutes (15 minutes) | Wait, or add the rescue line to wp-config.php (below) |
| Manual IP block | Free, any mode. An IP you blocked yourself gets "Request blocked" everywhere, with no end date | Unblock it from another IP, or use the rescue line |
| Account lock | Only after an admin approves it, on Free and Pro. "This account is temporarily locked by SecurynAI." Correct passwords are refused until it's reverted | Revert on the Identity page, or the WP-CLI line below |
| Incident IP block | Pro, runs without approval. Attacking IPs from an incident get "Too many failed login attempts" at login (any mode) and, in Block mode, "Request blocked" everywhere, for 24 hours | Wait, or Unblock under Identity › Blocked IPs |
| Signed out | Free and Pro. You're logged out of every device | Just log in again; your password still works |
The firewall starts in Monitor mode, logging attacks until you switch it to Block. In Monitor mode the only site-wide blocks are IPs you blocked yourself, but the login lockout works in either mode. The username counter counts guesses from any address, so bots hammering your username can trip it on your next typo.
In Block mode, your own requests can match a firewall rule too. Saving a post that contains a <script> tag is one example. One match gives a "Request blocked" page with a reference code. Ten in 15 minutes blocks your IP for 15 minutes. You can untick that rule on the Firewall page.
The rescue line, and the WP-CLI fixes
If the site-wide "Request blocked" page has you stuck, add this line to wp-config.php above "That's all, stop editing!". It only switches off SecurynAI's free firewall, for every visitor, so remove it as soon as you've cleared the block.
define( 'SECURYN_FIREWALL_RESCUE', true );The rescue line doesn't lift the login lockout or an account lock, and it doesn't cover Pro's adaptive firewall. WP-CLI is never blocked by the free firewall, so these work from the server. Replace wp_ with your table prefix and the IP with yours:
wp db query "DELETE FROM wp_securyn_ip_blocklist WHERE ip_address = '203.0.113.7'"
wp user meta delete your-username securyn_account_locked
The first removes an IP block, the same as the Unblock button. The second clears an account lock, the same as Revert. Both use standard commands (wp db query, wp user meta delete); SecurynAI's free plugin doesn't add its own wp securyn commands.
The last resort is renaming wp-content/plugins/securyn. That switches off every SecurynAI check and Pro with it, since Pro needs the free plugin.
On Pro, three more actions can affect access. Incident response can block attacking IPs for 24 hours without waiting for approval. A forced password reset gives a user a random password, signs them out and emails WordPress's reset link, so use that link. It never resets the admin applying it.
And "disable admin account" demotes an admin to Subscriber, but only after you approve it.
Signs it's an account takeover, not a lockout
A takeover looks like a lockout from the login screen, but the details don't add up. You're sure the password is right and it's refused with no lockout message. The reset email never comes, even with mail working. Or WordPress says your username isn't registered.
Stolen logins are a common way in. Verizon's 2025 Data Breach Investigations Report found credential abuse was the initial attack vector in 22% of breaches, just ahead of exploited vulnerabilities at 20%. Once in, an attacker may change the account's email so your resets go to them.
On WordPress the way in is often a plugin flaw. Patchstack's State of WordPress Security in 2026 counted 11,334 new WordPress vulnerabilities in 2025, 91% of them in plugins, and three of its ten most exploited were privilege escalation flaws, which can hand a stranger admin rights.
One WordPress.org thread shows how it looks. An owner and his wife were both locked out. Every account had been deleted except one admin, now carrying an email address he didn't recognise. He got in by changing that email in the database and using the normal reset, then asked the right question: how did they get in?
How to regain access to wp-admin from outside WordPress
You can fix an account without the login page if you have server, SFTP or database access. Back up the database first, because each step below writes to it. Your host's backup tool works, or wp db export if you have WP-CLI.
1. With WP-CLI, if you have SSH
This is the safest route, because WordPress hashes the new password itself. List the accounts, check the email on yours, then set a new password and, if needed, the correct email. Use your own username or ID and a long, new password:
wp user list --role=administrator
wp user update your-username --user_pass="a-long-new-password" --user_email="you@example.com"
Both forms come from WordPress's reset guide and the wp user update reference. If your account was demoted, wp user set-role your-username administrator puts it back. If it was deleted, wp user create with --role=administrator makes a new one.
2. With phpMyAdmin, if you only have database access
Open the wp_users table (your prefix may differ), find your user_login and click Edit. In user_pass, type the new password and choose MD5 from the function dropdown. Check user_email in the same row while you're there. A forum poster in an older "have I been hacked?" thread said this "worked like a charm."
The guide notes WordPress accepts the MD5 value and lets you log in. Since WordPress 6.8 passwords use bcrypt, but the core team's announcement says older hashes "will continue to work," and its author confirmed MD5 "will now remain supported."
3. Log everyone else out
Changing a password in the database doesn't end sessions that are already open. If anything points to a takeover, refresh the secret keys in wp-config.php, which signs out every logged-in user. wp config shuffle-salts does it in one line. You'll need to log in again too.
Back in wp-admin? Check these before you move on
If it was a plain lockout, you're done. If anything looked wrong, treat it as a hack until you've ruled it out.
- Go to Users and filter by Administrator. Can you name every account? If not, see a new admin user I didn't create.
- Check your own profile's email, and Settings › General › Administration Email Address.
- Look for roles that changed quietly; our privilege drift guide explains what to look for.
- Update or remove the plugin that let them in, then change every password again: WordPress, SFTP, hosting and database.
- Work through how to remove WordPress malware for anything left behind. If you'd rather start from a clean copy, see restoring from backup after a hack.
- Turn on two-factor login for every admin. Our guide to securing the WordPress login page covers what helps.
If SecurynAI was already installed, its free Audit Log helps with steps 1 to 3. It records logins and failed logins, new and deleted users, role changes and email changes made through WordPress, plus a change to the site's admin email. It keeps 7 days by default, adjustable up to 365, and exports to CSV.
A login lockout raises a high finding (lockouts within the same hour are grouped into one) and a new administrator a critical one, so if you've switched on the optional email alerts for critical and high findings, you'd hear about both.
None of this replaces backups, updates or good hosting, and changes written straight into the database with SQL won't show in the Audit Log.
Locked out of wp-admin: FAQ
How long does a WordPress login lockout last?
It depends on the plugin that set it. SecurynAI's free login lockout lasts 30 minutes by default, after 20 failed logins in 15 minutes. Other plugins use their own numbers, and some let you set a lockout of a day or more, so check the message on screen and the plugin's settings.
Will deleting or renaming my security plugin's folder break my site?
Usually not. WordPress treats the plugin as missing and deactivates it, and its settings stay in the database. Rename the folder back once you're in, then reactivate it from the Plugins screen. While it's off, the site has no protection from that plugin, so don't leave it that way.
Is it safe to reset my WordPress password in phpMyAdmin with MD5?
Yes, it's a documented recovery method. WordPress's own reset guide describes it, and WordPress 6.8 kept support for older hash formats. Back up the database first, edit only the user_pass field, and use WP-CLI instead if you have it, because it hashes the password properly.
Does a password reset log out an attacker who is already in?
Not on its own if you change the password in the database. Shuffle the salts in wp-config.php (wp config shuffle-salts) to end every session, then remove any admin accounts you don't recognise.
Back in and want to know sooner next time an admin account changes? The free SecurynAI plugin logs logins, role and email changes from the day you install it, and its lockouts come with a clear undo.
Install free →