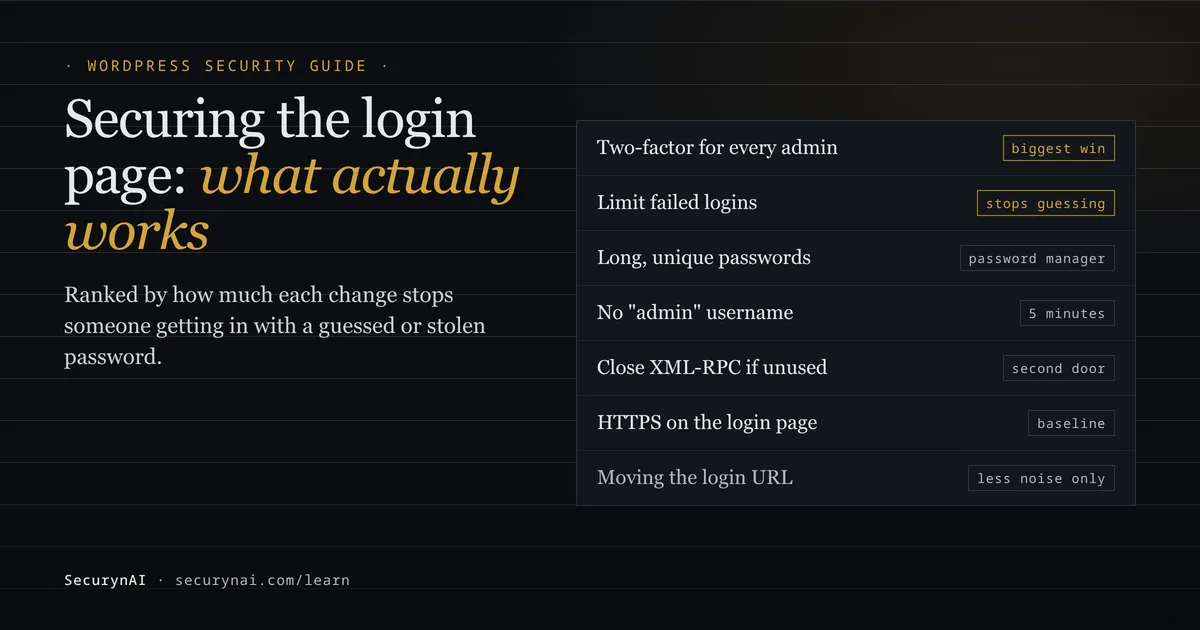
To secure the WordPress login page, you make a correct password not enough on its own (two-factor), make guessing slow (a limit on failed logins), and close the other ways in that take a password without the form. Everything else, including hiding the login URL, is a smaller extra.
WordPress login security is about one thing: stopping someone who isn't you from signing in as you. If you're just tightening things up, work down this page in order. If you've already spotted strange logins, start with what an unusual admin login means, then come back.
Why bots keep hammering your WordPress login page
Failed logins in your logs are normal. Every public WordPress site gets automated password guesses, and seeing them doesn't mean anyone got in. Bots try common usernames and leaked passwords on thousands of sites at once, hoping one combination works somewhere.
It's worth taking seriously, though, because stolen or guessed logins work. Verizon's 2025 Data Breach Investigations Report found that "credential abuse (22%) and exploitation of vulnerabilities (20%) continue to be the leading initial attack vectors" across the 12,195 confirmed breaches it studied.
And WordPress doesn't stop guessing by default. There's no built-in limit on failed logins, and WordPress's own brute force guidance notes that "WordPress core does not ship 2FA." Both have to come from a plugin, your host or a service in front of your site.
Turn on two-factor login for every admin first
If you do one thing from this guide, make it two-factor authentication (2FA) for every account that can change the site. A rate limit slows down guessing. Two-factor means a correct password, guessed or phished or leaked, still isn't enough to get in.
The evidence is strong. A Microsoft Research study, published in May 2023, estimated that multifactor authentication "reduces the risk of compromise by 99.22% across the entire population and by 98.56% in cases of leaked credentials." It also found authenticator apps did better than text-message codes.
- Who needs it: administrators, editors, shop managers and any agency or developer accounts. Old accounts nobody watches are the usual target, as our guide to the dormant admin account explains.
- Which method: an authenticator app or a passkey beats email or SMS codes. Keep the backup codes somewhere safe, away from the site.
- One catch: some 2FA plugins don't cover XML-RPC or app logins. We cover that further down.
How to limit login attempts without locking out real people
A limit on failed logins takes away the thing that makes guessing work: unlimited free tries. After a set number of wrong passwords in a short window, the source is blocked for a while. That turns millions of guesses into a handful.
There's no single right number. In a WordPress.org support thread about constant login attempts, Wordfence's support team suggested 3 to 5 attempts and a lockout of at least 30 minutes. NIST's 2025 SP 800-63B sets 100 consecutive failures as an upper bound, and says lower limits are fine.
Pick numbers that fit your site
| Your site | Tighter or looser? | Why |
|---|---|---|
| A few admins, no public accounts | Tighter | Real people rarely fail more than twice |
| Store or membership site | Looser | Customers forget passwords; office or mobile networks share IPs |
| Behind Cloudflare or another proxy | Fix the IP first | Otherwise every visitor looks like the proxy, and one lockout hits everyone |
That last row matters more than the numbers. If your site sits behind a CDN or proxy, make sure your login limiter reads the visitor's real IP address. WordPress's guidance also prefers throttling at the server or edge where you can, because a plugin still runs PHP for every attempt during a flood.
Passwords and usernames: the quiet half of WordPress login security
Long beats clever. NIST's current guidance asks for at least 15 characters when a password is the only factor, and at least 8 when it's paired with another factor. It also says not to force character mixes, and to check new passwords against lists of common and breached ones. A password manager makes all of that painless.
Next, retire the admin username. It's the first one bots try, and WordPress's own guidance says plainly: "Do not use the username admin." Create a new administrator with a different username, log in as them, then delete the old account and give its posts to the new one when WordPress asks.
Where real usernames leak, and how much it matters
Two WordPress defaults can reveal login names. Visiting ?author=1 redirects to an author archive whose address usually contains the username. The REST API's users list shows the same "slug," but logged-out visitors only see people who have published posts, not every account.
Hiding usernames is worth a few minutes, not a weekend. Bots guess common names anyway. Strong passwords and 2FA protect you whether or not a username is known. A display name that differs from the login name helps on author pages.
Close the other doors: XML-RPC and application passwords
The login form isn't the only place WordPress accepts a password. xmlrpc.php and application passwords take a username and password with no form, no CAPTCHA and often no 2FA prompt. Moving the login page doesn't touch either of them.
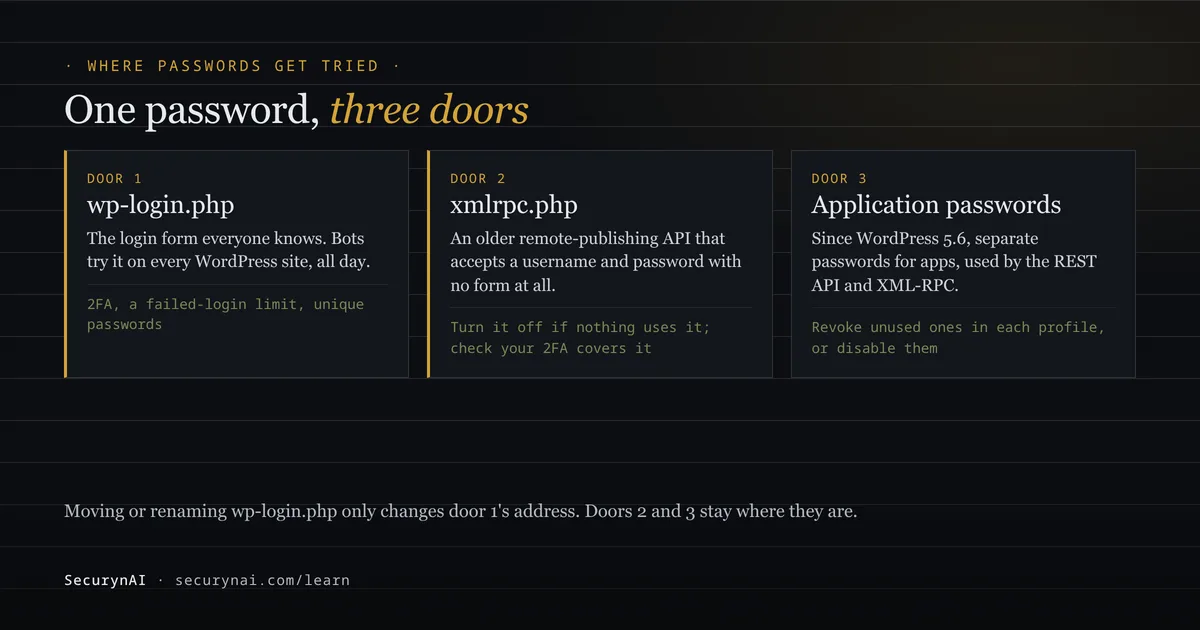
Site owners run into this all the time. In one WordPress.org thread, an owner asked how bots still hit the login after the admin URL was changed. Plugin support traced the attempts to XML-RPC, and the owner "completely disabled XMLRPC." In another thread, the same fix ended the failed logins.
- XML-RPC: if no app needs it (Jetpack, the WordPress mobile app and some remote-publishing tools do), turn it off. The
xmlrpc_enabledfilter only disables the methods that need a login, not pingbacks. Blocking the file at the server or CDN closes it fully. Our XML-RPC brute force guide walks through the choice. - Application passwords: since WordPress 5.6 they work in place of the real password for the REST API and XML-RPC. Check each admin's profile and revoke any you don't recognise. If nothing uses them, the
wp_is_application_passwords_availablefilter turns them off. - HTTPS: make sure the login page and wp-admin only load over HTTPS, so passwords aren't sent in plain text.
Does moving wp-login.php help at all?
A little, for noise. Not for safety. A custom login address removes your form from bots that only try /wp-login.php, so your logs get quieter. WordPress's guidance puts it fairly: obscuring the login URL "can reduce noise but should not be your only defense."
The trade-offs are real. A forum moderator in a thread on changed login URLs put it bluntly: "Moving the login does not work ever because there are other ways to log in via XML-RPC." Custom URLs can also break when a plugin updates, and they leave you with one more thing to remember when you're locked out.
CAPTCHA and bot checks sit in the same bucket. They cut down on simple scripts, but they do nothing about a correct, stolen password. Use them on top of 2FA and login limits, never instead.
Your WordPress login security checklist
- Turn on 2FA for every administrator, editor and shop manager.
- Add a failed-login limit, and check it sees real visitor IPs behind a proxy.
- Use long, unique passwords from a password manager.
- Remove any account called
admin. - Remove accounts you can't name, and old developer or agency logins.
- Turn off XML-RPC if nothing uses it, or confirm your 2FA covers it.
- Revoke application passwords you don't recognise.
- Confirm the login page and wp-admin load only over HTTPS.
For the wider set of changes beyond the login, see our WordPress hardening checklist.
What SecurynAI does at the login page, and what it doesn't
Let's start with the gap. We at SecurynAI don't provide two-factor login, CAPTCHA or a custom login URL. For 2FA, use a dedicated plugin. What the free plugin does is limit guessing, check that your admins have 2FA, and tell you about logins that don't look right.
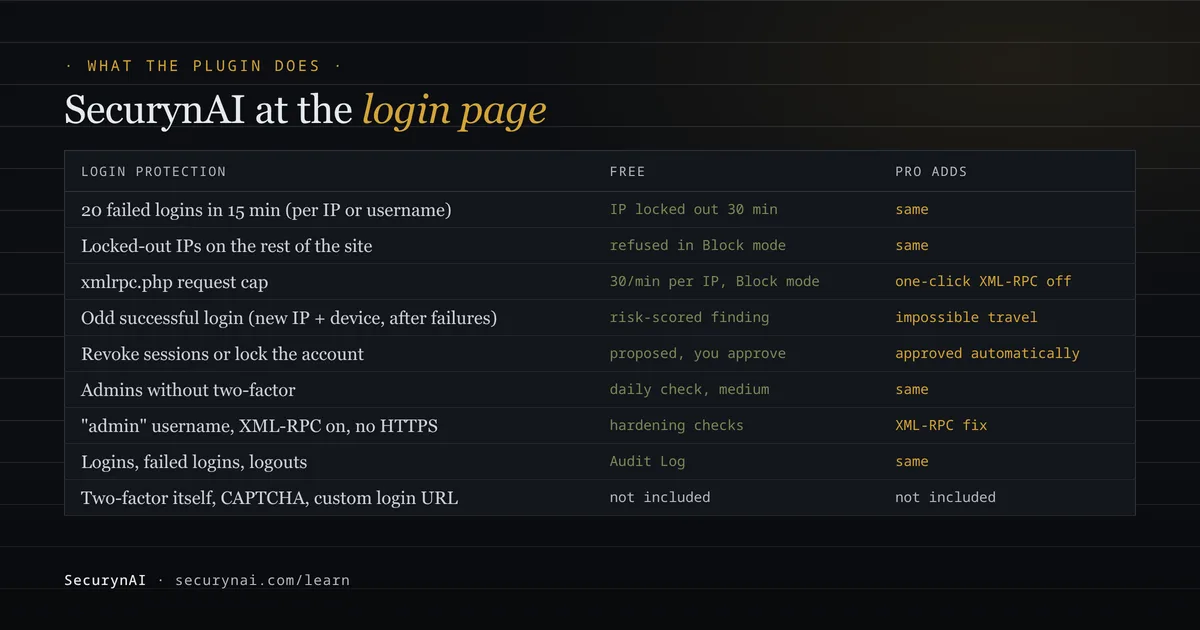
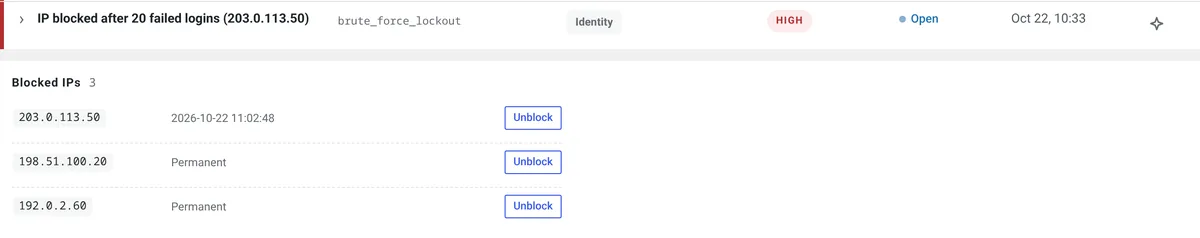
- Login lockout (Free): 20 failed logins in 15 minutes, from one IP or against one username, locks that IP out of logging in for 30 minutes and raises a high finding. Lockouts within the hour join that finding, so many IPs mean one finding and one email. Form and XML-RPC failures both count, in Monitor or Block mode.
- Site-wide blocks (Free): the firewall starts in Monitor mode, logging attacks without blocking. Once you switch it to Block, locked-out IPs are refused across the whole site, and xmlrpc.php is capped at 30 requests a minute per IP.
- Unusual logins (Free): each successful login is scored. A new IP plus a new device, or a success right after 5 or more failures in 15 minutes, raises a finding with the reasons in plain English.
- 2FA check (Free): once a day, we flag each administrator with no 2FA from Two-Factor, WP 2FA, All-In-One Security, Wordfence, Duo or Google Authenticator.
- Hardening and history (Free): checks flag an
adminusername, XML-RPC left on and an admin area without HTTPS. The Audit Log records logins, failed logins and logouts.
Our lockout defaults are deliberately loose so shared office or shop IPs don't lock out staff, and they can't be changed in the settings screen. If a username is under attack, even one wrong password from your own IP can lock you out for 30 minutes. Behind a proxy, turn on "Trust proxy headers" in Settings › General first.
For unusual logins, Free on its own only sends an email, to your "Send alerts to" address or else the site admin email. Signing the user out everywhere or locking the account waits on the Identity page for you to approve. Critical and high findings can also be emailed to you once you turn on email alerts in Settings.
On Pro ($79 per site per year), a re-verify request runs on its own and a high-confidence sign-out does too (an account lock still waits for you), flag "impossible travel" between two logins, and watch for a signed-in admin session that suddenly comes from somewhere else. Pro can also switch XML-RPC off, with undo. None of this replaces backups or a good host. Here's what's in Free and Pro.
Securing the WordPress login page: FAQ
Do I need a plugin to limit login attempts in WordPress?
WordPress itself doesn't cap failed logins, so something has to add a limit: a security plugin, your host, or a firewall or CDN in front of the site. WordPress's own guidance prefers stopping floods at the server or edge where you can, because a plugin still uses PHP for every attempt.
Does changing the login URL stop brute force attacks?
It cuts the bot traffic that only tries /wp-login.php, which can make your logs quieter. It doesn't stop password guessing through xmlrpc.php or application passwords, and it doesn't help against someone holding a real, stolen password. Treat it as tidying, not protection.
Does two-factor authentication protect XML-RPC logins?
It depends on the two-factor plugin and its settings. Some block password logins over XML-RPC, others let them through because there's no screen to ask for a code. Check your plugin's documentation, and turn XML-RPC off if nothing on the site uses it.
I locked myself out after too many wrong passwords. What now?
Most lockouts are tied to your IP address and expire on their own; SecurynAI's lasts 30 minutes by default. Another administrator can lift it early from the Blocked IPs list on the SecurynAI Identity page. If you can't wait, our guide to being locked out of wp-admin covers the safe ways back in.
Tightening up your login and want to know when someone keeps trying? The free SecurynAI plugin limits guessing, checks your admins for 2FA and explains every odd login in plain English.
Install free →