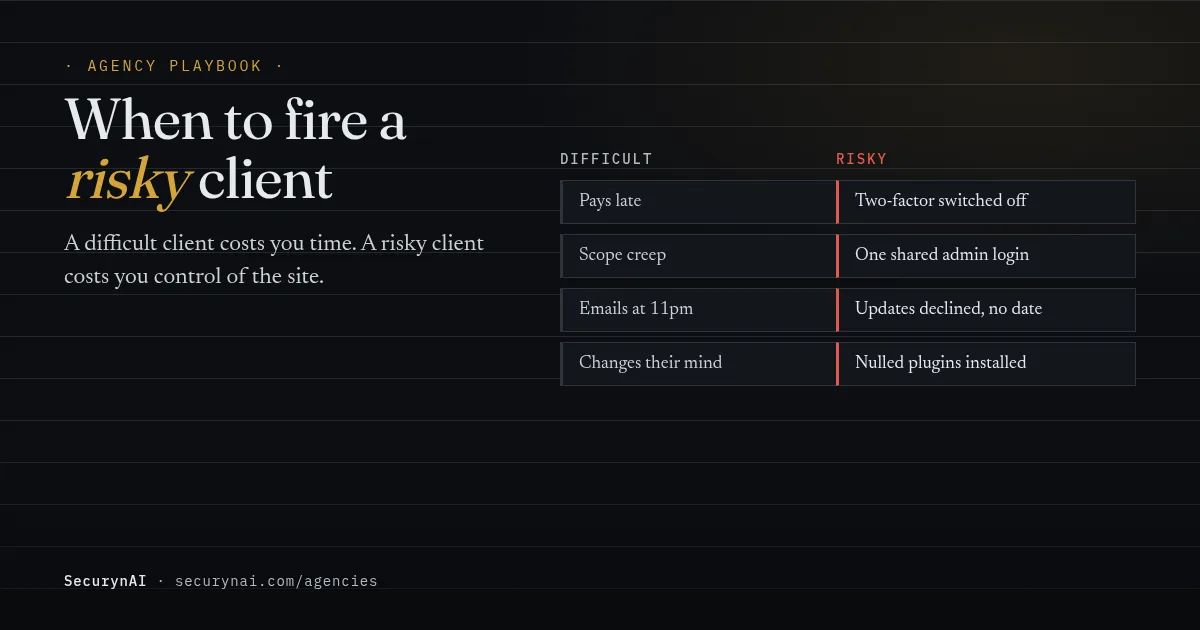
A risky client, in security terms, is one whose own decisions keep removing protections from a site you're still expected to answer for. You should fire a risky client when that gap keeps growing after you've warned them in writing, offered a fix and set a deadline. Firing comes last, after the paper trail, never as the first move.
Picture it (an illustrative scene, not a real client). It's Friday afternoon. A client asks you to switch off two-factor login for their whole team, because the codes are "annoying". It's the third security setting they've wanted gone this year. This playbook covers the client security risk behind that request, and when ending the client relationship is the right call.
When is a client a security risk, not just a difficult one?
A difficult client costs you time. A risky client costs you control. Slow payers, scope creep and 11pm emails are business problems. Security risk is narrower: the client keeps making choices that widen the gap between what you can protect and what everyone assumes you protect.
Here are the patterns we'd watch for, and what each one usually calls for. Treat the right-hand column as a starting point, not a rule. One bad week isn't a pattern.
| What the client does | Usually means |
|---|---|
| Asks to delay updates for a launch or a busy month | Normal. Agree a date and write it down |
| Declines updates or backups repeatedly, with no date | Get the decline in writing |
| Wants two-factor login, the firewall or login limits switched off | Get the decline in writing, then re-scope |
| Shares one admin login or reuses passwords after being told not to | Re-scope. You can't vouch for access you don't control |
| Installs pirated ("nulled") plugins or themes | Remove them, or exit. There's no safe middle |
| Gives admin access to people you've never heard of | Re-scope, then exit if it continues |
| Stops paying for maintenance but expects you on call | Re-scope in writing, then notice |
None of these are rare. In one WordPress.org support thread, a developer chasing a reinfection found out mid-cleanup that "the client informed me that they used a nulled theme and 2 nulled plugins." A forum moderator replied that nulled products "can sometimes deliver more invasive malware packages."
Why passwords and updates top the list
Two habits matter more than the rest, and the numbers explain why. Verizon's 2025 Data Breach Investigations Report found that credential abuse (22%) and exploiting vulnerabilities (20%) were the leading ways attackers got in. Shared logins feed the first. Skipped updates feed the second.
For WordPress specifically, Patchstack's State of WordPress Security in 2026 report says about half of high-impact vulnerabilities get exploited within 24 hours, with a weighted median time to first exploit of 5 hours. A client who says "update it next month" is betting against those numbers.
Credentials show up in forum threads too. In a review thread for the WPCode plugin, its developer said that in every case they'd looked at, the cause was "administrator user credentials being compromised", not the plugin itself.
Why "the client told us to" only protects you on paper
Your name stays on the site after the client turns the protection off. If it gets hacked, the client calls you, their customers see your footer credit, and your contract decides who pays for the cleanup. "They asked us to disable it" is a fair defence only if it's written down and dated.
This is a contract question as much as a security one. Agency owner Ben Ryan's maintenance contract guide excludes data loss "where Client declined a backup upgrade recommendation (document these in writing)". It also gives the agency a 7-business-day window after which it "may remove the affected plugin to protect site security."
You don't need those exact clauses. You need some version of three things: a way to record a client declining your advice, a right to change what you cover, and a termination clause with a notice period. Our guide to security in your maintenance plan covers the scope side.
The paper trail to build before you fire a client
Firing a client should feel obvious by the time you do it, because the record already says why. Each step below gives the client a real chance to fix things. Most clients do, at step one or two. The ones who don't have made the decision for you.
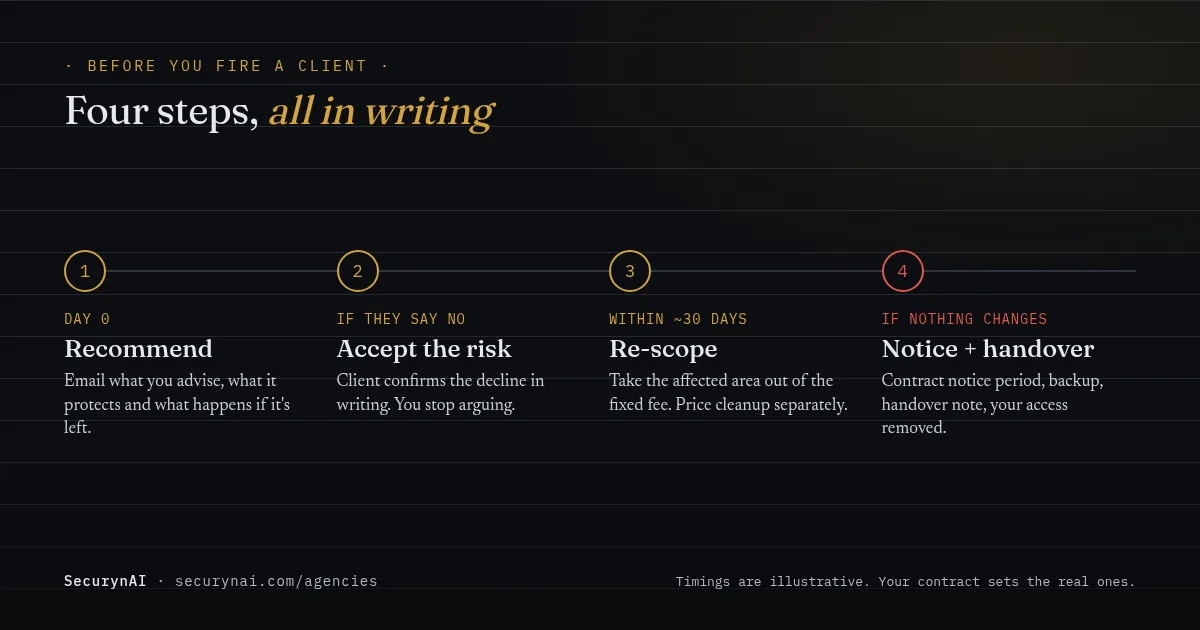
Step 1: put the recommendation in writing
An email is enough. Say what you recommend, what it protects against in one plain sentence, and what happens if it's left. Date it. A phone call or a chat message that scrolls away isn't a record, so follow every call with a short email that repeats what was agreed.
Step 2: if they say no, get the no in writing
A written "no" turns a disagreement into a decision with an owner. Don't argue a third time. Send a short risk-acceptance email that states the choice back to them and asks them to confirm. Here's a version you can copy.
SubjectConfirming your decision on [setting] for [Site Name]
Hi [Client Name],
Thanks for talking this through. To confirm: you've asked us to [turn off two-factor login / hold plugin updates / keep the shared admin login] on [Site Name], against our recommendation.
What this means: [one plain sentence, e.g. "Anyone who gets hold of a team password can log in as an administrator."]
What we'll do: we'll make the change on [date]. We'll keep monitoring the site as usual, but we can't protect against the risk above while it's in place.
What we can't cover: work to fix problems caused by this setting falls outside your plan and would be billed at [rate or "our incident rate"].
Please reply "confirmed" so we both have this on record. We'll raise it again at your next review on [date].
[Your name]
Step 3: re-scope what you cover
If the risky setting stays, change the agreement to match reality. Take the affected area out of your fixed-fee plan, price cleanup as separate work, and say so in writing. An incident-response retainer is one way to price that, and our guide to the real cost of a hack cleanup helps you set the rate.
Step 4: notice, if nothing changes
If the pattern keeps growing after re-scoping, it's time. Give the notice your contract requires, with a reason that's specific and calm: a named, ongoing security risk you're no longer willing to answer for. Avoid a list of grievances. One clear reason is harder to dispute than ten.
Quick check: keep, re-scope or fire this client?
Answer these about one client, honestly, using what's in writing rather than how you feel this week.
- Have they declined the same security recommendation more than twice?
- Did they refuse to confirm a decline in writing?
- Have they asked you to switch off login protection, two-factor login or the firewall?
- Do people you can't name have admin access to the site?
- Have they installed pirated plugins or themes, or refused to remove them?
- Are they behind on paying for the maintenance that keeps the site patched?
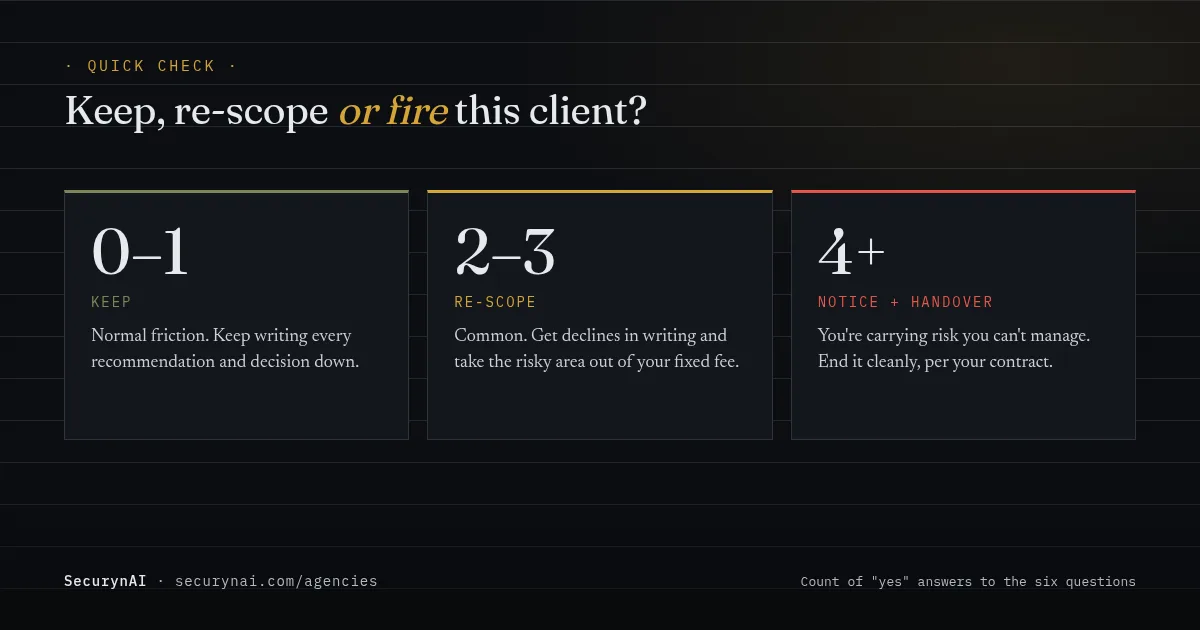
Zero or one yes: keep them. Keep writing things down. Two or three is common, and re-scoping usually settles it. Four or more, especially with question 2 or 5, means you're carrying risk you can't manage. That's when ending the client relationship protects you both.
How to end a client relationship without leaving a mess
A rushed exit can create a bigger problem than the client did. A site left with your old logins, alerts still going to your inbox and no backup in the client's hands is a liability with your name on it. End it the same way you'd end any contract, just more carefully.
SubjectEnding our maintenance agreement for [Site Name]
Hi [Client Name],
I'm writing to give [notice period, per our agreement] notice that we'll stop maintaining [Site Name] on [end date].
The reason is [the specific setting or practice], which we've discussed on [dates]. While it's in place, we can't take responsibility for the site's security, and we don't think it's fair to keep charging you as if we could.
Before [end date] we'll send you a full backup, a list of every account and service the site uses, and a short handover note for whoever looks after it next. Your final invoice will be [amount, or "for work up to the end date"].
[Your name]
- Hand over a full, recent backup and confirm the client can open it.
- Write a one-page handover note: hosting, domain, plugins with licences, open security issues and the decisions they declined.
- Remove your agency's admin accounts and API keys, and ask the client to change any password you knew.
- Point security alerts and notification emails at the client's address, not yours.
- Keep your own copy of the paper trail and the handover note, in case questions come later.
Our offboarding playbook has the full access-revocation checklist. If the site is already compromised when you leave, finish or hand over the cleanup first, and use our guide to explaining a hack to a client for that conversation.
How SecurynAI helps you keep the record straight
We at SecurynAI should be clear about where we fit. The plugin won't tell you to fire anyone, and it doesn't replace your emails. What it gives you is a dated, per-site record of the site's security state, so "the client turned it off in March" is something you can show, not just say.
What the free SecurynAI plugin records on each site
- Hardening checks, re-run daily and whenever you open the Hardening page. File editing in wp-admin, open user registration and XML-RPC each show as a check that passes or fails, and the Dashboard shows "X of Y checks passing" with the change this week.
- A daily two-factor check that flags each administrator with no recognised two-factor plugin set up. If a client turns it off, the finding comes back.
- An activity log of logins, failed logins, new users and role changes, plugin and theme changes, and edits to key settings such as the admin email and user registration. You choose how long to keep it, from 1 to 365 days (7 by default), and the Export CSV button saves a copy.
- Opt-in email for new critical and high findings, sent to the addresses in Send alerts to under Settings > General.
The log also records changes to SecurynAI's own settings, with who made them and the old and new values. When someone dismisses a finding, they can type a reason, and the log keeps it with their name. Still, keep your risk-acceptance emails as the main record. The plugin shows what changed, not what the client agreed to.
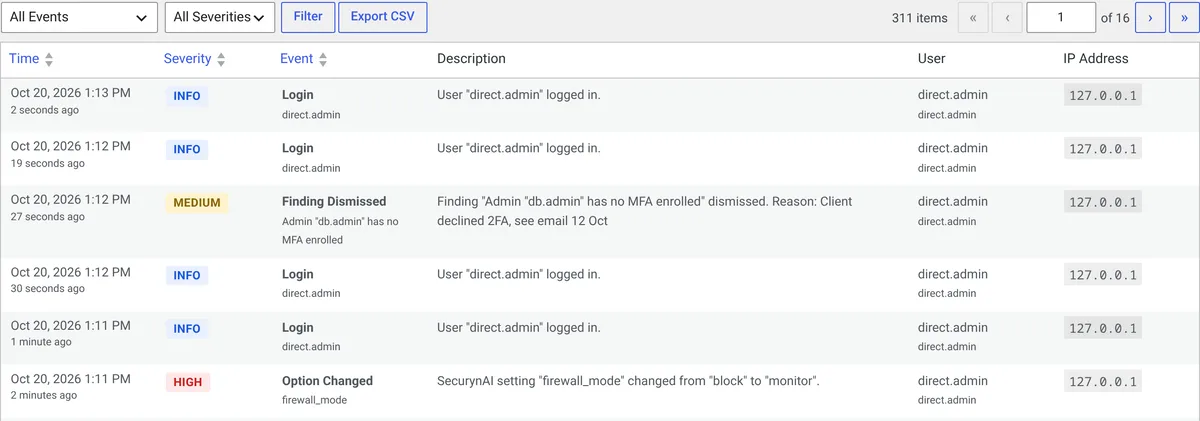
On the firewall: it starts in Monitor mode, where it logs matches without blocking until you switch the site to Block. Login lockout works in either mode. If a client asks you to switch Block back to Monitor, that's a decline worth putting in writing. The Audit Log then shows who made the switch and when.
What Pro adds for the paper trail
With Pro ($79 per site per year), fixes that need sign-off wait in an approval queue. When someone approves or denies one, Pro asks why and stores the answer with their name. Pro also keeps a 90-day audit archive that's hash-chained, so you can check it hasn't been altered, and download it.
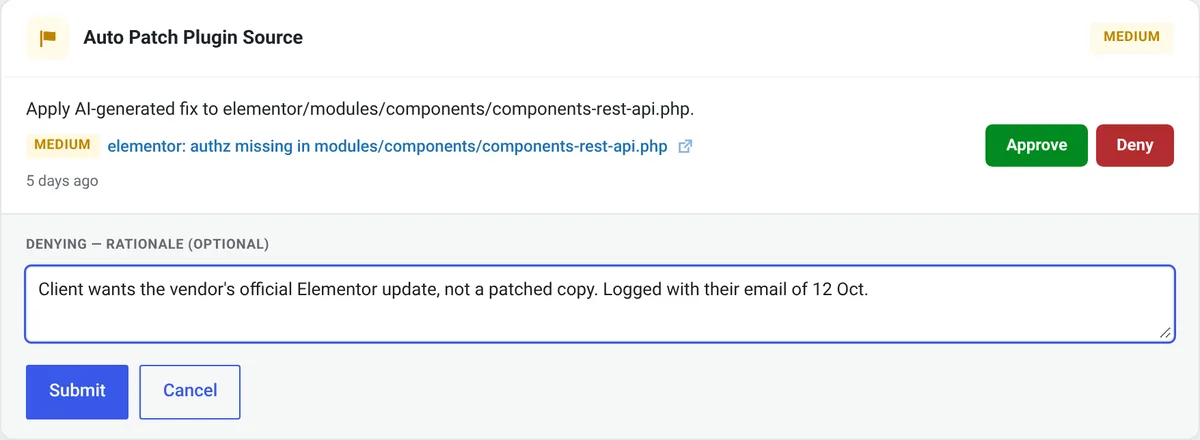
Pro's compliance export bundles findings, an audit trail excerpt and those policy decisions into a ZIP. It's built for compliance reviews, but it doubles as a clean "state of the site" record at handover.
On exit, export the free Audit Log as CSV for your own copy, then change Send alerts to to the client's address, so their alerts, approval emails and daily fix summaries stop reaching you.
Firing a risky client: FAQ
Can I fire a client in the middle of a maintenance contract?
Usually, if your contract has a termination clause, and most give either side a notice period. Read yours first: it decides the notice, what you owe on exit and what happens to prepaid months. If the contract is silent or the client disputes it, talk to a lawyer where you're based before you send anything.
Am I responsible if the site gets hacked after I leave?
Generally not for what happens after a clean, documented handover, but that depends on your contract and local law, so this isn't legal advice. What protects you in practice is a dated handover note, rotated passwords, your accounts removed and the client confirming they received everything. Without those, it's your word against theirs.
How do I tell a client their decisions are a security risk without insulting them?
Talk about the site, not the person. Name the specific setting or habit, say what it exposes in one plain sentence, and give them a choice: fix it, or accept the risk in writing. Most clients pick one of the two once it's put that way, and the conversation never gets personal.
Should I keep hosting or backups for a client I've fired?
Only for an agreed, short handover window, and say so in writing. Holding hosting or backups indefinitely keeps you tied to a site you no longer control. Give the client a full backup and their accounts, set an end date for anything you still host, and delete your copies when that date passes unless your contract says otherwise.
For the rest of the client-side process, from pricing to reporting, see the Agency Playbooks hub. If you're cleaning up access before a handover, our guides to an admin user you didn't create and privilege drift cover the checks.
Want a dated record of each client site's security, before a disagreement starts? Install the free plugin, point its alerts at your agency inbox, and let its checks and activity log keep the history.
Install free →