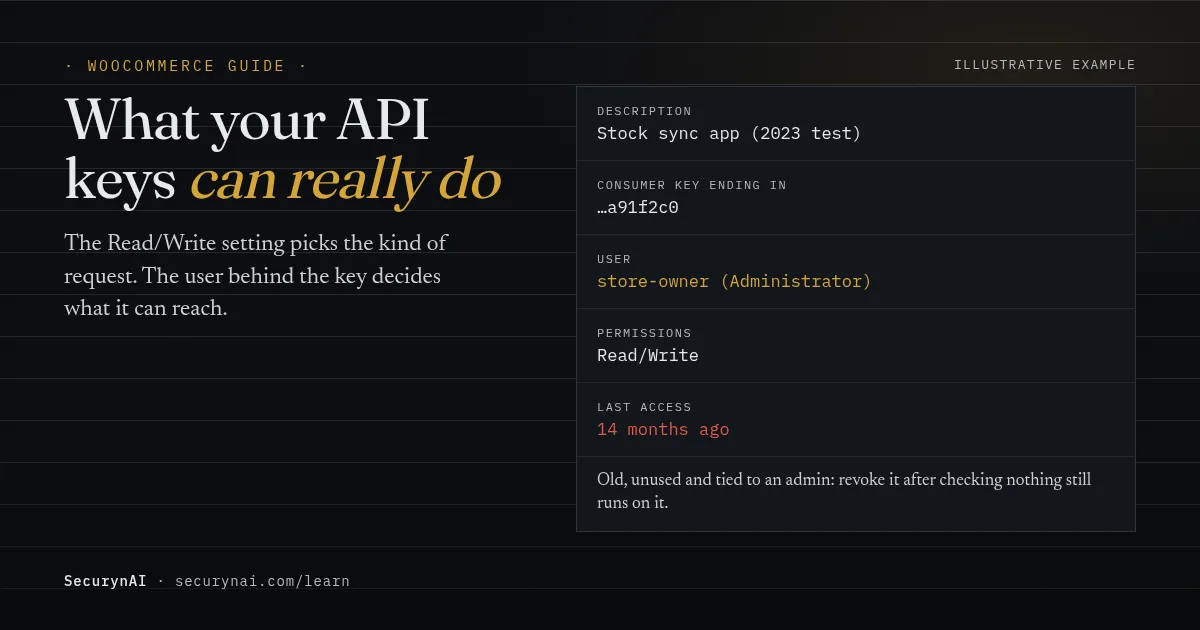
A WooCommerce API key is a consumer key and secret that lets another app read or change your store without logging in, acting as the WordPress user it was created for. Inventory sync tools, accounting apps, mobile apps and automation services all connect this way.
WooCommerce REST API security mostly comes down to two choices you make when you create WooCommerce API keys: which user the key belongs to, and which permission it gets. Most stores get the second one right and the first one wrong. If you're just checking your setup, start with the audit further down. It takes about ten minutes.
What can a WooCommerce API key actually reach?
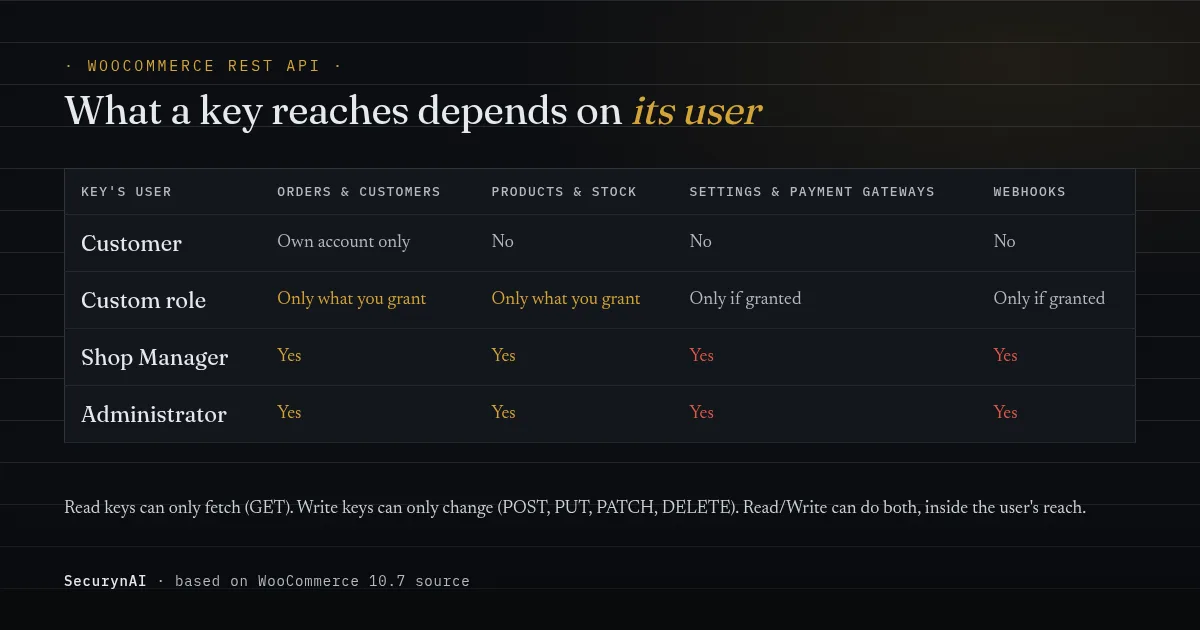
Everything its user can reach in WooCommerce, and nothing that user can't. WooCommerce's authentication docs say use of the API with generated keys "will conform to that user's WordPress roles and capabilities." The permission dropdown never widens or narrows what data the key can see.
The permission setting decides the kind of request. In WooCommerce's own code, a Read key may only fetch (GET and HEAD). A Write key may only create, change or delete (POST, PUT, PATCH and DELETE). Read/Write may do both. A request of the wrong kind is refused before it runs.
Keys also only work on WooCommerce's part of the API: addresses under /wp-json/wc/, plus extensions that opt in with a wc- prefix. A key can't log in to wp-admin or call the rest of WordPress's API. That's a useful limit, but WooCommerce's part covers your orders, customers and products, which is most of what matters.
Is a read-only key safe?
Safer, not safe. A Read key tied to an administrator can still download every order and customer record: names, emails, phone numbers and addresses. If that key leaks, nothing changes on your store, but your customer list walks out the door. Our guide to securing WooCommerce customer data covers what that means for you legally.
Why Shop Manager isn't the least-privilege choice
The common advice is to give integrations a Shop Manager account instead of an admin one. That's better than admin, but Shop Manager can still change store settings, payment gateways and webhooks through the API. WooCommerce gates all three on one permission, manage_woocommerce, and Shop Manager has it.
Webhooks are the part worth pausing on. A webhook sends store events, such as new orders, to a URL you choose (see WooCommerce's webhooks documentation). So a write key on a Shop Manager account can quietly add one more destination for your orders. That's not a flaw in WooCommerce. It's simply what that role is allowed to do.
The default advice can be even broader. In a WordPress.org support thread, a store owner's app failed with a Customer account, and the reply suggested apps "should be connected to someone who has an admin account." For a full-store tool, that may be fair. For a one-job tool, it's far more reach than needed.
When a custom role makes sense
For a tool with one job, such as syncing stock, a custom role with only the product permissions it needs is tighter. Role-editor plugins can build one. When a store owner asked on the WooCommerce forum whether keys work with third-party roles, a developer who tested it on staging replied, "It should work with other roles added to WordPress."
Test the integration on a staging copy first. Too few permissions show up as errors like "Sorry, you cannot list resources," and the fix is to add the one permission it needs, not to jump back to admin. As a WooCommerce volunteer put it in another support thread, "a 'Customer' can't view orders, even with API keys."
How to set up a WooCommerce API key safely
One integration, one user, one key. That way you can see which app did what, and switch one off without breaking the others. Here's the order we'd follow.
- Create a user for the integration. Name it after the app, like stock-sync, with the smallest role that works. Use an email address you control.
- Create the key for that user. In WooCommerce > Settings > Advanced > REST API, choose Add key, pick the integration user, and write a description that says what it's for, who asked for it and when.
- Pick the lowest permission. Reporting tools need Read. Only choose Read/Write if the app must both fetch and change data.
- Copy the secret once, into a password manager. WooCommerce's REST API guide says "The Consumer Secret is shown only once." Never paste it into email, chat or a code repository.
- Use HTTPS and send the key in a header. WooCommerce accepts the key in the URL, but OWASP's REST security guidance warns that API keys in URLs "can be captured in web server logs." Basic Auth in the header avoids that.
One catch with "Connect to WooCommerce" buttons. When an app sends you to an approval screen instead of asking for a key, WooCommerce creates the key for whoever is logged in when you click Approve. If that's you, as an admin, the app gets admin reach. Log in as the integration user first.
Why a leaked WooCommerce API key is easy to miss
A stolen password usually leaves traces: a login from somewhere new, a lockout, a session you don't recognise. An API key never logs in, so none of those signals fire. Requests with a valid key look exactly like your integration's normal traffic.
Keys also outlive the people who made them. Resetting a user's password doesn't touch their keys. Only revoking the key, or deleting its user, stops it. WooCommerce's code deletes a user's keys when that user is deleted, which is why offboarding a client site should include the key list, not just logins.
Leaks are common. GitGuardian's State of Secrets Sprawl 2026 counted 28,649,024 new secrets in public GitHub commits in 2025. Of valid secrets it found in 2022, 64% were still active four years later. A key pasted into a custom integration's code can sit there for years.
And stolen credentials are a main way in. Verizon's 2025 Data Breach Investigations Report found credential abuse was the leading first step in breaches, at 22%, and that third-party involvement in breaches doubled to 30%. Every integration you connect is a third party holding a credential.
How to audit your WooCommerce API keys in ten minutes
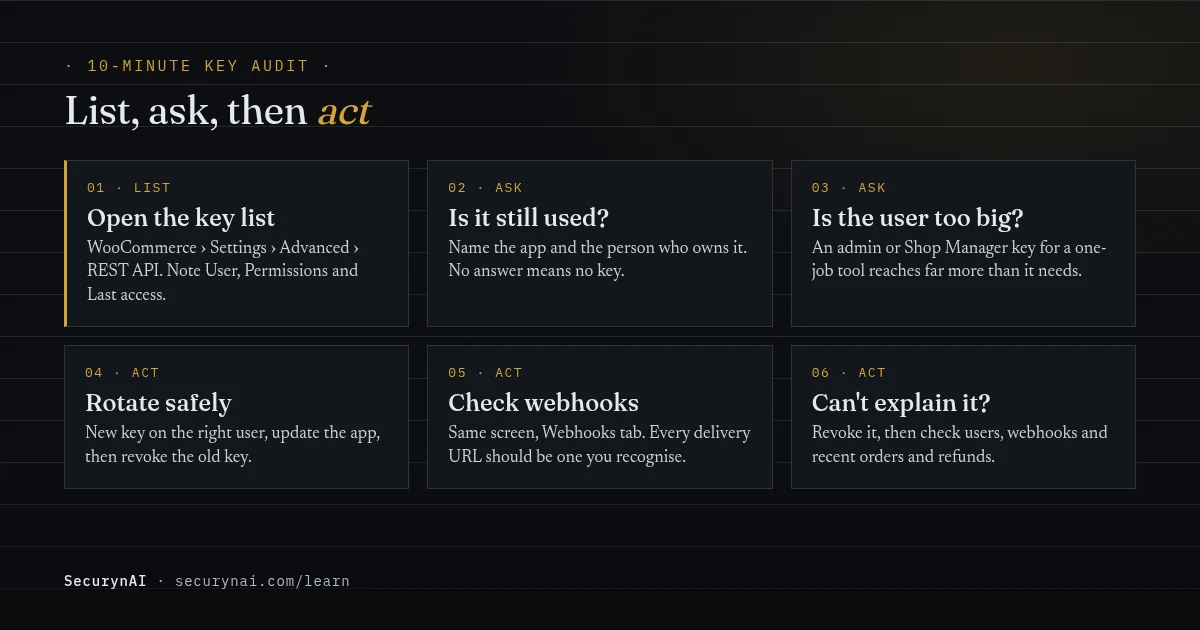
Look first, revoke second. Revoking a key takes effect at once, and any app still using it stops working, so confirm what each key is for before you remove it.
1. Read the key list
Open WooCommerce > Settings > Advanced > REST API. Each row shows a Description, the last characters of the consumer key, the User, the Permissions and the Last access time. Old keys with no recent access, keys tied to an admin, and descriptions nobody recognises are your shortlist.
2. Check the webhooks
On the same Advanced tab, open Webhooks. Every delivery URL should belong to a service you knowingly set up. An unfamiliar URL receiving order events deserves the same attention as an unknown admin account.
3. Optional: the same checks from the command line
If you have SSH and WP-CLI, these only read. Change wp_ if your table prefix is different, and set --user to an administrator's ID.
wp db query "SELECT key_id, user_id, description, permissions, truncated_key, last_access FROM wp_woocommerce_api_keys"
wp wc webhook list --user=1 --fields=id,name,status,topic,delivery_url
4. Rotate or revoke
To swap a key without downtime, create the new key on the right user, update the app, check it works, then revoke the old one. If you find a key or webhook nobody can explain, revoke it now. Then check for admin users you didn't create and review recent orders, refunds and product changes.
Where SecurynAI helps, and where it doesn't
We'll be straight about this. SecurynAI doesn't read WooCommerce's API key list or webhooks, so it won't alert you when a key is created. The audit above is still your job. What we at SecurynAI do cover is the WordPress around those keys.
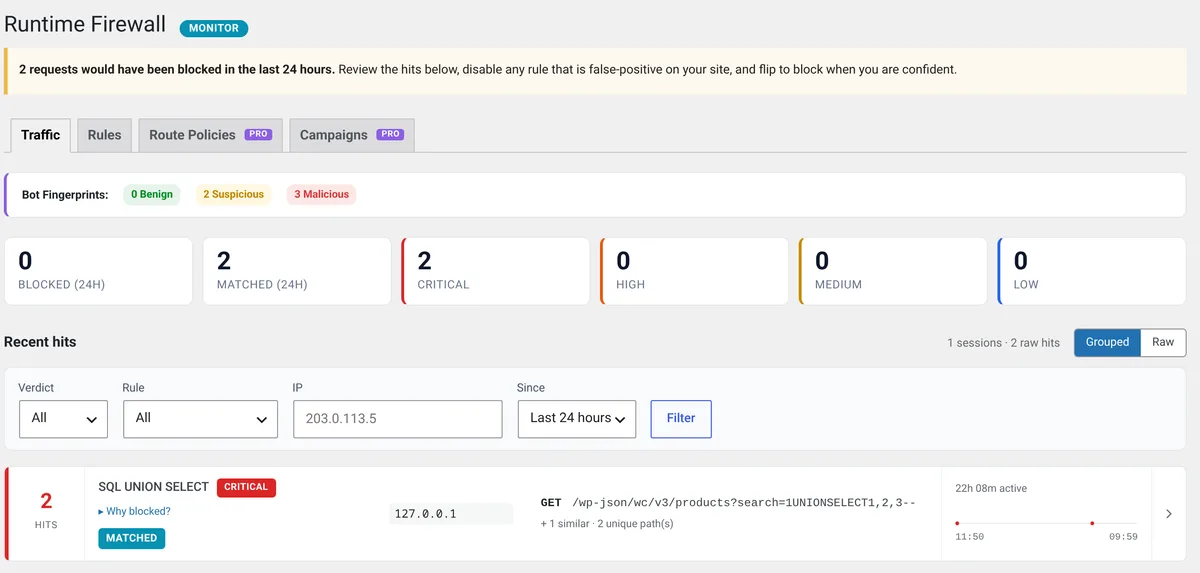
On the free plugin, the firewall checks incoming requests, including REST API calls and their JSON bodies, for attack patterns like SQL injection. It starts in Monitor mode, logging matches without blocking, until you switch it to Block. If someone promotes an integration user, the role check flags it: high for Shop Manager, critical for Administrator.
The free Audit Log records new users and role changes, and opt-in email alerts send you critical and high findings. Pro ($79 per site per year) adds WooCommerce checks on WooCommerce 8.3 or later. One flags stock changes by roles other than administrator or Shop Manager, outside normal purchases. That matters if your stock-sync user has a custom role.
Pro's behaviour monitoring also learns normal traffic on each REST API address, once it has seen 200 requests there, and flags requests that don't fit, such as a method never used on that address before. It can't judge brand-new addresses until they build history. None of this replaces revoking keys you don't need.
Quick check: are your WooCommerce API keys under control?
- Can you name the app and the owner behind every key on the REST API screen?
- Does every key belong to its own integration user, not an admin?
- Has every key been used in the last few months?
- Do you recognise every webhook delivery URL?
- Are secrets stored in a password manager, not email or code?
Five yeses means you're in good shape. Two to four is common and quick to fix this week. Fewer is a normal starting point. Our WooCommerce security checklist covers the rest of the store, and vetting WooCommerce extensions helps before you hand a new app a key.
WooCommerce REST API security FAQ
Does a read-only WooCommerce API key protect customer data?
No. Read only stops the key from changing things. If the key belongs to an administrator or Shop Manager, it can still fetch every order and customer record, including names, emails and addresses. Protect customer data by choosing a smaller user, not just a smaller permission.
What happens to a WooCommerce API key if I change or delete its user?
If you delete the user, WooCommerce deletes their API keys too, so they stop working. If you change the user's role, the key keeps working with the new role's access, because WooCommerce checks the user's permissions on every request. Resetting the user's password doesn't affect the key at all.
Is it safe to put the consumer key and secret in the URL?
WooCommerce accepts it over HTTPS, but it's better avoided. OWASP's REST security guidance says API keys shouldn't appear in URLs, because URLs get written to server logs. Send the key in the Authorization header with HTTP Basic Auth instead.
Should I turn off the WooCommerce REST API?
Usually not. WooCommerce's Store API, built for customer-facing cart and checkout features, runs on the same REST system and is public by design, so blanket blocking tends to break things. The protected parts of the API need a key or a logged-in user, so controlling your keys is the part that matters.
Want to hear about it the day an integration user gets promoted, or the day a request on your store looks like an attack? The free SecurynAI plugin starts watching from the moment you install it.
Install free →