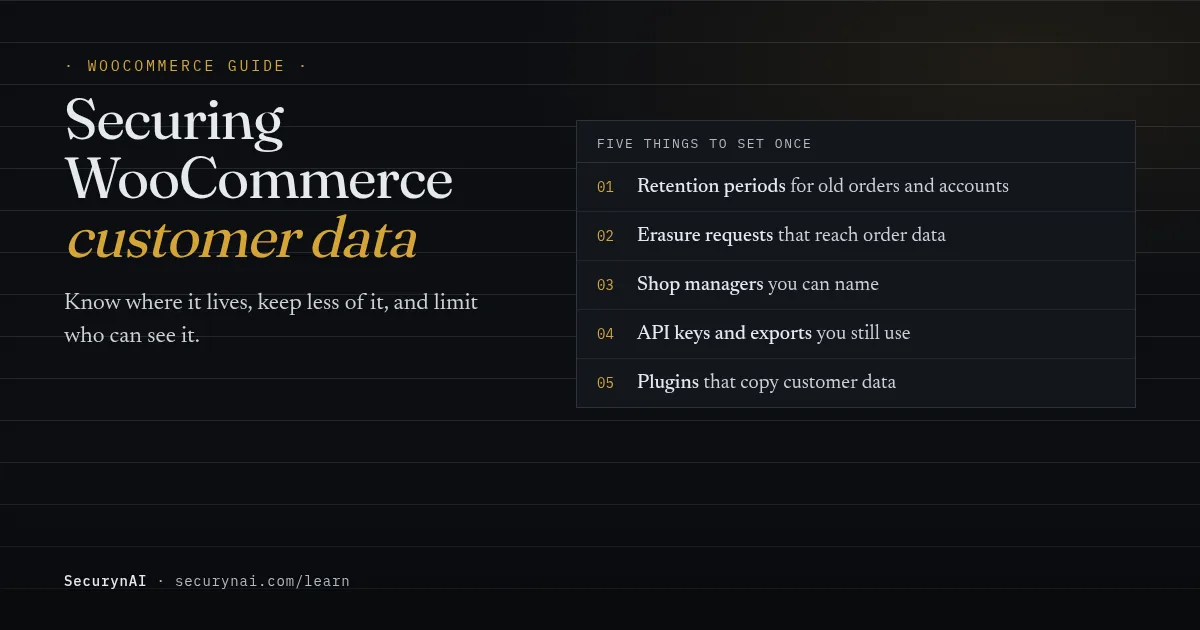
WooCommerce customer data is the personal information your store collects to sell and ship: names, emails, phone numbers, addresses, IP addresses and saved-card tokens, stored in your WordPress database. To secure WooCommerce customer data, you need three things: know where it lives, keep less of it with WooCommerce's personal data retention settings, and limit who can see it.
If a customer emailed tomorrow asking you to delete everything you hold about them, would you know where to look? Most store owners wouldn't, and that's fine. This guide walks through it once, so the answer is ready before anyone asks.
Our WooCommerce security checklist covers the store as a whole: payments, checkout scripts and card testing. This one stays narrow on purpose. It's about the customer records themselves.
What customer data does WooCommerce store, and where?
Customer data on a WooCommerce store isn't one thing in one place. It's spread across orders, accounts, saved cards and whatever other plugins copy. Where orders live depends on your setup.
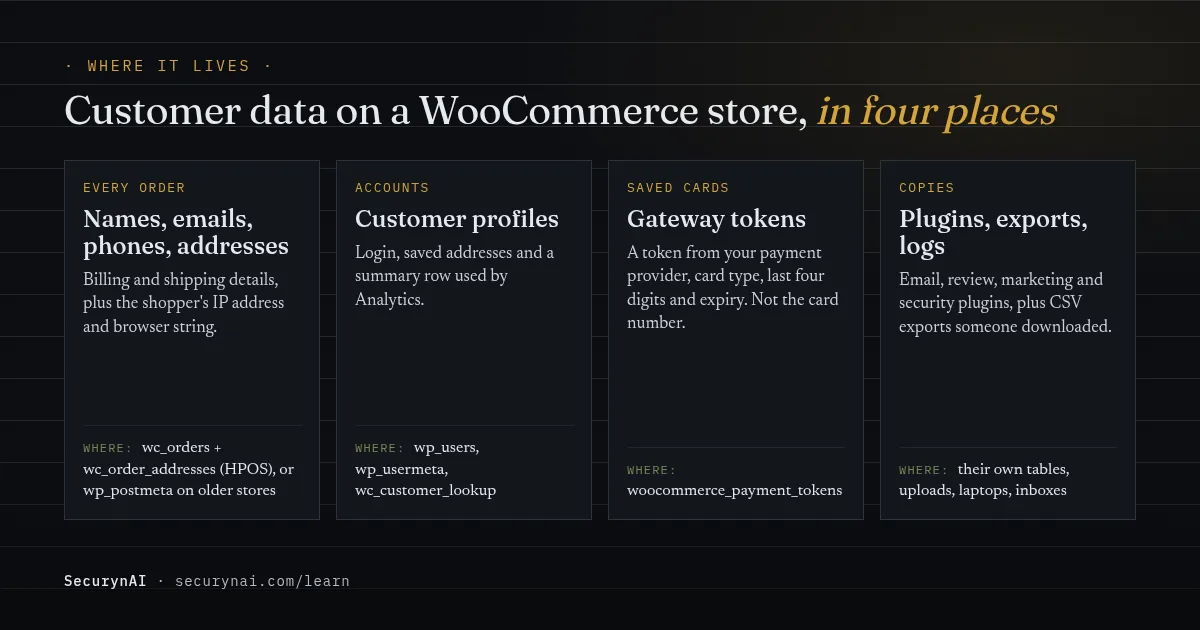
- Every order: billing and shipping name, email, phone and address, plus the shopper's IP address and browser string. Stores using High-Performance Order Storage (HPOS, the default for new stores since WooCommerce 8.2) keep these in the
wc_ordersandwc_order_addressestables. Older stores keep them inwp_postmeta. - Customer accounts: a WordPress user with saved addresses in
wp_usermeta, plus a summary row (name, email, city, postcode) inwc_customer_lookupthat Analytics uses. - Saved cards: a token from your payment provider, with the card type, last four digits and expiry. Not the card number.
- Copies: email marketing, review, abandoned-cart and security plugins often keep their own records. So do CSV exports sitting in someone's downloads folder.
The last item is the one people forget. Every plugin that touches customers is another place the same data lives, with its own retention rules, or none.
Why customer records are worth protecting first
Customer records are what a breach notice is written about. A defaced homepage is embarrassing. A leaked order table means emailing every customer, and maybe a regulator.
Most break-ins don't start with WooCommerce itself. Verizon's 2026 Data Breach Investigations Report found that 31% of breaches now start with software vulnerabilities, ahead of stolen passwords. On WordPress, those flaws sit mostly in extensions: Patchstack's State of WordPress Security in 2026 put 91% of 2025's 11,334 new vulnerabilities in plugins.
So the sensible approach is calm and boring. Keep fewer records, give fewer people access, and keep plugins updated. Data you've already deleted can't leak.
1. Set WooCommerce's personal data retention periods
Out of the box, WooCommerce keeps customer data forever. Under WooCommerce › Settings › Accounts & Privacy, the Personal data retention fields all start blank, and WooCommerce's own help text says blank means "retain this data indefinitely."
There are six fields: inactive accounts, and pending, failed, cancelled, refunded and completed orders. They don't all do the same thing, so it's worth knowing which is which before you fill them in.
| Setting | What happens after the period |
|---|---|
| Retain inactive accounts | Accounts with no login or order in that time are deleted. Their orders become guest orders. |
| Retain pending, failed or cancelled orders | Moved to the trash. |
| Retain refunded or completed orders | Personal data is anonymised. The order and its totals stay, so sales reports still add up. |
Two details catch people out. First, a trashed order is still in the database. In a WooCommerce support thread, one owner found that "as long as deleted orders remain in the trash, the customer records will remain too." Empty the trash.
Second, nobody is told. When an owner asked on the WooCommerce forum whether customers hear about the cleanup, support replied that "by default, WooCommerce does not automatically send notifications to customers." If your terms promise a notice, send it yourself.
Back up first. Anonymising can't be undone, and the cleanup runs daily once a field is set. Pick periods with your accountant: tax and refund rules decide how long completed orders must stay readable, and they vary by country.
2. Make sure erasure requests reach order data
WordPress has built-in privacy tools, and WooCommerce plugs into them. Tools › Export Personal Data and Tools › Erase Personal Data both work from an email address, and normally the customer confirms by clicking an emailed link first.
WooCommerce adds its own exporters and erasers for customer data, orders, downloads and saved payment tokens. But one default surprises almost everyone: an erasure request leaves order data alone unless you tick "Remove personal data from orders on request."
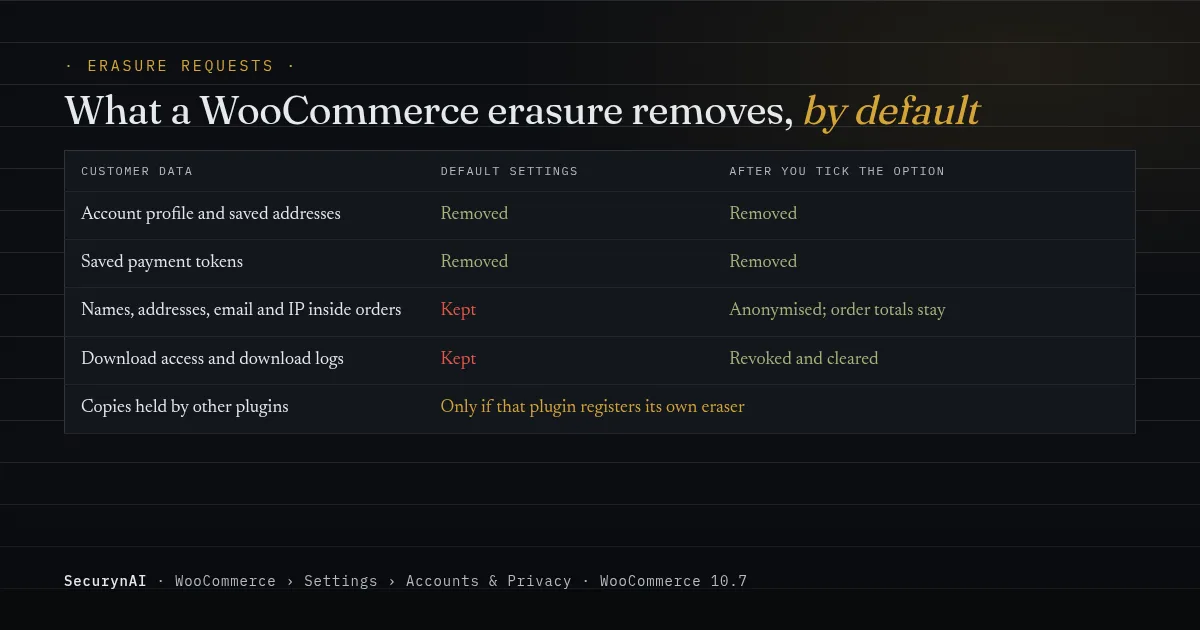
With that box ticked, orders are anonymised rather than deleted. A WooCommerce support rep put it plainly in an account erasure thread: the "actual orders made by the user won't be erased," but the personal details in them are removed, so your records still balance.
- Check: "Remove personal data from orders on request" and "Remove access to downloads on request" are ticked, if you serve customers with erasure rights.
- Check: your other plugins (marketing, reviews, abandoned carts) appear in the export. The WordPress export tool documentation warns it "ONLY gathers data from WordPress and participating plugins."
- Check: anything a plugin doesn't cover gets removed by hand, and you note what you did.
If you sell to people in the EU or UK, the GDPR's Article 5 asks you to keep personal data "for no longer than is necessary." Our GDPR guide for WordPress covers what happens when data leaks. This is general information, not legal advice.
3. Limit who can see customer records
Every account that can open an order can read a customer's address. No hacking is needed. That makes staff accounts the shortest path to customer data.
WooCommerce's roles documentation says Shop Managers can "view user details for all roles" and "view, edit, and delete orders, as well as process refunds." That's right for the person running the shop. It's a lot for someone who only packs boxes.
- Check: every Administrator and Shop Manager is a person you can name, who still needs it this month.
- Check: those accounts use two-factor login.
- Check: contractors and former staff lose access the day their work ends, not at the next tidy-up.
- Check: people with narrow jobs get a narrower custom role instead of Shop Manager.
Two alert guides fit here. Privilege drift explains what it means when an account quietly gains a bigger role, like a customer becoming a shop manager. A dormant admin account is a login nobody uses but anyone could steal.
4. Close the quiet exits: API keys, exports and plugins
Customer data can leave your store without anyone logging in. Three routes are easy to overlook.
REST API keys
WooCommerce's REST API docs say each key is "linked to a WordPress user on your site," and gets Read, Write or Read/Write access. A Read key made under a Shop Manager account can pull every order.
Review the list under WooCommerce › Settings › Advanced › REST API and revoke keys for services you've dropped. Our REST API security guide goes deeper.
CSV exports
An order export emailed to a bookkeeper is a copy of your customer list in someone's inbox. Export only the columns the job needs, delete old exports from the server and your downloads folder, and share through a link that expires rather than an attachment.
Plugins that copy customers
Review, wishlist, loyalty and abandoned-cart plugins often keep their own customer tables. They get less scrutiny than checkout, yet a flaw in one can expose the same names and emails. Our checklist for vetting WooCommerce extensions helps before you install one.
5. Guest checkout or customer accounts: which keeps less data?
Guest checkout keeps less, but not none. A guest order still stores the same name, address, email and IP. What you avoid is a standing account with saved addresses and a password that can be guessed or reused.
Neither is wrong. A store with repeat buyers has a good case for accounts. A store selling one-off items can make guest checkout the default and accounts optional. WooCommerce turns guest checkout on by default; the point is to choose, under Accounts & Privacy, rather than inherit.
Your WooCommerce customer data checklist
Work through this once, then repeat the monthly rows. None of it needs a paid tool.
| When | Check |
|---|---|
| Once | Personal data retention periods set (backup first), with your accountant's numbers. |
| Once | "Remove personal data from orders on request" and downloads options ticked, if you need them. |
| Once | A test export for your own email shows every plugin that holds customer data. |
| Once | Guest checkout or accounts chosen on purpose. |
| Monthly | Every Administrator and Shop Manager named, needed and on two-factor. |
| Monthly | REST API keys and old CSV exports reviewed, unused ones removed. |
| Monthly | Trash emptied, plugins updated, unused customer-data plugins deleted. |
What SecurynAI does, and doesn't do, for customer data
We at SecurynAI want to be clear about this, because it's easy to assume a security plugin guards everything. The free plugin watches the accounts and files around your customer data. It doesn't watch the customer records themselves.
On the free plugin
- Role changes: someone becoming a Shop Manager or Editor is flagged as high, and an Administrator as critical. Role changes and new accounts are also written to the Audit Log.
- Store hardening: the checks pass WooCommerce's Customer as a safe default role, and note when shoppers can register at checkout or on My Account.
- Files: every file in WordPress core and WordPress.org plugins, JavaScript included, is checked against official checksums. PHP files in themes and other plugins are fingerprinted, so a changed or new file is flagged.
- Malware patterns: PHP files under wp-content, including cache drop-ins, are checked against 13 bundled signatures, flagging clear obfuscation. It detects only, with no cleanup and no live feed.
- Known flaws: WooCommerce and your plugins are checked against a public vulnerability feed.
- Firewall: it starts in Monitor mode, logging attacks without blocking until you switch it to Block. Login lockout works in either mode.
- Records: opt-in email for critical and high findings, and an Audit Log you can export as CSV, kept 7 days by default (up to 365).
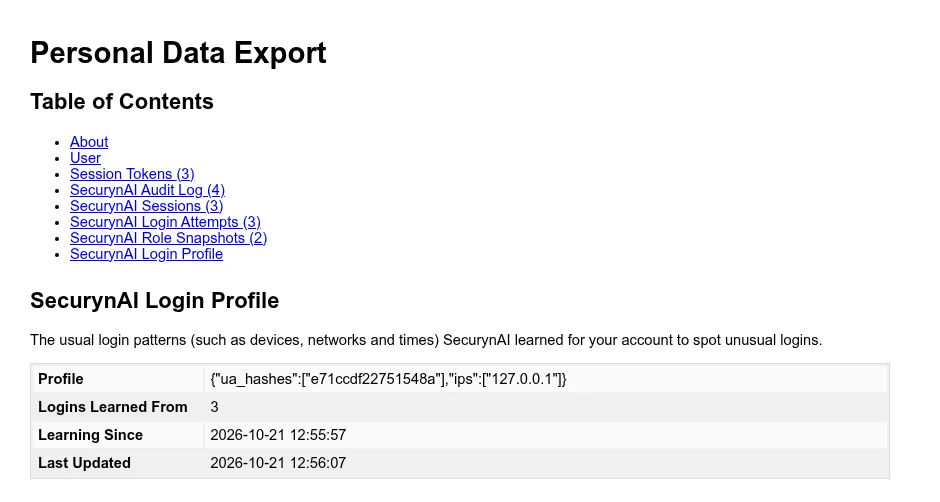
SecurynAI keeps personal data of its own, too: IP addresses and browser strings from logins, sessions and firewall events. It registers with WordPress's Export and Erase Personal Data tools, so a registered customer's request also covers SecurynAI's Audit Log, session, login and login-profile records for that account. Guest shoppers' IP addresses aren't covered.
On Pro ($79 per site per year)
Pro adds a compliance export: a ZIP of JSON evidence (findings, an Audit Log excerpt, and the last 90 days of incidents and policy decisions) mapped to GDPR, PCI DSS, SOC 2 or ISO 27001 controls. It's evidence for your own records, not a certification. See what Pro adds for the rest.
What you'll still need elsewhere
Neither version records who viewed or exported orders, or watches REST API keys. Neither scans theme or premium-plugin JavaScript, the database, plugin settings or outside scripts for skimmers. The retention, erasure and access settings above are WooCommerce's, and they're yours to set. SecurynAI doesn't replace backups, updates or those settings.
WooCommerce customer data FAQ
Does WooCommerce store customers' card numbers?
Not with a normal gateway setup. When a shopper saves a card, WooCommerce keeps a token from your payment provider plus the card type, last four digits and expiry. The full card number stays with the provider. If a plugin ever asks to store full card numbers on your server, treat that as a red flag.
If I delete a customer's account, is their data gone?
No. Their orders keep the names, addresses, email and IP address typed at checkout. Use Tools › Erase Personal Data instead, and tick "Remove personal data from orders on request" in WooCommerce › Settings › Accounts & Privacy first, or the orders stay as they were.
How long should a WooCommerce store keep order data?
Long enough for your tax, accounting and refund obligations, and no longer. The right number depends on where you trade, so ask your accountant. Then set it under Personal data retention; completed orders are anonymised, so your sales reports stay intact.
Does SecurynAI store my customers' personal data?
It stores IP addresses and browser strings from logins, sessions, firewall events and the Audit Log, for logged-in accounts and visitors alike. It adds its records for registered users to WordPress's Export and Erase Personal Data tools, and the Audit Log is kept for 7 days by default.
Want to know the day someone on your store becomes a Shop Manager, or a plugin holding customer data gets a known flaw? The free SecurynAI plugin starts watching as soon as you install it.
Install free →