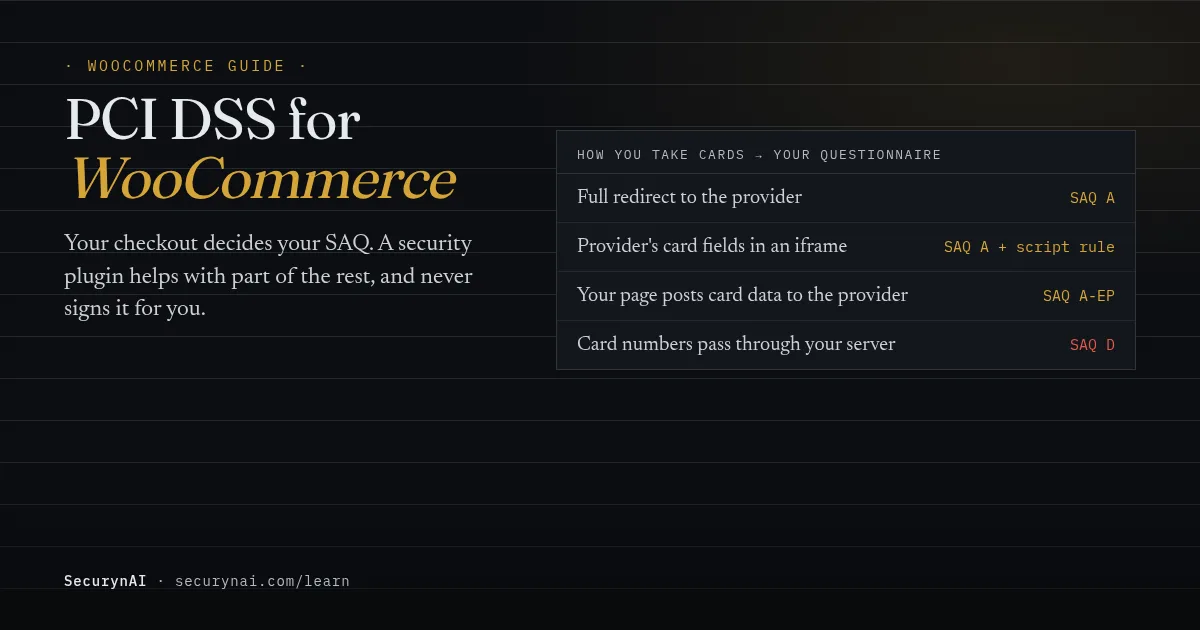
PCI DSS (the Payment Card Industry Data Security Standard) is the card industry's security standard for any business that accepts card payments, including a WooCommerce store that never sees a card number. For most stores, WooCommerce PCI compliance comes down to one yearly self-assessment questionnaire (SAQ). Which SAQ you file depends almost entirely on how your checkout takes cards.
So if your provider has asked you to "validate PCI compliance", don't panic. Most WooCommerce stores using Stripe, WooPayments, PayPal or Square land on SAQ A, the shortest form. This guide shows how to check that, what the 2025 SAQ A script rule means, and where a security plugin fits.
Is PCI DSS a law for WooCommerce stores?
No. PCI DSS is a contract requirement, not a law. It's written by the PCI Security Standards Council and enforced through the agreement you accepted with your payment provider. There's no government inspector. Your provider asks you to confirm compliance, usually once a year.
WooCommerce is clear about who holds the job. Its PCI DSS page says the core plugin "is not PCI certified, as it does not handle cardholder data or process payments directly." It also says "PCI DSS compliance is ultimately the responsibility of the store owner." Your gateway shrinks the work. It doesn't remove it.
Which SAQ does your WooCommerce checkout put you on?
Your SAQ follows the path a card number takes, not your store's size or revenue. Two stores with the same sales can file very different forms because one uses embedded card fields and the other built its own payment form.
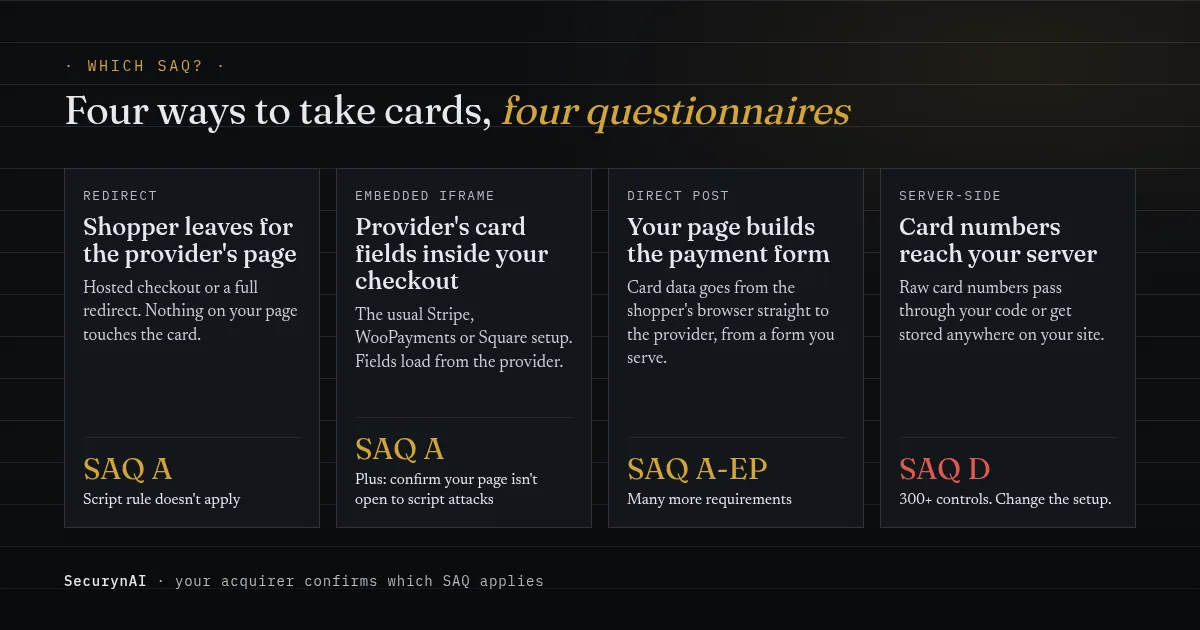
The PCI Council's own FAQ 1291 explains the split. With a redirect or an iframe, "the third-party payment processor produces the webpage that accepts payment data," so you can use SAQ A. If your own site produces the payment form and posts it to the processor, that's SAQ A-EP.
| How your checkout takes cards | Usual SAQ |
|---|---|
| Full redirect to the provider's hosted page (shopper leaves your site to pay) | SAQ A |
| Provider's card fields in an iframe on your checkout (the usual Stripe, WooPayments or Square setup) | SAQ A, plus the 2025 script rule below |
| Your own page builds the card form and posts it to the provider | SAQ A-EP |
| Card numbers pass through your server or get stored on it | SAQ D |
For the standard extensions, WooCommerce's Stripe extension docs say "most merchants using the Stripe extension can validate their PCI compliance via Self-Assessment Questionnaire (SAQ) A." They add that Stripe may ask for a different SAQ depending on your PCI level. So treat the table as a starting point and confirm with your provider.
If you're on SAQ D, fix the setup rather than the paperwork
Stripe's integration security guide says a business that handles raw card numbers "might be required to meet more than 300 security controls." Stripe's PCI FAQ says SAQ D usually means your integration passes card numbers through your own code. Moving to the provider's own card fields is usually far cheaper than meeting SAQ D.
What changed in SAQ A in 2025: the script rule
If your checkout embeds a provider's card fields, SAQ A now asks you to confirm your page isn't open to script attacks. A script attack means malicious JavaScript on your checkout page, such as a card skimmer that copies what shoppers type or swaps the real payment form for a fake one.
In January 2025 the PCI Council announced the change. It removed requirements 6.4.3 and 11.6.1 (payment page script management and tamper detection), plus 12.3.1, from SAQ A. In their place, merchants must "confirm their site is not susceptible to attacks from scripts." The new SAQ A took effect on 31 March 2025.
The Council's follow-up FAQ (February 2025) says there are two ways to meet it:
- Protect the page yourself, using techniques like those in requirements 6.4.3 and 11.6.1, deployed by you or by a third party.
- Get confirmation from your payment provider that its embedded form, set up the way it tells you to, protects your page from script attacks.
The rule doesn't apply if you fully redirect shoppers to the provider's site. For most small stores, the realistic route is the second one: ask your provider for that confirmation in writing and keep it with your SAQ.
Why this rule exists: skimmers don't need your files
A card skimmer only has to run on the page where cards are typed. In May 2026, Sansec reported attackers abusing a flaw in the Funnel Builder checkout plugin, used on more than 40,000 WooCommerce stores. They wrote fake tracking code into the plugin's "External Scripts" setting, which prints on every checkout page. Version 3.15.0.3 fixed it.
Stripe's guide makes the same point in calmer terms: every third-party script on a payment page makes your security depend on theirs, so keep them to a minimum. A checkout page with your gateway's fields and little else is easier to defend. Our guide to Magecart-style skimmers covers what to do if you think one is already there.
What's still your job on SAQ A?
Even on the shortest SAQ, the website that shows the checkout is yours to keep secure. WooCommerce's PCI page lists the basics: strong passwords and sensible roles for admins, SSL on checkout and account pages, WordPress and plugins kept up to date, and ASV scans if your processor requires them.
Updates matter most, because flaws mostly live in extensions. Patchstack's State of WordPress Security in 2026 counted 11,334 new WordPress vulnerabilities in 2025, with 91% in plugins. It found 46% had no patch available when they were made public.
The full PCI DSS sets a one-month deadline for critical patches (requirement 6.3.3). That's a useful benchmark even where your SAQ doesn't list it.
Store owners are often unsure where their part ends. On the WordPress.org forums, one owner using a Stripe plugin asked whether it would "ever expose my server to customer's payment information." Plugin support replied that card data goes to Stripe and isn't stored on the site, which is exactly what keeps that store near SAQ A.
Advice also conflicts. In a Square checkout thread, an Automattic engineer said the Square plugin is SAQ-A compliant. Another user suggested an approved ASV scan as well, and Square's plugin support said nothing more was needed beyond a valid SSL certificate. When forum answers disagree, your payment provider's answer is the one that counts.
Agencies get caught too. In a Helcim plugin thread, a developer whose client received PCI notices asked whether the official plugin "meets all website requirements." It never got a reply. If you build stores for clients, that's a question to settle with the provider before launch.
Your WooCommerce PCI checklist
Work through this once, then repeat the monthly rows. None of it needs a paid tool.
| When | Check |
|---|---|
| Once | Confirm how your checkout takes cards and which SAQ your provider expects. |
| Once | If you embed card fields, ask your provider for written confirmation about script protection. |
| Once | Ask whether your provider requires ASV scans, and note the answer. |
| Once | Check that no card numbers sit in order notes, emails, logs or form plugins. |
| Monthly | Update WooCommerce, your gateway and checkout plugins first (back up before updating). |
| Monthly | Review admins and shop managers. Remove anyone who no longer needs access. Keep two-factor on. |
| Monthly | View your checkout page source and confirm you recognise every script. |
| Yearly | File your SAQ and keep it with the provider's confirmation and your records. |
The wider store basics are in our WooCommerce security checklist, and customer records outside the card data are covered in securing WooCommerce customer data.
Where SecurynAI helps with PCI DSS, and where it doesn't
We at SecurynAI want to be straight about this, because people make real compliance decisions on it. No plugin makes a store PCI compliant, and ours doesn't either. SecurynAI covers parts of the security work behind your SAQ and keeps records you can point to. It doesn't fill in, file or sign anything.
On the free plugin
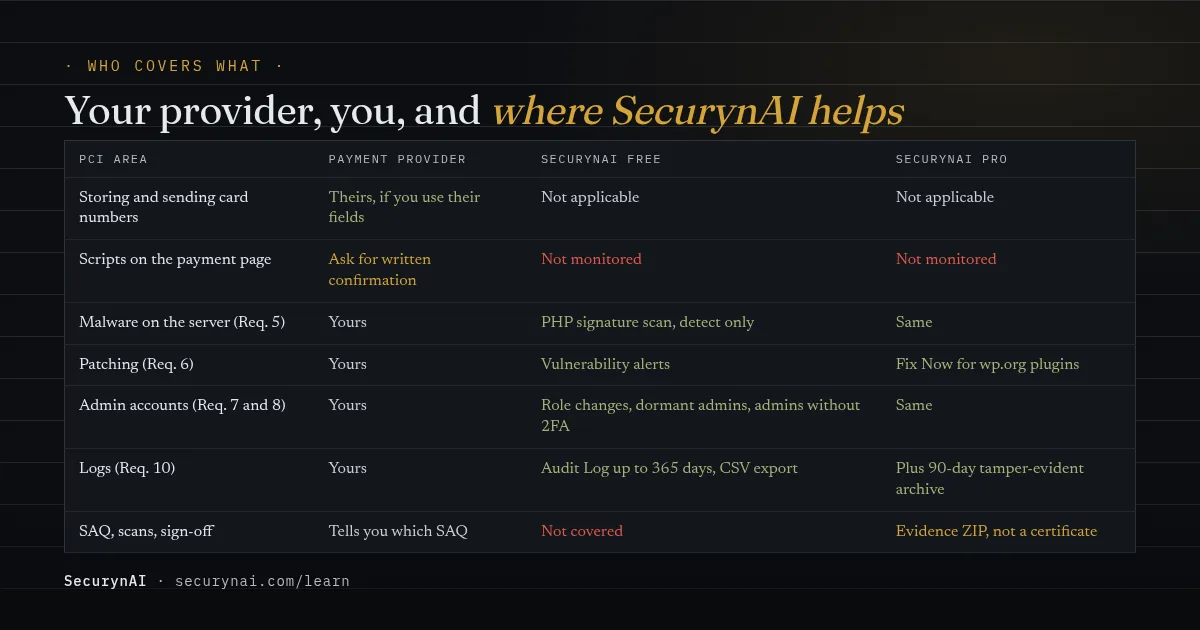
- Malware (requirement 5's area): the daily file scan checks PHP files under wp-content (including .phtml, .phar and cache drop-ins) against 13 bundled signatures and flags high-confidence obfuscation, like a decoder fed into eval. It detects only, with no cleanup and no live feed. It runs alongside checksum checks of core, plugin and theme files.
- Patching (requirement 6's area): WooCommerce and your other plugins are checked against a public vulnerability feed, wpvulnerability.net by default.
- Admin accounts (requirements 7 and 8): a promotion to shop manager is flagged high and to administrator critical. Admins with no two-factor plugin detected, and admins unused for 90 days (the default), get a medium finding. Repeated failed logins are locked out.
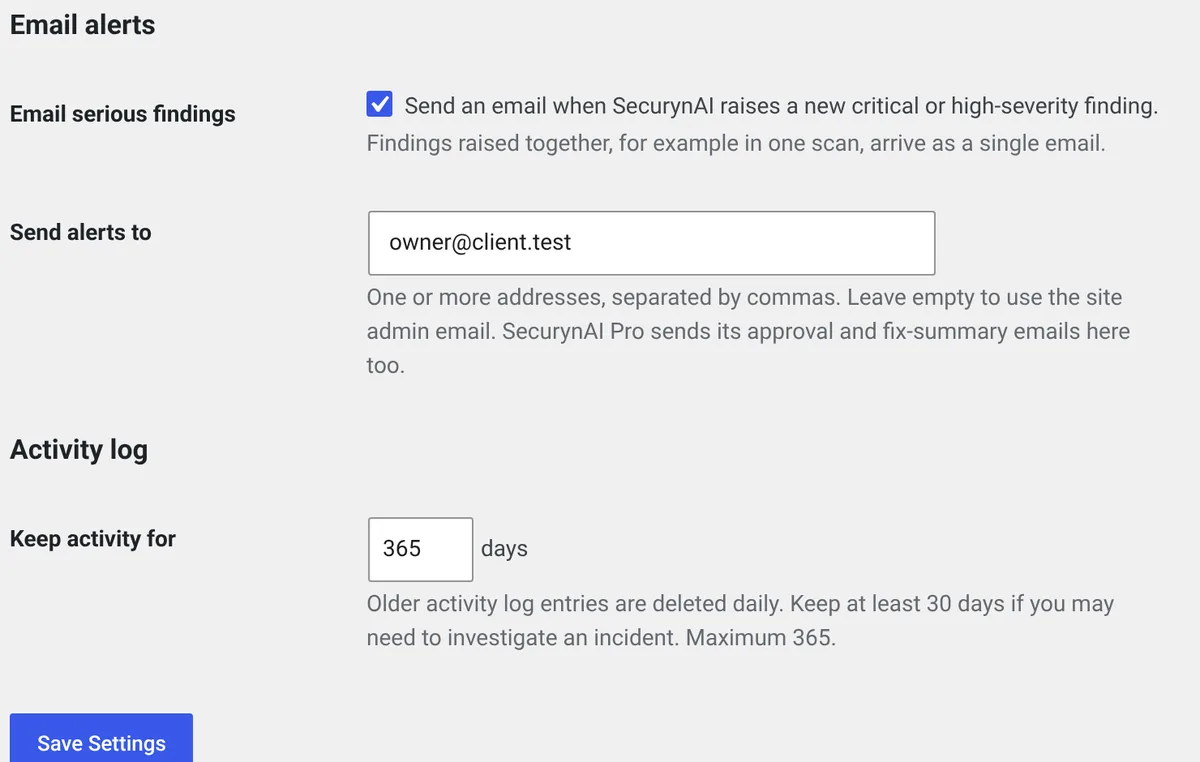
- Logs (requirement 10's area): the Audit Log records logins, failed logins, role changes, plugin installs and updates, and SecurynAI setting changes. It keeps 7 days by default, adjustable up to 365 under Settings › General. You can export it as CSV.
- Alerts: opt-in email for critical and high findings, off by default.
- Firewall: it starts in Monitor mode, logging attacks without blocking until you switch it to Block. Login lockout works in either mode.
Two settings are worth a look if you're keeping PCI records. The full standard asks for 12 months of log history (requirement 10.5.1), so set Audit Log retention to 365 days and export the CSV now and then to somewhere off the server. The 90-day dormant-admin check also lines up with the standard's 90-day rule for inactive accounts (requirement 8.2.6).
On Pro ($79 per site per year)
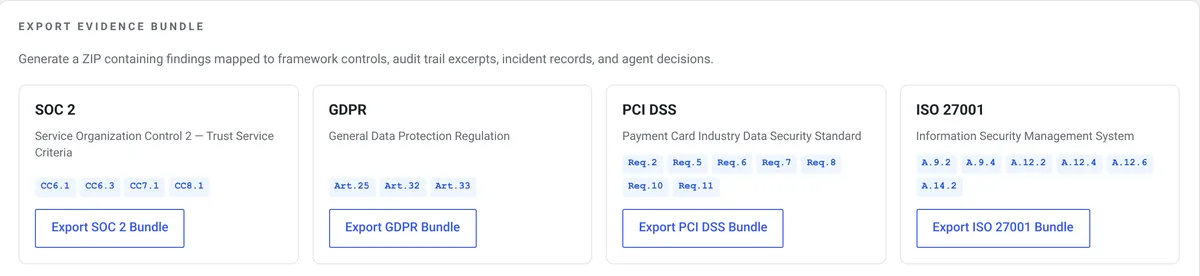
Pro adds a Compliance Export tab to the Audit Log. Choose PCI DSS for a ZIP of JSON files: findings mapped to PCI DSS v4.0.1 requirements 2, 5, 6, 7, 8, 10 and 11, an archived Audit Log excerpt with its integrity check, and 90 days of incidents and fix decisions.
It's evidence you can hand to whoever helps with your SAQ, not a certificate or an SAQ.
Pro also keeps Audit Log entries in a tamper-evident archive for 90 days after normal cleanup would delete them. Its Patch Queue can update WordPress.org plugins that have a fixed version with Fix Now. Themes, core and premium extensions show "Manual update required." See what Pro adds for the full list.
What you'll still need elsewhere
Neither version watches your payment page's scripts as shoppers' browsers receive them, so neither meets the SAQ A script rule. Free checksum checks do cover JavaScript files in WordPress core and WordPress.org plugins. Theme and premium plugin JavaScript, the database, plugin settings and outside scripts aren't checked, and a plugin setting is where the Funnel Builder skimmer lived.
Your provider's confirmation, ASV scans if required, and the SAQ itself stay with you and your provider.
PCI DSS for WooCommerce: FAQ
Is WooCommerce PCI compliant?
WooCommerce itself isn't PCI certified, because the core plugin doesn't handle card data or process payments. Once your store accepts cards, though, your store is in scope, and WooCommerce says compliance is ultimately the store owner's responsibility.
Does using Stripe or WooPayments make my store PCI compliant?
No, but it makes the job much smaller. Their card fields keep card numbers off your server, and WooCommerce says most merchants using the Stripe extension can validate with SAQ A. WooCommerce's WooPayments page says plainly that using it doesn't automatically make your whole site compliant.
Do I need an ASV scan for my WooCommerce store?
It depends on your SAQ and your payment provider. WooCommerce's PCI page says to run ASV scans if your processor requires them. Advice in support forums is mixed, so ask your provider directly and keep their answer in writing.
Can a security plugin make my store PCI compliant?
No. Compliance is an annual self-assessment you sign and your payment provider accepts. A plugin can cover parts of the security work behind it, such as malware checks, patch alerts, account monitoring and logs, and can give you records to point to.
Getting your store's records in order before the next SAQ? The free SecurynAI plugin starts logging admin activity and checking your files from the moment you install it.
Install free →