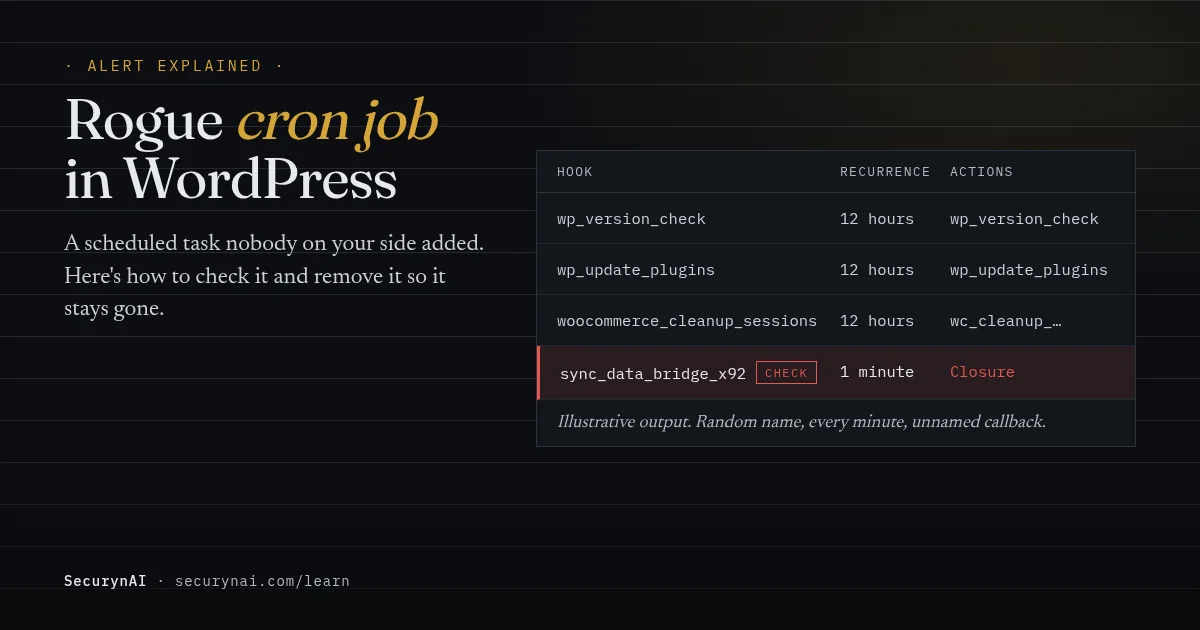
A rogue cron job is a scheduled task on your WordPress site that nobody on your side added. It runs code on a timer, again and again, without anyone logging in. That's why attackers like it: it can put back a deleted file or admin account long after you think the site is clean.
Maybe your host flagged it, a scanner listed it, or you spotted a strange name yourself. Don't delete anything yet. First, find out what the task actually runs and where that code lives. A suspicious WordPress cron job is a clue, and you want to keep the clue until you've followed it.
Is a rogue cron job serious?
If it's really rogue, yes. A malicious scheduled task means someone already ran code on your site, because that's the only way to add one. The task is the symptom. The way in, usually an outdated plugin or a stolen password, is the real problem.
Hidden extras are common after a break-in. Sucuri's 2023 Hacked Website Report found that 49.21% of the hacked sites its team cleaned had at least one backdoor, as Sucuri wrote in 2025. A cron job is one way to keep a backdoor alive.
And the ways in keep growing. Patchstack's State of WordPress Security in 2026 counted 11,334 new WordPress vulnerabilities in 2025, 91% of them in plugins. It also found 46% had no fix from the developer by the time they were made public.
When it's probably fine
- The task belongs to a plugin or theme you use, and its callback (the code it runs) is inside that plugin's folder.
- It's a leftover from a plugin you deleted, and it has no callback at all, so it does nothing when it runs.
When to act today
- You can't match the task to anything you installed, and it has a callback.
- It runs every minute or every few minutes, and nothing you use needs that.
- Files, admin accounts or redirects you already removed keep coming back.
- It turned up alongside a new admin user you didn't create or a changed core file.
Where does a rogue cron job hide?
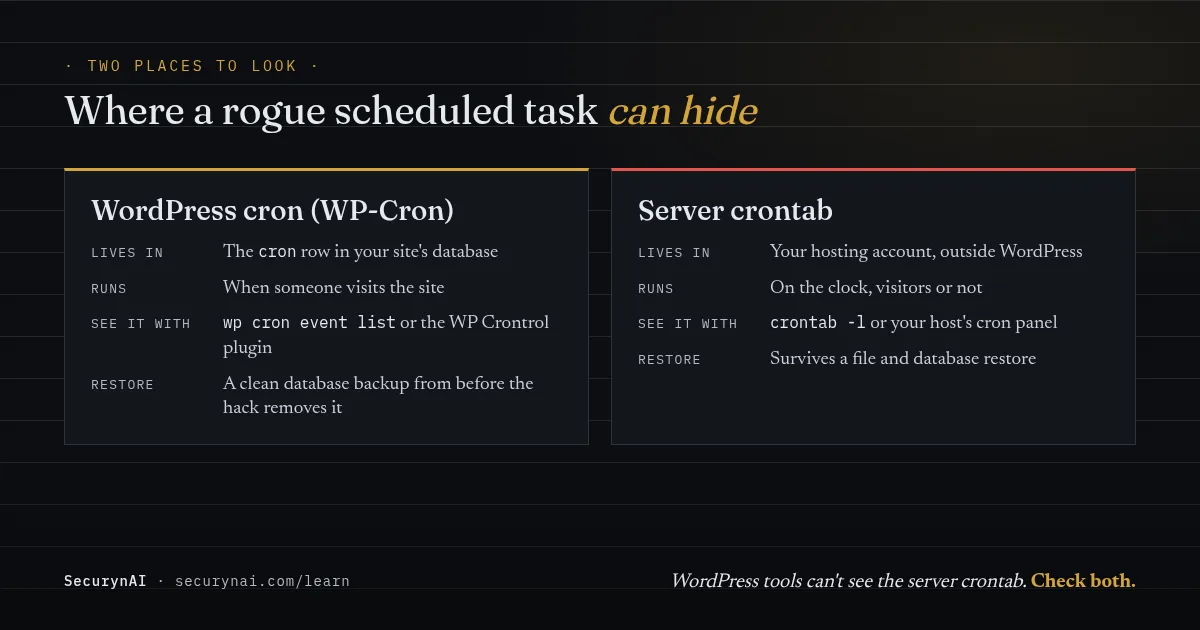
There are two kinds of scheduled task on most WordPress hosting, and they live in different places. Checking only one is the most common reason a cleanup doesn't stick.
The first is WordPress's own cron, or WP-Cron. The WordPress plugin handbook says it "works by checking, on every page load, a list of scheduled tasks to see what needs to be run." The list lives in your database. Monarx described malware in 2026 that used a WP-Cron job with a randomized name to re-create a hidden admin account.
The second is the server's own scheduler, the crontab on your hosting account. It runs on the clock whether anyone visits or not. In 2023 Sucuri documented server cron jobs that rewrote backdoors into WordPress folders, one of them "set to run every single minute." WordPress tools can't see these at all.
How to check a suspicious WordPress cron job
Look first, change things later. Everything in this section only reads. You can do it with WP-CLI over SSH, or from the dashboard with a plugin.
1. List what WordPress has scheduled
wp cron event list --fields=hook,recurrence,next_run_relative,actionsThe actions field shows the callback each task runs, or "None" if nothing is attached. Plain wp cron event list skips that column. If you'd rather click, the free WP Crontrol plugin shows the same list with callbacks and warns about events that have no action.
hook                          recurrence   next_run_relative   actions
wp_version_check              12 hours     3 hours             wp_version_check
woocommerce_cleanup_sessions  12 hours     5 hours             wc_cleanup_session_data
sync_data_bridge_x92          1 minute     now                 Closure
2. Read each line for warning signs
No single sign proves a task is bad. The callback tells you more than the name does. Here's how we'd read the columns:
| What you see | What it usually means |
|---|---|
| A familiar name | Normal if the callback lives in that plugin. Leave it. |
| Actions: None | Usually a leftover from a removed plugin. It does nothing when it runs, but find out where it came from. |
| A random name | Worth following up today if it has a callback. |
| Every minute | Rare for normal plugins. Check what it calls. |
| Actions: Closure | An unnamed function. Plenty of plugins do this, so you'll need to search the code. |
| Same name, many rows | Can be normal. Check the plugin's docs. |
Names can fool you in both directions. In a WordPress.org thread, a host traced heavy disk use to wp_image_process_cron. It looks like core, but WP Crontrol showed it belonged to the Astra theme. In another thread, SolidWP support explained that many itsec_cron rows are "expected behavior, not duplication."
3. Check the server's crontab too
Over SSH, crontab -l lists the scheduled jobs for your hosting user, as Sucuri suggests. On shared hosting, look for a "Cron Jobs" screen in your control panel instead. Most sites have none, or one that calls wp-cron.php. Anything that downloads a file, decodes text or writes into your WordPress folders needs explaining.
How to remove a rogue cron job so it stays gone
Delete the code first and the schedule second. If you only delete the event, the code that created it can simply add it back. Back up the files and database before you start, so you can undo a mistake.
- Save the list. Run
wp cron event list --format=json --fields=hook,schedule,interval,actions > cron-before.jsonso you have a record of what was there. - Find the code the task calls. Search your plugins, theme and
wp-content/mu-pluginsfolder for the callback's name. Code in a folder you don't recognise is the strongest sign. - Remove that code. Delete the bad file, or reinstall the plugin or theme from a fresh copy. Our guide to finding a webshell covers what else to look for nearby.
- Delete the event. Run
wp cron event delete sync_data_bridge_x92, using your hook's name. The WP-CLI docs say this "deletes all scheduled cron events for the given hook." - Check again tomorrow. Run the same list. If the hook is back, something else is re-adding it.
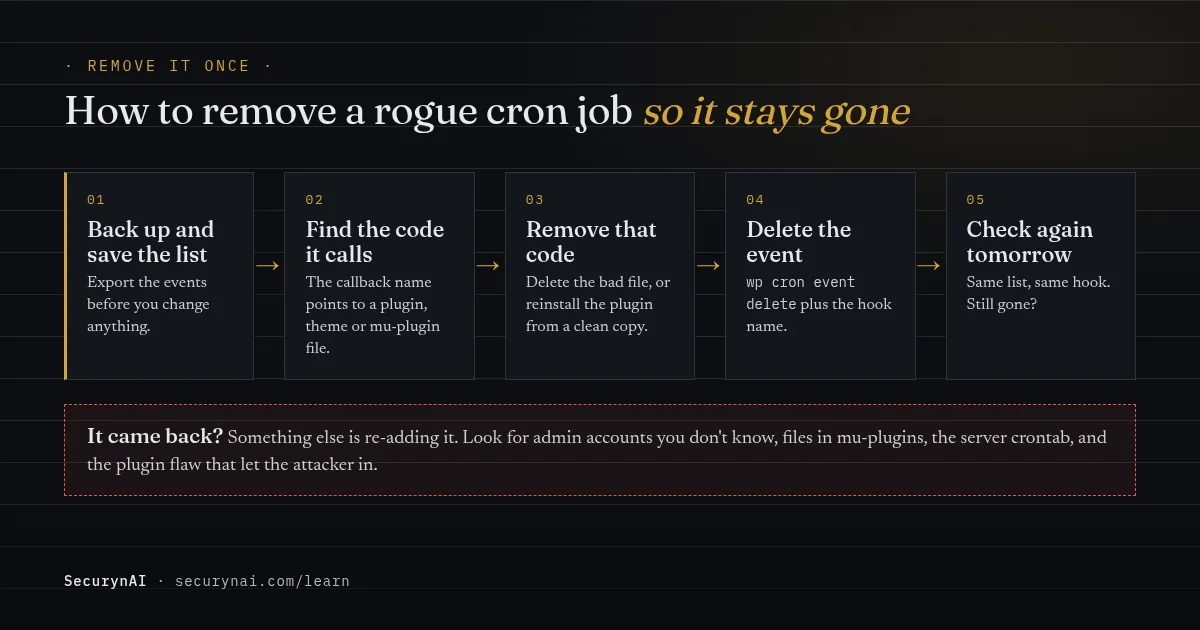
That "it came back" moment is common. One site owner in the WordPress.org support forums suspected their malware worked "with the cron job, adding new plugins to the Plugins folder twice a day." When that happens, look for unknown admin accounts, files in mu-plugins and the server crontab.
Then close the way in. Reset every admin password, update all plugins and themes, and remove the ones you don't use. Our malware removal guide walks through the full cleanup. If you look after client sites, our playbook on explaining a hack to a client helps with the email afterwards.
How SecurynAI checks your scheduled tasks
We at SecurynAI built a persistence check into the free plugin. After every file-integrity scan, which runs daily by default, it reviews your scheduled tasks alongside your admin accounts and mu-plugin files. You can switch the scan to weekly in settings.
It sends up to 50 scheduled hooks from WP-Cron and Action Scheduler to your own AI provider. The AI is told to flag only clear signs, like random-looking names, and to ignore core and well-known plugin tasks. Anything flagged shows up as a finding named Persistence indicator: cron: followed by the hook, with a severity and the reason.
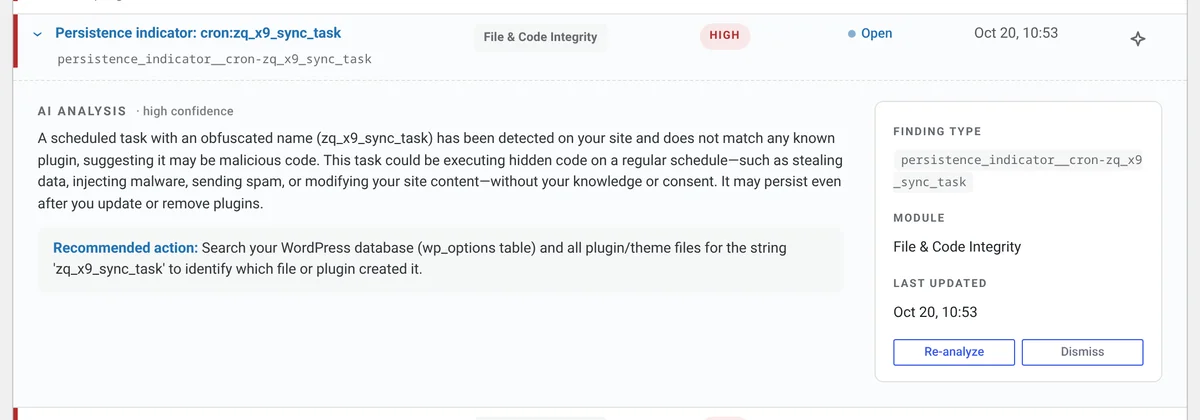
Here are the honest limits. This check needs your own AI key. Without one, the free plugin makes no cron findings, so check by hand with the steps above. It sends hook names and next run times only, not the code behind them. It can't see your server's crontab. And neither Free nor Pro deletes a scheduled task for you.
Pro ($79 per site per year) adds behavior monitoring for scheduled tasks. Once it has watched a task run 30 times, it learns that task's normal schedule, arguments and timing, and flags a sharp change. It doesn't flag a brand-new task the first time it appears, which is the free AI check's job.
None of this replaces backups you've tested or prompt plugin updates.
Quick check: could a rogue task hide on your site?
- Can you name the plugin behind every scheduled task on the site?
- Have you looked at the server's crontab, not just WordPress's list?
- Are all plugins and themes updated, with unused ones removed?
- Do you have a backup from before any recent trouble?
- Would you notice if a file you deleted came back?
Five yeses means you're in good shape. Two to four is common and quick to fix this week. Fewer is a normal starting point. Our WordPress hardening checklist is a good next step, and the guide to an outbound request to an unknown domain covers another sign of hidden code.
Rogue cron job FAQ
Can I stop a rogue cron job by disabling WP-Cron?
Not really. Setting DISABLE_WP_CRON in wp-config.php only stops page visits from triggering tasks. Your legitimate tasks stop too, the bad code is still on the site, and a server crontab entry keeps running. Remove the code and the event instead.
Is a cron event with no action dangerous?
On its own, usually not. An event with no callback does nothing when it runs, and most are leftovers from a plugin you removed. Delete it if you're sure where it came from. If you can't place it, treat it as a clue and check the rest of the site.
Will restoring a backup remove a rogue cron job?
A WordPress cron event lives in the database, so restoring a clean database from before the break-in removes it. A server crontab entry lives on the hosting account and survives a restore. Sucuri found server cron jobs that reinfected sites minutes after a clean restore. Our guide to restoring from backup after a hack covers the rest.
Does a hook name that starts with wp_ mean it's from WordPress core?
No. Any plugin, theme or attacker can choose any name. In one WordPress.org thread a busy wp_image_process_cron task turned out to belong to the Astra theme. Check the callback, not the name.
Want a second pair of eyes on your scheduled tasks after every scan, instead of checking by hand? Install the free SecurynAI plugin and add your AI key when you're ready.
Install free →