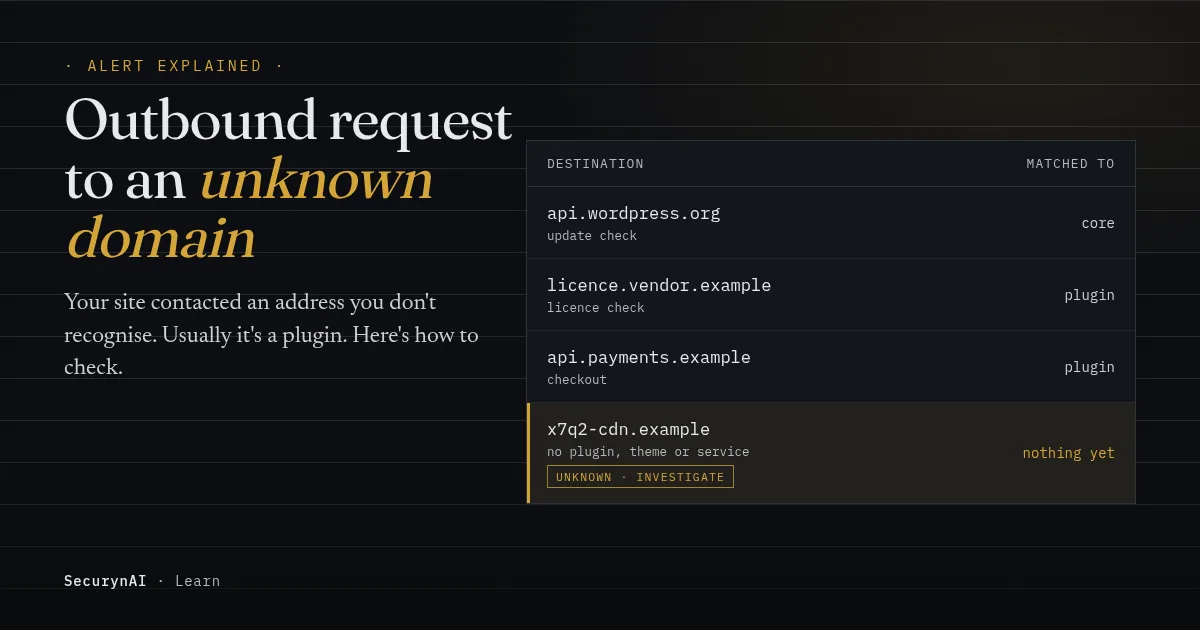
Your host sent a warning, or a log shows your site talking to a domain you've never heard of. Don't block it or delete anything yet. First, write down three things: the exact domain, roughly when the requests started, and who or what spotted them. Every step below depends on those.
An outbound request is any connection your site starts itself, rather than one a visitor sends to it. WordPress makes lots of them. It checks WordPress.org for updates, plugins validate licences, and stores talk to payment gateways. "Unknown" only means you can't match the domain to something yet.
Is an outbound request to an unknown domain a sign of a hack?
Usually not. Most unknown domains turn out to belong to a plugin, theme or service you installed. Premium plugins call their vendor's licence server. SEO plugins ping search engines. None of these domains look familiar until you go looking.
Even careful site owners have to ask. In one WordPress.org support thread, a user who wanted to lock down outside requests had to ask Yoast's team which hosts the free plugin contacts. The answer: Google and Bing for sitemaps, plus a couple of integrations. Nothing in the dashboard would have told her.
When it is malicious, though, it's often the part that does the damage. In Sucuri's 2023 Hacked Website & Malware Threat Report, the most common WooCommerce card skimmer (found on 37.5% of sites with ecommerce malware) was server-side code that "contacts a third-party malicious server" to fetch the skimmer it injects into checkout.
The same report found at least one backdoor on 49.21% of the compromised sites Sucuri cleaned in 2023. Some malware it describes works by asking a remote server what to do next, such as which domain to redirect visitors to. That's exactly the kind of traffic that shows up as an unknown domain.
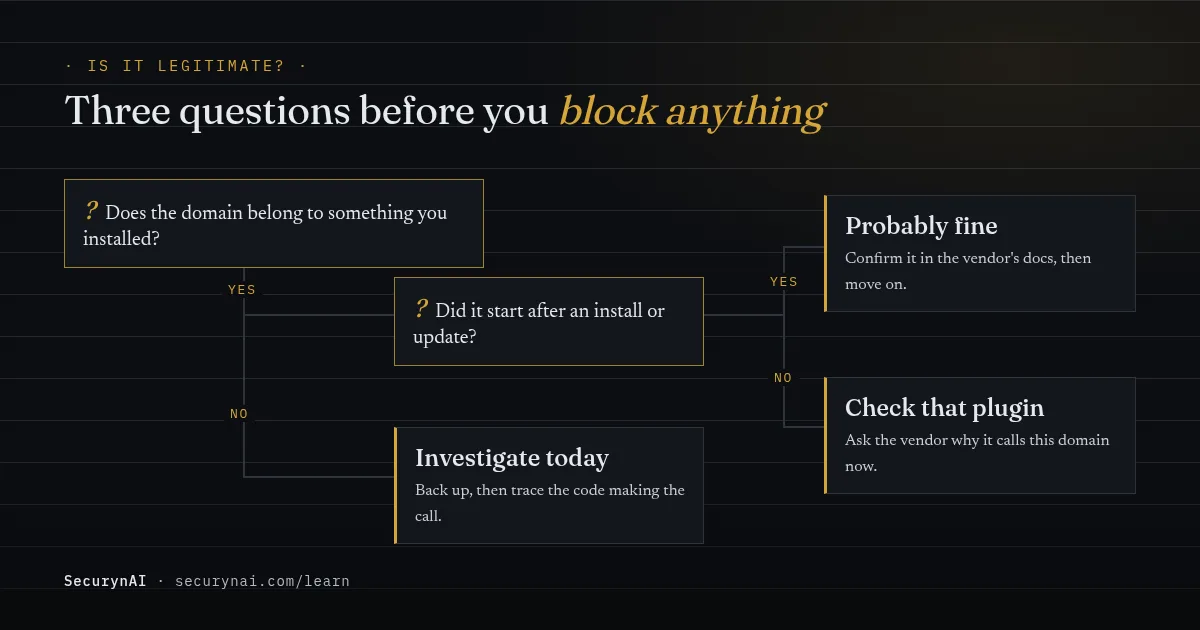
When it's probably fine
- The domain belongs to a plugin, theme or service you use, and its docs or support team confirm it.
- The requests started right after you installed or updated something.
- It's a well-known service: a CDN, payment processor, email provider or AI API you've connected.
When to act today
- The domain looks random, or it was registered very recently.
- The requests began when nobody changed anything on the site.
- Your host has blocked outgoing connections or suspended the account.
- You're also seeing other odd signs, like an admin user you didn't create or changed core files.
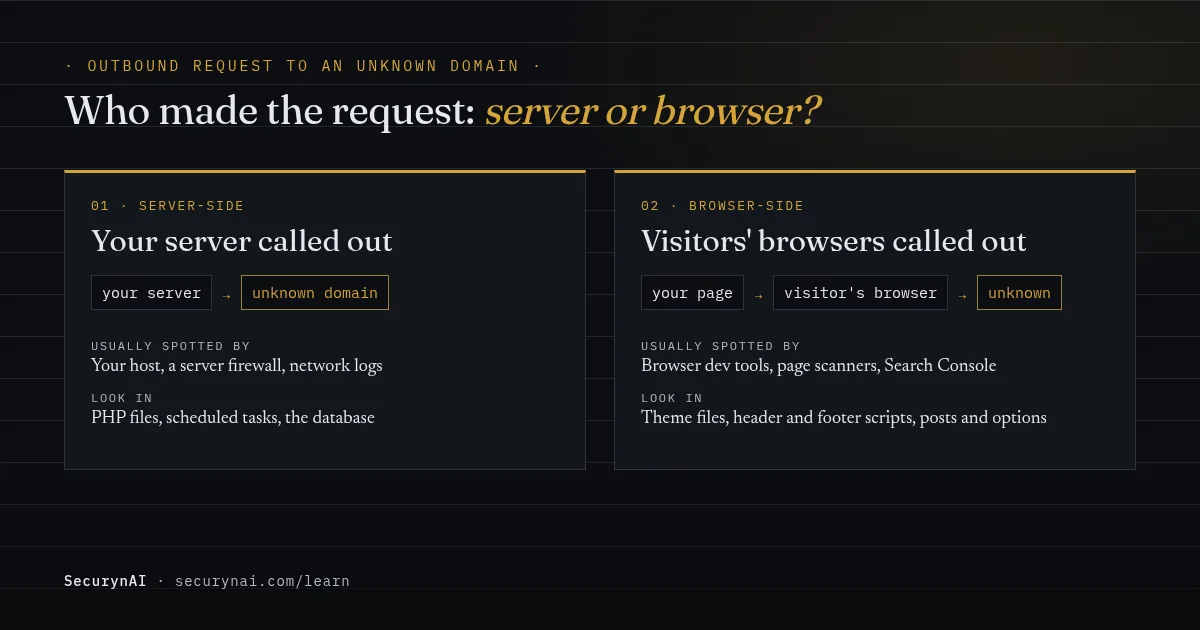
Server or browser: where did the outbound request come from?
Before you hunt for the cause, work out who made the request. The two sources hide in different places, and the tool that flagged it is usually the biggest clue.
| Who flagged it | What it saw | Where to look first |
|---|---|---|
| Your host, a server firewall or network logs | Your server opening a connection | PHP files, scheduled tasks, the database |
| Browser dev tools, a page scanner, Search Console | Your page making visitors' browsers load something | Theme files, header and footer scripts, posts and options |
| A WordPress plugin that logs requests | Calls made through WordPress's own HTTP functions | The plugin or theme it names as the caller |
Browser-side cases hide well. A fake caching plugin documented by Monarx in January 2026 loads attacker code in visitors' browsers but stays quiet when an admin is logged in. Check the page in a private window too.
How to trace an unknown outbound request, step by step
Look first, delete later. If you haven't yet, back up the whole site (files and database) before you change anything. The commands below only read and list. They need SSH access and, for the wp commands, WP-CLI. Your host's support team can usually run them for you.
1. Look the domain up
Paste it into VirusTotal or urlscan.io to see whether others have already flagged it. A clean result isn't proof of safety. New attacker domains often have no history yet, which is why a very young domain deserves a closer look.
2. Search your files for it
grep -rIl "unknown-domain.example" wp-content/A hit in a plugin you know usually settles it. No hit doesn't clear the site, because attackers scramble domains. In one sysadmin's write-up, the culprit domain was encoded, and the code sat inside a ZIP file in uploads.
3. Search the database
wp db search "unknown-domain.example" --all-tables-with-prefixThis checks posts, options and plugin tables for the domain (docs). Browser-side injections often live here rather than in files.
4. Check scheduled tasks and changed files
wp cron event list
wp core verify-checksums
wp plugin verify-checksums --all
Look for cron hooks you can't explain (our guide to a rogue cron job helps here). The checksum commands compare core and WordPress.org plugins against the official copies (core, plugins). Premium plugins aren't covered, so compare those with a fresh vendor download.
5. Log requests if it keeps happening
A logging plugin such as HTTP Requests Manager records requests made through WordPress's HTTP functions and which plugin made them. Its own page notes the limit: it won't see code that calls cURL or sockets directly. Your host's network logs are the full picture.
Outbound request looks malicious? Here's what to do next
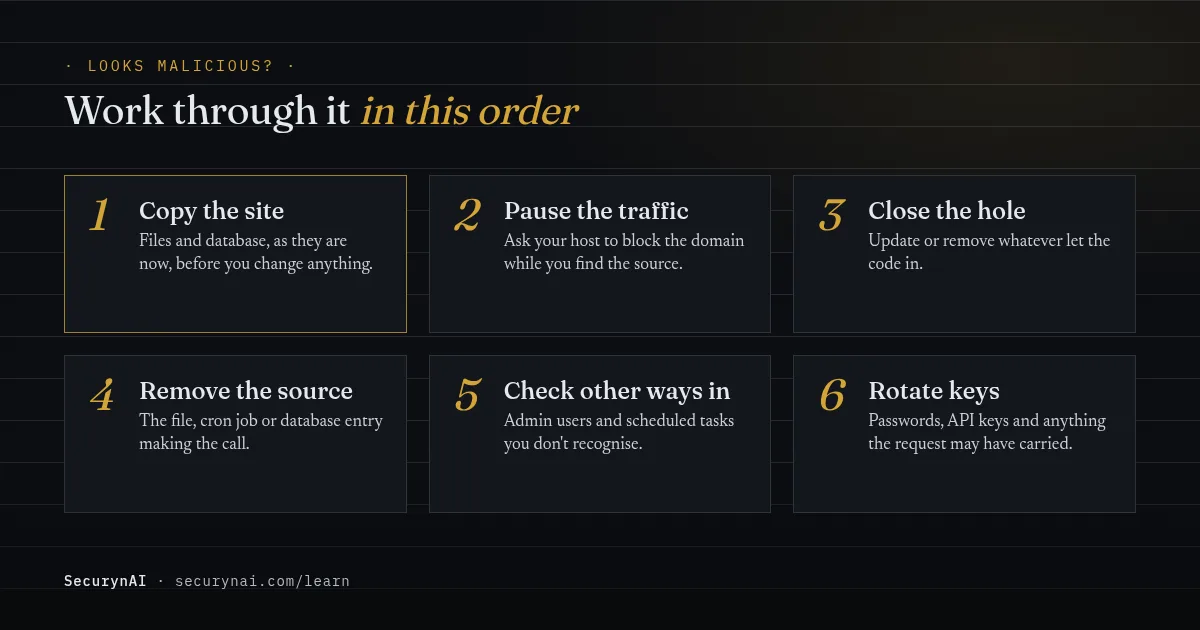
Remove the code making the call, not just the call. Blocking a domain hides the symptom, and the same code can switch to a new address tomorrow. Once you have a copy of the site for your records, work through this order:
- Pause the traffic. Ask your host to block the domain while you work. Many will, and their block catches every kind of request.
- Close the hole. Update or remove the plugin or theme that let the attacker in, or a new backdoor will follow.
- Remove the source, whether that's a file, a cron job or a database entry. Look for a spare webshell too. Our malware removal guide covers a full cleanup.
- Check other ways back in: admin users you don't recognise and scheduled tasks you didn't add.
- Rotate passwords and keys: WordPress, hosting, database, the keys in
wp-config.php, and any API keys your plugins store.
If the requests could have carried customer data, such as checkout details or form entries, read our guide to card skimmers in WooCommerce and check your breach notification duties. That's general information, not legal advice.
Can I block outbound requests in WordPress itself?
You can, with care. WordPress has a built-in switch that blocks outside requests except to your own site and the hosts you list. Back up wp-config.php first:
define( 'WP_HTTP_BLOCK_EXTERNAL', true );
define( 'WP_ACCESSIBLE_HOSTS', 'api.wordpress.org,*.wordpress.org' );
Expect things to break until you add every host your plugins need. A WordPress.org thread shows the usual sign: plugin and theme search failing with "Unexpected Error" because outbound connections were blocked. This switch also only covers WordPress's HTTP functions, so malware using raw cURL walks past it.
What SecurynAI sees, and what it doesn't
The free SecurynAI plugin doesn't watch outbound traffic. It looks for the code that usually causes it. Daily by default, it checks PHP files in wp-content for known malicious patterns, including code that downloads from a remote server and runs it. It also flags PHP in uploads and checks core and WordPress.org plugins against official checksums.
Pro ($79 per site per year) adds behavioral monitoring. We at SecurynAI record each request your site makes through WordPress's HTTP functions: the destination, method, size, response time and status. Once we've seen about 100 of them, we compare new requests against your site's normal pattern. Requests to WordPress.org and a short list of well-known services are skipped.
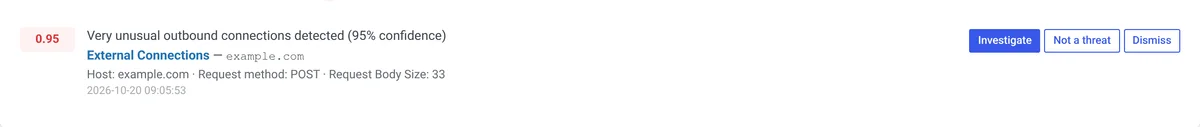
Out-of-pattern requests go into an "External Connections" queue, grouped by destination, where you can investigate or mark them as not a threat. If an unusual outbound request and a malicious-code finding land within an hour of each other, Pro links them into one incident.
Once those first 100 requests are in, a domain your site has never contacted before is flagged. Requests to domains it already knows are flagged only when they look very different from usual, for example far larger than normal.
We'll be straight about the limits. It's a pattern check, not a blocklist. It can't see code that skips WordPress's HTTP functions, or requests made by visitors' browsers. It doesn't replace your host's logs, backups or updates. See the full Free vs Pro breakdown.
Outbound request FAQ
Why is my WordPress site connecting to a domain I don't recognise?
Most often it's a plugin or theme checking for updates, validating a licence or talking to a service it depends on. Less often it's malicious code fetching instructions or sending data out. Matching the domain to something you installed answers it in most cases.
Should I just block the unknown domain?
Blocking it is a sensible pause while you investigate, but it isn't a fix. The code making the request is still on your site and can be pointed at a new domain. Find and remove the source, then keep the block if you like.
Can my host see outbound traffic that WordPress can't?
Yes. Your host sees connections at the server level, including ones made by code that skips WordPress's own HTTP functions. Plugins that log requests inside WordPress only see calls made through those functions, so ask your host for their logs if the picture doesn't add up.
Will blocking external requests in wp-config break my site?
It can. With WP_HTTP_BLOCK_EXTERNAL on, WordPress only allows requests to your own site and the hosts in WP_ACCESSIBLE_HOSTS. Updates, plugin search and services like payment gateways stop working until you add their hosts.
If you look after client sites, our playbook on explaining a hack to a client helps with the conversation that follows a finding like this.
Chasing an unknown domain? The free SecurynAI plugin checks your files every day for the code that usually makes these calls.
Install free →