A WordPress security plugin is software that runs inside your site to block bad traffic, limit login guessing and tell you when something changes that shouldn't. The best WordPress security plugins in 2026 all do some of that free. The paid plans add faster rules, a cleanup team or fixes done for you.
Most security-plugin comparisons are written by a security plugin company. This one is too, so here's how we'll keep it fair. We say what each plugin does well, where its free version stops and what it costs, using each vendor's own pages. We put our plugin, SecurynAI, last, and we say what it doesn't do.
How we compared these WordPress security plugins
There's no lab test here and no score out of ten. We sorted the plugins by the main job each one is built for, then checked four things for each. Every fact comes from the vendor's pricing page or its WordPress.org listing, checked in October 2026. Prices change, so check before you buy.
- What the free version actually does, not what the sales page implies.
- Where it stops, such as delayed rules or paid cleanup.
- What the first paid plan costs, per site, per year where the vendor says so.
- Who it suits: a solo owner, a store or an agency.
Why these four? Because most risk sits in plugins you already run. Patchstack's State of WordPress Security in 2026 counted 11,334 new WordPress vulnerabilities in 2025, 91% of them in plugins. It also found 46% "did not receive a fix from the developer in time for public disclosure." Patchstack sells protection for exactly that gap, so weigh it accordingly.
WordPress security plugins compared: free tiers and prices
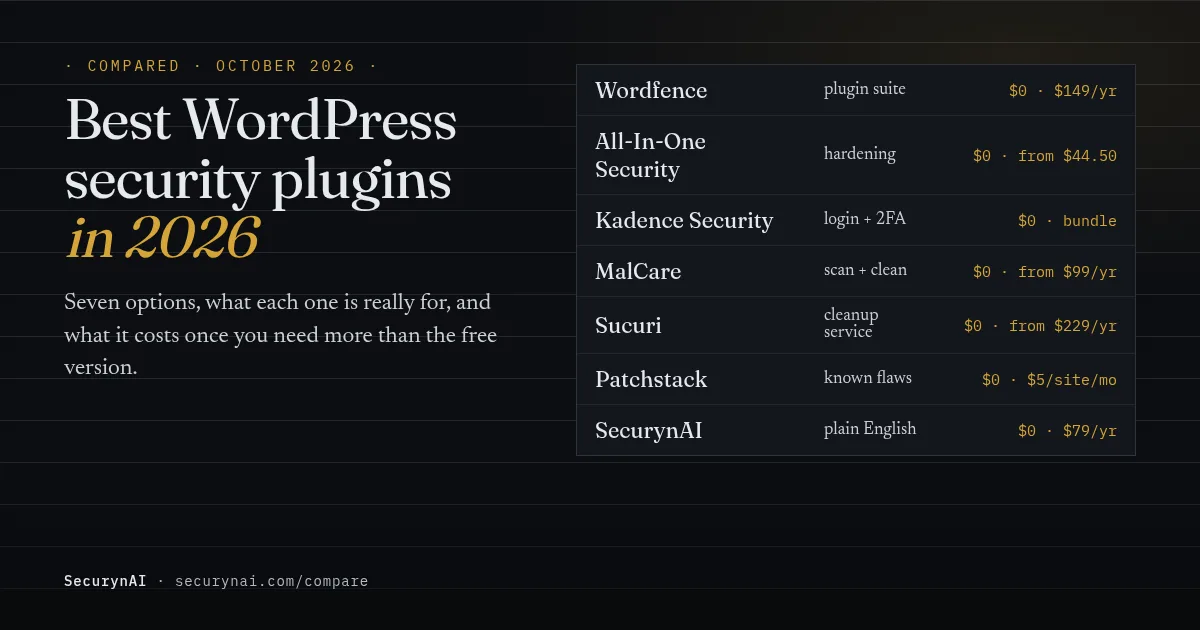
Here's the short version. Every plugin below has a free version with no time limit, but "free" covers very different amounts of work. Paid prices are the lowest published plan for one site unless noted.
| Plugin | What the free version does | Paid from | Best fit |
|---|---|---|---|
| Wordfence | Firewall, malware scanner, 2FA, login CAPTCHA. Free rules and signatures arrive 30 days late. | $149/yr (Premium) | Hands-on owners who want one broad plugin |
| All-In-One Security | Firewall rules, login lockout, 2FA, file change scanner. No malware scan. | $44.50 first year, then $89/yr (2 sites) | Hardening on a budget |
| Kadence Security | 2FA, brute-force protection, file change detection, known-vulnerability scan 4 times a day. | Sold within Kadence plans | Login security, Kadence users |
| MalCare | Cloud malware scan, firewall (rules weekly), login protection. Finds malware but doesn't remove it. | $99/yr (Protect), $299/yr with cleanup | Owners who want removal on a plan |
| Sucuri | Activity audit, file integrity, remote malware scan, blocklist checks, hardening. Firewall is paid. | $229/yr (platform, cleanups included) | Owners who want a team to clean up |
| Patchstack | Known-vulnerability detection and alerts. No firewall. | $5/site/month for virtual patching | Add-on for known plugin flaws |
| SecurynAI | Firewall, login lockout, file-integrity checks, a basic malware signature check, vulnerability alerts, hardening checks, each explained in plain English. | $79/site/yr (Pro) | Owners and agencies who want clear alerts |
The best WordPress security plugins, one by one
Each entry covers the same three things: what it does well, the catch, and who should pick it. None of these is a bad choice; they're built for different readers.
Wordfence: the broad, hands-on default
Wordfence has 5+ million active installs on WordPress.org. The free version is a real toolkit: a web application firewall, a malware scanner for core, themes and plugins, two-factor login with an authenticator app, and a login CAPTCHA. Login protection matters: Wordfence's 2024 annual report says it blocked over 55 billion password attacks that year.
The catch is timing. The WordPress.org listing says free firewall rules and malware signatures are "delayed by 30 days"; Premium gets them in real time. Per Wordfence's plans page, Premium is $149 a year, Care $590 (hands-on help and incident response) and Response $1,250 (24/7, with a 1-hour response time).
Pick it if you're comfortable reading technical alerts yourself and want one plugin that covers a lot. We compare it with ours in detail in SecurynAI vs Wordfence.
All-In-One Security (AIOS): hardening on a budget
AIOS has 1+ million installs on WordPress.org, and its free version is generous. You get PHP, .htaccess and 6G firewall rules, login lockout after failed attempts, two-factor authentication and a file change scanner. Malware scanning is Premium only.
Premium is cheap for small portfolios. The AIOS pricing page lists $44.50 for the first year and $89 a year after for up to 2 sites, or $124.50 then $249 for up to 35. Pick it if your main gap is hardening and login security, and you're happy to tune settings yourself.
Kadence Security: login security first
This is the plugin formerly called iThemes Security, later Solid Security. On WordPress.org it has 700,000+ installs. The free version covers two-factor login, local and network brute-force protection, file change detection, and a site scan for known vulnerabilities four times a day.
Pro adds hourly scans, Patchstack virtual patching, passwordless logins and automatic updates through Version Management. We couldn't find a standalone Pro price on the official site; it's sold as part of Kadence's bundles. Pick it if strong logins are your priority, or you already pay for Kadence.
MalCare: scanning, with cleanup on a plan
MalCare's free version on WordPress.org (100,000+ installs) runs a cloud-based malware scan of files and the database, a firewall whose rules update every 7 days, and login protection with a CAPTCHA.
The free version finds malware but doesn't remove it. MalCare's pricing page lists Protect at $99 a year (adds virtual patching, no cleanup), Repair at $299 (automated cleanup) and Fortify at $499 (adds manual fixes). Pick it if you'd rather pay for one-click removal than clean up by hand.
Sucuri: a team to clean up after a hack
Sucuri's free plugin on WordPress.org (600,000+ installs) covers activity auditing, file integrity monitoring, remote malware scanning, blocklist monitoring, hardening and post-hack steps. Its firewall "is not included as a free option."
Sucuri's real product is the paid platform: a cloud firewall plus people who clean up your site. Its signup page lists $229, $339 and $549 a year, each with unlimited manual cleanups and response times of 30, 12 and 6 hours. Firewall-only plans start at $9.99 a month. More in SecurynAI vs Sucuri.
Patchstack: the known-flaw specialist
Patchstack does one job: it tells you when a plugin or theme you run has a known vulnerability. Its WordPress.org listing (70,000+ installs) says the free version "does not include a firewall" and focuses on detection and alerts. Its strength is virtual patching: a rule that blocks attacks on a known flaw before you've updated.
You can add virtual patching to one site for $5 a month. For agencies, the pricing page lists a Developer plan at $69 a month, billed annually ($828 a year). Pick it alongside another plugin, not instead of one. See SecurynAI vs Patchstack.
SecurynAI: the alerts explained in plain English
We built SecurynAI, so read this one knowing that. Our angle is that every finding tells you what happened, whether it matters and what to do, in plain English. The free plugin covers the basics on its own, with built-in explanations and no account or API key needed.
- Firewall: rules for SQL injection, cross-site scripting, path traversal, command injection, file inclusion and author enumeration. It starts in monitor mode, logging what it would block, until you switch it to block mode, which also rate-limits XML-RPC.
- Login: locks out an IP or username after 20 failed logins in 15 minutes, for 30 minutes.
- Files: checks core and WordPress.org plugin files against official checksums, and tracks PHP changes in wp-content.
- Malware signatures: the daily file scan checks every PHP file in wp-content against 13 signatures that ship with the plugin (no live feed), and flags clearly obfuscated code, such as a decoder fed straight into eval. It's a narrow check, not a research-fed scanner like Wordfence's, and it doesn't clean anything up.
- Known flaws: matches every installed plugin and theme, active or not, against vulnerability data. See how to read a CVE for what those alerts mean.
- Accounts: flags privilege drift and admins with no two-factor plugin it recognises, plus hardening checks you fix yourself.
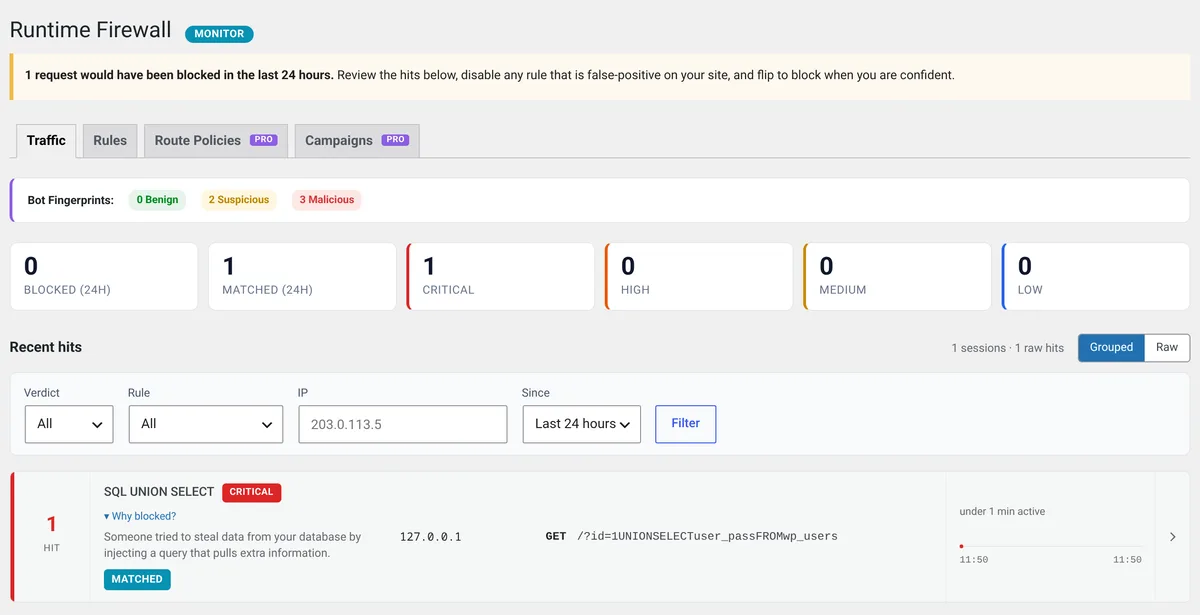
What it doesn't do matters too. There's no two-factor login of its own, no cloud firewall and no cleanup team. Its firewall rules ship with the plugin rather than a live feed. The free activity log keeps 7 days. And it's newer than everything above, with a shorter track record.
Pro is $79 per site per year. It adds one-click fixes for many hardening items, with undo, and a patch queue that can update a vulnerable plugin through your approval rules. It also groups related events into attack chains every 5 minutes, and keeps a 90-day tamper-evident audit archive.
Pro's adaptive firewall writes new rules from the attack traffic it sees and checks front-end requests against them, alongside rate limits on REST API routes. New rules run a trial period first (24 hours by default), and like the free firewall they block only in block mode; in monitor mode they just log.
Plugin firewall or cloud firewall: does it matter?
Most plugins here, ours included, run their firewall on your own server, inside WordPress. A cloud firewall, like Sucuri's paid one, filters traffic on the provider's network before it reaches your host. A cloud firewall takes load off your server; a plugin firewall costs nothing extra and knows more about WordPress itself.
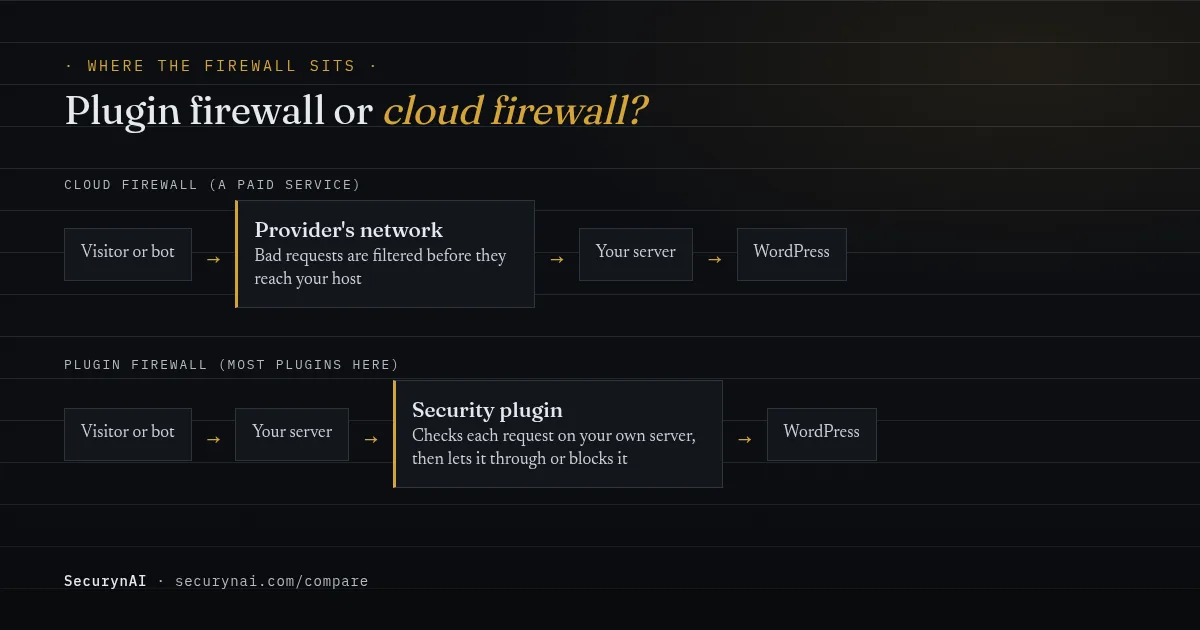
For a small brochure site, a plugin firewall is usually plenty. If you're seeing heavy bot traffic or a slow server under load, a cloud firewall starts to earn its fee. Our guide do you need a WAF? walks through the decision.
Which WordPress security plugin should you pick?
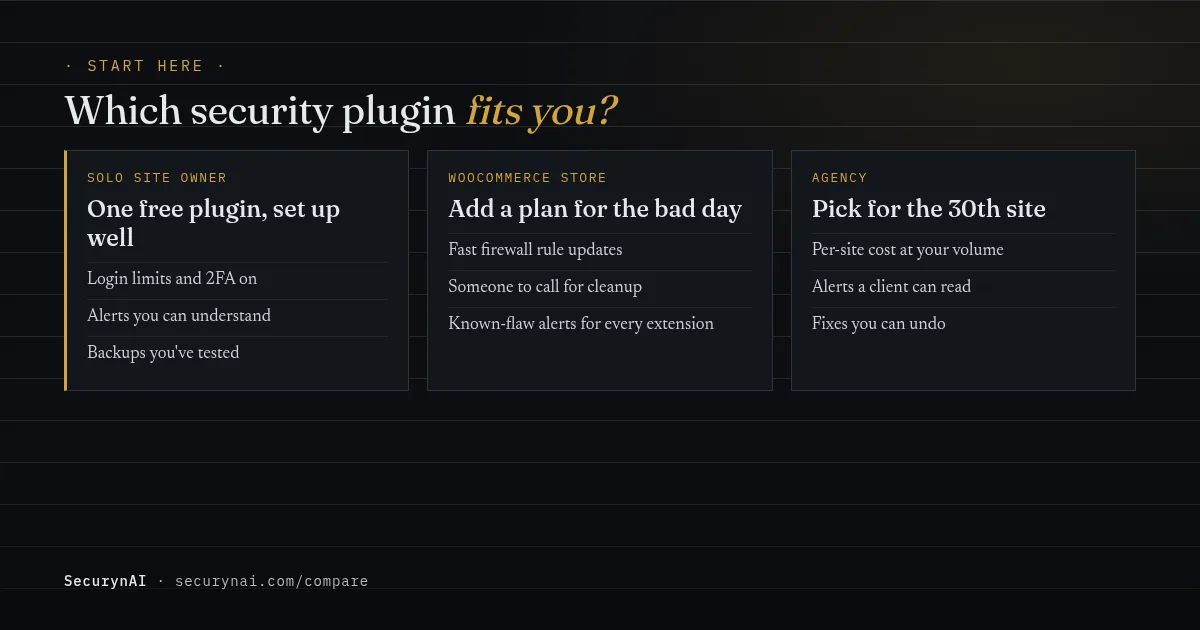
Start from your situation, not the feature list. The right plugin is the one you'll actually set up, read and act on.
If you run one site yourself
One free plugin, set up properly, beats three half-configured ones. Wordfence, AIOS and Kadence Security all give you two-factor login for free. If you'd rather understand each alert without looking things up, that's the gap SecurynAI's free version fills. Then work through our hardening checklist and secure the login page.
If you run a WooCommerce store
A store has more to lose on a bad day, so the paid features matter more. Decide now who cleans up if something gets through: you, MalCare's Repair plan, Sucuri's team or Wordfence Care. Faster firewall rules are worth paying for too. Our WooCommerce security checklist covers the store-specific risks.
If you look after client sites
Price the 30th site, not the first. Per-site plans add up, while AIOS and Patchstack sell multi-site bundles. Think about who reads the alerts: a finding your client understands saves you a late-night email. Our playbook on managing 30+ client sites covers the workflow, and SecurynAI's bulk licensing is a contact form away.
Can you run two security plugins at once?
You can, but most support teams say don't, at least not with the same features switched on in both. Two firewalls or two login guards on one site tend to clash. Pairing a broad plugin with a narrow one, such as Patchstack for known flaws, is the usual exception.
When a user asked about running Wordfence with another security plugin, a Wordfence support rep replied on WordPress.org: "I would recommend against having both security plugins active on your site," because both hook into the login process. WPMU DEV's team gave the same advice for Defender plus Wordfence in another thread, unless both are "really carefully configured."
Switching needs care too. In one WordPress.org thread, a site owner moved from Wordfence to Solid Security, set up two-factor login, and "couldn't get to the site" from his main connection for a while. Fully remove the old plugin's settings first, keep a second admin session open, and test on staging if you have one.
WordPress security plugin FAQ
Is a free WordPress security plugin enough?
For many small sites, yes, if it's set up properly and paired with updates and tested backups. What free versions usually leave out is speed (Wordfence's free firewall rules arrive 30 days later) and cleanup (MalCare and Sucuri charge for removal). Pay when you need one of those, not before.
Do I need a security plugin if my host has a firewall?
Probably still yes. A host firewall filters traffic, but it usually won't tell you about a changed core file, a new admin account or a plugin with a known flaw. Ask your host what they cover, then fill the gaps.
Will a security plugin slow down my site?
A plugin firewall adds a check to every request, and scans use server time while they run. On most sites that's hard to notice, but two security plugins doubling up is a common cause of slowdowns and odd conflicts. Run one, and schedule heavy scans for quiet hours if your plugin allows it.
Which WordPress security plugin is best for WooCommerce?
There isn't one store-specific winner. A store needs the same basics as any site, plus faster firewall rules, alerts for every extension you run and a plan for cleanup if something gets through. Wordfence Premium, MalCare's paid plans and Sucuri's platform each cover the cleanup side in different ways.
Still weighing it up? See exactly what the free SecurynAI plugin covers, and what Pro adds for $79 per site per year.
Compare free and Pro →