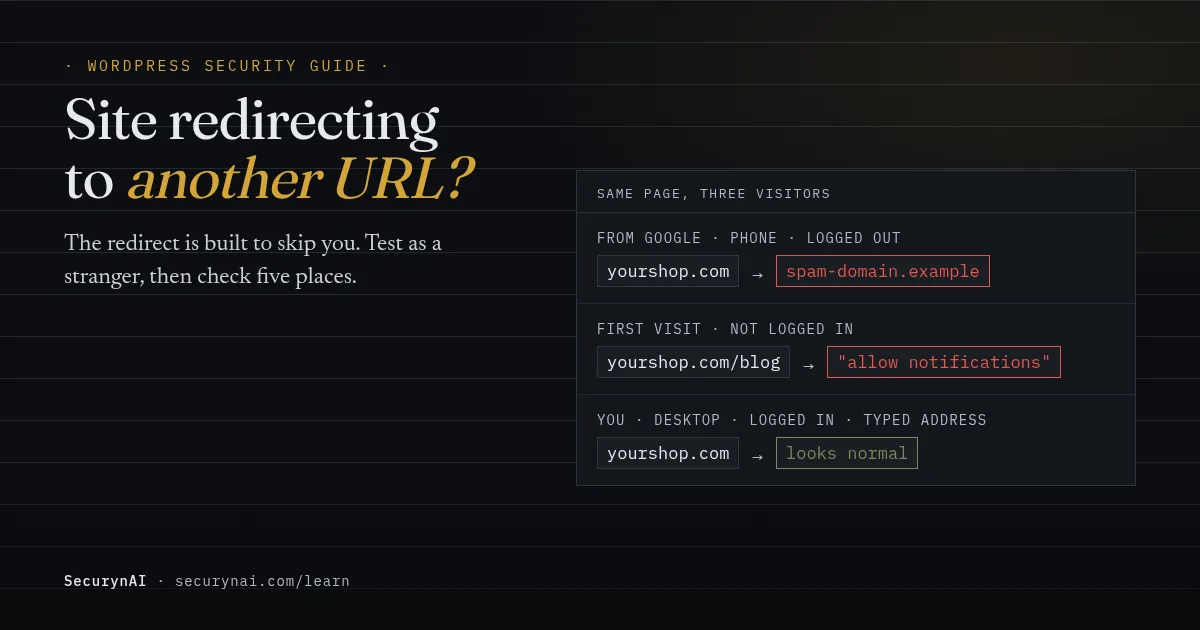
A WordPress redirect hack is code or data an attacker adds to your site that sends some of your visitors to another website, usually spam, scams or fake "allow notifications" pages. If you've caught your WordPress site redirecting to another URL you don't recognise, treat it as a break-in until you've found the cause.
Before you change anything, back up the site as it is, files and database, and keep that copy off the server. Then write down what visitors told you: which page, which device, and where they came from. Those three details tell you where the redirect is hiding.
Is a WordPress redirect always a hack?
No. Plenty of redirects are normal. A redirect to your own site or a page you recognise is usually a setting. A redirect to an unrelated domain is almost always a hack.
When it's probably fine
- HTTP goes to HTTPS, or
wwwgoes to the bare domain. That's your host or your settings. - Old page addresses go to new ones, and you use a redirect or SEO plugin.
- Visitors see a "coming soon" page from a maintenance-mode plugin.
- You recently moved the site or changed its domain.
Plugins can get this wrong too. In one WordPress.org thread about a mobile-only redirect, phone visitors were sent to the latest post instead of the homepage. The owner later wrote, "a plugin caused this and I fixed it," and blamed their own configuration.
When to treat it as a hack
- Visitors end up on a domain you've never heard of.
- It only happens from Google results, only on phones, or only on the first visit.
- The other page asks visitors to "allow notifications", claim a prize or install something.
- Your WordPress Address or Site Address in Settings > General shows a domain that isn't yours.
Why can't I see the redirect on my own site?
Because it was built that way. Most redirect hacks fire only for visitors who are unlikely to fix the site, and skip the person who would. You check from a desktop, logged in, by typing the address. That's exactly the visit the code ignores.
- Where they came from. Only visitors arriving from a search engine (the referrer) get sent away.
- Their device. Only phones, or only one operating system.
- Whether they're logged in. Logged-in users, meaning you, see the normal site.
- Whether they've been before. The first visit redirects, and repeat visits look fine.
Forum threads show all of these. In a WordPress.org thread from September 2024, a site owner described malware stored in the database where "non-logged-in users or visitors with certain IP addresses are redirected to malicious external URLs."
In another thread, an owner wrote that "this happens only on Mobile device, on PC all is looking good," with visitors asked to tap "Allow" on notifications. And in a third, pages redirected on the first visit only, and a forum moderator couldn't reproduce it at all.
This is a common kind of infection. In Sucuri's 2023 Hacked Website & Malware Threat Report, malicious redirects to spam pages made up 28.19% of SEO spam infections, and 13.48% of infected sites loaded scripts or iframes from blocklisted third-party sites.
How to see the redirect for yourself
Test as a stranger, not as the owner. Each of these removes one of the conditions the code looks for.
- Open a private window, stay logged out, and click your site from a Google search result, not a bookmark.
- Try a phone on mobile data, not your own Wi-Fi, in case your IP address has been skipped.
- Fake a search referrer with curl. This only reads headers, so it's safe. A
Location:line pointing at another domain is your redirect.
curl -sI -e "https://www.google.com/" -A "Mozilla/5.0 (iPhone)" https://example.com/If you use Google Search Console, the URL Inspection tool can also run Test live URL and show the page as Google's own crawler sees it. That helps when the code targets search engines.
Where do WordPress redirect hacks hide?
There are five usual places. The redirect can live in a file or in the database, so cleaning only files often misses it. Sucuri's same report found that the wp_options and wp_posts tables held over 70% of the malicious database entries it removed.
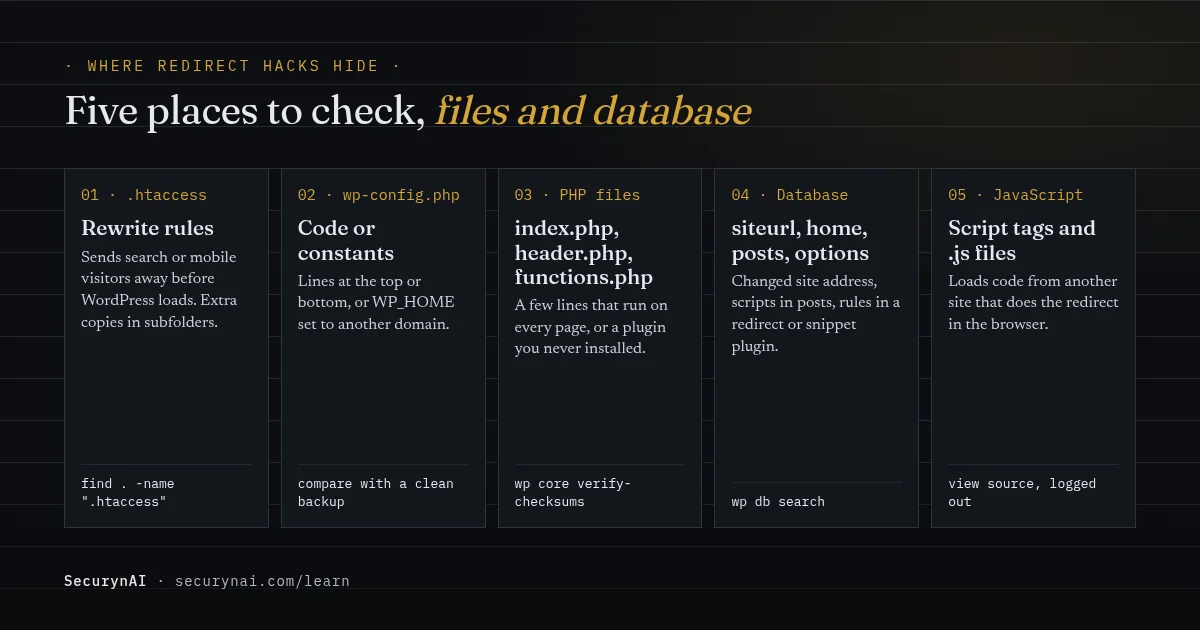
| Where | What it looks like | How to check |
|---|---|---|
.htaccess | Rewrite rules that send search or mobile visitors to another domain, before WordPress even loads | Read the root file, and look for extra copies in subfolders |
wp-config.php | Code at the very top or bottom, or WP_HOME / WP_SITEURL set to a strange domain | Compare it with your last clean backup |
| PHP files | A few lines in the root index.php, the theme's header.php or functions.php, or a plugin you don't recognise | Checksums for core and WordPress.org plugins; compare themes with a fresh copy |
| Database | Changed siteurl or home, scripts in posts or widgets, rules saved by a redirect or code-snippet plugin | wp option get, wp db search, and each plugin's own rule list |
| JavaScript | A script tag or edited .js file that loads code from another site | View the page source logged out; check theme and plugin .js files |
The WordPress.org "My site was hacked" FAQ singles out .htaccess as one of the files "most often updated and used for nefarious activities," and notes it can be "embedded within several other directories." It also names index.php, header.php and the theme's functions file, because changes there affect every page.
One detail catches people out. WordPress's wp-config.php documentation says WP_HOME "overrides the wp_options table value for home but does not change it in the database." So a clean-looking database can still sit behind a redirected site.
How to find the redirect, step by step
Look first, delete later. Everything below only reads. If you have SSH and WP-CLI, run the commands from the WordPress folder. If not, your host's file manager and phpMyAdmin show the same things.
1. Check the site address
wp option get siteurl
wp option get home
grep -n "WP_HOME\|WP_SITEURL" wp-config.php
Both options should show your own domain. A grep result is fine if you set it yourself during a move. A domain you don't own, in either place, is the redirect.
2. Read every .htaccess file
find . -name ".htaccess"A normal WordPress .htaccess is short. Look for RewriteCond lines that mention a referrer such as google or a user agent such as mobile, and RewriteRule lines pointing at another domain.
3. Verify core and plugin files
wp core verify-checksums
wp plugin verify-checksums --all
These compare your files with the official WordPress.org copies (core, plugins). They can't check themes or premium plugins, so compare those with a fresh download from the vendor.
4. Search the database
wp db search "spam-domain.example" --all-tables
wp db search "<script" wp_options wp_posts --stats
wp db search finds text anywhere in the database. The script search will also hit legitimate code, so look for scripts that load from a domain you don't recognise. Then open any redirect or code-snippet plugin and read its rule list.
5. Remove it, then close the way in
Once you've found it, take a backup, then remove the rule, file or database entry. Deleting the redirect without closing the way in usually means it comes back. Our guide to removing WordPress malware covers the full order: replace files from clean sources, check users and scheduled tasks, update, and change passwords again.
The way in is usually a plugin. Patchstack's State of WordPress Security in 2026 counted 11,334 new WordPress vulnerabilities in 2025, 91% of them in plugins, and 46% had no fix by the time they were made public.
If a clean backup from before the redirect exists, restoring it can be quicker. Our guide to restoring from backup after a hack covers that. If Google already shows a warning, the "Deceptive site ahead" guide explains how to get it lifted once you're clean.
What SecurynAI sees in a redirect hack, and what it doesn't
We at SecurynAI would rather you know the gaps than assume you're covered. The free plugin watches most of the places a redirect hides, but not plugin settings in the database, theme JavaScript or scripts loaded from other sites.
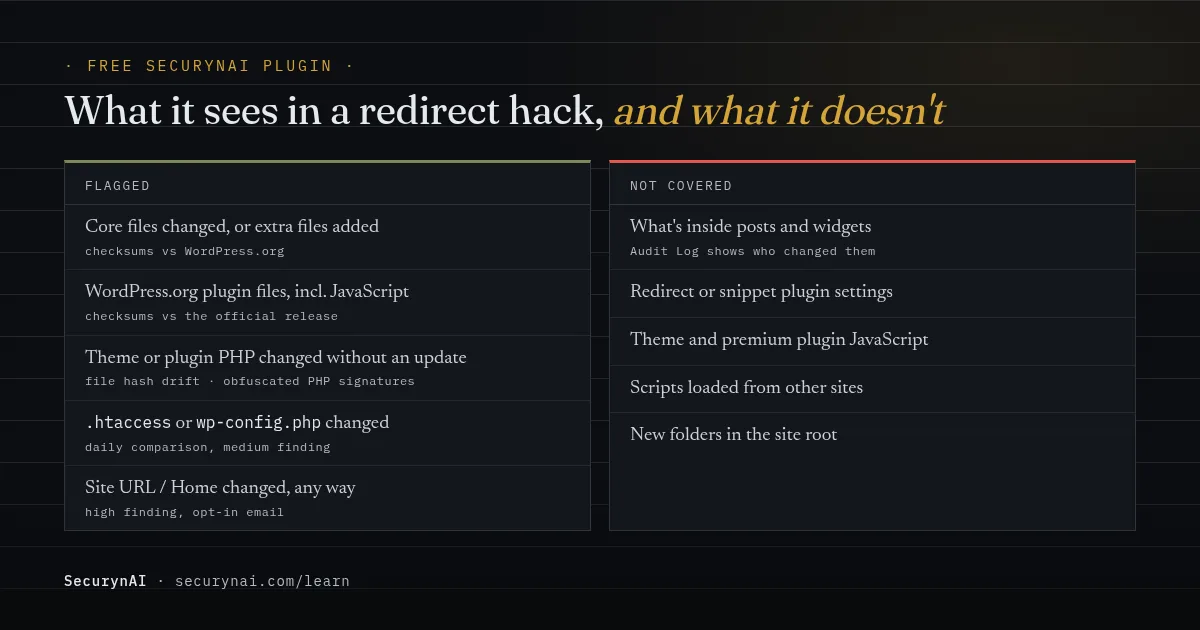
| Where the redirect is | Free SecurynAI |
|---|---|
Core files, including the root index.php | Yes. Daily checksum check against WordPress.org; a changed file is a high finding. |
| Extra files WordPress didn't ship | Yes, for PHP files in wp-admin and wp-includes, and PHP files or index.html in the site root. Not new folders in the root. |
| WordPress.org plugin files, JavaScript included | Yes. Every file is checked against the official release. |
| Theme and premium plugin PHP | Yes, as "file hash drift": a PHP file that changes, or appears, without a version update. |
Obfuscated PHP, like eval(base64_decode(...)) | Yes, through 13 bundled signatures. A plain, readable redirect line won't match. |
.htaccess, .user.ini, php.ini, wp-config.php | Yes. Each daily scan compares them with the last one; a change is a medium finding showing the added lines. |
| Site URL or Home | Yes. Changed through WordPress, or straight in the database, or forced in wp-config.php: a high finding. |
| Posts, pages, templates, widgets | Partly. The Audit Log records who changed them, but nothing scans their content, and SQL writes aren't logged. |
| Redirect or snippet plugin settings, theme or premium plugin JavaScript, outside scripts | No. |
The site address finding exists because redirect hacks rewrite those two settings. A change made through WordPress is flagged straight away, and a daily check catches one written into the database or forced in wp-config.php. If you've turned on email alerts in Settings > General, which are off by default, it arrives by email too.
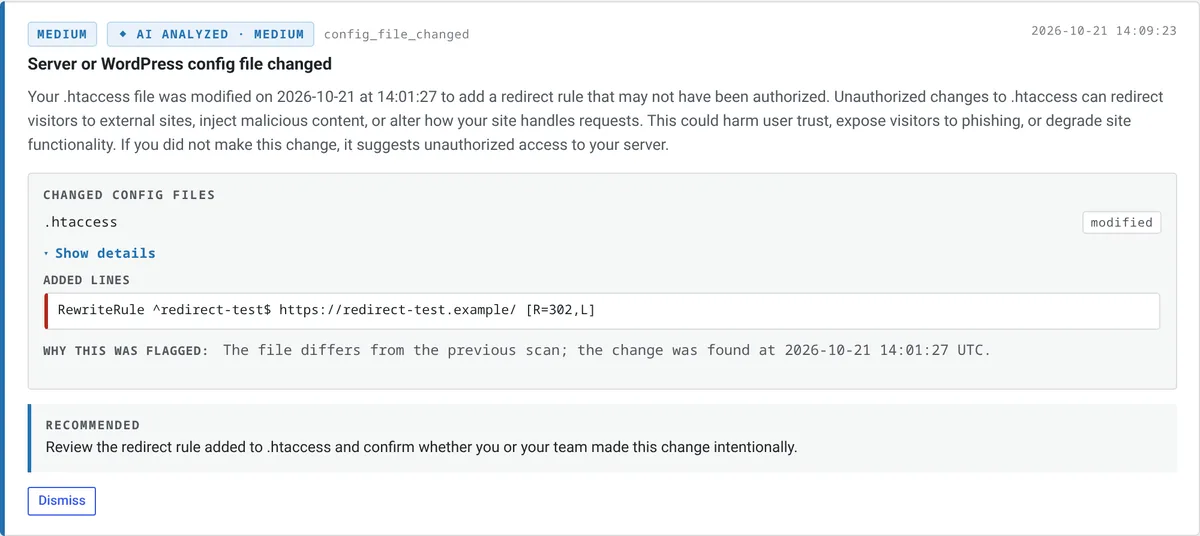
A changed .htaccess or wp-config.php is a medium finding, because caching plugins and saving your permalinks edit them too. Medium findings don't send an email, so check the Findings screen. The first scan only records the files, so changes made before you installed SecurynAI won't show.
SecurynAI also doesn't watch Google's blocklists, so it won't tell you if Google has flagged the site. Use Search Console for that. The free malware scan detects only and never cleans files.
What Pro adds after a redirect hack
On Pro ($79 per site per year), a changed core file or WordPress.org plugin file can be restored from the official copy, and a PHP file matching a malware signature can be moved to quarantine with undo. Each fix waits for your approval by default.
Quarantine refuses files that belong to an installed plugin or the active theme, so those you clean by hand.
Quick check: could you spot a redirect quickly?
- Have you tested your site logged out, on a phone, from a Google result in the last month?
- Do
siteurlandhomeboth show your own domain? - Do you know what a normal
.htaccesslooks like on your site? - Would you hear within a day if a core or theme file changed?
- Do you have a backup from before anything looked wrong?
Five yeses and you'd likely catch a redirect early. Two to four is common, and quick to improve. Our guides to the signs of WordPress malware and the WordPress hardening checklist are good next steps. If spam pages also show up in Google, read about the pharma hack and SEO spam.
WordPress redirect FAQ
Why does my WordPress site only redirect on mobile?
Because the injected code checks the visitor's device and only fires for phones. Site owners usually check from a desktop while logged in, so the redirect stays hidden from them. Test on a phone using mobile data, not your office Wi-Fi, and logged out.
Why does my site only redirect when people click it in Google?
The code is reading the referrer, the header that says where a visitor came from, and only redirects search traffic. Typing your address or using a bookmark sends no search referrer, so it looks fine. You can fake a Google referrer with curl to test it.
Can a plugin cause a redirect without a hack?
Yes. Redirect, SEO, maintenance-mode and mobile plugins all send visitors elsewhere on purpose, and a wrong setting can look like a hack. If the destination is your own site or a page you recognise, check those plugins first. A redirect to an unrelated domain is a different story.
Will changing my passwords stop the redirect?
No. The redirect is code or data already sitting on your site, and new passwords don't remove it. Change passwords as part of the cleanup, and again once the site is clean, as the WordPress.org hacked-site FAQ advises.
Cleaned up a redirect and want to hear the day a core file, plugin file or site address changes again? The free SecurynAI plugin starts checking from the moment you install it.
Install free →