WordPress file permissions are the three-digit numbers that decide who on the server can read, change or run each file and folder of your site. Get them right and other accounts on a shared server can't read your database password or plant files in your folders. Get them wrong and you either open the door or break updates.
This guide explains what the numbers mean, the correct WordPress permissions from WordPress.org's own handbook, why setting everything to 777 keeps showing up as a "fix", and how to set wp-config.php permissions without locking yourself out. You don't need SSH for any of it.
What do WordPress permission numbers like 644 mean?
Each digit is one audience: the file's owner, its group, and everyone else on the server. Almost all WordPress hosting runs on Linux, where every file and folder carries these three sets of rights. Read is worth 4, write is worth 2 and execute is worth 1. Add up the ones that apply and you get one digit per audience.
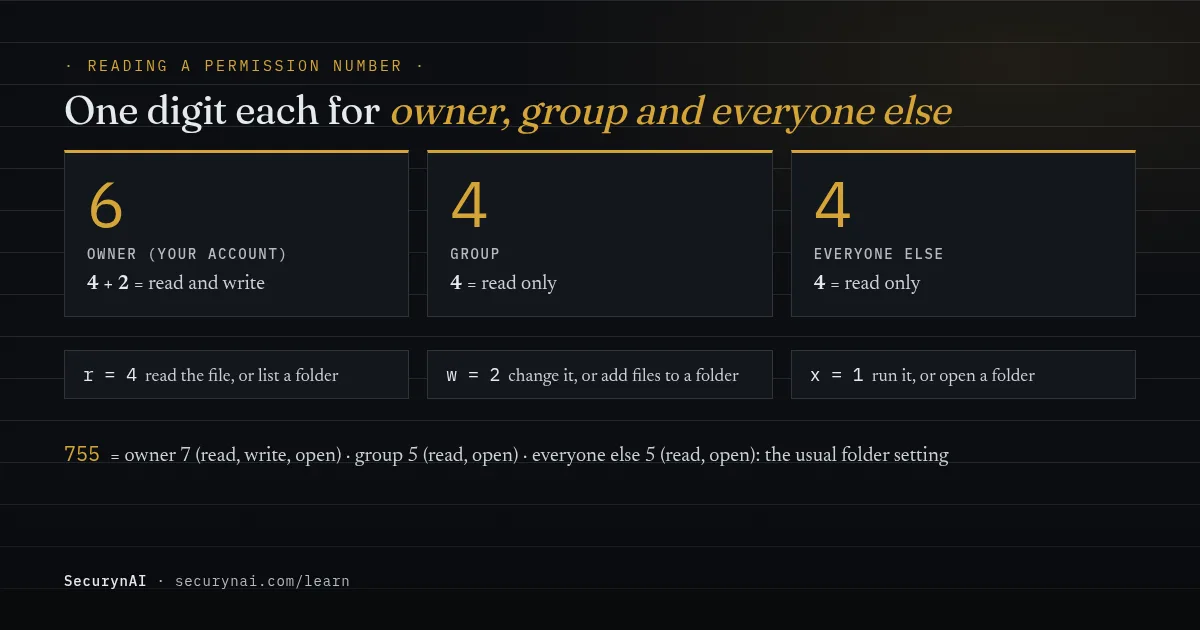
So 644 means the owner can read and change the file, and everyone else can only read it. 755 adds execute. On a folder, "execute" is what lets anyone open it and reach the files inside, which is why folders need it and plain files don't.
You'll also see these written as letters, for example -rw-r--r-- for 644 in an SFTP client or ls -l. Same information, different spelling.
The correct WordPress file permissions, from WordPress.org
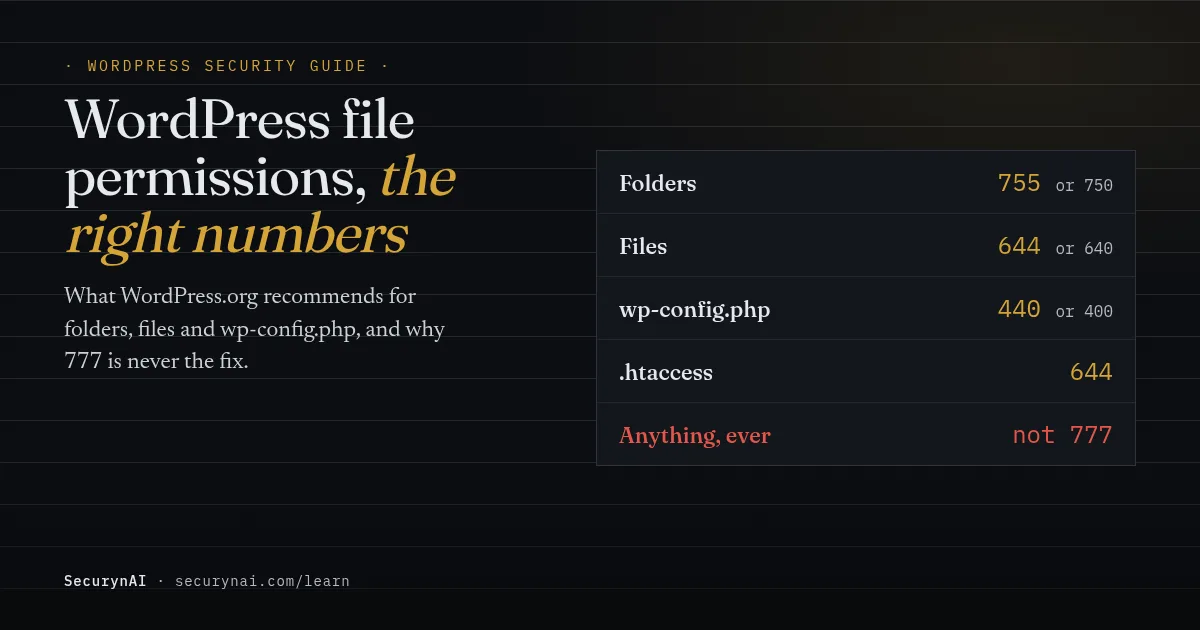
For most shared hosting, WordPress.org's answer is folders 755, files 644 and wp-config.php 440 or 400. The official Changing File Permissions page says "all directories should be 755 or 750" and "all files should be 644 or 640", with one exception: "wp-config.php should be 440 or 400 to prevent other users on the server from reading it."
| What | Recommended | Why |
|---|---|---|
| Folders | 755 (or 750) | Everyone can open them; only the owner can add files |
| Files | 644 (or 640) | Readable by the web server; only the owner can change them |
wp-config.php | 440 or 400 | Holds your database password and keys; nobody else should read it |
.htaccess | 644 | WordPress writes it when you save permalinks |
wp-content/uploads | 755 | WordPress needs to write here, but never 777 |
Those numbers assume PHP runs as your own account, which the handbook calls a suexec setup. On servers where PHP runs as a separate web server user, it describes looser group-writable values, "775 rather than 755 for folders, and 664 instead of 644". If you're not sure which one you have, your host can tell you in one line.
Ownership matters as much as the number
The handbook says files "should be owned by your user (ftp) account" and, on shared hosts, "should never be owned by the webserver process itself". The right number on the wrong owner still fails. In one WordPress.org thread, a plugins folder at 775 owned by root still refused updates. The reply: "you never want to use root."
Why 777 "fixes" permission errors, and why it's the wrong fix
777 makes the error go away because it lets anyone on the server write the file, including people and processes you never meant to trust. The handbook is direct: "No directories should ever be given 777, even upload directories." It adds, "I've never come across anything that needed more than 767, so when you see 777 ask why it's necessary."
It's a trap because it works. The upload succeeds, and the real cause, usually a folder owned by the wrong user, is still there. In an old WordPress.org thread on upload permissions, one reply said it "has to be 777"; the next answered, "That's totally dependent upon server config." The second reply is the one to trust.
The cost shows up later. One site owner in a WordPress.org thread titled "Hackers editing files?" wrote: "I had mistakenly left a lot of files with 777 file permissoins", and attackers "kept putting in links and scripts into them files and index.php." Nobody proved that was the way in, but it made every file easy to write.
How to check and change WordPress file permissions
You can do this from an SFTP client or your host's file manager; SSH is optional. Back up your site first, and write down the current values of anything you change, so you can put them back.
- SFTP client (FileZilla, Cyberduck or similar). Connect with your host's SFTP details, right-click a file or folder and choose "File permissions" or "Attributes". Type the number directly.
- Host file manager. cPanel, Plesk and most managed WordPress dashboards have a file manager with the same right-click option.
- SSH. Set folders and files separately, because they need different values. Swap in your own path.
find /path/to/wordpress -type d -exec chmod 755 {} \;
find /path/to/wordpress -type f -exec chmod 644 {} \;
chmod 440 /path/to/wordpress/wp-config.php
If the site shows an error right after the last line, PHP can't read wp-config.php at 440, which means it runs as a different user from the file's owner. Set it back to 640, or 644 if 640 fails too, and ask your host what they recommend.
For files WordPress creates itself during updates, the wp-config.php documentation lists two optional constants, FS_CHMOD_DIR and FS_CHMOD_FILE, with 0755 and 0644 as its examples. Most sites never need them.
What breaks when WordPress permissions are too strict?
Tighter isn't always safer: WordPress needs to write to a few places, and locking those breaks updates and uploads. The handbook names wp-content, and sometimes wp-content/uploads and wp-content/cache, plus .htaccess if you want WordPress to write permalink rules. If something fails right after you tighten permissions, start here.
| What you see | Likely cause | What to check |
|---|---|---|
| "Could not create directory" on a plugin install or update | The web server can't write to wp-content or wp-content/upgrade | Owner and permissions of those two folders |
| WordPress asks for FTP details to install anything | Files are owned by a different user than PHP runs as | Ownership, not the numbers |
| Image uploads fail | wp-content/uploads or this month's folder isn't writable | That folder's owner; 755 is enough when the owner is right |
White screen after tightening wp-config.php | PHP can't read the file at 440 or 400 | Set it to 640 or 644 and ask your host |
| Permalink changes don't stick (Apache) | WordPress can't write .htaccess | .htaccess owner, or paste the rules in by hand |
The first row is the most common. When a WordPress.org user's plugin install failed in this 2024 support thread, the plugin team's answer was: "Check the permissions of the wp-content and wp-content/upgrade directories. They should be writable by the web server."
The FTP prompt has a precise cause. WordPress's get_filesystem_method() writes a test file and only writes directly if that file's owner matches the owner of WordPress's own files. Loosening permissions won't clear the FTP prompt; fixing ownership will.
File permissions on Nginx, LiteSpeed and managed hosts
The numbers work the same on every Linux server, but the .htaccess advice only applies to Apache and LiteSpeed. W3Techs' web server survey on 22 October 2026 put Nginx at 30.2% of sites with a known server, Apache at 21.3% and LiteSpeed at 13.9%. Cloudflare, at 32.6%, hides whichever server sits behind it.
Nginx never reads .htaccess, so its permissions don't matter there and many Nginx sites don't have one. Any rule that protects wp-config.php or blocks PHP in uploads has to go in the Nginx server config instead, which is usually your host's job. Our WordPress hardening checklist has the snippets for both servers.
On managed WordPress hosts, permissions are often set for you and reset on deploy, and some won't let you change them. That's fine. Ask your host what they set for wp-config.php, and leave the rest alone.
File permissions are one layer, not the whole wall
Permissions stop other accounts from touching your files. They don't stop a flaw in a plugin, which runs as the same user WordPress writes with. If a plugin has an upload or code-execution bug, the attacker gets whatever write access WordPress has, whatever the numbers say.
That's where most real break-ins start. Patchstack's State of WordPress Security in 2026 counted 11,334 new vulnerabilities in 2025, 91% of them in plugins, and 46% had no fix when they were made public. So keep updates first, and treat correct permissions as the cheap layer behind them.
If you're already cleaning up a hacked site, reset permissions as part of the cleanup, after the malicious files are gone. Our guide to removing WordPress malware covers the order, and what a webshell is explains why fixed permissions don't remove a backdoor already planted.
How SecurynAI checks your WordPress file permissions
We at SecurynAI kept the permission checks narrow on purpose: the free plugin checks two files every day, wp-config.php and the root .htaccess, and tells you how to fix either one. It doesn't change anything itself, and it doesn't check folder modes, other files or who owns them.
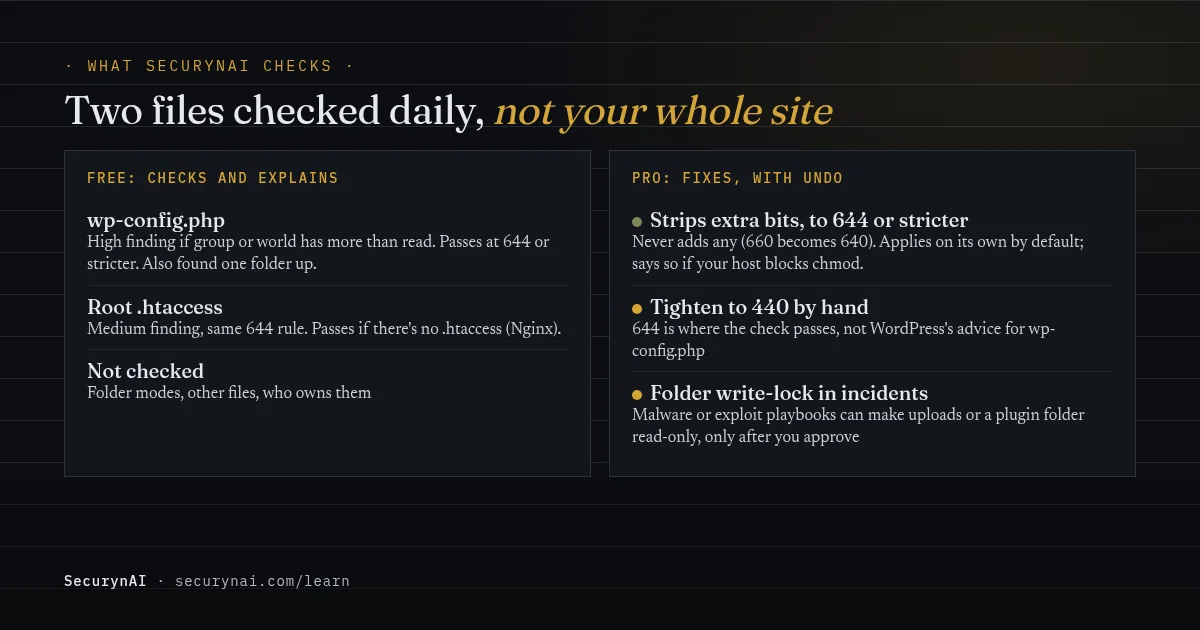
A loose wp-config.php is a high finding, so it triggers the free opt-in email for serious findings if you've switched that on. A loose .htaccess is medium.
Both show on the Hardening & Configuration page with "Manual fix required" and steps; for wp-config.php the steps recommend 440 or 400 where your host allows it, 644 otherwise. Both pass at 644 or anything stricter, so 440 and 400 pass too.
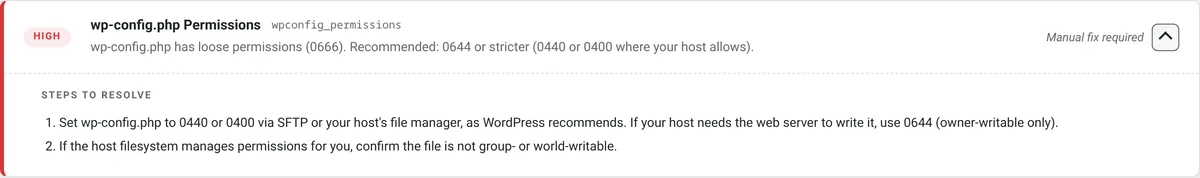
The check compares permission bits, not the digits as a number, so a mode like 0606 that looks "lower" than 644 but is world-writable still fails. Separately, the daily file scan flags any change to the contents of wp-config.php or .htaccess as a medium "Server or WordPress config file changed" finding.
The firewall starts in Monitor mode, logging attacks until you switch it to Block. It doesn't touch file permissions either way.
What Pro does with file permissions
On Pro ($79 per site per year), SecurynAI removes the extra write and read bits from a loose wp-config.php or .htaccess, down to 644 or stricter. It never adds a bit, so a file at 660 becomes 640, not a world-readable 644. It finds wp-config.php one folder up too.
Both are low-risk fixes that apply on their own by default, and each can be undone from the Activity page, back to the exact mode it had. If your host blocks chmod, the fix fails and says to tighten it by hand.
One honest gap: 644 is where the check passes, not WordPress.org's advice for wp-config.php. Pro's fix stops at 644 from a looser 664 or 666. If your host allows 440 or 400, tighten it by hand afterwards. The free check won't complain.
During an incident, Pro's malware and exploit playbooks can also make the uploads folder, or a vulnerable plugin's folder, read-only. That step waits for your approval by default, because it can stop uploads and updates. See what Pro adds for the rest. None of this replaces backups, updates or a good host.
Quick check: are your WordPress file permissions right?
- Are your folders at 755 (or 750) and files at 644 (or 640)?
- Is
wp-config.phpat 440 or 400, or as strict as your host allows? - Is nothing on the site set to 777?
- Are the files owned by your account, not
rootor the web server process? - Do plugin updates and image uploads work without asking for FTP details?
Five yeses means you're done; come back only if updates or uploads start failing. Three or four is common and fixable in ten minutes. If you're unsure about question 4, ask your host; it's the one that fixes most permission errors.
WordPress file permissions FAQ
Should the WordPress uploads folder be 777?
No. WordPress's own handbook says no directory should ever be 777, even upload directories. If uploads only work at 777, the folder is owned by the wrong user. Fix the owner, or ask your host to, and set the folder back to 755.
What permissions should wp-config.php have?
WordPress.org recommends 440 or 400 on hosts where PHP runs as your own account, so other users on the server can't read it. If your site breaks at 440, PHP runs as a different user; use 640, or 644 as a last resort, and ask your host.
Why does WordPress ask for FTP details when I install a plugin?
WordPress writes files directly only when a test file it creates is owned by the same user as WordPress's own files. If the owners differ, it falls back to asking for FTP or SSH details. Fixing ownership usually makes the prompt go away; loosening permissions doesn't.
Can a security plugin fix my file permissions?
Partly. A plugin runs as the web server user, so it can usually only change files that user owns, and some hosts block it. SecurynAI's free plugin checks wp-config.php and .htaccess daily; Pro can strip the extra bits down to 644 or stricter, with undo. Folders, ownership and 440 are still a job for you or your host.
Set the numbers once and want to know if wp-config.php ever loosens again? The free SecurynAI plugin checks it every day and tells you in plain English.
Install free →