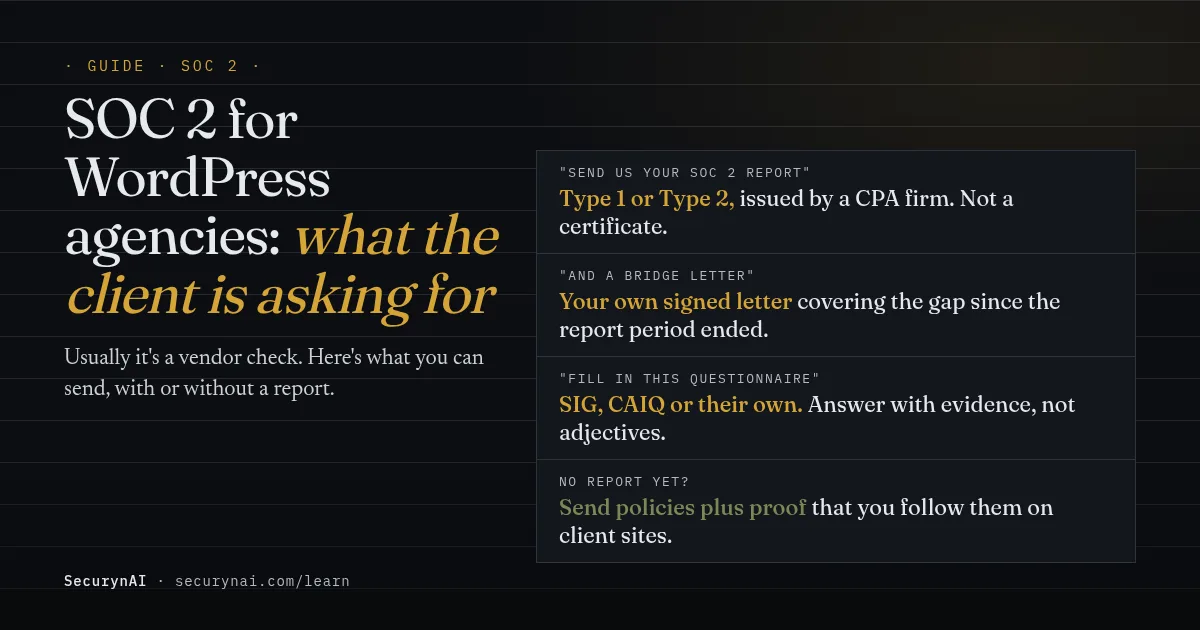
Short answer: when a client asks a WordPress agency about SOC 2, they're usually running a vendor check on you, not asking you to audit their site. A SOC 2 report is an independent CPA firm's report on your agency's own security controls. If you don't have one, most reviews still need a SOC 2 report, a questionnaire, or both.
This page is general information, not audit advice: your auditor decides what counts as evidence and what's in scope. For your own case, talk to a licensed CPA firm that performs SOC 2 examinations.
What is SOC 2, in plain English?
SOC 2 is a report, not a certificate. A CPA firm examines how a service organisation protects the systems it uses for customers, measures that against the AICPA's 2017 Trust Services Criteria (now published with revised points of focus from 2022), and gives its opinion.
The AICPA describes its SOC services as offerings "CPAs may provide" on a service organisation's controls. Its own SOC 2 page says the reports play a role in "vendor management programs" and that their use is restricted. That's why clients ask for yours under NDA instead of finding it online.
The five categories, and the one that's always there
The criteria cover five categories: Security, Availability, Processing Integrity, Confidentiality and Privacy. The Security criteria, called the common criteria (CC1 to CC9), apply to every report. The other four add their own criteria only when the engagement includes them. For most agencies, Security alone is the starting point.
SOC 2 Type 1 vs Type 2
| Type 1 | Type 2 | |
|---|---|---|
| What the auditor looks at | Your description of the system and whether your controls are suitably designed | The same, plus whether the controls actually operated effectively |
| Time covered | A point in time | A period, agreed with the auditor |
| Tests of controls in the report | No | Yes, with the results |
| What it proves to a client | You've designed the right controls | You kept running them |
Those differences come straight from the Trust Services Criteria document: a Type 1 report "does not contain an opinion on the operating effectiveness of controls nor a detailed description of tests of controls". If a client says "SOC 2", ask which type they'll accept before you plan anything.
Why a client asks a WordPress agency about SOC 2
Your agency has admin access to their website, which makes you one of their vendors. Larger clients review vendors before signing, and a request for a SOC 2 report is the shortest way to ask "how do you protect our access?"
It can feel out of proportion. On Information Security Stack Exchange, a six-person business wrote that a client was "demanding that we complete a SOC 2 Type II audit", with no IT department to run it. That's a common starting point, and it's worth asking the client what else they'll accept.
What the client usually asks for
- Your SOC 2 report, Type 1 or Type 2, and its period.
- A bridge letter if the report period ended a while ago. It's a short letter your own management signs, saying nothing material has changed since. The CPA firm doesn't audit it.
- A security questionnaire, either their own, the Shared Assessments SIG, or the Cloud Security Alliance's CAIQ, a set of yes/no questions about a provider's controls.
- Supporting documents: access, incident response and change policies, and proof you follow them.
Without a report, the questionnaire and your evidence carry the whole answer. Be specific. "We remove access within one business day of a contract ending, and here's last quarter's log" beats "we take security seriously".
Your host's SOC 2 report doesn't cover your agency
A host's SOC 2 report is about the host's system, not yours. It can cover data centres, servers, the platform and the host's own staff. It says nothing about who in your agency can log in to wp-admin on a client site.
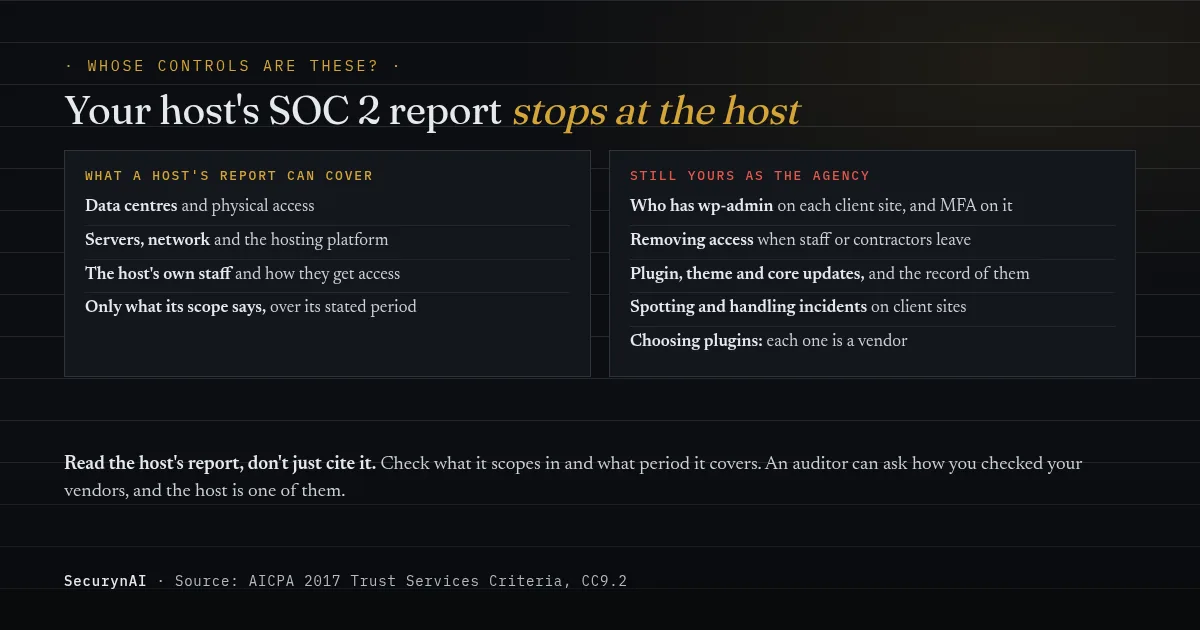
Someone asked exactly this on Stack Exchange: could they lean on their host's SOC 2 compliance? The answer said yes for the host's part, but the "more pertinent question" is whether you checked the host's controls under your own vendor policy, because "an auditor could ask for evidence".
So a line like "our sites are hosted on a SOC 2 audited platform" is true and useful, but it only answers the hosting questions. The rest is about how your team works.
SOC 2 criteria mapped to WordPress site work
Four groups of common criteria cover most of what an agency does on client sites: CC6, CC7, CC8 and CC9. The quotes below are the criteria's own words. How you meet them is up to you and your auditor, since SOC 2 sets criteria, not a technical checklist.
As one highly voted Stack Exchange answer put it, "SOC 2 Type 2 does not have specific technical requirements. What you have to do is to satisfy your assessor." Write down what you do, then do it every time.
| Criteria (2017 TSC) | What it says | On client WordPress sites |
|---|---|---|
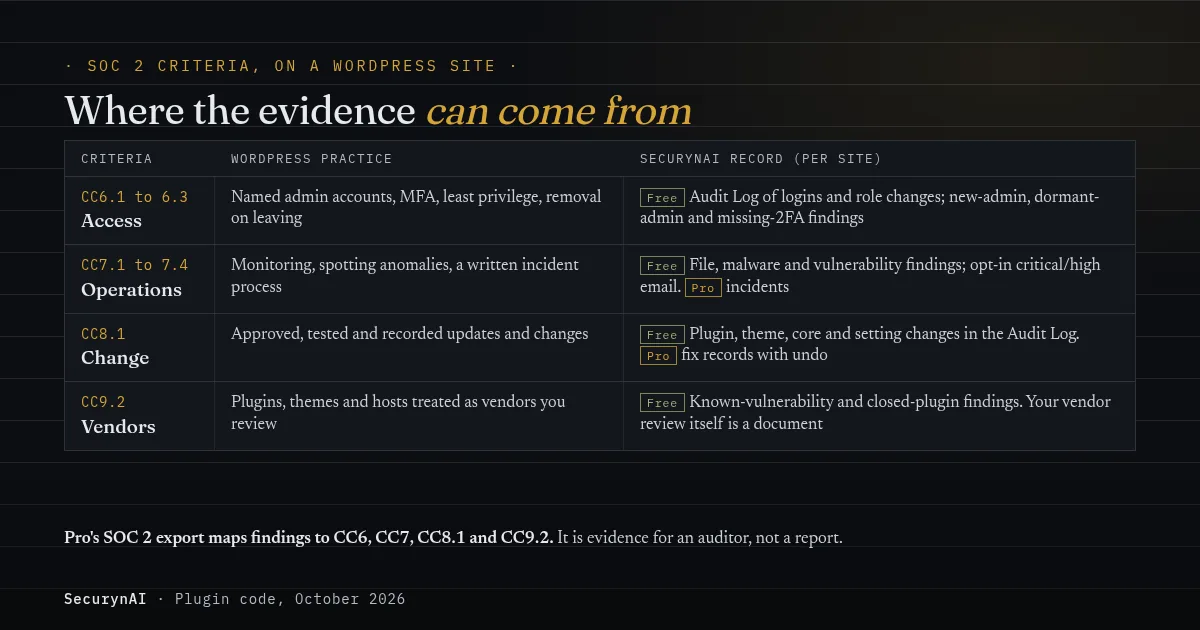
| CC6.1 to CC6.3, logical access | Register and authorise users before access; remove credentials "when user access is no longer authorized"; least privilege | Named admin accounts only, MFA on every admin, editor rather than admin where it's enough, access removed when people leave |
| CC7.1 to CC7.4, system operations | Detect new vulnerabilities, monitor "for anomalies that are indicative of malicious acts", run "a defined incident-response program" | Vulnerability alerts, file and login monitoring, a written incident process with who calls the client |
| CC8.1, change management | Changes are authorised, tested, approved and implemented | An update routine: staging or backup first, who approves, and a record of what changed |
| CC9.2, vendors | "assesses and manages risks associated with vendors and business partners" | Hosts, premium plugins and themes treated as vendors you review and keep a list of |
The numbers show why CC7 and CC9 matter on WordPress. Verizon's 2026 Data Breach Investigations Report says 31% of breaches now start with software vulnerabilities. Patchstack's State of WordPress Security in 2026 counted 11,334 new WordPress vulnerabilities in 2025, and 91% were in plugins.
In other words, every plugin is a vendor, and your update routine is a change-management control. For the details on each, see our guides to automatic updates and dormant admin accounts, and the agency playbook on offboarding a client site.
No SOC 2 report yet? What a WordPress agency can honestly send
You can't claim SOC 2 without a report, but you can show the same discipline with documents and evidence. Ask whether the client will accept this instead of a report, or as a first step. Here's a packet worth building:
- A one-page security overview: what you host, who has access, how you protect it. No claims you can't evidence.
- An access policy covering how admin accounts are created, MFA, and removal when people leave. Attach a recent access review for one site.
- A change policy for plugin, theme and core updates: when, who approves, how you roll back. Attach one month of update records.
- An incident process: who's on call, when you tell the client, how you keep evidence. Our incident-response retainer playbook is a good base.
- A vendor list: host (with its SOC 2 report, if it has one), premium plugins, backup and email services.
- Sample evidence from a real site: an Audit Log export, an access review and an alert you acted on. Strip other clients' names first.
- The completed questionnaire, pointing to the documents above.
If you already run a security audit on new client sites and send a monthly security report, half of this exists already. Clients in regulated fields will also ask about GDPR, HIPAA or PCI DSS, which are separate from SOC 2.
Should your WordPress agency get its own SOC 2 report?
Get one when a deal you want needs it, not before. A Type 2 report means running your controls through a full review period, so the work starts months before the report exists. Cost and timing depend on your size and scope, so get quotes from CPA firms rather than relying on figures online.
It's worth it when several clients ask for it, or one contract is big enough to pay for it. It's probably not yet worth it if your clients are local businesses that have never sent you a questionnaire. Either way, the habits it asks for are worth having anyway.
If you do start, choose your scope carefully. A report that covers your client-site maintenance service, with Security only, is a smaller first step than one that covers everything you do.
What SecurynAI records that you can use as SOC 2 evidence
We at SecurynAI built the plugin to keep a record of what happens on each WordPress site, and that record is useful evidence. It isn't a SOC 2 report and doesn't make your agency compliant. Here's what it records, from the plugin code as of October 2026.
In the free plugin
- Audit Log: logins, failed logins, user and role changes, plugin and theme installs, updates and removals, core updates, SecurynAI setting changes, and post and media changes. Kept 90 days by default, adjustable from 1 to 365 in Settings › General, with an Export CSV button that follows your filters.
- Access findings: a user promoted to admin, an admin with no login for 90 days, and admins without two-factor login from a known 2FA plugin. SecurynAI checks for 2FA; it doesn't provide it.
- Findings history: each finding records when it opened and when it was resolved. Dismissing one asks for a reason, which goes into the Audit Log with your name.
- Monitoring: daily file checks against WordPress.org checksums, a malware signature scan, a vulnerability feed, and an opt-in email for critical and high findings, off by default.
In Pro ($79 per site per year)
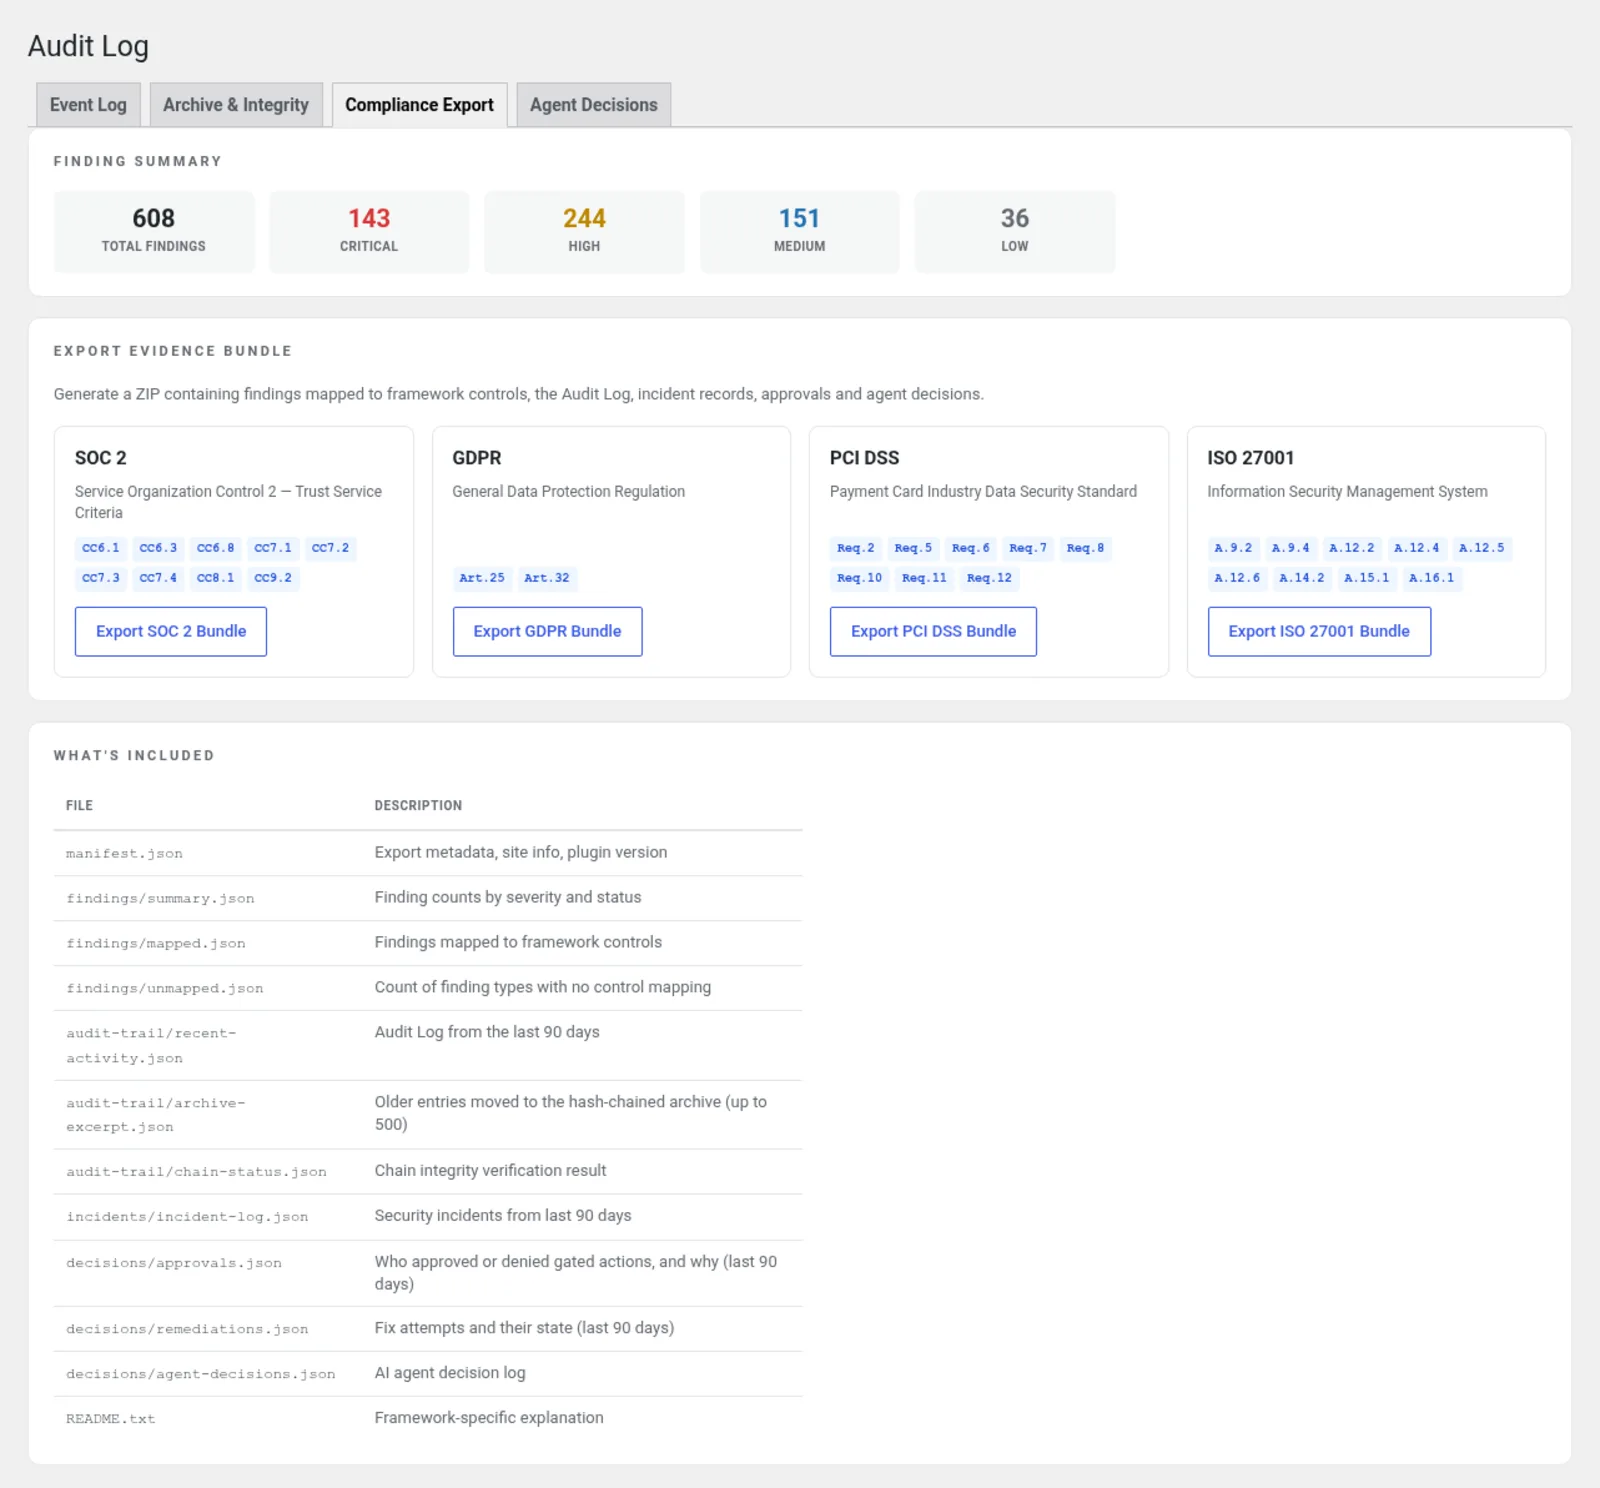
Pro adds a Compliance Export tab to the Audit Log page. The SOC 2 option downloads a ZIP of JSON files, with a manifest saying what each file covers. Its README calls it "supporting evidence for an assessor, not a certification". The mapping is our own; your auditor decides what's relevant.
- Findings mapped to criteria: every stored finding, tagged with CC6.1, CC6.3, CC6.8, CC7.1 to CC7.4, CC8.1 or CC9.2. Core file and config changes map to CC8.1, closed or unlisted plugins to CC9.2, grouped incidents to CC7.3 and CC7.4. Types with no mapping are counted in a separate file, not dropped.
- Audit trail: the last 90 days of the live Audit Log (up to 20,000 rows), plus Pro's hash-chained archive of older entries, which shows if anyone tampered with them.
- Decisions from the last 90 days: incidents, fix attempts, AI agent decisions, and approvals. Pro asks before riskier fixes, and the approvals file records each decision, who made it and why. That's useful CC8 evidence.
What it doesn't do
Each install covers one WordPress site. There's no central console across client sites, so you export each site's evidence separately. It doesn't record your agency's laptops, password manager, hiring or vendor reviews, and it can only show what it recorded. Your policies, and the auditor's opinion, come from you and your CPA firm.
SOC 2 for WordPress agencies: FAQ
Is SOC 2 a certification?
No. A SOC 2 report is an attestation report: a CPA firm examines your controls against the AICPA's Trust Services Criteria and gives its opinion. There's no certificate, and anyone who promises one is describing something else. The report covers a stated system and, for Type 2, a stated period.
Does my host's SOC 2 report cover my agency?
It covers the host's own system, within the scope and period the report states. It doesn't cover who in your agency has admin access to client sites, how you remove that access, or how you handle updates and incidents. Those are your controls, and the client's vendor review is asking about them.
Should we get SOC 2 Type 1 or Type 2?
Ask the client which one they'll accept. A Type 1 report looks at the design of your controls; a Type 2 report adds tests of whether they operated over a period, so it takes longer to produce. You can ask whether they'll take a Type 1 report while your Type 2 period runs.
Can a WordPress security plugin make us SOC 2 compliant?
No. SOC 2 is about how your agency runs: policies, people, access, vendors and the evidence that you followed them. A plugin can produce some of that evidence for each site it runs on, such as logs of logins and changes. The report itself comes only from a CPA firm.
Answering a client's security questionnaire and need a record of who logged in and what changed on their site? Install SecurynAI free on that site and start the Audit Log today.
Install free →