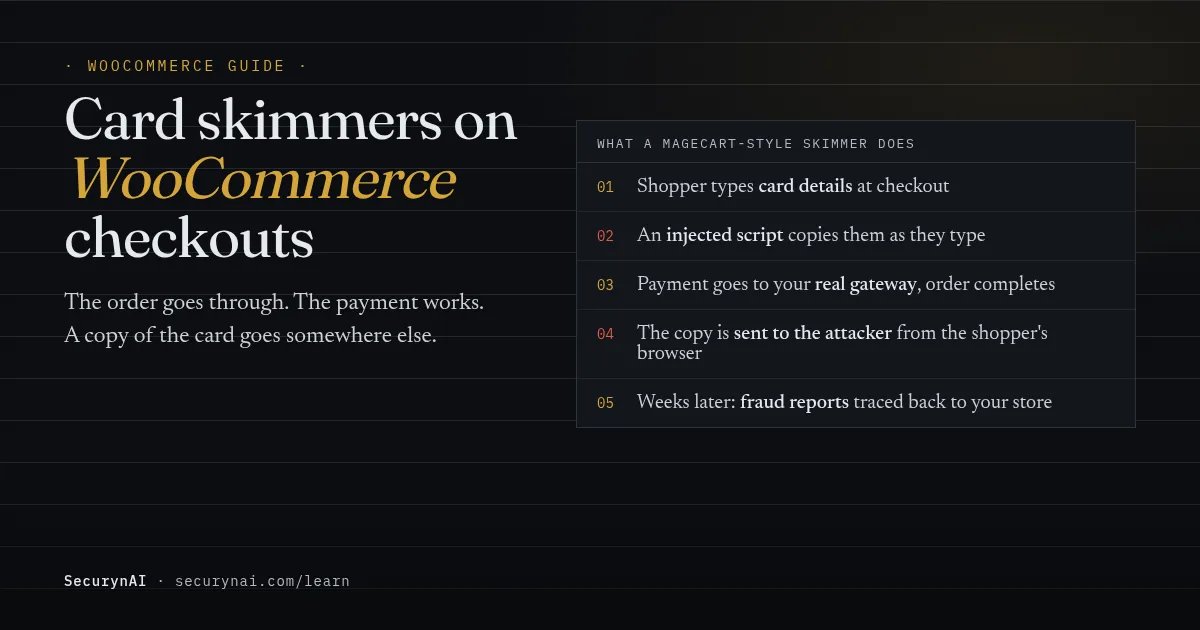
A Magecart-style card skimmer is a small piece of malicious code on a checkout page that copies card details as the shopper types them and sends them to an attacker. On WooCommerce, a credit card skimmer can sit in a template file, a JavaScript file, a plugin setting or an outside script. The order goes through, so nothing looks broken.
That's what makes skimmers different from most store problems. Card testing is loud: hundreds of failed orders. A skimmer is quiet. Often the first sign is a customer, or your payment provider, telling you that cards used on your store are turning up in fraud.
What is a Magecart card skimmer, and why does it target WooCommerce?
"Magecart" started as the name researchers gave to groups skimming Magento stores. Today it's shorthand for the technique on any platform. If your store takes card details on its own checkout page, in any form, it's a possible target.
It isn't rare. Recorded Future's Annual Payment Fraud Intelligence Report for 2024 found Magecart infections on nearly 11,000 unique e-commerce domains that year, a threefold increase on 2023. Most stores will never be one of them. But the attacks are steady, and WooCommerce is a big share of online stores.
Here's the mechanism in plain terms. The skimmer runs in the shopper's browser, on your checkout page. It reads the card number, expiry and security code from the form, then sends a copy to a server the attacker controls. Your real gateway still takes the real payment, so your sales numbers look healthy.
Don't confuse it with card testing. In one WooCommerce forum thread, an owner who suspected a phishing scam had hundreds of failed orders for one item under different names. Support said it "definitely looks like your checkout is being spammed by bots." That's card testing, covered in our fraudulent orders guide.
Where do WooCommerce card skimmers hide?
There are four common hiding places, and each one needs a different check. This matters because a scan that only looks at one of them can report "clean" while a skimmer sits in another.
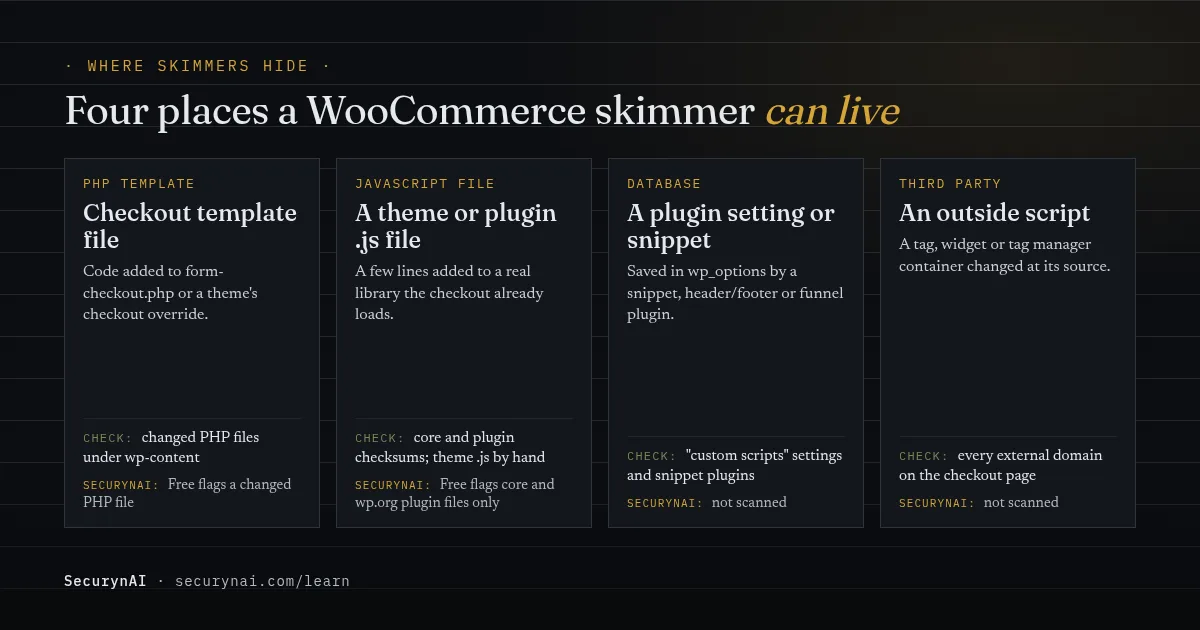
1. A checkout template file (PHP)
WooCommerce builds the checkout from template files, and themes can override them. Attackers who get in can edit one. On the WordPress.org forums, a store owner noticed card fields at checkout that their store didn't offer. They wrote that in every similar case they'd read about, "the malware code was found in form_checkout.php in Woocommerce files."
Their removed files kept coming back, because a hidden plugin folder was re-adding them. The forum moderators' advice was blunt: restore a clean backup, update everything and change hosting passwords, rather than cleaning by hand.
2. A JavaScript file the checkout already loads
Some skimmers are added to a real script file. In May 2026, security researcher Scott Helme took apart a WooCommerce skimmer injected at the start of a theme's JavaScript library, with the original code left intact below it. It read checkout fields as the shopper typed, then removed itself from the page once connected, so it's hard to spot later.
3. A plugin setting or snippet in the database
A skimmer saved in the database never changes a file on disk. In May 2024, Sucuri found a skimmer stored in a code-snippets plugin's setting in the wp_options table, hidden below dozens of blank lines. It added card fields to the WooCommerce billing form and posted what customers typed to an outside server.
Snippet plugins come up again and again. In a WordPress.org forum thread from 2024, an owner found malware stored in wp_options entries including a snippet plugin's own setting. They listed more than a dozen security scanners that missed it, and only found it by searching the database directly.
4. A plugin's "external scripts" box or an outside script
The fourth place is a script loaded from somewhere else. In May 2026, Sansec reported attackers abusing a flaw in the Funnel Builder plugin, used on more than 40,000 WooCommerce stores. They put fake Google Tag Manager code into the plugin's "External Scripts" setting, which loads on checkout pages. Version 3.15.0.3 fixed the flaw.
An analytics tag, chat widget or tag manager container can also be changed at its source. Then every store loading it serves the skimmer, with no change to your own site at all.
What are the signs of a skimmer on your checkout?
Often there are no signs on the store itself, which is why the outside signs matter. Take any of these seriously:
- Fraud reports that point back to you. Several customers say their card was misused after buying from you, or your payment provider asks about a pattern.
- Payment fields you didn't add. A card form appears even though your gateway redirects to PayPal or uses its own embedded fields, or customers mention payment methods you don't offer.
- Unknown domains on the checkout page. Your browser's developer tools show scripts or connections to a domain you can't explain.
- Settings you don't recognise. Code in a "custom scripts", header/footer or snippet plugin that nobody on your team added.
- Other signs of a break-in. A new admin you didn't create, or a changed core or plugin file. Our guide to signs of WordPress malware covers these.
How to check your WooCommerce checkout for a skimmer
Work from the outside in: what the shopper's browser loads first, then the settings, then the files. None of these steps change anything, so they're safe to run on a live store.
- Watch the checkout load. Open your checkout in a private window, add a product, and open the browser's developer tools on the Network tab. Note every domain scripts load from or send to. Your gateway, WooCommerce and your theme are expected. Anything else needs an owner.
- Read the script boxes. Check any plugin setting that takes custom code: header and footer scripts, snippet plugins, funnel and checkout plugins, and your tag manager container. Remove nothing yet; just list what's there and who added it.
- Check the checkout templates. If your theme has a woocommerce/checkout folder, ask whoever built the theme whether every file in it is expected.
- Verify files against official copies. With WP-CLI,
wp core verify-checksumsandwp plugin verify-checksums --allcompare every file, JavaScript included, against WordPress.org. They only cover core and WordPress.org plugins, not your theme or premium extensions. - Update the checkout plugins. If a checkout or funnel plugin has a known flaw, back up first, then update it before anything else.
If that's more than you want to do yourself, it's a reasonable job to hand to a developer. Give them this list and ask for the domains and settings they found, in writing.
Found a skimmer? What to do first
Your first goal is to stop new cards being copied, without destroying the evidence of how it got there. Stay calm and go in this order.
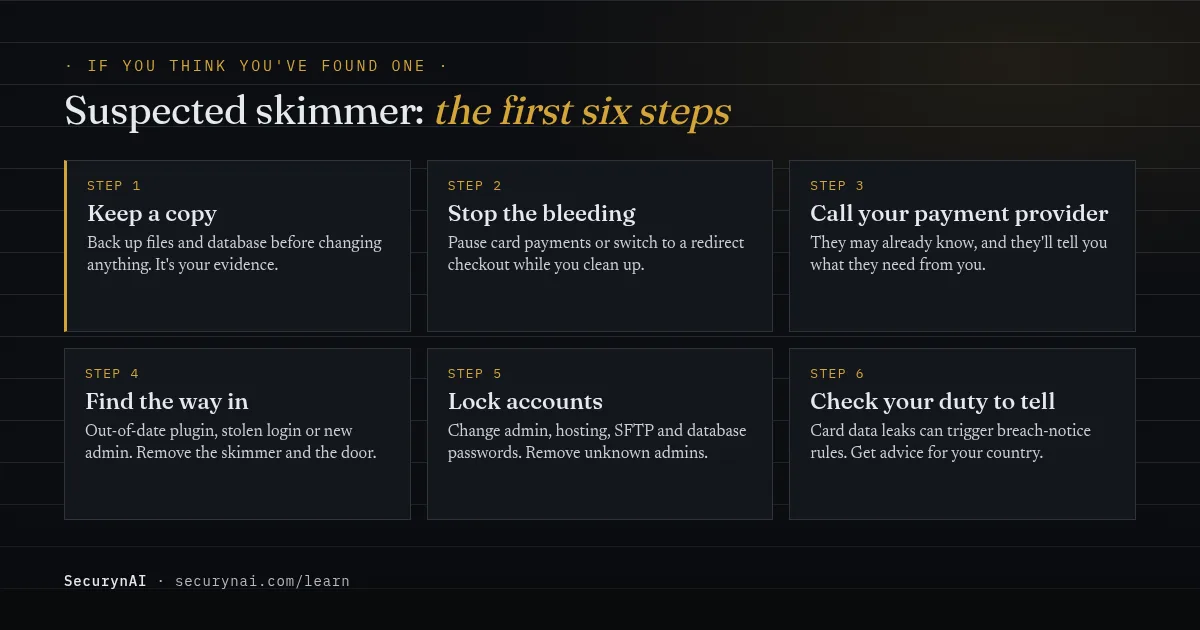
- Keep a copy. Back up the files and database as they are now, before you delete anything. That copy shows how the attacker got in.
- Stop new cards being taken. Pause card payments, or switch temporarily to a payment method that redirects to the provider's own page.
- Call your payment provider. They handle this regularly, may already have seen the pattern, and will tell you what they need for their own process.
- Remove the skimmer and the way in. The skimmer is the symptom. The cause is usually an outdated plugin or a stolen login. Restoring from a clean backup is often faster than cleaning by hand, as the forum moderators above advised.
- Lock every account. Change admin, hosting, SFTP and database passwords, and remove any admin you can't name.
- Check whether you have to tell anyone. Card data leaks can trigger breach-notice rules. Start with our guides to GDPR data breaches and US state breach laws. This is general information, not legal advice.
For the clean-up itself, our guides on removing WordPress malware and restoring from a backup after a hack go step by step.
How to make your WooCommerce checkout harder to skim
The best protection is having less on your checkout page for a skimmer to hide in. These steps are free, and most take an afternoon.
- Prefer a redirect or embedded payment form. If cards are typed on the payment company's page, a skimmer on yours has much less to read.
- Cut checkout scripts to the minimum. A chat widget or marketing pixel may earn its place on your homepage. It rarely needs to run where cards are typed.
- Pin outside scripts you can. Subresource Integrity gives the browser a hash a script must match, and it refuses to load one that changed. It only suits files that don't change, so not tag managers.
- Limit where scripts can come from. A Content-Security-Policy header can block scripts and connections to unknown domains. Start in report-only mode, as our security headers guide explains, because a strict policy can break checkout.
- Turn off the dashboard file editor. Adding
define( 'DISALLOW_FILE_EDIT', true );to wp-config.php stops anyone editing theme and plugin files from wp-admin. - Treat snippet and checkout plugins as high risk. Keep them updated, remove ones you don't use, and vet new ones with our extension vetting checklist.
Card rules point the same way. PCI DSS requirements 6.4.3 and 11.6.1, which the PCI Security Standards Council says focus on payment page scripts being "properly authorized, checked for integrity, and monitored for tampering," took effect in 2025.
Many smaller stores file SAQ A instead. Since April 2025 that includes confirming your site "is not susceptible to attacks from scripts," either through your own controls or your provider's written confirmation. Our PCI DSS for WooCommerce guide explains which applies. This is general information, not compliance advice.
What SecurynAI can and can't see on a skimmer
We at SecurynAI would rather you know the limits than trust us blindly here. The free plugin catches a skimmer that changes a known file. It doesn't scan plugin settings, the database or outside scripts.
On the free plugin
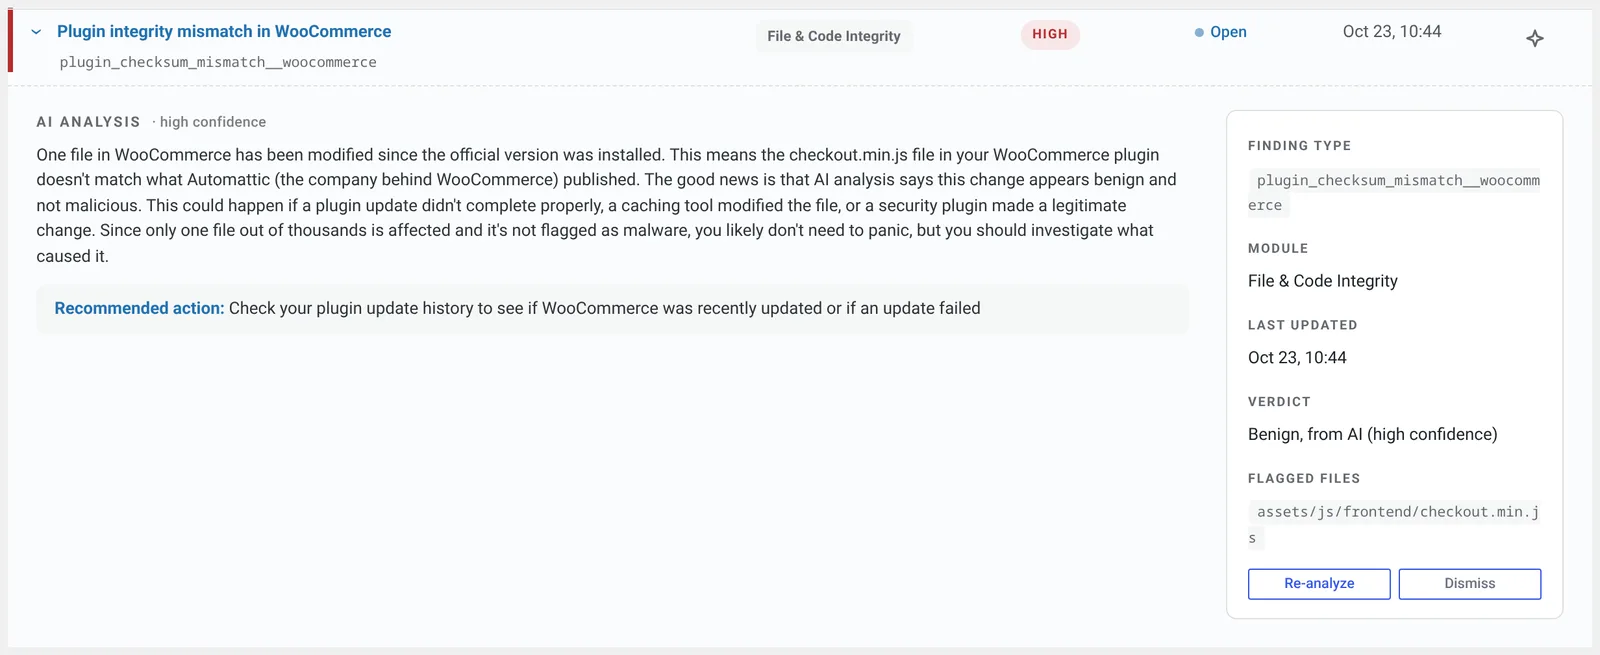
- Core and WordPress.org plugin files: the daily scan compares every file in WordPress core and in each WordPress.org plugin, WooCommerce included, against official checksums. A JavaScript file with a skimmer added fails that check.
- PHP files under wp-content: SecurynAI keeps a fingerprint of each one, theme checkout templates included, and flags a file that changes without a version update. A new PHP file that appears inside a plugin or theme without an update is flagged too.
- Malware patterns: the same scan checks every PHP file under wp-content, including .phtml and other PHP-runnable files, against 13 bundled signatures and flags clear obfuscation, like a decoder fed into eval. It detects only, with no cleanup and no live signature feed.
- The way in: new admins and role changes are flagged, failed logins are locked out, and the hardening check reports whether the dashboard file editor is still on.
- Firewall: it starts in Monitor mode, logging attacks without blocking until you switch it to Block. Login lockout works in either mode.
With your own AI key, a flagged file's explanation can say what kind of code it looks like, including a credit card skimmer.
A changed file is high severity, critical if the AI is sure it's malicious. If the AI thinks the change is harmless, it says so on the finding, but the severity stays high: text planted in a tampered file shouldn't be able to talk the alert down. Opt-in email alerts cover critical and high findings, so a likely skimmer reaches you the same day.
On Pro ($79 per site per year)
Pro can act on those findings. It can restore a changed core file, or a changed file in a WordPress.org plugin, from the official copy, checking the download's checksum first. It can also move a file that matches a malware signature into quarantine, but it won't move a file that belongs to an installed plugin or your active theme.
Your Pro policy rules decide whether each fix runs on its own or waits for approval. See what Pro adds for the full list.
What you'll still need to check yourself
Neither version scans JavaScript in your theme or premium extensions, plugin settings, the database or third-party scripts. That covers three of the four hiding places above, so the manual checks still matter. SecurynAI doesn't replace backups, updates or your payment provider's own fraud tools.
WooCommerce card skimmer FAQ
Is Magecart only a Magento problem?
No. The name comes from early attacks on Magento stores, but it now means any script that copies card details from a checkout page. Recent campaigns researchers have written up target WooCommerce through its templates, theme files, plugin settings and checkout plugins.
If Stripe or PayPal handles my payments, can I still be skimmed?
A full redirect to the payment company's own page removes most of the risk, because cards aren't typed on your site. Embedded card fields are safer than a form on your server, but a skimmer can still add a fake card form or read the billing details around them. That's why PCI DSS asks SAQ A merchants about script attacks.
Is a wave of failed orders a skimmer?
Usually not. Hundreds of failed orders for a cheap product is card testing: bots checking stolen cards against your checkout. A skimmer is quiet. Orders look normal, and the first sign is often customers or your payment provider reporting fraud.
Can a security plugin detect a card skimmer?
Partly. File checks catch a skimmer that changes a known file, such as a WordPress core file, a WordPress.org plugin file or a PHP template. Skimmers saved in plugin settings, in the database or in third-party scripts need a check of what actually loads on the checkout page.
Want to know the day a core file, a WordPress.org plugin file or a checkout template on your store changes? The free SecurynAI plugin starts checking from the day you install it.
Install free →