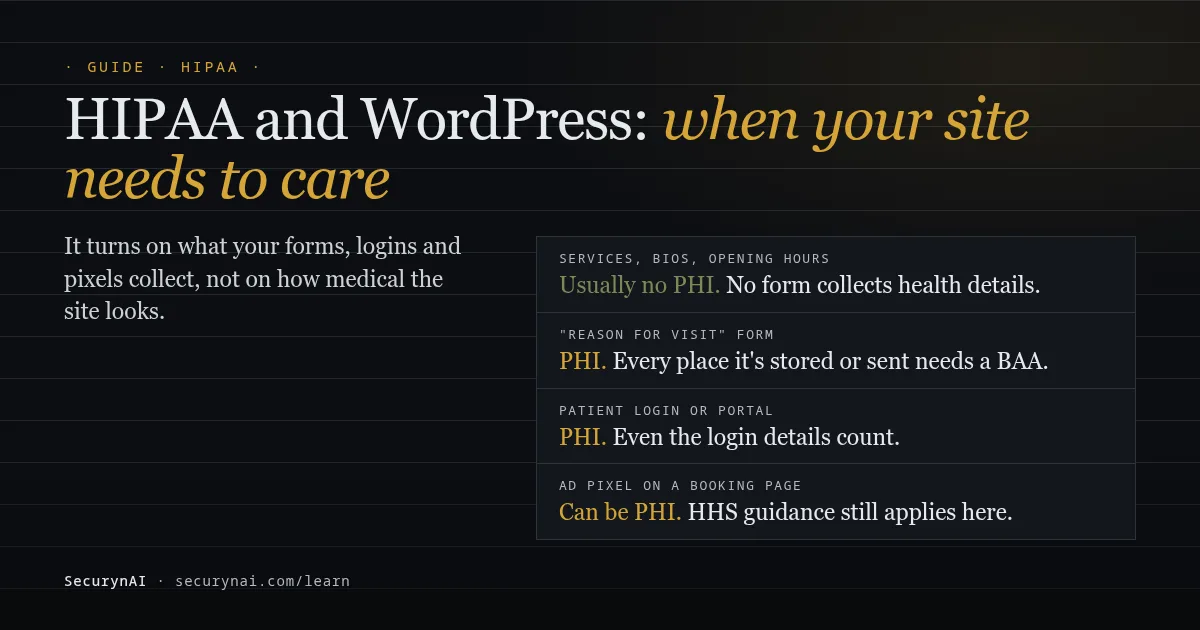
Short answer: HIPAA and WordPress only meet when your site handles protected health information (PHI) for a covered healthcare business. PHI is health information that identifies a person, such as a name next to a reason for a visit. Once a form, login or pixel handles it, every vendor in that path needs a business associate agreement (BAA).
This page is general information about US law, not legal advice. For your own practice or client, talk to a healthcare lawyer, or read the guidance from the HHS Office for Civil Rights (OCR), which enforces HIPAA.
Does HIPAA apply to your WordPress site?
Two questions decide it: is the business covered by HIPAA, and does the website touch PHI? You need a yes to both before HIPAA's website rules come into play.
HIPAA covers health plans, clearinghouses and healthcare providers who send health information electronically in connection with standard transactions such as insurance claims, according to HHS's business associate guidance. It also covers their business associates. A wellness coach or cash-only studio may sit outside it, but check before you assume.
The second question is about data, not about how medical the site looks. Under 45 CFR 160.103, PHI is health information about a person's past, present or future health, care or payment that identifies them, or could reasonably be used to. A page about knee surgery isn't PHI. A form where Jane says her knee hurts is.
| What's on the site | Likely PHI? | Why |
|---|---|---|
| Services, staff bios, opening hours, blog posts | Usually no | Nobody's health details are collected |
| "Call me back" form: name, phone, preferred time | Low risk | Contact details only, but it still shows the person contacted a provider |
| Appointment form asking the reason for the visit | Yes | Identifies a person and their health concern |
| Intake forms, file uploads, symptom checkers | Yes | Health details tied to a named person |
| Patient login, portal or member area | Yes | HHS treats patient login details as identifiable |
| Ad or analytics pixel on pages like those above | Can be | The pixel may receive what the visitor types or selects |
If the honest answer is "no PHI anywhere", the site's HIPAA risk is small. Keep it that way on purpose: decide which forms are allowed to ask what, and write it down.
Where a WordPress site starts holding PHI
Most sites start holding PHI through a form, and the form plugin is rarely the only place the data lands. A submission is saved in the database, emailed to the front desk and copied into every backup.
Forms and their copies
General form plugins aren't built for this, and their own support teams say so. When one site owner asked on the WordPress.org support forums whether a popular form plugin could take medical information, support replied that the needed protections "are not inherently built into general form plugins".
In another forum thread, a plugin team explained it doesn't "store any of the data collected by your forms on our own servers", and that uploads go inside wp-content/uploads. Good for privacy, but it means your host holds the PHI.
The notification email is the copy people forget. In a thread asking whether a form plugin would sign a BAA, the reply warned that "passing form information over regular email is not secure". If the email includes the answers, the mail service and inbox are part of the PHI path too.
Patient logins
A login area changes things even before anyone types a symptom. HHS's tracking guidance says that when someone enters login or registration details on a patient portal page, "such information meets the definition of IIHI", meaning individually identifiable health information. Membership plugins, booking accounts and course logins for patients all count.
Who needs to sign a business associate agreement?
Any outside party that creates, receives, stores or sends PHI for the practice needs a signed BAA before it handles that data. A BAA is the contract HIPAA requires, setting out what the vendor may do with PHI, how it protects it, and that it reports breaches back to you.
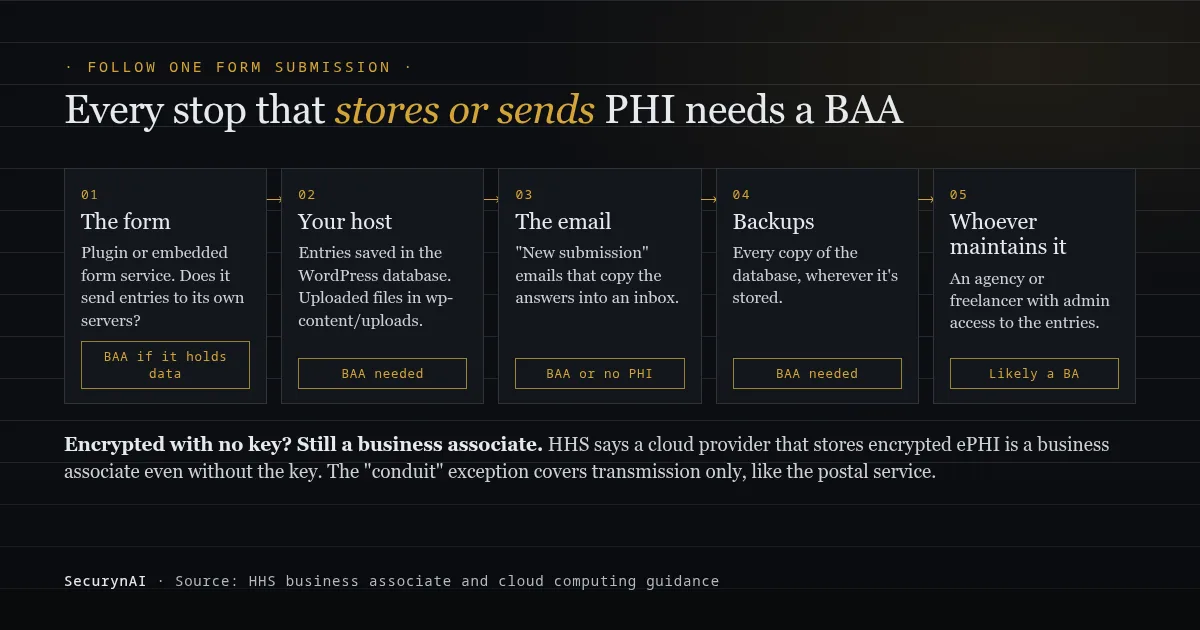
On a WordPress site, that usually means:
- The host, because entries live in its database. HHS's cloud computing guidance says a provider storing encrypted ePHI is still a business associate "even if the CSP cannot view the ePHI".
- The form service, if entries pass through or are stored on its servers.
- The email or messaging service, if notifications carry the answers.
- Backup and storage services holding copies of the database.
- You, if you maintain the site. HHS lists an "IT contractor or vendor" providing maintenance or support that involves ePHI as a business associate.
Don't lean on the "conduit" idea for storage. HHS says that exception is "limited to transmission-only services", like the postal service. A host that keeps the data isn't a conduit.
If a vendor won't sign a BAA, it can't be in the PHI path. That's why many practices keep WordPress as the public brochure and link out to a separate patient system, whose vendor signs one, for intake, booking and messaging.
Tracking pixels on healthcare WordPress sites after the 2024 ruling
Part of HHS's tracking-pixel guidance was struck down in 2024, but the parts that matter for forms and logins still stand. It covers analytics tags, ad pixels and session-recording scripts.
On June 20, 2024, a federal court in Texas vacated the guidance where it said HIPAA applies when a tool connects a visitor's IP address with a visit to a public page about a health condition or provider. HHS's bulletin page carries that notice and says HHS "is evaluating its next steps".
What remains is still a lot. The bulletin says trackers on pages behind a login "generally" have access to PHI. So can trackers on public pages where someone books an appointment or enters symptoms. And any disclosure to a tracking vendor without patient authorization "requires the vendor to have a signed BAA".
The practical fix is simple to say: keep marketing pixels off login, booking, intake and symptom pages, unless the vendor has signed a BAA. Check your tag manager too, since pixels often get added there without anyone touching WordPress.
HIPAA's technical safeguards, translated for WordPress
If the site holds electronic PHI, the HIPAA Security Rule expects technical safeguards on it. They're listed in 45 CFR 164.312, some "Required" and some "Addressable", meaning you assess them and document your decision.
| Safeguard (164.312) | What it means on WordPress | Where SecurynAI helps |
|---|---|---|
| Access control: unique user IDs, automatic logoff, encryption | One account per person, no shared logins, sessions that end, encrypted storage of entries | Flags admins without 2FA and new or changed admins. Doesn't provide 2FA or encrypt your database |
| Audit controls | Record activity on systems that hold ePHI | Audit Log of logins, failed logins, user, role, plugin and setting changes. Doesn't record who viewed a form entry |
| Integrity | Spot improper changes or deletion of ePHI | Watches site files for changes and known malware patterns. Doesn't watch form entries in the database |
| Person or entity authentication | Prove users are who they claim | Login lockout and risky-login checks. 2FA comes from another plugin |
| Transmission security | Encrypt data in transit | Checks for the HSTS header. HTTPS itself is set up by your host |
OCR's 2024 breach report to Congress counted 663 reported breaches affecting 500 or more people in 2024, and found that hacking or IT incidents made up 81% of them.
The same report names "information system activity review, audit controls, and person or entity authentication" among the key areas for improvement, and says risk analyses often miss "web, email, and backup servers". In other words, the website and its copies.
HHS also proposed a stricter Security Rule on January 6, 2025. As of October 2026 it's still a proposal, with no final rule published.
What SecurynAI does, and doesn't do, on a HIPAA site
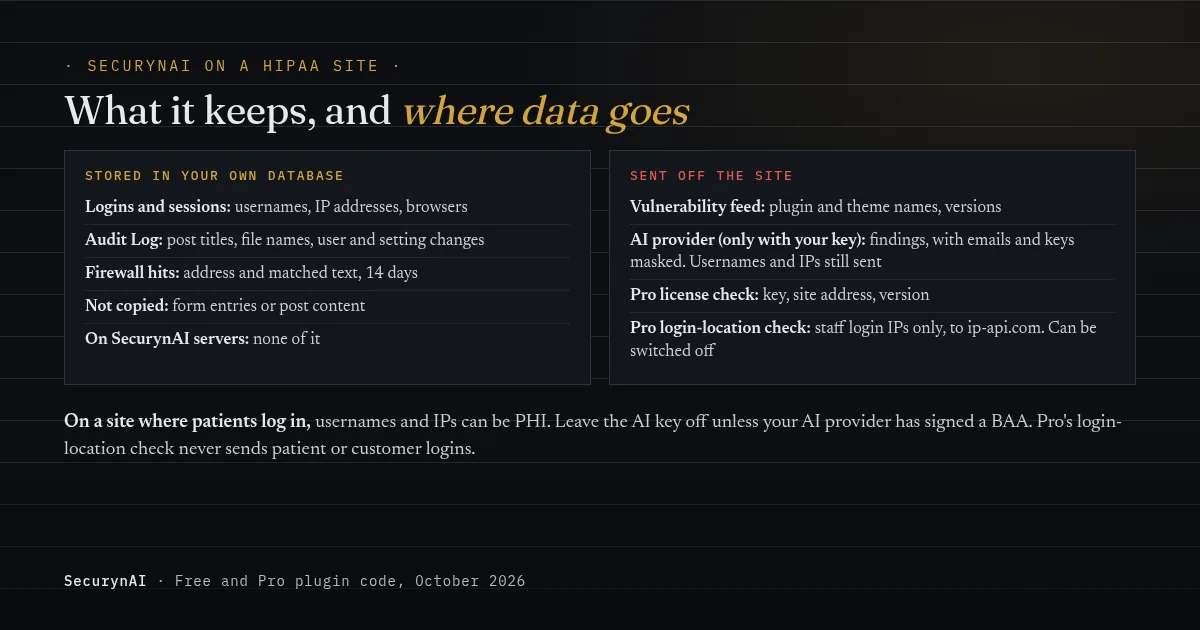
We at SecurynAI built the plugin to keep its records inside your own WordPress database, and we run no servers that collect them. Still, a security plugin holds personal data too, so here's exactly what it keeps and what leaves the site, based on the plugin code as of October 2026.
What it stores
- Logins and sessions: usernames, IP addresses and browser details, plus a login profile per user to spot unusual logins.
- Audit Log: logins, user and role changes, plugin, theme and setting changes, and post titles and media file names when content changes. Kept 90 days by default, adjustable from 1 to 365 in Settings › General. Old login attempts, ended sessions and role history are cleared on the same schedule.
- Firewall hits: the address requested, the browser, and up to 512 characters of the text that matched a rule, kept 14 days.
It doesn't copy form entries or post content. It adds suggested privacy-policy text listing all of this, and joins WordPress's personal data export. An erase request removes a user's login profile but keeps security records until retention deletes them, because they're needed to investigate attacks. Confirm that basis with your lawyer.
What leaves the site
The free plugin sends plugin and theme names and versions to the vulnerability feed, and checks file checksums against WordPress.org. Alert emails are off by default; when on, they list only each finding's title and severity, not visitor data.
AI explanations are optional and go straight to your own provider (OpenAI, Anthropic or Google Gemini). SecurynAI masks email addresses and secrets first, but usernames and IP addresses are still sent, and a risky-login finding can name a patient.
So on a site where patients log in, leave the AI key off unless your provider has signed a BAA. Pro's Copilot questions are masked the same way. Our AI key checklist covers the rest.
With Pro, the license check sends your license key, site address and plugin version to the WisdmLabs license server. Pro's impossible-travel check sends staff login IPs (accounts that can edit posts) to ip-api.com, a third-party service, over plain HTTP. Patient and customer logins are never sent, and you can switch the check off under Settings › Modules.
What Pro adds for evidence
Pro keeps a 90-day hash-chained copy of expired Audit Log entries, so tampering shows up. WordPress's export and erase tools skip it, since editing it would break the chain. Its compliance export is a ZIP of findings and log evidence mapped to SOC 2, GDPR, PCI DSS and ISO 27001. There's no HIPAA mapping, and it isn't a certification.
The limits, plainly: SecurynAI isn't offered as a BAA-covered service, doesn't encrypt form entries, doesn't decide whether an incident is reportable, and notifies no one. It can't make a site HIPAA compliant. It gives you detection and a record of what happened.
If PHI may have been exposed through your site
Under HIPAA, a breach of unsecured PHI starts a 60-day outer limit for notifying the people affected. The Breach Notification Rule (45 CFR 164.400 to 414) says notice must go out "without unreasonable delay and in no case later than 60 days following the discovery of a breach".
| Who | When |
|---|---|
| Affected individuals | Without unreasonable delay, no later than 60 days after discovery |
| HHS, 500 or more people | Same 60-day limit |
| HHS, fewer than 500 people | Annual log, due within 60 days after the end of the calendar year |
| Media | More than 500 residents of one state or jurisdiction, within 60 days |
| A business associate (your host, or you as the agency) | Tells the practice within 60 days of discovery, or sooner if the BAA says so |
HHS presumes an impermissible disclosure is a breach unless a risk assessment shows a low probability the PHI was compromised. "Unsecured" means not encrypted or destroyed to HHS's standard. State breach notification laws can apply on top.
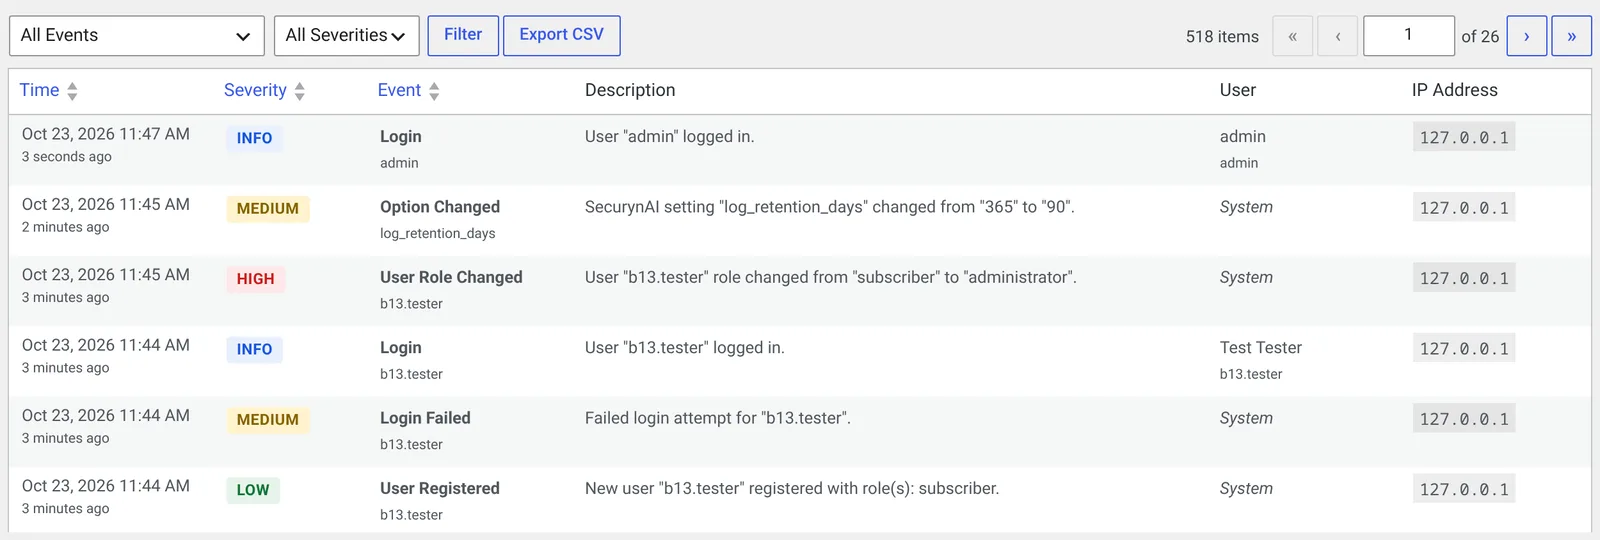
A security plugin's job here is evidence, not the legal call. Export the Audit Log CSV and the relevant findings before retention deletes them, then give the timeline to whoever decides on notification. For the clean-up, see what to do after a defacement and restoring from a backup.
Checklist: HIPAA and your WordPress site
Use this whether you own the practice's site or look after it for a client:
- List every form and what it asks. Remove health questions from any form whose tools haven't signed a BAA.
- Trace each form's copies: database, notification email, uploads folder, backups, any connected service.
- Get a signed BAA from every vendor in that path, or move the form to a service that will sign one.
- Strip answers out of notification emails so they only say "new submission".
- Remove ad and analytics pixels from login, booking, intake and symptom pages, including tags added through a tag manager.
- Give everyone their own account, require 2FA for anyone who can see entries, and remove old users.
- Turn on logging and alerts: set the Audit Log retention you need and export it regularly, since HIPAA keeps required security documentation for six years under 164.316.
- Agencies: decide whether you're a business associate for each client, and sign a BAA where you are.
If you can tick all eight, the website part of your HIPAA work is in good shape. Risk analysis, policies and training sit with the practice. For the basics, see our hardening checklist and login page guide.
HIPAA and WordPress FAQ
Can I use a normal contact form for appointment requests?
If it only asks for a name, phone number and preferred time, the risk is low. Once it asks why the person is coming in, or lets them describe symptoms, it collects PHI, and the form, host, email and backups all need to be covered. Many practices keep the public form to contact details only.
Does my web developer or agency need to sign a BAA?
If they maintain a site that stores PHI and can reach it, very likely yes. HHS lists IT contractors who provide maintenance or support involving ePHI as business associates. If the site never holds PHI, there's nothing for them to sign for.
Is Google Analytics on a clinic website a HIPAA violation?
It depends on the page. A court vacated part of HHS's tracking guidance for public pages in 2024, but the guidance still covers patient logins and pages where people book appointments or enter symptoms. On those pages, a tracking vendor that receives PHI needs a BAA or the tracking has to go.
Does SecurynAI make my WordPress site HIPAA compliant?
No. It isn't offered as a BAA-covered service, and it doesn't decide whether an incident is reportable or notify anyone. It records logins and changes, watches files, and gives you evidence to work with, which is one part of the safeguards HIPAA expects.
Looking after a practice's WordPress site and want a record of who logged in and what changed? Install SecurynAI free. It keeps its records in your own database and works without an AI key.
Install free →