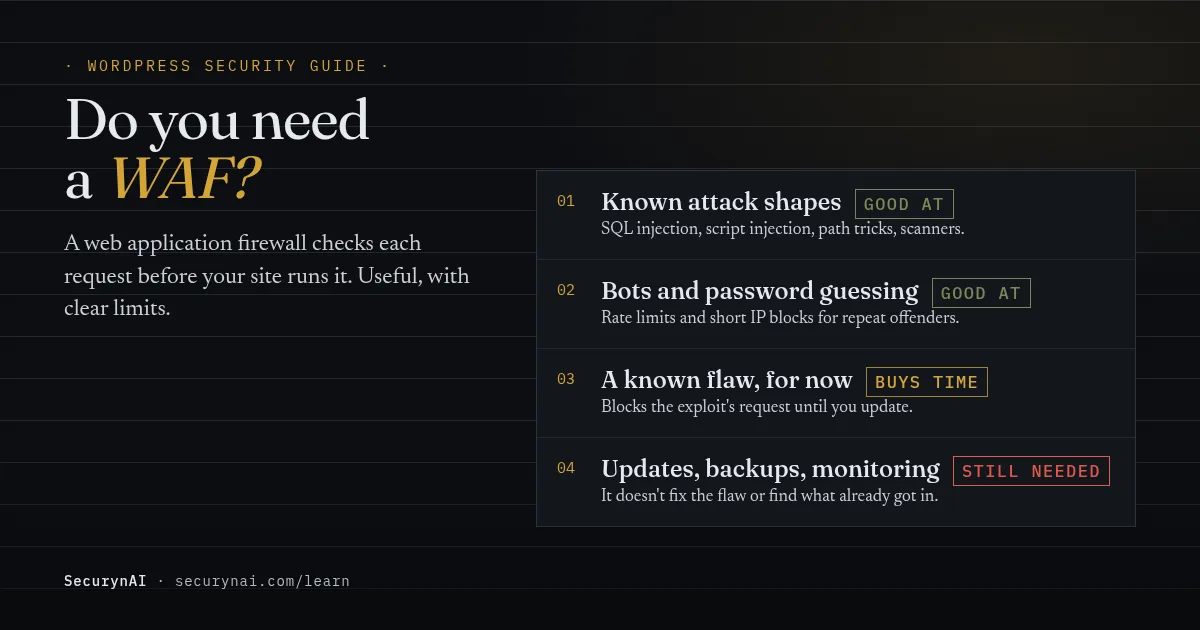
A web application firewall (WAF) is a filter that checks every request to your site and blocks the ones that look like attacks before your code runs them. So do you need a WAF for WordPress? "WAF" gets sold as a one-word answer to security, which it isn't. It's a useful layer with clear limits.
This guide explains what a WAF actually blocks, the difference between an edge WAF and a plugin firewall, what no firewall can fix, and how to decide what your site needs. We'll be upfront: SecurynAI includes a plugin firewall, so we'll also say plainly what ours doesn't do.
What does a web application firewall actually do?
A WAF compares each incoming request against patterns of known attacks, and lets everything else through. If someone sends a search box a chunk of SQL, or asks for a file path stuffed with ../../, the rule matches and the request is stopped. Ordinary visitors never notice it.
That's pattern-matching at the door. A WAF doesn't know what your site does after a request gets in, and it doesn't look at the files already on your server. It answers one question per request: does this look like an attack I know?
Some WAFs also count requests, so one IP that hits your login page 500 times a minute can be slowed or blocked. And many can block a specific attack against a known flaw. OWASP calls this virtual patching: a layer that "detects and blocks matching exploitation attempts" without changing the vulnerable code.
Edge WAF or plugin firewall: where it runs changes what it stops
The biggest difference between WAFs isn't the brand, it's where they sit in the path between a visitor and your site. There are three common places, and each sees a different slice of the problem.
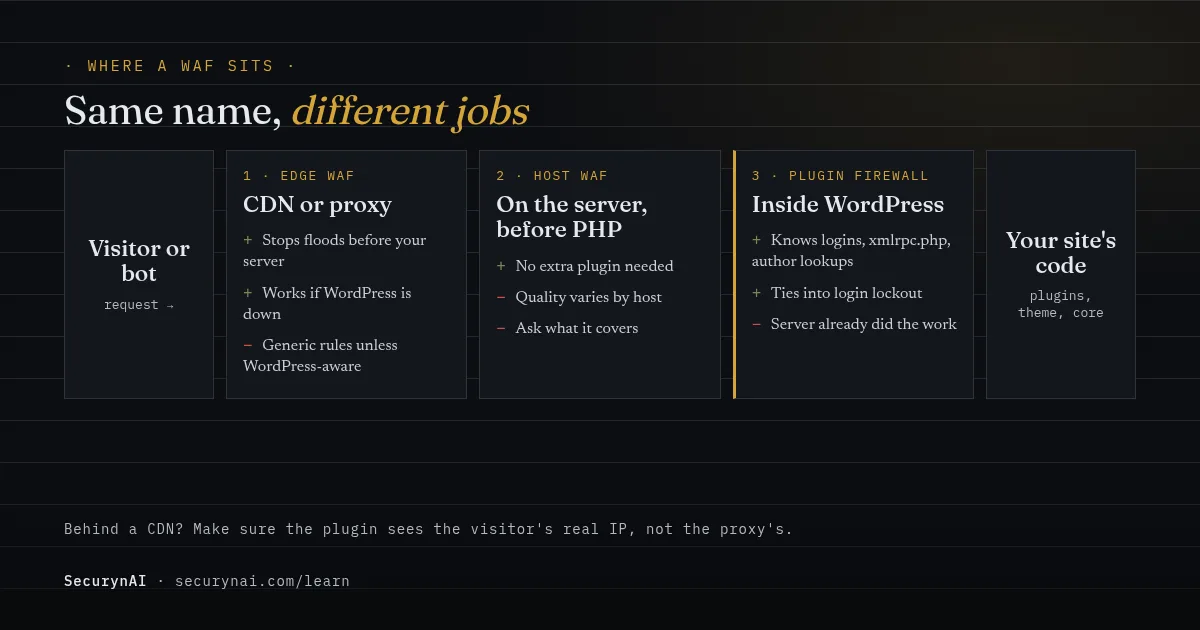
- Edge WAF. A CDN or proxy in front of your server. Bad traffic is dropped before it costs your server anything, and it keeps working even if WordPress is broken. It knows the web in general, not your site's logins or plugins.
- Host WAF. Rules your hosting company runs on the server, before PHP starts. Quality varies a lot from host to host, so ask what's included.
- Plugin firewall. Runs inside WordPress. It sees WordPress-shaped traffic (logins,
xmlrpc.php, username lookups) and can tie blocks to your login lockouts. But every request it checks has already reached your server and started PHP.
| What you need | Edge WAF | Plugin firewall |
|---|---|---|
| Stops a large flood (DDoS) | Yes, that's its job | No, the server already took the hit |
| Knows WordPress logins and endpoints | Only if its rules are WordPress-aware | Yes |
| Works if WordPress won't load | Yes | No |
| Sees the visitor's real IP | Yes | Only if your site is set up to pass it on |
| Setup | DNS change or host setting | Install a plugin |
Behind a CDN, make sure your plugin sees the real visitor
When a site sits behind a proxy, every request arrives from the proxy's IP. A plugin that doesn't read the forwarded IP will block the proxy instead of the attacker. In one WordPress.org support thread, an owner reported their security plugin "keeps banning Cloudflare IPs instead of the offending IPs".
If you run both layers, check that your plugin logs real visitor IPs before you let it block anything. In SecurynAI, that's the "Trust proxy headers" setting, used by both the firewall and login lockout. Turn it on only when your site really is behind a trusted proxy.
What a WAF is good at blocking
Most traffic that hits a small site is automated, and automated attacks are exactly what a WAF's patterns are built for. Imperva's 2025 Bad Bot Report found automated traffic made up 51% of all web traffic in 2024, with malicious bots at 37% of internet traffic.
- Known attack shapes. SQL injection, script injection, path traversal and attempts to read files like
/etc/passwd. Our guide to SQL injection shows what these requests look like. - Scanners and repeat offenders. An IP that trips rule after rule can be blocked for a while, so it stops probing.
- Password guessing. Rate limits on
wp-login.phpandxmlrpc.php. The XML-RPC brute force guide covers why that file gets hammered. - A known flaw you haven't patched yet. If your WAF provider writes a rule for it, you get breathing room until you can update safely.
What no WAF can fix for you
A WAF blocks attacks that look like attacks it knows. It doesn't fix the flaw underneath. OWASP is direct about virtual patching: "It does not remove the underlying vulnerability." If a slightly different request triggers the same bug, the rule may not catch it.
The numbers show why that matters. Patchstack's State of WordPress Security in 2026 counted 11,334 new vulnerabilities in 2025, 91% of them in plugins. For heavily targeted flaws, the weighted median time to first exploit was 5 hours.
The same report tested hosting defences against real WordPress exploits. In one experiment, "traditional defences only blocked 12% of WordPress-specific vulnerability attacks"; in a broader test, 26% of attacks were blocked. Patchstack sells its own protection, so read that as a vendor's test. The direction is still worth knowing: generic rules miss a lot of WordPress-specific bugs.
Things a WAF won't handle on its own:
- Logged-in abuse. A flaw that lets a subscriber do an admin's job often uses normal-looking requests. Patchstack notes broken access control is "very difficult to defend against using traditional WAFs".
- Stolen passwords. A correct username and password looks like a normal login. That's a job for two-factor, covered in our login page guide.
- Malware already on the site. A WAF checks requests, not files. If something got in last month, it's still there.
- Plugins with no fix. Patchstack found 46% of 2025's vulnerabilities had no fix by public disclosure. Sometimes the only safe move is removing the plugin.
So a WAF works best alongside updates, not instead of them. Our automatic updates guide explains what to let update on its own.
So, do you need a WAF for your WordPress site?
For most sites, some kind of WAF is worth having, and the right kind depends on your situation. Community opinion runs both ways. In one Local community thread, a developer argued that if you can pay, "you're probably better off with a WAF ... than relying on a plugin".
Others point out the two do different jobs. In a WordPress.org thread asking how a CDN differs from a security plugin, one reply put it bluntly: "Cloudflare is not a security plugin." Both views have a point. Here's how we'd decide.
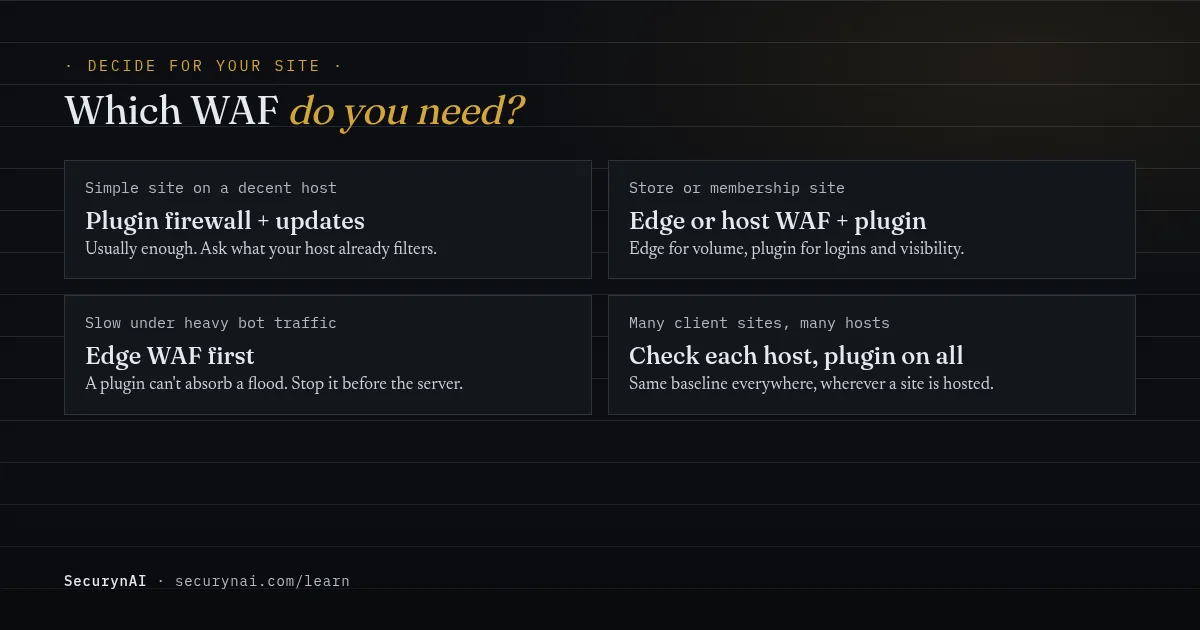
- A brochure site on a decent host. A plugin firewall with login lockout, plus prompt updates, covers the usual automated traffic. Ask your host what it already filters.
- A store or membership site. More logins, more forms, more to lose. Use an edge or host WAF if one is available, and keep a plugin layer for login protection and to see what's being tried.
- A site that's slow under bot traffic. Start at the edge. A plugin can't absorb volume. Our guide to a suddenly slow WordPress site helps you tell bots from ordinary causes.
- An agency looking after many sites. Hosts differ, so check each one's WAF. A plugin firewall gives every site the same baseline wherever it's hosted.
Cost is rarely the barrier. Some edge providers have a basic tier: Cloudflare's own managed rules documentation lists a Free Managed Ruleset as "Available on all Cloudflare plans", with its fuller Cloudflare Managed Ruleset on paid plans. Many security plugins include a firewall in their free version too.
What SecurynAI's firewall does, and what it doesn't
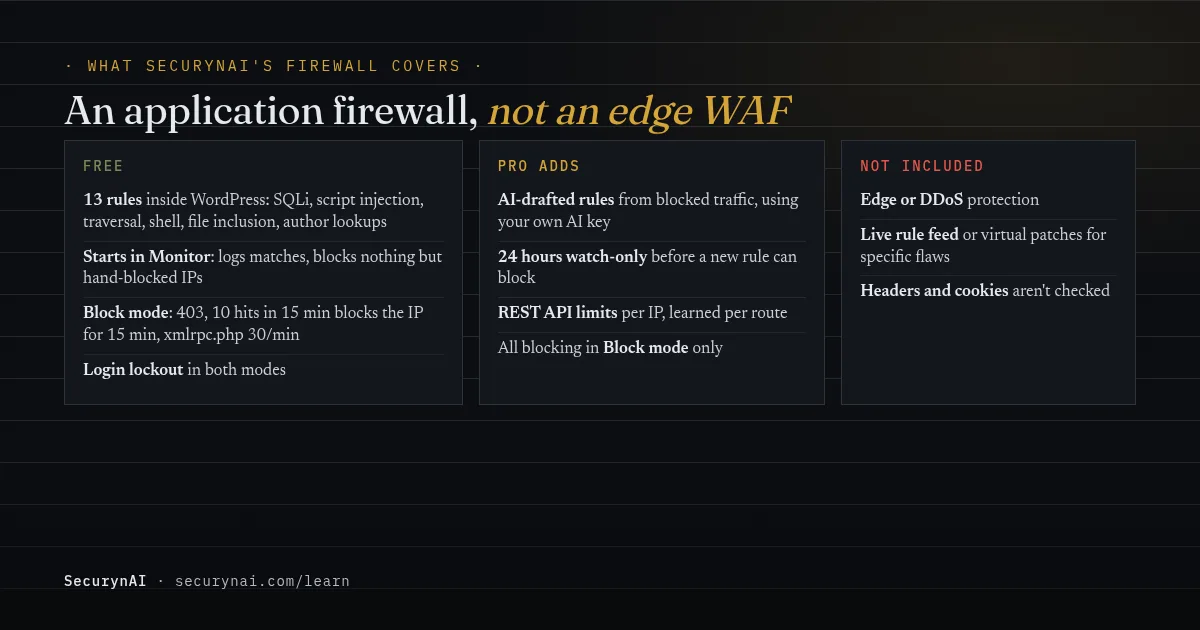
We at SecurynAI built a plugin firewall, so here it is without the gloss. The free plugin's firewall is an application-level firewall: it runs inside WordPress on every request, with 13 rules, and it starts in Monitor mode. It's switched on from install, and it runs as soon as WordPress has loaded your plugins.
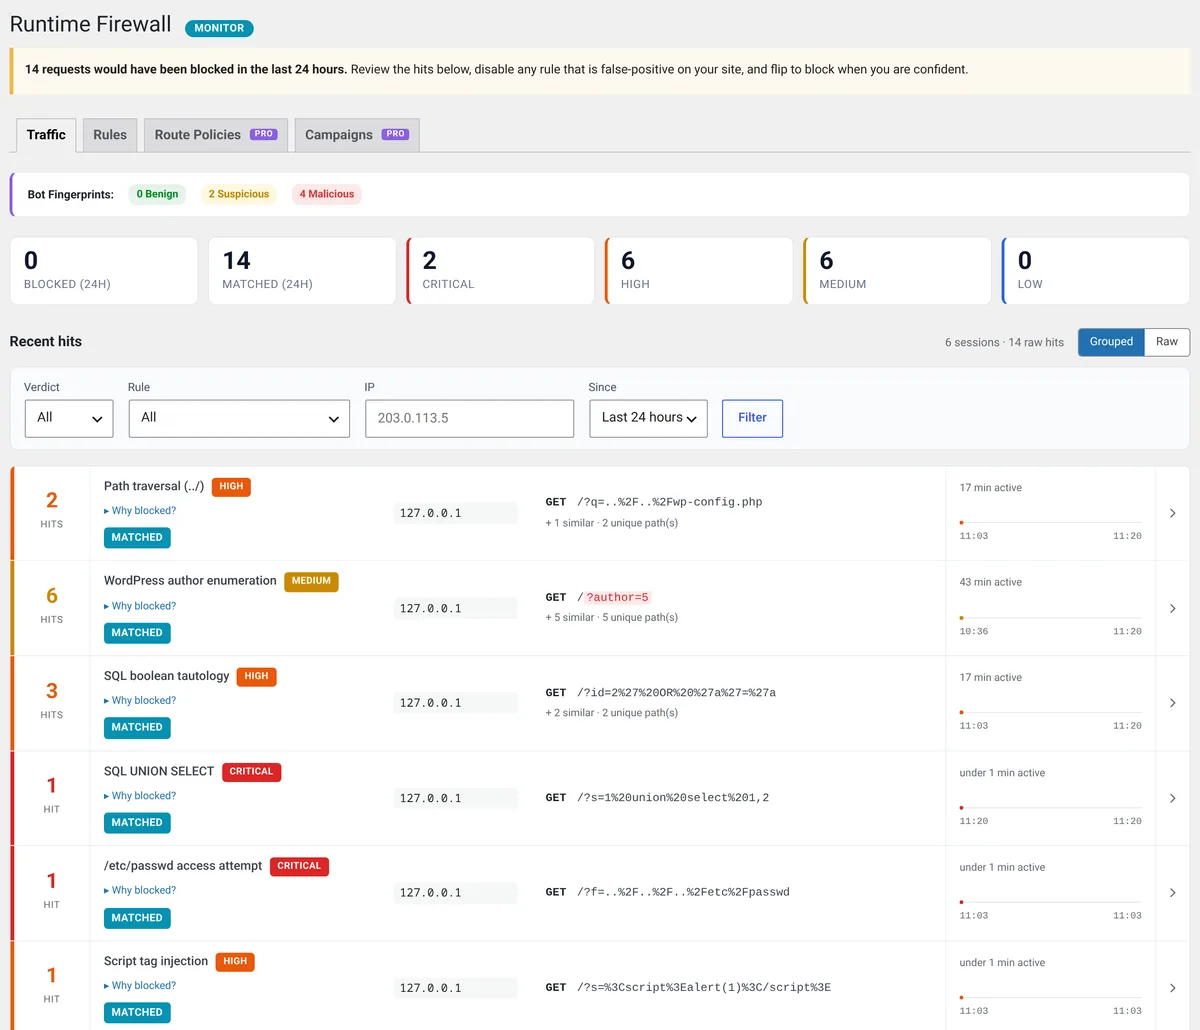
The 13 rules look for SQL injection (3 rules), script injection (3), path traversal (2), shell commands (2), file-inclusion tricks (2) and username lookups via ?author= (1).
They check the URL, the query string, form fields and JSON request bodies, as sent, so a <script> tag or a quoted ' OR '1'='1 in a form field reaches them. They don't check cookies or request headers.
Monitor mode first, then Block
In Monitor mode the firewall logs every match and blocks nothing, except IPs you've blocked by hand. The Firewall page shows the hits and how many requests "would have been blocked in the last 24 hours". If a rule trips on your own forms, untick it. Hits are kept for 14 days.
When you switch to Block mode, matching requests get a 403 page with a reference number. An IP with 10 matches in 15 minutes is blocked site-wide for 15 minutes, and xmlrpc.php is capped at 30 requests a minute per IP. IPs locked out for failed logins are also refused site-wide.
Login lockout works in both modes: 20 failed logins in 15 minutes, from one IP or against one username, locks that IP out of logging in for 30 minutes. If you ever lock yourself out, our locked out of wp-admin guide covers the safe way back in.
What it isn't
It isn't an edge WAF. It can't absorb a flood or protect you if WordPress won't load, and a plain flood of ordinary-looking requests matches none of its rules. There's no live rule feed and no virtual patches for specific plugin flaws; the rules update when the plugin does.
What helps with known flaws is a different free feature: vulnerability alerts, which tell you when an installed plugin or theme has a known vulnerability so you can update or remove it. That's the fix a WAF only delays.
What Pro adds to the firewall
On Pro ($79 per site per year), the adaptive firewall drafts extra rules from requests the free firewall blocked in Block mode during the past week. It sends samples to your own AI provider, tests each draft against known-good requests, and runs new rules in watch-only mode for 24 hours. After that they can block, in Block mode only.
Pro also limits REST API requests per IP. Once a route has 200 or more normal requests, its limit is learned from them; until then a default of 60 a minute applies. You can set a manual cap for a route. These limits apply only in Block mode, and logged-in administrators are never limited.
Pro also has code for tightening rules during reported attack campaigns, but no campaign feed ships with it today, so don't count on that part.
None of this replaces backups, updates or good hosting. See what Pro adds for the full list.
Quick check: is your WordPress firewall set up well?
- Do you know whether your host runs a WAF, and what it covers?
- If your site is behind a CDN or proxy, do your logs show real visitor IPs?
- Is some firewall, edge or plugin, actually blocking, not just logging?
- Did you review a week of matches before switching a plugin firewall to Block?
- Is login lockout or rate limiting on for
wp-login.phpandxmlrpc.php? - Are plugins and themes updated within days of a security release?
- Do you know how to switch the firewall off if it locks you out?
Six or seven yeses is a solid setup. Three to five is common and quick to improve. Fewer than that is a normal starting point: begin with questions 1 and 6. The hardening checklist covers the rest of the basics.
WAF for WordPress: common questions
Do I need a firewall plugin if my host already has a WAF?
Not always. Ask your host what its WAF covers and whether it has WordPress-specific rules. If it does, a plugin firewall is an extra layer, mostly useful for login lockouts and for seeing what's being tried. If the host only runs a network firewall, a plugin firewall fills a real gap.
Will a WAF slow down my WordPress site?
An edge WAF usually doesn't, because it runs on the provider's servers. A plugin firewall adds a little work to every request, since PHP has to check each one. On most sites that's small next to loading WordPress itself, but a site under a heavy flood will feel it.
Can a WordPress firewall plugin stop a DDoS attack?
No. By the time a plugin sees a request, your server has already accepted it and started PHP. A large flood has to be stopped before it reaches the server, by your host or an edge network. A plugin can still block the attacking IPs, but it can't absorb the volume.
Does a WAF protect me from a vulnerable plugin?
Sometimes, and only for a while. A WAF can block the request pattern an exploit uses, which buys time until you update. It doesn't remove the flaw, and a slightly different request can get past the rule. Updating or removing the plugin is the fix.
Want to see what's already knocking on your site before you decide on a WAF? The free SecurynAI firewall starts in Monitor mode and shows every match, without blocking anything until you're ready.
Install free →