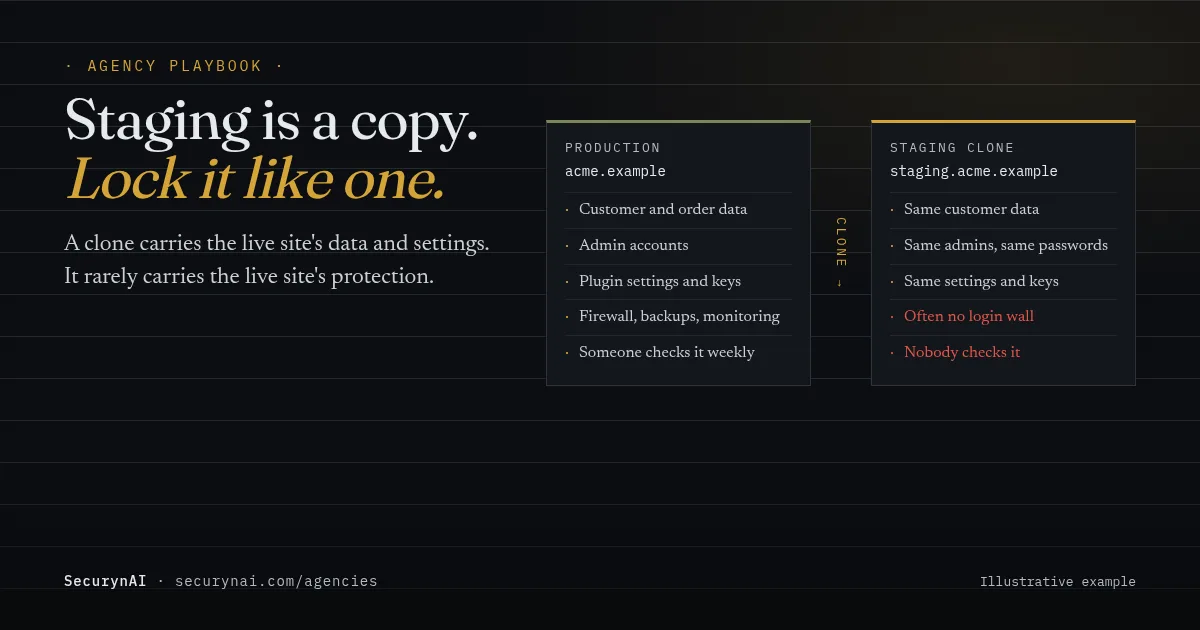
Staging vs production security is the gap between how well you protect a client's live site and how well you protect its copy. A WordPress staging site is a working clone of the live site, used to test changes before they go live. It usually carries the same customer data, admin logins and plugin settings, behind weaker walls.
So here's a fair question for any agency: how many staging sites are running for your clients right now, and who last checked them? This playbook gives you a lock-down routine for new staging sites, a list of what to keep out of them, and a read-only check to run on the live site after every push.
Why does a staging clone need the same care as the live site?
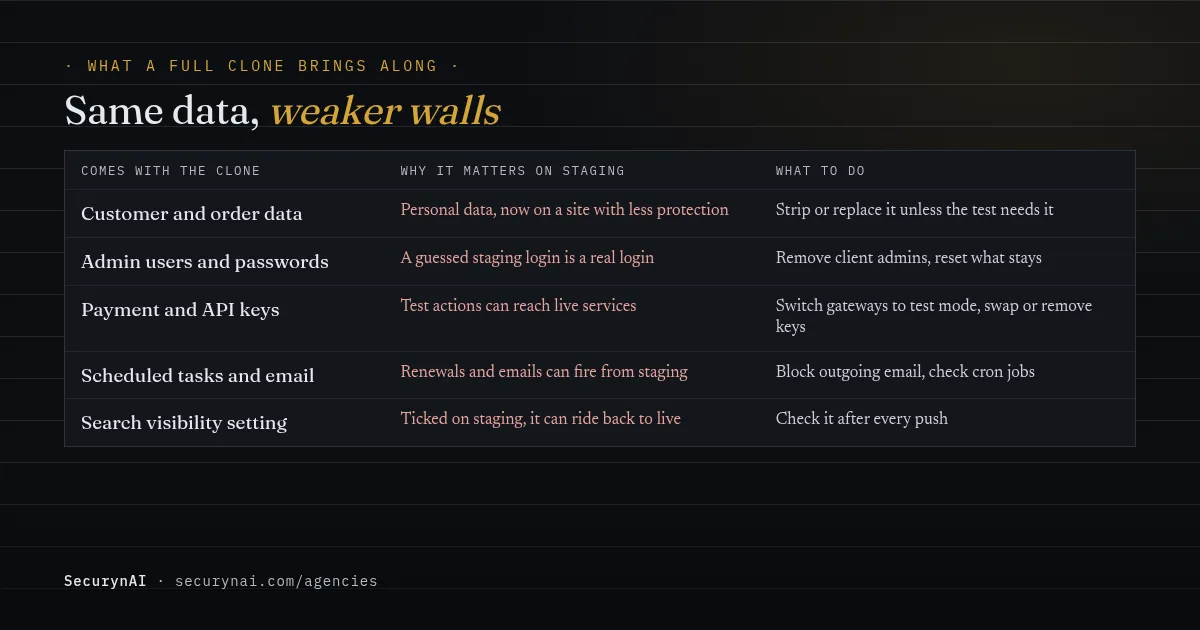
Because a full clone copies everything that makes the live site worth protecting. Customer records, order history, admin accounts with their password hashes, plugin settings and saved API keys all come along. What usually doesn't come along is the attention: the login wall, the monitoring, the weekly check.
Old plugins, same flaws
A staging site runs the same plugins as the live site, often at older versions because nobody updates it. Patchstack's State of WordPress Security in 2026 report counted 11,334 new WordPress vulnerabilities in 2025, with 91% in plugins. It also found about half of high-impact flaws were exploited within 24 hours of going public.
That speed is a problem for a site nobody patches. And "nobody knows the URL" isn't a wall. Every HTTPS certificate is recorded in public Certificate Transparency logs that anyone can query, so a subdomain like staging.client.com is easy to find once it has a certificate.
Copied data is still personal data
A WooCommerce clone holds real names, addresses and order histories. Labelling the copy "test" doesn't change what the data is. Under UK and EU GDPR, the data minimisation principle means you don't hold more personal data than the purpose needs. A theme tweak rarely needs a thousand real customers. (General information, not legal advice.)
Our guide to securing WooCommerce customer data covers what a store actually stores, and the GDPR data breach guide covers what happens if a copy leaks.
How do you keep a WordPress staging site out of Google, and out of reach?
Put a password on the whole staging site at the server, before you share the link. Google's own guidance on controlling what you share says private content needs password protection so only authorised users can reach it. A server password also stops bots before WordPress even loads.
Many hosts' staging tools can add this for you. If yours doesn't, it's a few lines. On Apache, create a password file outside the web root, then add this to the staging site's .htaccess, as the Apache docs describe.
htpasswd -c /home/acme/.htpasswd-staging agency

# in the staging site's .htaccess
AuthType Basic
AuthName "Staging"
AuthUserFile /home/acme/.htpasswd-staging
Require valid-user
On Nginx, the auth_basic module does the same job inside the staging site's server { } block. Either way, serve staging over HTTPS: Apache's docs point out that Basic auth sends the password unencrypted otherwise.
auth_basic           "Staging";
auth_basic_user_file /etc/nginx/htpasswd-staging;
Don't stack robots.txt on top of noindex
The old advice was "use a robots.txt block and a noindex tag, belt and braces." Google says those two fight each other. Its noindex documentation says a page blocked by robots.txt never has its noindex rule read, so it can still show up in results if other pages link to it.
So: the server password is the wall. WordPress's "Discourage search engines" setting (which adds a noindex rule) is a backup. Leave robots.txt alone on staging, because the password already keeps crawlers out.
Mark it as staging, and make it look like staging
Two small changes stop a lot of confusion. First, set WordPress's environment type in the staging site's wp-config.php. wp_get_environment_type() accepts local, development, staging or production, and defaults to production when nothing is set.
wp config set WP_ENVIRONMENT_TYPE staging --type=constant
wp option update blogname "STAGING - Acme Store"
Second, renaming the site title is optional but helps. Emails and screens that use only the site name will then say "STAGING", so nobody mistakes them for the real thing. SecurynAI's own alerts read the environment type, so they're tagged either way.
What should never ride along to staging?
Anything that lets the copy act on the real world: live payments, real emails, live API keys and client logins. A clone doesn't know it's a clone. Unless something tells it otherwise, it will try to do everything the live site does.
WooCommerce's own documentation shows how real this is. WooCommerce Subscriptions switches into a manual-renewal "staging mode" when the site URL changes. But if a database is moved and keeps the same domain, staging mode isn't triggered, and an old copy "will continue to process real recurring payments."
Paid Memberships Pro's staging guide makes the same point about charges: with working gateway credentials, "a test charge in staging could hit a real member's card." Their advice fits most client sites: treat staging as "a code and design sandbox, not a place to experiment with live data."
The staging intake list
- Customer data: strip or replace it unless the test needs it. Keep a few dummy orders and accounts instead.
- Client admin accounts: remove the ones staging doesn't need. Give your own team separate logins, not a shared one.
- Payments: switch every gateway to test or sandbox mode before anyone clicks anything.
- Email: block or redirect outgoing mail so customers never get a staging receipt or password reset.
- API keys: swap live keys for test keys, or remove them, wherever the plugin allows.
- Scheduled tasks: check what cron jobs, renewals and imports will fire from the copy.
How do you push changes live without breaking production security?
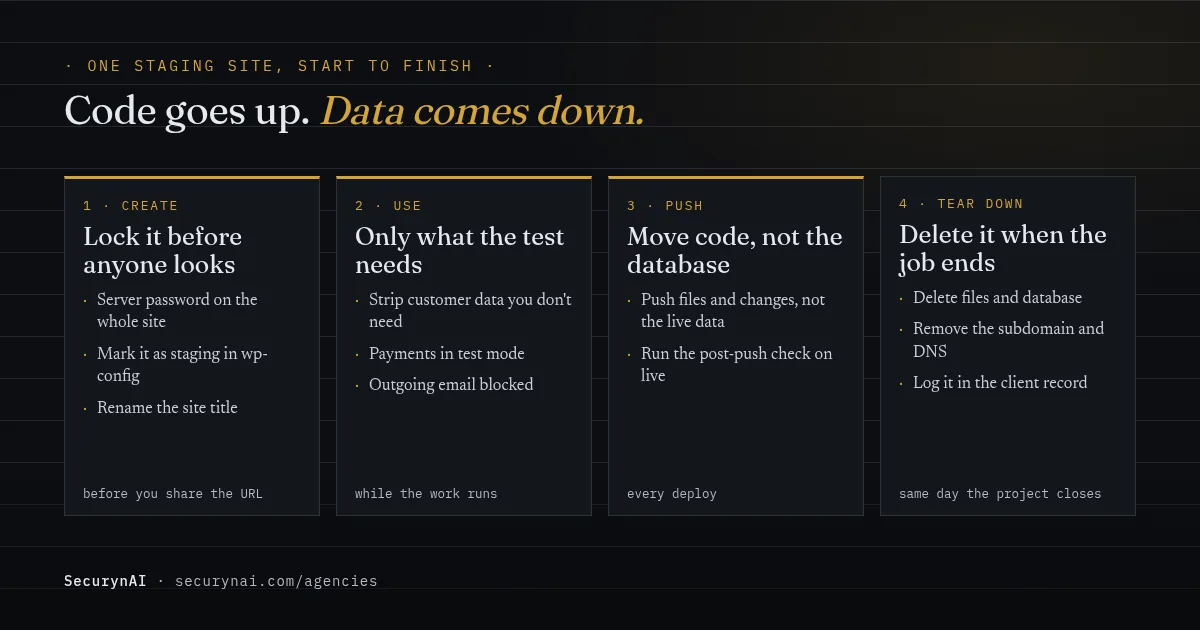
Push code and configuration up. Don't push the staging database over the live one. A database push replaces everything on live with whatever staging had: orders taken since the clone, user changes, and every setting you changed while testing. That includes the ones that weaken security.
The search setting is a well-known casualty. In one WordPress.org thread, a site owner asked how to stop "no index" syncing to production. The moderator's answer: it's saved in the database, so "yes that option would be enabled on sync."
It can go unnoticed for a long time. Mickey Mellen wrote in 2021 about a client whose site had the "discourage search engines" box ticked, a setting "they had mistakenly left turned on for a few years." Search traffic rose once it was switched off. Nothing looks broken to visitors, so nobody notices.
The post-push check (read-only)
Run these on the live site after any push, or ask your host to. They only read. Each line has an expected answer, so a wrong one stands out. The SecurynAI lines are for sites running our plugin; skip them otherwise.
wp option get blog_public          # expect 1 (0 = hidden from search)
wp option get blogname             # expect no "STAGING"
wp option get home                 # expect the live URL
wp config get WP_DEBUG --format=json   # expect false
wp eval 'echo wp_get_environment_type() . "\n";'   # expect production
wp option pluck securyn_settings firewall_mode          # expect what you set for live
wp option pluck securyn_settings alert_email_recipient  # expect your agency address
The commands come from the WP-CLI handbook. We ran each one on our own test site. If one answer is wrong, fix that setting on live and note it in the deploy log. A two-minute check beats finding out from a client's falling traffic.
If you must push a database
Sometimes a content migration really does need it. Back up the live database first, then push only the tables the change needs, if your migration tool allows it. wp db tables lists tables by pattern, which helps you decide what to leave out. Run the post-push check straight after.
When should a staging site be deleted?
The day the work it was made for goes live. A staging site made for one redesign tends to stay up for months, still reachable and still holding the data from the day it was cloned. Each forgotten copy is one more WordPress install with old plugins and real logins.
- Delete the staging files and its database, not just the WordPress login.
- Remove the subdomain and its DNS record, and any staging-only password files.
- Revoke staging-only accounts, API keys and any test keys you created for it.
- Write the date it was deleted in the client's record.
Need staging again next month? Clone a fresh one with current plugins. Our offboarding playbook covers the same "access outlives its reason" problem for people and tools, and the security audit playbook lists what to look for when you inherit a client with old copies lying around.
How does SecurynAI behave on a staging copy?
We at SecurynAI want to be straight about this. The plugin doesn't detect staging by itself. Apart from tagging alert emails once you set the environment type, it behaves the same on a clone as on live, and a clone copies its settings. A few things are worth knowing before you clone a site that runs it.
Alerts follow the clone
If the live site has Email serious findings switched on (it's off by default), the staging copy will email the same Send alerts to address. The subject shows the site title and host, so a copy on staging.acme.com reads differently from acme.com. With WP_ENVIRONMENT_TYPE set to staging, it also starts "[STAGING: …]".
Decide on purpose: either point staging at a separate inbox, or switch email alerts off on staging in Settings > General. Either way, a staging alert shouldn't look like a live one.
Settings and history travel with database pushes
SecurynAI keeps its settings in one WordPress option and its findings and activity log in tables named {prefix}securyn_…. A full database push from staging replaces the live site's copies. That can flip the live firewall back to Monitor and swap the live activity history for staging's.
The free firewall starts in Monitor mode, logging matches without blocking until you switch it to Block. Switching it in the settings is written to the Audit Log at high severity, with who did it. A database push skips WordPress and logs nothing, so the post-push check above is how you spot a push that undid Block.
Can't avoid a full push? Export the live Audit Log first with its Export CSV button. It saves the events matching the current filters, so clear them for the full history. It only holds what retention keeps (7 days by default), so file it with the deploy notes.
Checks that catch staging habits on live
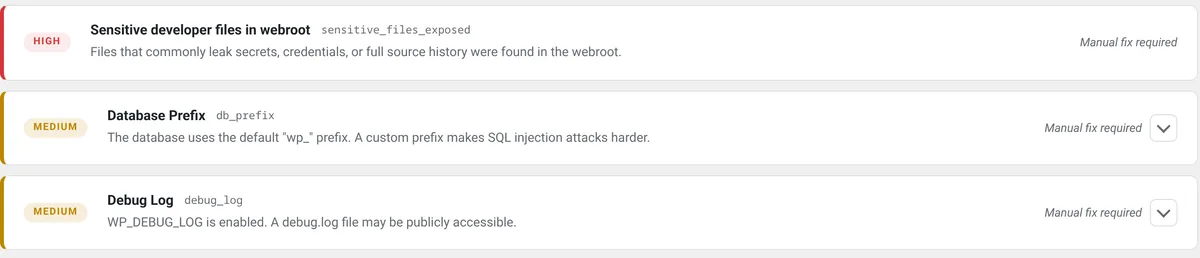
- Debug settings: the free hardening checks flag
WP_DEBUG,WP_DEBUG_DISPLAYandWP_DEBUG_LOGwhen they're on. On staging that's expected. On live, it's a finding to fix, and the checks re-run daily, so a pushed debug setting shows up within a day. Pro can switch them off inwp-config.phpfor you, taking a backup of the file first. - Developer files in the web root: a free check flags
.git,.svn,.env,composer.jsonand similar files left where visitors could reach them, a common side effect of deploy scripts. - Search and URL changes: the free activity log records changes to the search setting, site URL, admin email and SecurynAI's own settings made through WordPress. A raw database import skips WordPress, so the post-push check is still your safety net.
- Files on live: the daily scan compares core, plugin and theme files with official checksums, and checks PHP files under wp-content against 13 bundled malware signatures, with no live feed. It detects only and doesn't clean anything.
One more detail for AI users. If you've added your own AI key, SecurynAI stores it encrypted, using keys from the site's wp-config.php. A staging copy that shares the live wp-config.php can use that key.
One with its own fresh salts can't read it. WordPress admin then shows a warning linking to Settings > AI Provider to re-enter the key, and findings use the built-in explanations until you do.
None of this replaces backups, a staging password or good hosting. It makes the live site's state easier to check after a push. Managing many client sites this way? Our 30+ client sites playbook turns these checks into a weekly WP-CLI sweep, and our agency page covers bulk licensing.
Quick check: are your staging sites under control?
- Could you list every staging site your agency runs, with its client and purpose, in five minutes?
- Does every one ask for a password before WordPress loads?
- Are payments in test mode and outgoing email blocked on each one?
- Do you push code rather than databases, by default?
- Do you check the live site's search setting after every push?
- Do staging sites get deleted when the project ends?
Five or six yeses means staging is under control. Three or four is common, and a week of tidying closes most gaps. Fewer is a normal place to start: list what's running, password the ones you keep, and delete the rest.
Staging vs production security: FAQ
Does a staging site need a security plugin?
If it's online and holds client data, it needs the same basics as live: updates, a password wall and someone who looks at it. The server-level password matters most, because it stops bots before WordPress loads. A staging site that's locked, short-lived and deleted on time needs far less than one left running for months.
Is "Discourage search engines" enough to keep a staging site out of Google?
No. WordPress itself says it's up to search engines to honour the setting, and it does nothing to stop people or bots who find the URL. Google's own advice for private content is to password-protect it. Use the setting as a backup, and check it after every push so it doesn't land on the live site.
Should a staging site have real customer data?
Only when the test truly needs it, which is rarer than it seems. Theme changes, plugin updates and layout work can be tested with a few dummy orders and accounts. If you do copy real data, it's still personal data, so protect it like the live site and delete the copy when the work ends.
Does SecurynAI know when it's running on a staging site?
Only if you tell it. A clone copies SecurynAI's settings, including the alert address and firewall mode. Set WP_ENVIRONMENT_TYPE to staging and alert subjects start with "STAGING", next to the site title and host. Decide whether staging alerts should reach you at all, and after a database push, check the live site's SecurynAI settings too.
Running staging and live copies for a lot of client sites? Start with the free plugin on your live sites, then talk to us about bulk licensing for the rest. A real person replies.
See agency options →