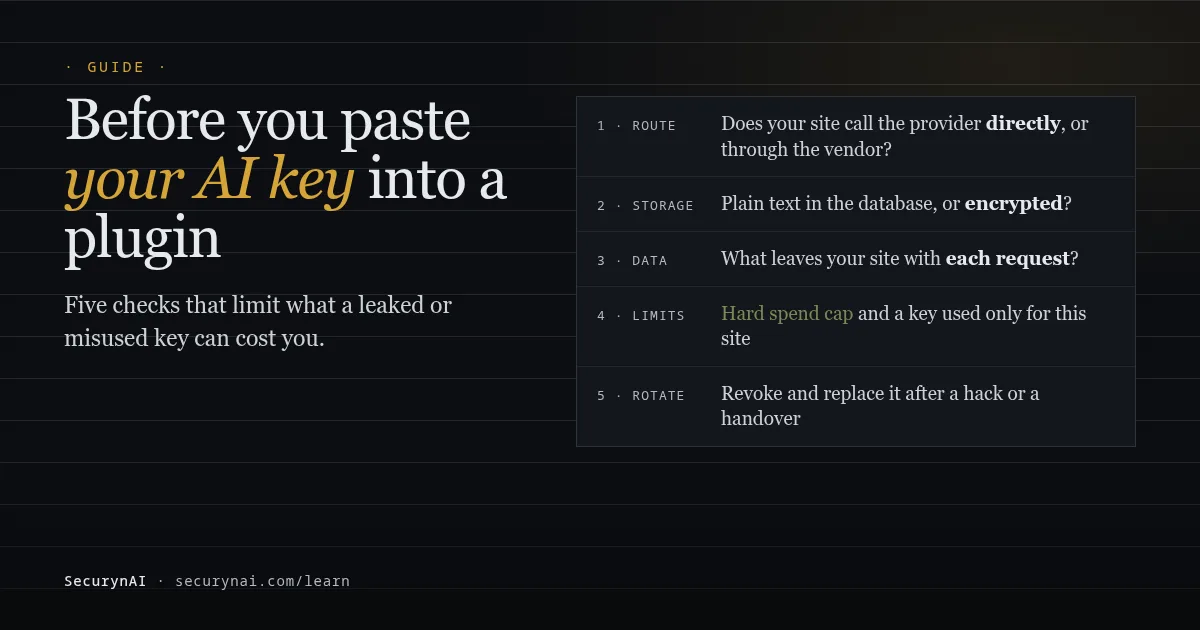
An AI API key is a password that lets whoever holds it use your OpenAI, Anthropic or Google Gemini account, and you pay for every request. When a plugin asks for one, AI API key security comes down to two questions: how well does the plugin look after it, and how much damage can it do if it leaks?
Short answer: giving a plugin your key is reasonable, as long as you control the blast radius at the provider. Set a hard monthly spend limit, make a key that's used only for this site, and know how to revoke it. Those three steps protect you even if the plugin, or the site, lets you down.
Why plugins ask for your own OpenAI or Anthropic API key
"Bring your own key" means you pay the AI provider directly, at its own prices, with no markup from the plugin. You also see every request in your own usage dashboard. That's a fair deal, and it's why many AI features in WordPress plugins, including ours, work this way.
The catch is that the key is a credential, and leaked keys get used. GitGuardian's State of Secrets Sprawl 2026 report counted 1,275,105 leaked AI-service secrets in public GitHub commits during 2025, up 81% on the year before.
Leaked keys also stay live for a long time. The same report found that over 64% of secrets confirmed valid in 2022 still worked when retested in January 2026.
People feel this as surprise bills. In one OpenAI community forum thread, a developer reported large charges on a key they hadn't used for weeks. One of the first questions back was whether the key had been pasted into any third-party "bring your own key" apps. That's the right question, and the checklist below is how you answer it.
Check 1: does your site call the AI provider directly?
The same "paste your API key here" box can hide two very different setups. Ask the vendor which one you're getting, or read the plugin's privacy notes or code.
- Direct: your WordPress server sends each request straight to OpenAI, Anthropic or Google with your key. The plugin vendor never sees the key, the request or the reply.
- Proxied: your site sends the request, and sometimes the key, to the vendor's own server first, which then calls the AI provider. Your data now passes through a third party, even if the vendor promises not to log it.
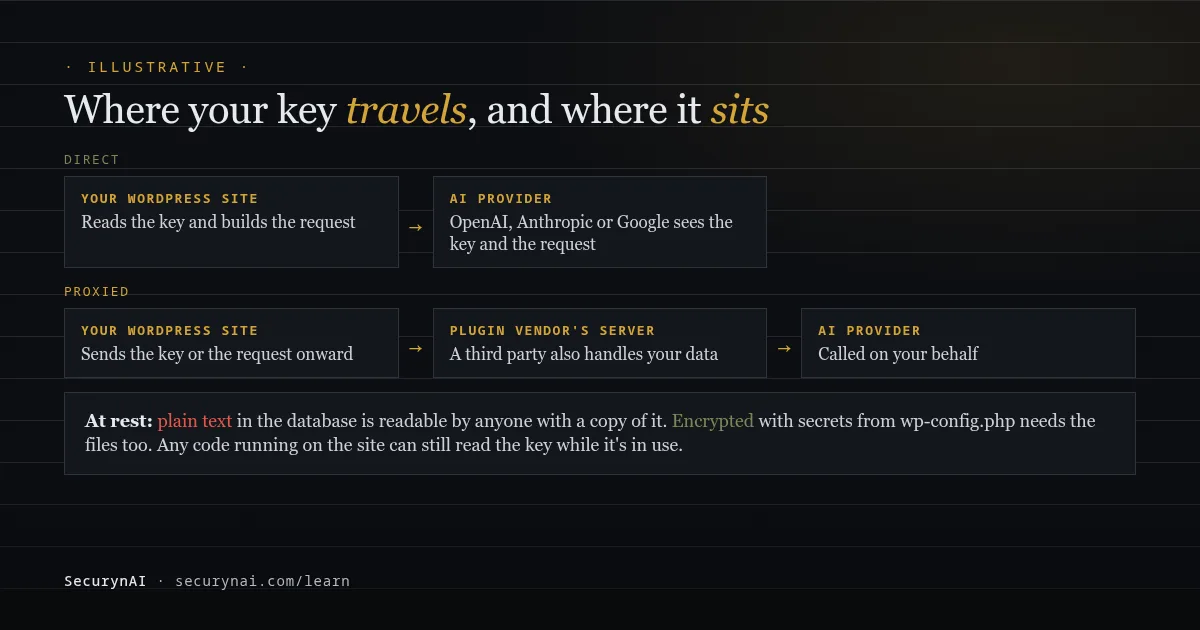
A proxy isn't automatically bad. Some vendors use one to add caching or usage limits. But a plain answer to "does my key or my data ever touch your servers?" should be easy to get. If it isn't, that tells you something.
Check 2: how does the plugin store your AI API key?
Plain text in the database is the default unless a plugin deliberately does something better. A plain-text key can be read by anyone with a copy of your database: a backup file, a staging copy, a migration export, or an attacker who found a SQL injection flaw that reads data.
WordPress itself is a good example. WordPress 7.0 added a Connectors screen that saves one AI provider key for every plugin on the site to share. The Connectors API announcement says plainly that "API keys stored in the database are not encrypted but are masked in the user interface," and that encryption is being explored in a follow-up ticket.
The same post lists a better option. WordPress checks for the key in an environment variable first, then a PHP constant (for example in wp-config.php), and only then the database. A key kept outside the database doesn't end up in database backups or exports.
What encryption does, and what it doesn't
Encrypting the key protects it from database-only leaks. It doesn't protect it from code running on your site. Most plugins encrypt with secrets from wp-config.php. Someone holding only the database gets scrambled text. Someone who can read your files or run PHP can decrypt it, because the plugin does exactly that on every AI call.
The WordPress community has said as much. In the comments on the Connectors announcement, a core contributor pointed out that environment variables and constants are just as reachable by the third-party plugins you install. Every plugin on your site runs with the same access, so a bad plugin can read any key. That's why Check 4 matters more than storage.
Check 3: what data leaves your site with each AI request?
A well-scoped AI feature sends only what one task needs, not your whole database. Ask what goes into a typical request. For a security plugin explaining an alert, that's usually the finding itself. It may still include usernames, IP addresses, file paths or a snippet of code from a flagged file.
That data goes to the AI provider under your own account, so the provider's data terms apply. If you look after client sites, mention it in your privacy notice and your client agreement. And if a feature that "explains one alert" sends post content or your user table, that's broader than it needs to be.
One related risk sits on the other side of the request: text an attacker plants on your site can try to steer what the AI says. That's prompt injection, and it gets its own guide.
Check 4: set a hard spend limit and scope the key at the provider
This is the step that protects you even when everything else fails. A leaked key with a $20 monthly cap is an annoyance. A leaked key with no cap has no ceiling. Do it the day you create the key, not after a surprise bill.
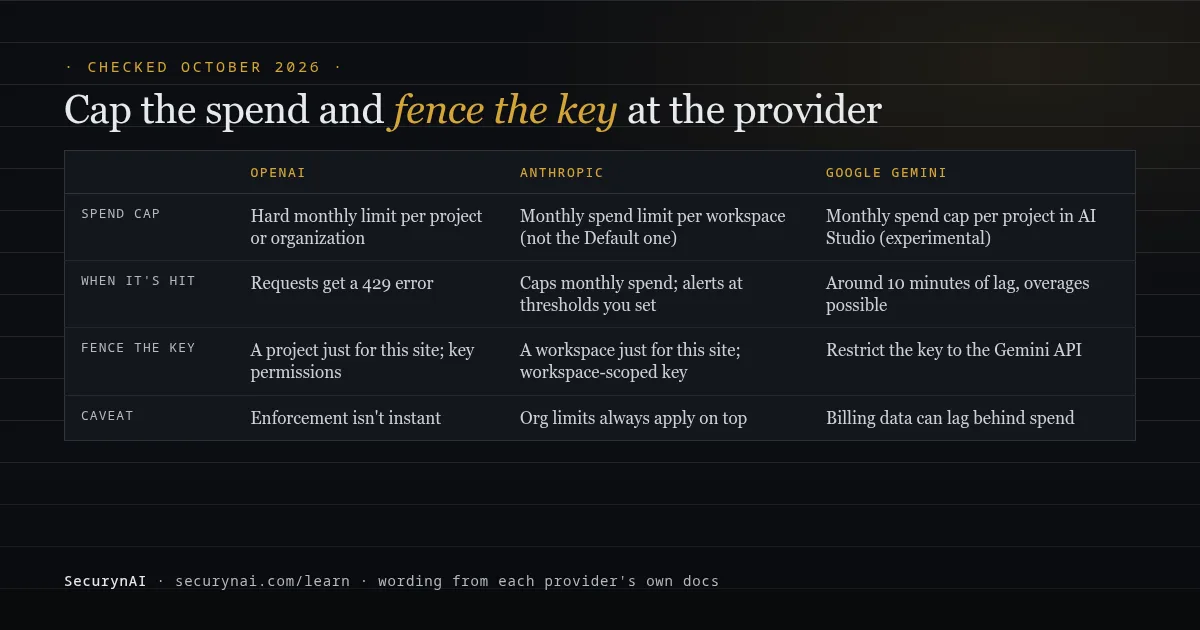
Here's what each provider's own documentation says today:
| Provider | Spend limit | Scope the key |
|---|---|---|
| OpenAI | A monthly hard limit per organization or project. When it's reached, requests "return a 429 error". OpenAI notes "enforcement is not instantaneous", and that spend alerts alone "do not enforce a cap". | Create a project just for this site and set its limit. OpenAI also recommends an expiry date on project keys. |
| Anthropic | A monthly spend limit per workspace, set under Workspaces › Spend limits in the Claude Console, with alerts at thresholds you choose. It can't be set on the Default Workspace. | Create a workspace for this site and a key scoped to it, so the workspace limit applies. |
| Google Gemini | A monthly spend cap per project in AI Studio (Spend › Monthly spend cap). Google calls it experimental and warns of overages for "around a 10 minute latency period". | Restrict the key to the Gemini API. New AI Studio keys are restricted to it by default. |
Sources: OpenAI spend limits and production best practices, Anthropic workspaces, and Google's Gemini billing and API key pages, all checked October 2026. Provider screens change, so check the names before you click.
Alerts aren't limits. In a 2026 thread on Google's AI developer forum, a developer described about ₹8.3 lakh in charges within roughly two hours on a compromised key. Several replies said budget alerts had warned them but hadn't stopped the charges. Set the hard cap, not just the email.
One key per site, especially for agencies
If you manage several client sites, give each its own key, inside its own OpenAI project or Anthropic workspace. A leak on one site then costs one capped budget, and revoking that key doesn't break the others. Billing each client for their AI use gets simpler too. Our guide to offboarding a client site covers revoking keys at handover.
Check 5: know how to rotate the key, and when
Rotating means making a new key, putting it in the plugin, then revoking the old one. In that order, the AI features don't go dark in between. All three providers let you revoke a key instantly from their dashboard.
Rotate the key when:
- The site was hacked, or you think someone read the database or files. Treat the key like the database password. Our malware removal guide covers the rest of the clean-up.
- Someone with admin or server access leaves, such as a freelancer or a former agency.
- A copy of the site went somewhere you don't control, like a shared staging server or a backup you sent to a developer.
- Your usage dashboard shows requests you can't explain. Revoke first, investigate second.
If you restore the site from a backup after a hack, the key in that backup is the old, possibly exposed one. Save the new key again after restoring. Our guide to restoring from a backup after a hack walks through the rest.
How SecurynAI handles your AI API key
We at SecurynAI built our AI features to pass this checklist, so here's exactly how they work. AI is optional in the free plugin. Without a key, every finding still gets a shorter built-in explanation, and the detection itself (firewall rules, file checksums, malware signatures, hardening checks) never depends on AI.
Where the key goes
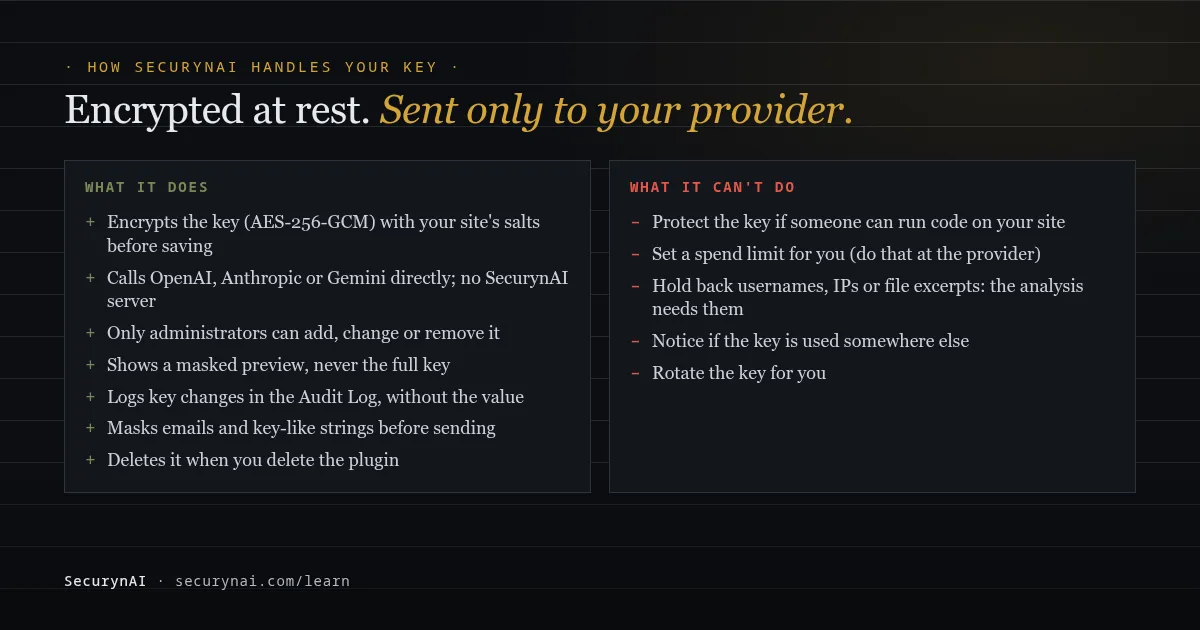
Your site calls OpenAI, Anthropic or Google Gemini directly, using your key. There's no SecurynAI server in between. If you don't pick a model, we use a small, low-cost default for each provider.
The free plugin asks the AI about every new critical or high finding. Medium and low findings share 10 AI calls a day. Each answer is saved for 30 days, so the same finding isn't paid for twice, unless you click Re-analyze to ask again.
What goes out is the finding itself: usernames, IP addresses and excerpts of flagged files are sent, because the analysis needs them. Email addresses and anything shaped like a key or password, such as API keys or wp-config.php secrets, are masked before the request leaves your site.
How the key is stored
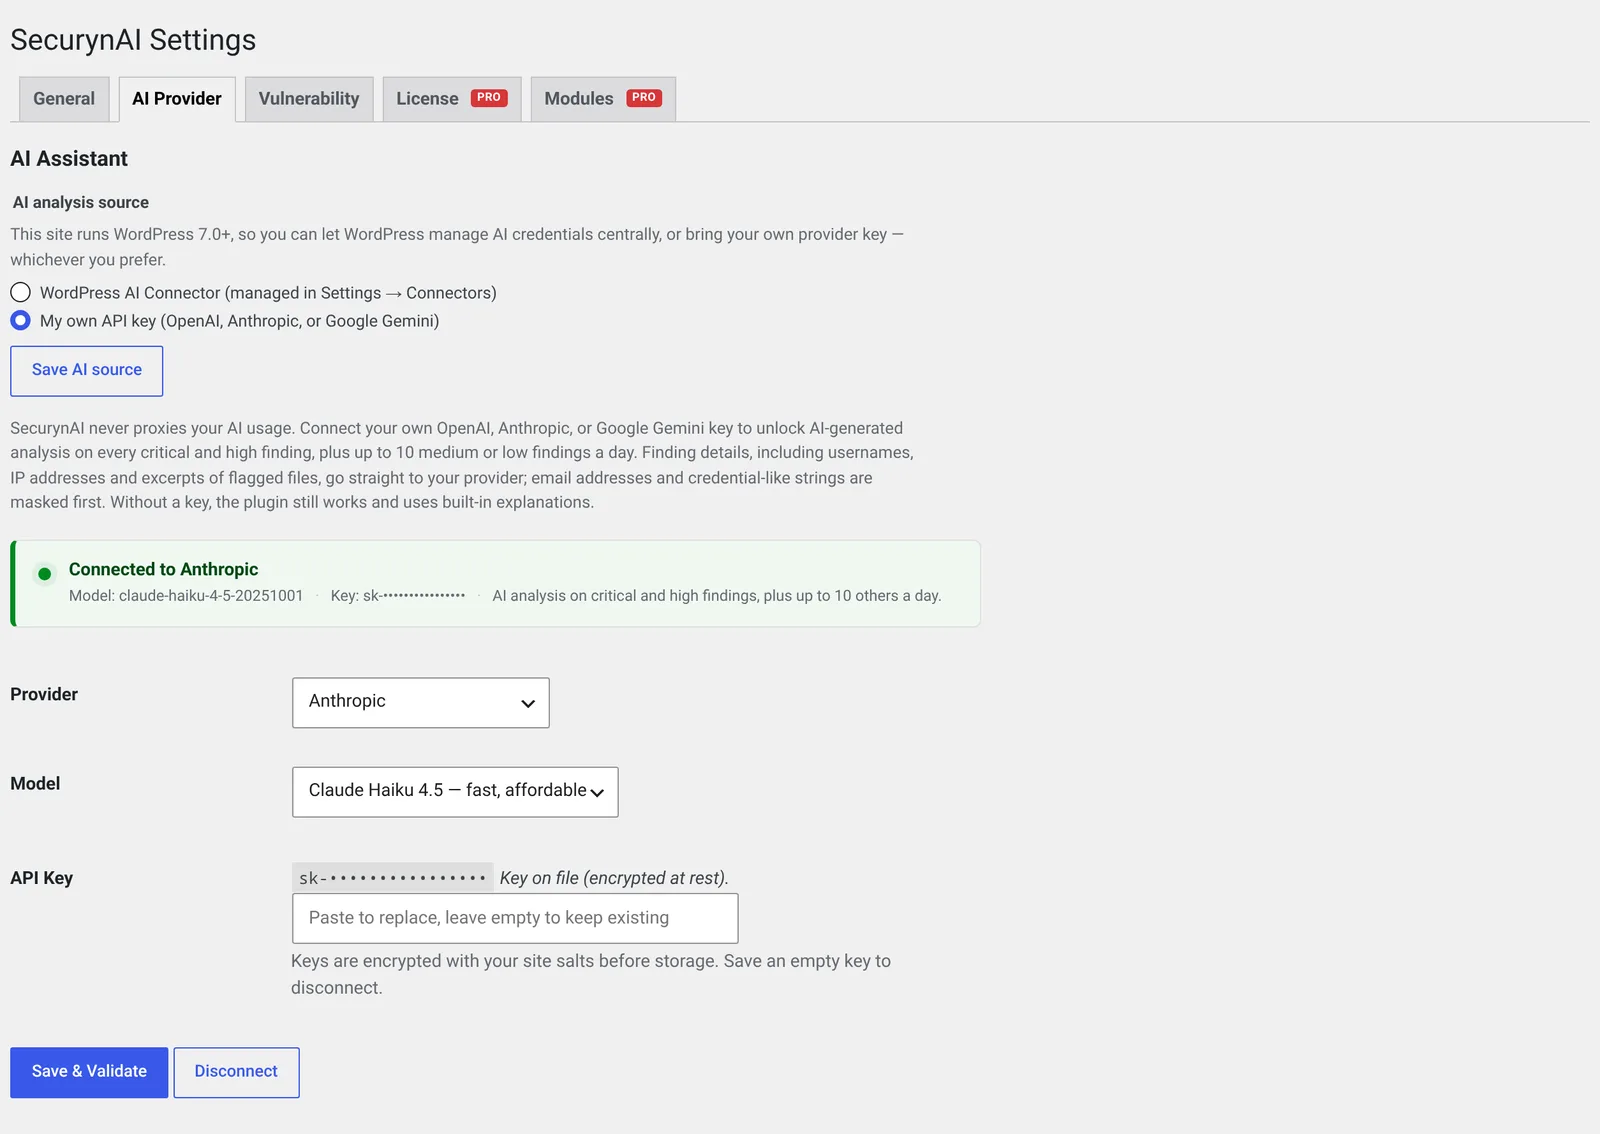
- Encrypted at rest. The key is encrypted with AES-256-GCM, using an encryption key derived from your site's secret keys in wp-config.php. If the server can't encrypt, you get an error and nothing is stored. A Wordfence Intelligence key, if you add one, is stored the same way.
- Admins only. Adding, changing or removing it needs the "manage options" permission, which in practice means administrators.
- Never shown back in full. The Settings › AI Provider tab shows a masked preview, such as the first few and last four characters.
- Logged without the value. The Audit Log records that the key changed, and who changed it, but never the key itself.
- Removed with the plugin. Clicking Disconnect clears it. Deleting the plugin from WordPress deletes all its settings, key included. Deactivating alone doesn't.
Encryption has the limit described above. It keeps the key out of a stolen database dump, but anyone who can run code on your site can still use it.
If your wp-config.php secret keys change, for example after a hack clean-up or a move, the saved key can't be decrypted any more. The plugin then shows an admin warning asking you to enter it again, and uses built-in explanations until you do.
If your site runs WordPress 7.0 or later
On WordPress 7.0+, SecurynAI's AI source starts out set to the WordPress AI Connector. In that mode we don't store a key at all: WordPress does, under Settings › Connectors, with the storage rules described in Check 2. You can switch to "My own API key" on the AI Provider tab if you'd rather we store it encrypted.
What Pro adds
Pro ($79 per site per year) uses the same saved key for more features, such as Copilot answers, attack-chain reports and AI checks of suspicious code. Expect higher usage, and set the spend limit first. Whether AI should be allowed to change anything is a separate question, covered in our guide to AI auto-fixes.
Here's what neither version does. SecurynAI can't set a spend limit at your provider, can't tell if your key is being used somewhere else, and doesn't hold back the usernames, IP addresses or file excerpts in the findings it sends for explanation. None of this replaces updates, backups or good hosting.
Your AI API key security checklist
Run through this before you paste a key into any plugin, ours included:
- Confirm the route. Does the site call the provider directly, or through the vendor's server?
- Check the storage. Plain text in the database, encrypted, or kept in wp-config.php or an environment variable?
- Check the payload. What goes out with a typical request, and does it include personal data?
- Set a hard spend limit at the provider, not just an alert.
- Use a key for this site only, in its own project or workspace.
- Know who can change it. Only administrators should be able to see or replace the key.
- Write down how to revoke it, and do it after a hack, a staff change or a handover.
Seven ticks means a leak would cost you a capped amount and a few minutes. If you only do two today, do the spend limit and the per-site key. For the bigger picture of what AI is and isn't good at in a security plugin, read what "AI-powered security" actually means and how to fact-check an AI security explanation.
AI API key FAQ
Can a WordPress plugin steal my OpenAI or Anthropic API key?
Any plugin you install runs with full access to your site, so it can read a key stored by another plugin or by WordPress itself. That's why the provider-side controls matter most: a hard spend limit, a key used only for that site, and revoking the key when you stop trusting the plugin.
Is it safer to put my AI key in wp-config.php?
It keeps the key out of database backups and exports, which helps. It doesn't hide the key from plugins, because any code on the site can read a constant. Use it if your plugin supports it, but still set a spend limit.
How much can a leaked AI API key cost me?
Without a hard spend limit, there's no ceiling: forum reports describe bills of thousands of dollars within hours. With a hard monthly cap at the provider, the most you lose is that cap, give or take a short enforcement delay.
Do I need to change my AI key after my WordPress site is hacked?
Yes. If an attacker could run code or read your database, assume the key was seen. Create a new key, save it in the plugin, then revoke the old one at the provider. Do the same for other passwords and keys on the site.
Want plain-English security alerts, with AI explanations only if you choose to add a key? The free SecurynAI plugin keeps the key encrypted and talks to your provider directly.
Install free →